What are your key focus areas? *
AI Workflow and Operations
Data Management and Operations
AI Governance
Analytics and Insights
Observability
Security Operations
Risk and Compliance
Procurement and Supply Chain
Private Cloud AI
Vision AI

Tell us about you and your priorities so we can prepare the right conversation. It takes about 2 minutes.

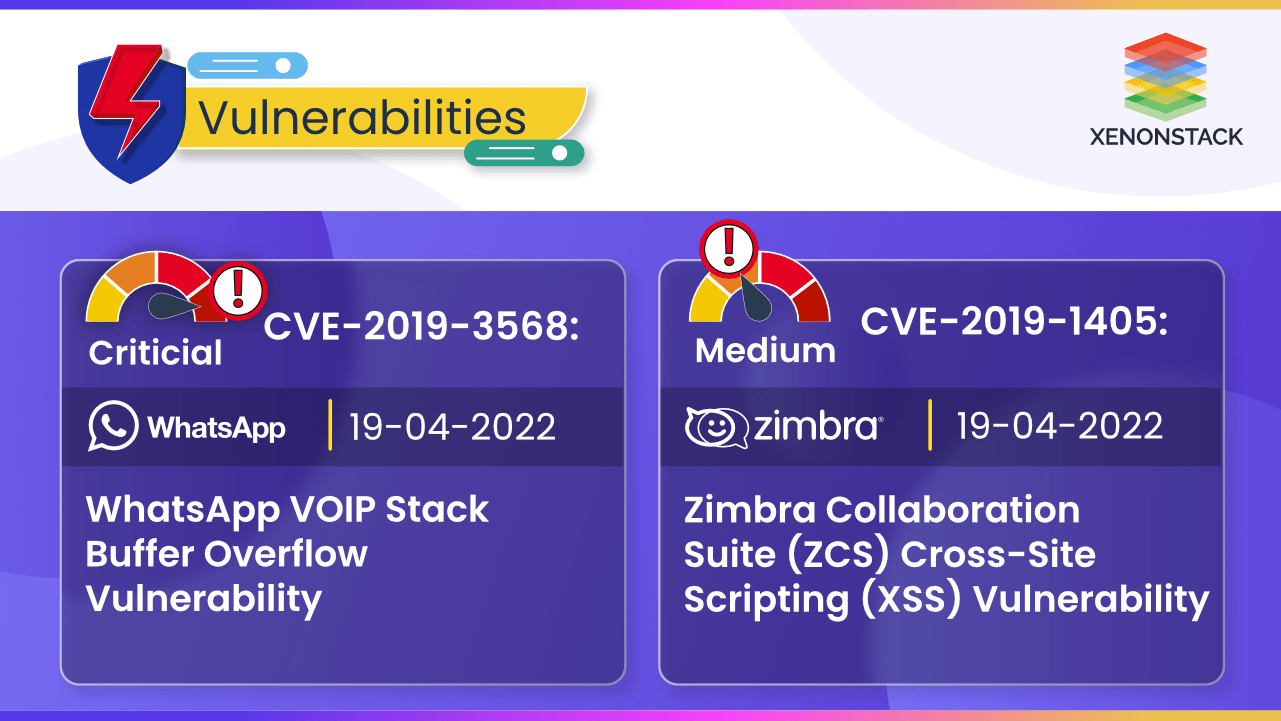
CVE-2019-3568 (Whatsapp) and CVE-2018-6882 (Zimbra) Vulnerabilities allow attackers to remotely inject arbitrary HTML or remotely execute code
CVE-2019-3929 hits Crestron and other presentation gateways; CVE-2022-1388 bypasses F5 BIG-IP login. See affected versions, CISA KEV status and fixes.
Fix CVE-2022-22947 (Spring Cloud Gateway) and CVE-2022-30525 (Zyxel firewalls): fixed versions, CISA KEV status and what to check now if you run them.
Remcos RAT for security leaders: how phishing delivers it, ATT&CK mapping, email and EDR controls, and a response runbook. Defensive guidance only.
Code Red worm explained: the 2001 IIS exploit (MS01-033), how it spread, what CERT/CC advised, and the patching lessons for security leaders.
The Sasser virus was a 2004 Windows worm that exploited LSASS flaw MS04-011. Learn how it spread, how to spot it and the defences that still apply.
Spring4Shell (CVE-2022-22965) is a critical Spring Framework flaw. See affected and fixed versions, who is exposed, workarounds and how to confirm ...
Clop (CL0P) is a ransomware and data-extortion group linked to TA505. Learn how its attacks work, what CISA advises, and the steps to take first.
Tinba is a 20 KB banking trojan. Learn how it steals credentials, why its 2014 leak matters and which CISA-based controls and response steps defend ...
Critical flaws CVE-2022-25880 (DIAEnergie SQL injection) and CVE-2022-1040 (Sophos Firewall auth bypass): affected versions, scores, fixes, response.
CVE-2020-5135 (SonicOS buffer overflow) and CVE-2019-1405 (Windows UPnP privilege escalation): what they are, affected versions, scores and how to ...
CVE-2022-24086 hit Adobe Commerce and Magento Open Source; CVE-2022-0609 hit Chrome. See what each flaw is, the affected versions and how to respond.
Read what the CVE records say about the Zimbra Calendar XSS flaw and the Microsoft Office RCE flaw, how they compare, and how to check and fix ...
Atlassian Jira CVE-2019-11581 and Pulse Connect CVE-2020-8218 Injection Vulnerabilities allow attackers to execute arbitrary code
Learn to triage and patch CVEs using CVE-2021-21973 and CVE-2017-6077: NVD, CVSS, CISA KEV, patch SLAs, asset inventory and governed AI agents.
CVE-2022-23131 let attackers bypass Zabbix frontend SAML login and CVE-2022-23134 exposed setup.php. See affected versions, fixes and workarounds.


Application release engineering explained: branching, pipelines, rolling, blue/green and canary releases, tooling and DORA metrics for enterprise ...
Agentic process automation in logistics and supply chain: where APA beats RPA, which processes suit it, the controls it needs and how to adopt it.
Application modernization explained: the seven migration strategies AWS lists, how to choose between them, the steps to follow and where AI agents ...
DataOps as a service is a managed way to run pipelines, quality checks and monitoring. See what it includes, how it works and when to buy or build.
Conversational UI best practices for enterprise teams: how CUIs work, design rules, governance, current tools and when not to use a chatbot.
Real-time intelligence turns streaming events into decisions in seconds. See the architecture, use cases, trade-offs and how to govern automated ...
The transformative impact of ai and emergingtechnologies on the world of finance and banking
6 min | Dr. Jagreet Kaur
Comprehensive approach combines cost forecasting, resource optimization, and financial accountability
4 min | Dr. Jagreet Kaur
Unleashing data agents empowers real-time insights, driving smarter decisions and transforming business operations effectively
5 min | Dr. Jagreet Kaur
AI continuously monitors systems for risks before they escalate. It correlates signals across logs, metrics, and traces. This ensures faster detection, fewer incidents, and stronger reliability
 Proactive detection of performance and availability issues
 Root-cause analysis across microservices and environments
 Automated remediation playbooks to reduce MTTR

AI converts camera feeds into instant situational awareness. It detects unusual motion and unsafe behavior in real time. Long hours of video become searchable and summarized instantly
 Real-time detection of suspicious motion or intrusion
 Natural language video search and instant playback
 Smart summaries for audits, investigations, and compliance

Your data stack becomes intelligent and conversational. Agents surface insights, detect anomalies, and explain trends. Move from dashboards to autonomous, always-on analytics
 Connects to warehouses, lakes, and streaming sources
 Question-answering in natural language
 Continuous monitoring for anomalies and KPI deviations

Agents identify recurring failures and performance issues. They trigger workflows that resolve common problems automatically. Your infrastructure evolves into a self-healing environment
 Automated diagnostics for recurring errors
 Playbook execution: restart services, scale pods, clear queues
 Feedback loop for improving remediation strategies

AI continuously checks controls and compliance posture. It detects misconfigurations and risks before they escalate. Evidence collection becomes automatic and audit-ready
 Continuous control checks across infrastructure and SaaS
 Automated evidence collection for audits
 Risk scoring and prioritized remediation recommendations

Financial and procurement workflows become proactive and insight-driven. Agents monitor spend, vendors, and contracts in real time. Approvals and sourcing decisions become faster and smarter
 Real-time visibility into spend and commitments
 Anomaly detection on invoices and vendor performance
 Intelligent workflows for approvals and sourcing decisions


