Key takeaway
- How ServiceNow AI agents support governance, risk and compliance: policy, controls, reporting and risk work, plus the limits and the governance they need.
ServiceNow AI agents for governance, risk and compliance (GRC) are software agents that work inside the ServiceNow platform to help teams manage policies, controls, risks and audit evidence with less manual effort. They sit on top of the GRC workflows a team already runs, and a person still owns every decision that carries regulatory weight.
This guide is for risk, compliance and internal audit leaders, and for the ServiceNow architects who support them. It covers what GRC on ServiceNow includes, where agents can help, how the platform fits together, where the limits are, and how to start. Our ServiceNow solutions page shows the wider practice.
What is GRC on the ServiceNow platform?
GRC is the set of practices an organisation uses to set rules, understand its risks and prove it follows its obligations. The ServiceNow GRC page describes a "unified, proactive approach to risk management" that connects AI, workflow and data, and describes compliance management as continuously monitoring IT systems for "adherence to industry standards, legal regulations, and internal policies". It also covers third-party risk, which it frames as managing the vendor lifecycle "from onboarding to retirement".
ServiceNow positions the offer as unifying GRC "with AI insights, automated workflows, and connected data". That framing matters: agents are only as useful as the records, controls and workflows they can reach.
What do ServiceNow AI agents do?
The ServiceNow AI agents page says AI agents "act autonomously to get work done" and that an orchestrator coordinates teams of agents towards a goal. Unlike a single prompt-and-answer assistant, an agent can plan a short sequence of steps, call tools and hand the result to a person or another agent. In a GRC setting those steps run across policies, controls, risks, issues and evidence.
One caution on naming. ServiceNow has renamed and regrouped its AI features since older articles, including this topic, were written. The governance console for agents appears as the "AI Control Tower" on the GRC page and as the "Super Intelligence Control Tower" on the AI agents page. Check current names and licensing with ServiceNow before you plan a rollout.
Where can AI agents help across the GRC lifecycle?
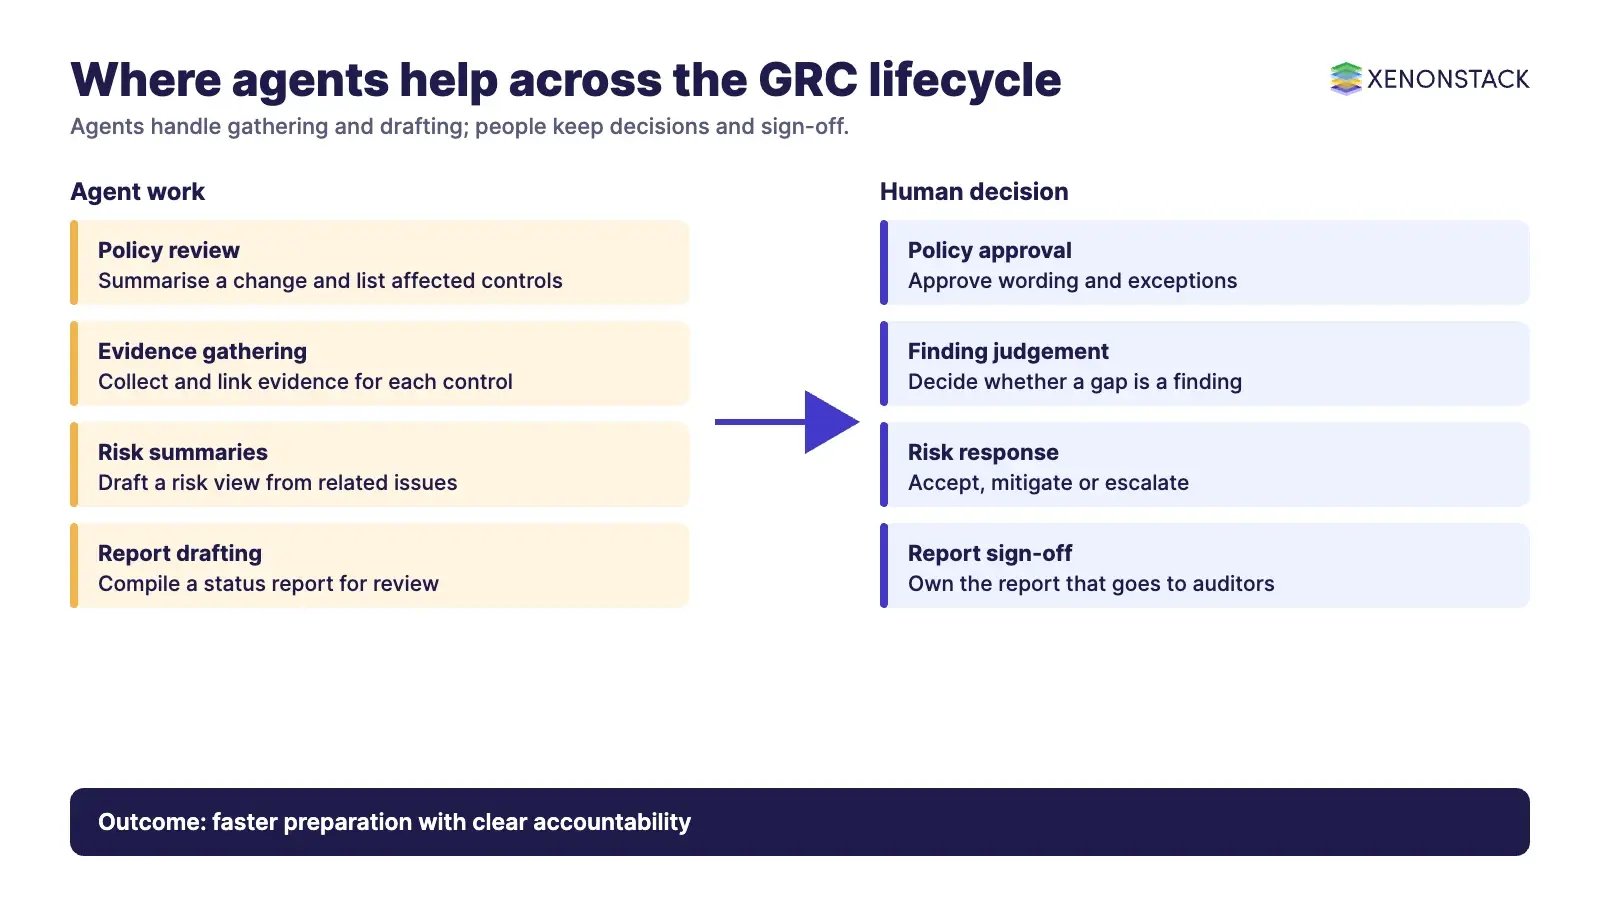
The areas below are the usual starting points. The right-hand column describes the type of help an agent can give; it is a design pattern, not a measured outcome.
| GRC area | Typical manual work | Where an agent can help | What a person still decides |
|---|---|---|---|
| Policy management | Drafting, reviewing and mapping policies to controls | Summarise a policy change, suggest affected controls, route reviews | Approving policy wording and exceptions |
| Compliance monitoring | Collecting evidence and testing controls against rules | Gather evidence from connected records, flag controls with gaps, prepare reports | Judging whether a gap is a finding |
| Risk assessment | Scoring risks and chasing owners for updates | Pull related incidents and issues, draft a risk summary, remind owners | Accepting, mitigating or escalating the risk |
| Third-party risk | Questionnaires and vendor reviews across a vendor lifecycle | Check responses for missing items, summarise vendor posture | Onboarding or offboarding a vendor |
| Audit and reporting | Assembling evidence and status reports | Compile evidence, draft a status summary, keep records linked | Signing off the report |
How do agents support policy, compliance reporting and risk work?
Policy management. Agents can read a new or changed policy, show which controls and owners it touches, and open review tasks. The policy itself stays under human approval.
Compliance reporting. Reporting is mostly assembly: finding the right evidence, checking it is current and putting it in a format an auditor accepts. An agent can do the gathering and drafting so reviewers spend time on judgement. This depends on controls being mapped to evidence sources in the first place.
Risk mitigation. Teams get more from risk data when it is monitored continuously, in the way that real-time monitoring turns a stream of events into action. Our guide to generative AI for risk management covers the wider method. On ServiceNow, the ServiceNow AI agents page says Workflow Data Fabric gives "real-time access to data from any source", which is the route by which outside risk signals can reach GRC records.
How does the architecture fit together?
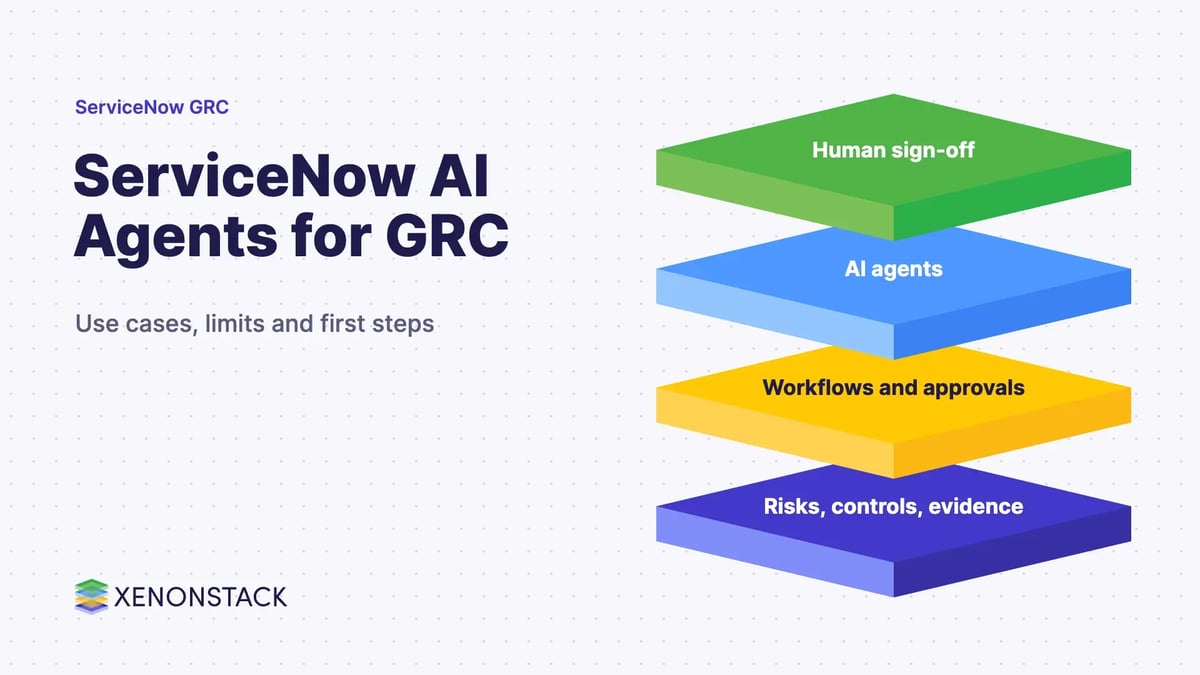
Think of four layers. Data and records sit at the bottom: the risk register, control library, policies and evidence. Workflows come next, moving each item through review and approval. Agents sit above them, working on those records through defined tools. A governance layer, which ServiceNow calls a control tower, lets administrators "manage, monitor, and optimize any AI". Each layer limits the one above it. An agent cannot be more reliable than the records it reads.
What are the limits of AI agents in GRC?
| Limit | Why it matters | What to do |
|---|---|---|
| Data quality | Stale controls, duplicate risks or missing owners lead to confident but wrong output | Clean the control library and ownership before enabling agents |
| Accountability | Regulators and auditors expect a named person to own each conclusion | Keep human approval on findings, exceptions and sign-off |
| Explainability | A summary with no trail to its source cannot be defended in an audit | Require every agent output to link to the records it used |
| Change management | Teams may distrust or ignore agent output | Start with one workflow and review results with its owners |
| Licensing and naming | Product names and entitlements change | Confirm the current scope with ServiceNow before design |
How do AI agents change governance itself?
When agents act in GRC workflows, the organisation has a second governance task: governing the agents. Each action needs a policy that says what the agent may do, the evidence behind it and a record of who approved it. XenonStack's ElixirData is its Context OS, a decision layer for the data, policy and context that agent decisions depend on. It is a separate layer from the ServiceNow platform and is worth considering where you want one view of policy across several agent platforms.
What should you do first?
- Pick one GRC workflow with a clear owner, such as evidence collection for one control family.
- Check that the controls, risks and owners in that workflow are current and linked.
- Define what the agent may read, draft and change, and what needs human approval.
- Run it in draft mode, and compare agent output with what your team produced by hand.
- Record the lessons and widen scope only when reviewers trust the output.
To map one decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
Can ServiceNow AI agents replace GRC analysts?
No. They can take on gathering, drafting and routing work, but findings, exceptions and sign-off need a named person. The aim is to give analysts more time for judgement.
What is the difference between GRC automation and AI agents?
Classic GRC automation follows fixed rules and workflows. An agent can plan a short sequence of steps, call tools and adapt to the case, within limits you set, and it still works inside workflow and approval rules.
Do AI agents need clean data to work in GRC?
Yes. Agents read the risk register, control library and evidence records. If those are stale or duplicated, the output will be wrong, however good the model is.
Which ServiceNow pages describe these capabilities?
The ServiceNow GRC page and the ServiceNow AI agents page describe the platform. Product names and packaging change, so confirm current details with ServiceNow.
How should a team start with agents in GRC?
Start with one workflow, define what the agent may do and where a person approves, run it in draft mode and expand only after reviewing results.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE