Key takeaway
- Read what the CVE records say about the Zimbra Calendar XSS flaw and the Microsoft Office RCE flaw, how they compare, and how to check and fix exposure.
CVE-2022-24682 is a cross-site scripting flaw in the Calendar feature of Zimbra Collaboration Suite, and CVE-2017-8570 is a remote code execution flaw in the way Microsoft Office handles objects in memory. Both depend on a user acting on crafted content: one in Zimbra's Calendar feature, the other in a vulnerable Office build.
This page is for security, IT and messaging teams that still run Zimbra or older Office builds. It explains what each CVE record says, how the two compare, how to check exposure, and how AI agents can help with the triage. For related write-ups, see our security intelligence archive.
What is CVE-2022-24682 in Zimbra?
The National Vulnerability Database entry quotes the CVE record: "An issue was discovered in the Calendar feature in Zimbra Collaboration Suite 8.8.x before 8.8.15 patch 30 (update 1)." The flaw lets an attacker place HTML containing executable JavaScript inside element attributes, and the application then renders it without escaping it. NVD lists the weakness as CWE-116, improper encoding or escaping of output.
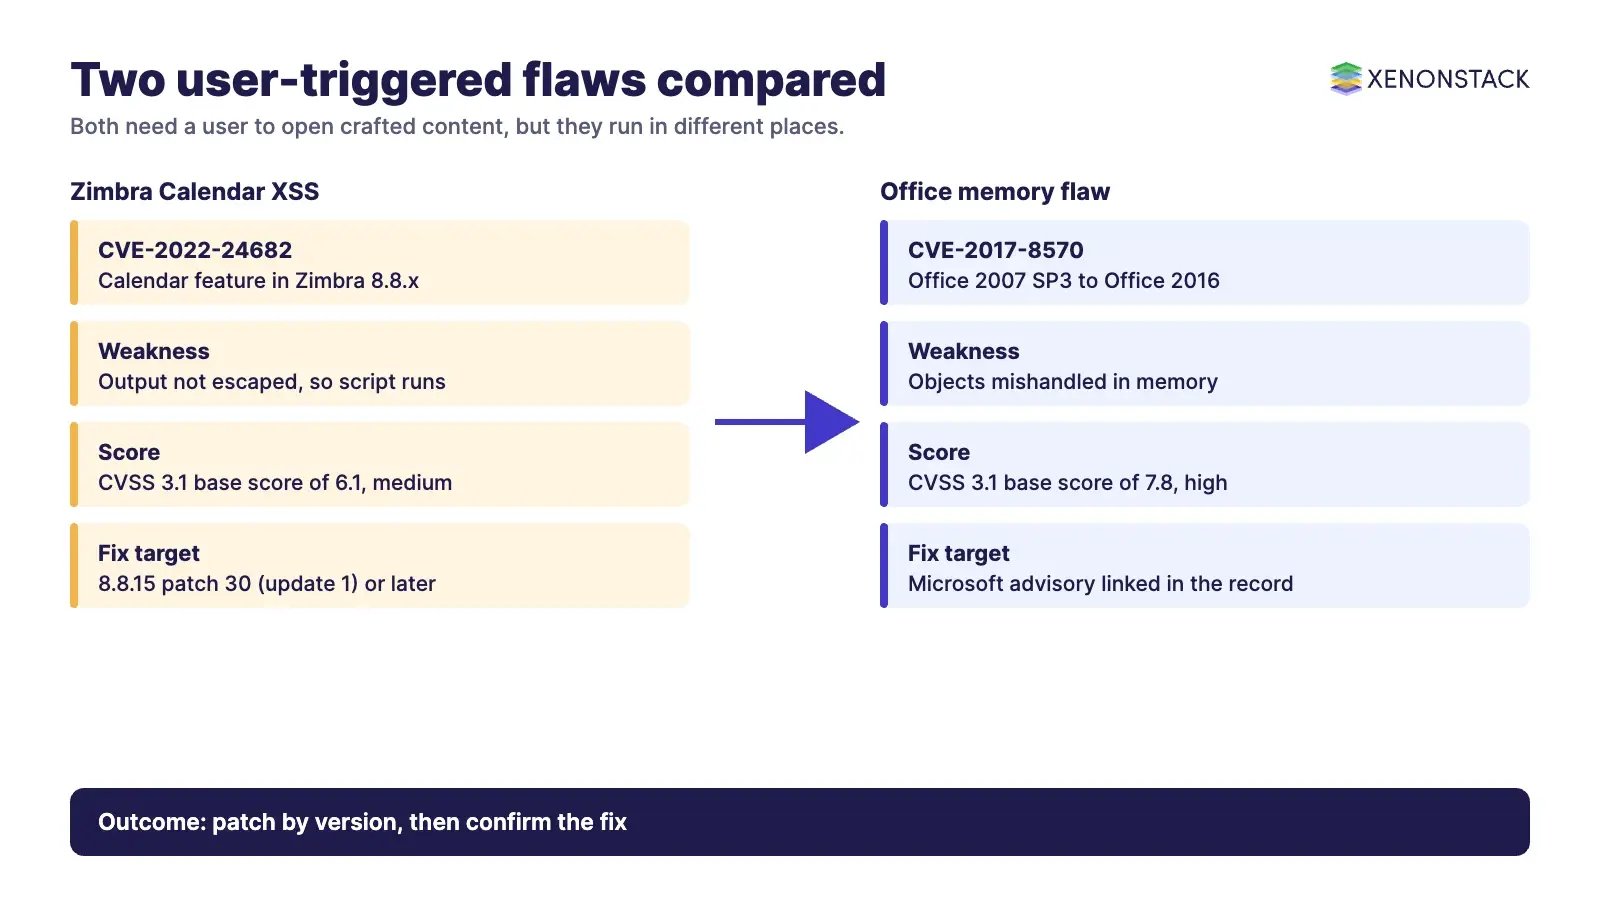
That is cross-site scripting: script from an attacker runs inside the victim's logged-in session. NVD records a CVSS 3.1 base score of 6.1 (medium) with the vector AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N. In plain terms, it can be attacked over the network, needs no privileges and no special conditions, but needs a user to act, and it can affect data beyond the vulnerable component.
NVD shows it was published on 8 February 2022. It also shows the flaw in the Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities catalog, added on 25 February 2022 with a due date of 11 March 2022 and the required action "Apply updates per vendor instructions."
What is CVE-2017-8570 in Microsoft Office?
The CVE record for CVE-2017-8570 says that Microsoft Office allows a remote code execution vulnerability because of the way it handles objects in memory. It states that this ID is unique from CVE-2017-0243, so the two should not be confused. The record lists Microsoft Office 2007 SP3, 2010 SP2, 2013 SP1 and 2016 as affected, and was published on 11 July 2017.
The record gives a CVSS 3.1 base score of 7.8 (high) with the vector AV:L/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H. The attack vector is local and user interaction is required: the user has to open a crafted file in a vulnerable Office version. The record links Microsoft's own advisory for this CVE and a CISA Known Exploited Vulnerabilities entry, so use those pages for fix details rather than relying on summaries.
How do the two vulnerabilities compare?
| Question | CVE-2022-24682 | CVE-2017-8570 |
|---|---|---|
| Product | Zimbra Collaboration Suite, Calendar feature | Microsoft Office 2007 SP3, 2010 SP2, 2013 SP1, 2016 |
| Type | Cross-site scripting (CWE-116 in NVD) | Remote code execution through memory handling |
| CVSS 3.1 base score | 6.1 (medium) | 7.8 (high) |
| What the user must do | Interact with crafted content (user interaction required) | Open a crafted file in a vulnerable Office build |
| Where to find the fix | Zimbra 8.8.15 patch 30 (update 1) or later, per the description | Microsoft advisory linked from the CVE record |
A medium score does not mean low priority. A CVSS score describes the flaw in isolation. Whether a flaw is being exploited, as the CISA catalog entry shows for CVE-2022-24682, matters at least as much when you rank work.
How do you check and reduce exposure?
Start from version, not from headlines. For Zimbra, confirm whether any 8.8.x server is older than 8.8.15 patch 30 (update 1). For Office, list which installed builds fall under the products named in the record. Zimbra and Microsoft have both released many updates since these records were written, so check each vendor's current advisories before you decide what the right target version is.
Then apply the vendor update. CISA's required action for the Zimbra entry is to apply updates per vendor instructions, and that applies equally to Office. Where you cannot patch quickly, reduce the ways in: limit who can reach the webmail interface, and stop users opening files from unknown senders in an affected Office version. Our cyber security services page explains how XenonStack approaches detection and response.
How do AI agents change vulnerability response?
The slow part of a CVE is rarely reading the record. It is finding which of your systems it touches, checking whether a patch is available and who owns the system, and recording the decision. An AI agent can do the matching: read the CVE record and vendor advisory, compare them against an asset inventory, and draft a ticket for the owner.
The decision should stay with a person, and the agent should cite the pages it read, since CVE records and vendor guidance change. XenonStack's ElixirClaw, the AI agents computing platform, is where we build agent workflows of this kind.
What should you do first?
- List every Zimbra 8.8.x server and every Office 2007 to 2016 install.
- Compare versions with the CVE records and each vendor's current advisory.
- Patch the systems that are exposed and are reachable from the internet or by email.
- Record who approved each exception and the date it expires.
- Re-check the CISA Known Exploited Vulnerabilities catalog on a regular schedule.
To map one decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What does CVE-2022-24682 allow an attacker to do?
It allows HTML containing executable JavaScript to be injected into element attributes in the Zimbra Calendar feature, which is then rendered without escaping. The script runs in the victim's session.
Which Zimbra versions does CVE-2022-24682 affect?
The record describes Zimbra Collaboration Suite 8.8.x before 8.8.15 patch 30 (update 1). Check Zimbra's current advisories for the version you should run today.
Is CVE-2017-8570 the same as CVE-2017-0243?
No. The CVE record states that CVE-2017-8570 is unique from CVE-2017-0243.
Why is a medium-scored CVE still urgent?
CISA lists CVE-2022-24682 in its Known Exploited Vulnerabilities catalog, so evidence of exploitation exists even though the CVSS score is 6.1. Use both the score and the exploitation status to set priority.
How can AI agents help with CVE triage?
They can match a CVE record and vendor advisory against your asset inventory and draft tickets with sources cited. A person should still approve the patching decision.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE