Key takeaway
- Platform Security Architecture explained: the four PSA stages, PSA Certified levels, EU CRA and RED rules, and the tools that secure IoT platforms in 2026.
Platform Security Architecture (PSA) is a framework, created by Arm, for building security into connected devices from the chip upwards. It breaks the work into four steps: analyse threats, architect the protections, implement them with trusted firmware and standard APIs, and certify the result through PSA Certified, an independent scheme that evaluates the hardware Root of Trust and the software and devices built on it.
In 2026 PSA matters for a different reason than when it launched. Governance of PSA Certified has moved to GlobalPlatform, and connected products sold in the EU now face cybersecurity rules under the Radio Equipment Directive and, from 2027, the Cyber Resilience Act. This guide explains the framework, the certification levels, how they map to regulation, and where wider platform security tools fit for enterprise leaders and architects.
What is platform security architecture?
The term is used in two ways. In general, platform security is the set of designs, controls and processes that protect a computing platform's hardware, firmware, software, network and services as one system rather than application by application. More specifically, Platform Security Architecture is the Arm-originated framework and certification scheme for connected devices. This guide covers both, starting from the device foundation.
| Term | What it means | Who maintains it |
|---|---|---|
| Platform Security Architecture (PSA) | A framework for designing security into connected devices, from threat model to certification | Created by Arm; the PSA Certified scheme is now run by GlobalPlatform |
| Root of Trust (RoT) | The hardware and firmware that the rest of the device relies on for secure boot, keys, cryptography and attestation | Chip vendors, evaluated under PSA Certified |
| PSA Certified | Independent security evaluation of chips, system software and devices at defined assurance levels | GlobalPlatform working group, chaired by Arm |
| PSA Certified APIs | Standard interfaces for cryptography, secure storage, attestation and firmware update | GlobalPlatform, since June 2026 |
| Trusted Firmware-M (TF-M) | Open source reference implementation of the secure processing environment for Armv8-M and Armv8.1-M processors | Trusted Firmware project |
What has changed in platform security since 2024?
Leaders reviewing an older platform security plan should check these changes first. Several tool names in older guides are also out of date.
| Change | What it means | Current status |
|---|---|---|
| PSA Certified governance | GlobalPlatform took over governance of the scheme Arm and partners launched in 2019 | Since September 2025; brand, levels and evaluation methodology unchanged. More than 250 products certified at the time of the move |
| PSA Certified APIs | GlobalPlatform now governs the APIs for cryptography, secure storage, attestation and firmware update, with a compliance test suite | Announced June 2026 |
| Level 4 iSE/SE | A higher level for chips using an integrated secure enclave or external secure element | Available alongside Levels 1 to 3 |
| EU Radio Equipment Directive | Regulation (EU) 2022/30 adds cybersecurity, privacy and fraud-protection requirements for internet-connected radio equipment | Applies from 1 August 2025; EN 18031-1, -2 and -3 are the recognised harmonised standards, used voluntarily |
| EU Cyber Resilience Act | The CRA sets cybersecurity requirements for products with digital elements across their lifecycle | In force 10 December 2024; vulnerability reporting from 11 September 2026; main obligations from 11 December 2027 |
| Tool owners and names | Several tools in older lists changed owner or name | Black Duck became independent of Synopsys in October 2024; Fortify is OpenText Fortify SAST; AppScan is HCL AppScan; Klocwork is sold by Perforce; Arxan is now Digital.ai Application Security; ZAP is ZAP by Checkmarx |
What are the four stages of Platform Security Architecture?
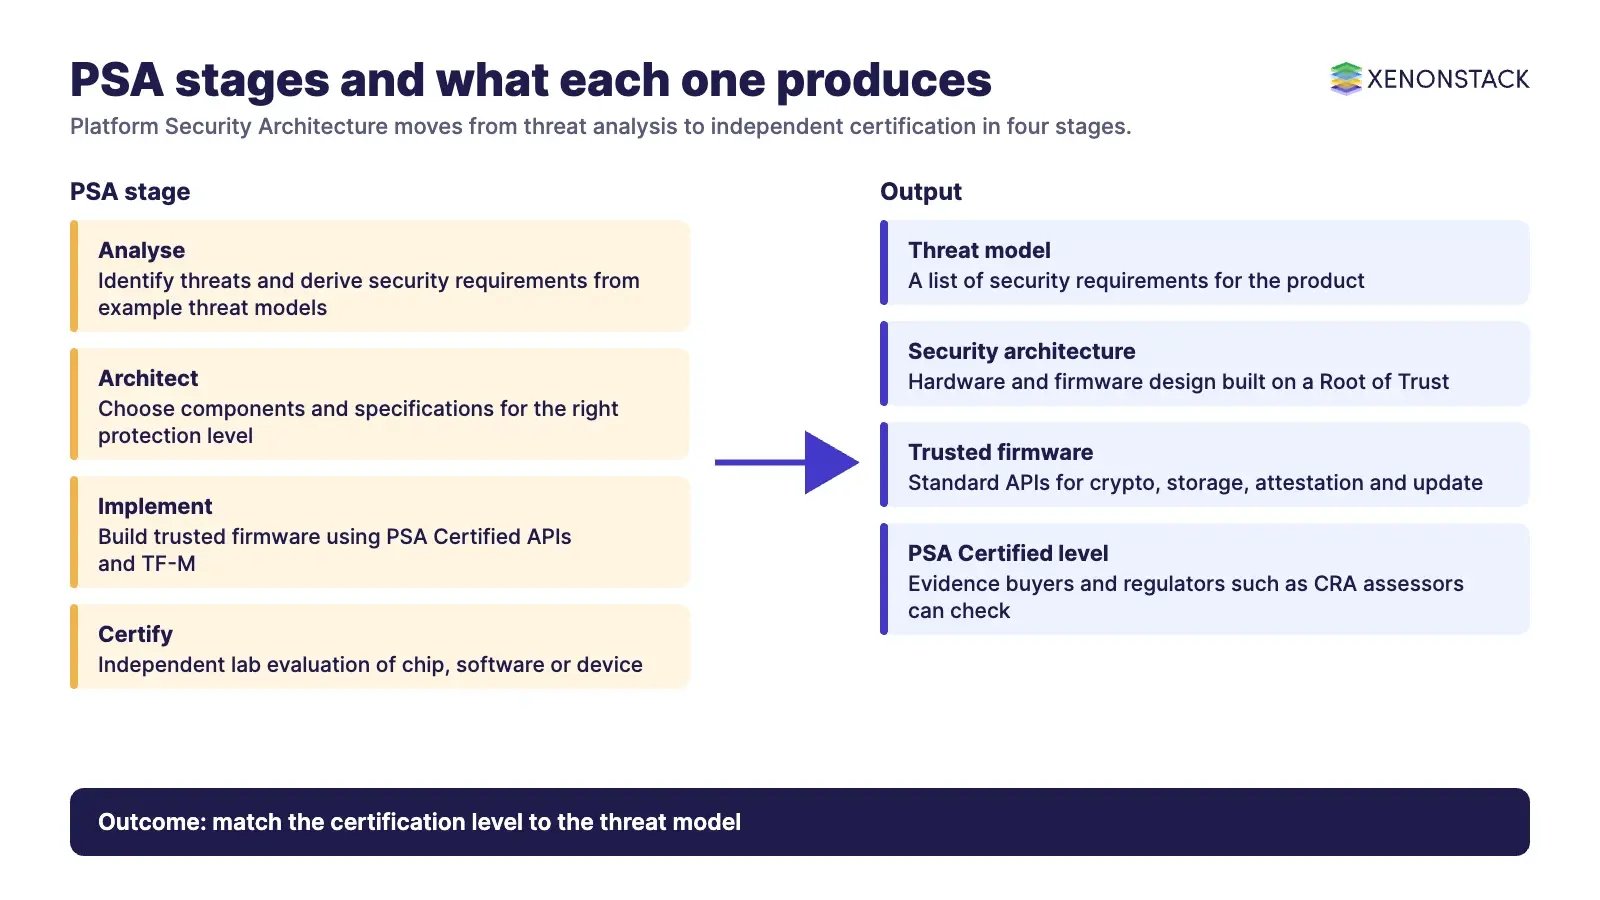
PSA divides security design into four stages. Each produces something the next stage depends on, which is why skipping the threat model usually leads to over- or under-engineered devices.
| Stage | What you do | Output |
|---|---|---|
| Analyse | Identify the threats that could compromise the device and derive security requirements; PSA Certified provides free, editable example threat models | A threat model and a list of security requirements |
| Architect | Use the requirements to choose components and specifications that give the right level of protection | A hardware and firmware security architecture built on a Root of Trust |
| Implement | Build trusted components and firmware, using high-level APIs to reach the hardware Root of Trust; TF-M offers a reference secure processing environment for Armv8-M and Armv8.1-M | Firmware and software that use standard security APIs |
| Certify | Have the chip, system software or device independently evaluated by a lab | A PSA Certified level that buyers and regulators can check |
The same discipline applies to software that runs on the platform. Our guide to application security best practices covers the controls above the firmware layer.
Which PSA Certified level fits your product?
PSA Certified defines levels of assurance for the Root of Trust and the products built on it. Higher levels need lab vulnerability assessment and suit chips that protect higher-value assets. The PSA Certified site listed 318 certifications from 124 companies when read on 11 November 2026.
| Level | What it shows | How it is assessed | When it fits |
|---|---|---|---|
| Level 1 | Good security principles have been applied | Questionnaire, reviewed by an evaluation lab | Device, software and chip vendors starting out, or low-risk products |
| Level 2 | The PSA Root of Trust resists software attacks | Lab vulnerability assessment | Chips for connected products that hold credentials or personal data |
| Level 3 | The PSA Root of Trust resists substantial hardware and software attacks | Lab vulnerability assessment | Products exposed to physical access or higher-value targets |
| Level 4 iSE/SE | A secure enclave or secure element with high robustness to physical and software attacks | Lab vulnerability assessment | Payment, identity and other high-assurance key storage |
| Level 2 or 3 RoT Component | An IP component meets a subset of the PSA Root of Trust requirements | Lab evaluation of the component | IP vendors supplying security blocks to chip makers |
Levels 2 and 3 also have Secure Element add-ons for solutions that give substantial physical protection to cryptographic keys and operations.
How does PSA map to regulation and standards?
Certification does not replace a legal obligation, but it gives manufacturers reusable evidence. GlobalPlatform states that PSA Certified Levels 2 and 3 are based on SESIP, the Security Evaluation Standard for IoT Platforms, which it maintains as European standard EN 17927, and that SESIP helps manufacturers demonstrate conformance with regulations such as the Cyber Resilience Act.
| Rule or standard | What it requires | How PSA evidence helps |
|---|---|---|
| EU Cyber Resilience Act | Security by design and lifecycle vulnerability handling for products with digital elements | Threat models, a certified Root of Trust and secure update support part of the technical file |
| RED delegated regulation (EU) 2022/30 | Network protection, privacy safeguards and fraud protection for internet-connected radio equipment, from 1 August 2025 | Secure storage, cryptography and update mechanisms support EN 18031 assessments |
| SESIP (EN 17927) | A common methodology for evaluating IoT platform security, designed for reuse | PSA Certified Levels 2 and 3 are built on it, so platform results can be reused by device makers |
Which security tools protect the platform beyond the chip?
A certified chip does not secure the application, the cloud service or the supply chain around it. Enterprises still need one tool per job across the software layers. The examples use current product names.
| Layer | Job | Current examples | When it fits |
|---|---|---|---|
| Firmware and device | Secure boot, isolation, cryptography and attestation | TF-M, PSA Certified APIs, a certified Root of Trust | Any connected device you design or specify |
| Source code | Static analysis (SAST) against CWE, CERT and OWASP rules | Klocwork, OpenText Fortify SAST, HCL AppScan, Veracode | All embedded and application code |
| Open source and supply chain | Find vulnerable or unlicensed components and list them in an SBOM | Black Duck, Veracode | Every build, and as evidence for the CRA |
| Running applications and APIs | Dynamic testing and penetration testing | Burp Suite, ZAP by Checkmarx, HCL AppScan | Web applications, device portals and public APIs |
| Mobile and client apps | Obfuscation, anti-tamper and runtime self-protection | Digital.ai Application Security, Thales Imperva Runtime Protection | Apps that hold keys or control devices |
| Operations | Log collection, detection and response | SIEM and XDR platforms | Production fleets and cloud back ends |
These checks belong in the delivery pipeline rather than at the end of a project; our guide to DevSecOps shows where each gate runs, and penetration testing remains the final check before major releases. For operations, our overview of Microsoft Sentinel shows how a cloud SIEM gathers these signals, and MetaSecure AI is powered by modular AI agents and protocol-driven automation for round-the-clock coverage.
How should enterprises govern platform security across devices, cloud and AI agents?
- Set a minimum level in procurement: specify the PSA Certified level, or equivalent evidence, for each class of device you buy or build.
- Own the update path: secure firmware update, signed artefacts and a published vulnerability disclosure route are now regulatory expectations, not extras.
- Keep evidence in one place: threat models, certificates, SBOMs and test results per product version, ready for CRA and RED assessments.
- Treat device data as untrusted until attested: use attestation from the Root of Trust before cloud services act on device data.
- Govern automated actions: when AI agents triage alerts or push configuration to fleets, give them scoped permissions and keep human approval for high-impact changes.
For physical AI and edge fleets, NexaStack is an agentic operating platform for physical AI that runs across on-premises, cloud and hybrid environments. Where agents act on security decisions, AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
How should an enterprise adopt Platform Security Architecture?
- Inventory connected products: list devices, chips, firmware owners and the markets each is sold into.
- Map obligations: mark which products fall under the RED delegated regulation now and the Cyber Resilience Act from 2027.
- Write or adopt a threat model: start from the PSA Certified example threat models and adapt them to each product.
- Choose the Root of Trust: prefer chips already certified at the level your threat model needs.
- Implement with standard APIs: use the PSA Certified APIs and a reference implementation such as TF-M where your architecture supports it.
- Certify and keep evidence: certify where buyers or regulators expect it, and keep test results and certificates with each release.
What are the trade-offs, and when is PSA not the right fit?
- Cost and time: higher levels need lab evaluation, and labs set their own prices, so get several quotes and match the level to the risk.
- Architecture fit: TF-M targets Armv8-M and Armv8.1-M or dual-core platforms; other architectures need their own secure environment, although the PSA Certified APIs are being kept architecture-neutral.
- Scope: PSA certifies the device foundation, not your cloud services, mobile apps or business processes. Those need their own controls.
- Not a compliance shortcut: certification supports, but does not equal, conformity with the Cyber Resilience Act or the RED requirements.
- When to hold back: for enterprise IT servers and cloud workloads, use cloud and server security baselines instead; PSA is designed for connected devices and their chips.
To map the device, update and access decisions your platforms and agents make, and the policy each depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about Platform Security Architecture
What is Platform Security Architecture (PSA)?
Platform Security Architecture is a security framework that Arm created for connected devices. It splits security work into four steps (analyse, architect, implement, certify) and is backed by PSA Certified, an independent evaluation scheme that rates the Root of Trust in a chip, plus the software and devices built on it.
Who runs PSA Certified now?
GlobalPlatform. Arm and its partners launched PSA Certified in 2019, and governance moved to a GlobalPlatform working group in September 2025. GlobalPlatform said the brand, certification levels and evaluation methodology would stay the same. In June 2026 it also took on governance of the PSA Certified APIs.
Which PSA Certified level do I need?
Level 1 shows that good security principles were applied, through a questionnaire reviewed by a lab. Level 2 adds lab testing that the PSA Root of Trust resists software attacks, Level 3 covers substantial hardware and software attacks, and Level 4 iSE/SE covers a secure enclave or secure element with high robustness to physical and software attacks. Choose by the value of what the device protects and what your buyers or regulators ask for.
Does PSA Certified help with the EU Cyber Resilience Act?
It can provide evidence. PSA Certified Levels 2 and 3 are based on SESIP, which GlobalPlatform maintains as the European standard EN 17927, and GlobalPlatform states that SESIP helps manufacturers show conformance with regulations such as the Cyber Resilience Act. Certification is not a substitute for the Act's own requirements, which apply in full from 11 December 2027.
Is platform security only about chips and firmware?
No. PSA covers the device foundation: the Root of Trust, secure boot, firmware update, cryptography and attestation. Enterprises still need application security testing, supply chain checks, monitoring and governance for the cloud services and software that run on and around those devices.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE