Key takeaway
- GDPR compliance checklist for businesses: the six principles, roles, breach notification, rights, and how AI agents handling personal data are affected.
GDPR, the General Data Protection Regulation, is the European Union law that sets rules for how organisations collect, use, store and protect personal data about people in the EU. It applies to organisations in the EU and to organisations elsewhere that offer goods or services to people in the EU.
This guide is for compliance, security and data leaders who need a working GDPR checklist rather than the legal text. It covers the principles, the roles, a practical checklist, breach notification, and how AI agents that touch personal data change the work. It is general information, not legal advice: confirm requirements against the regulation and with counsel.
What does GDPR require of organisations?
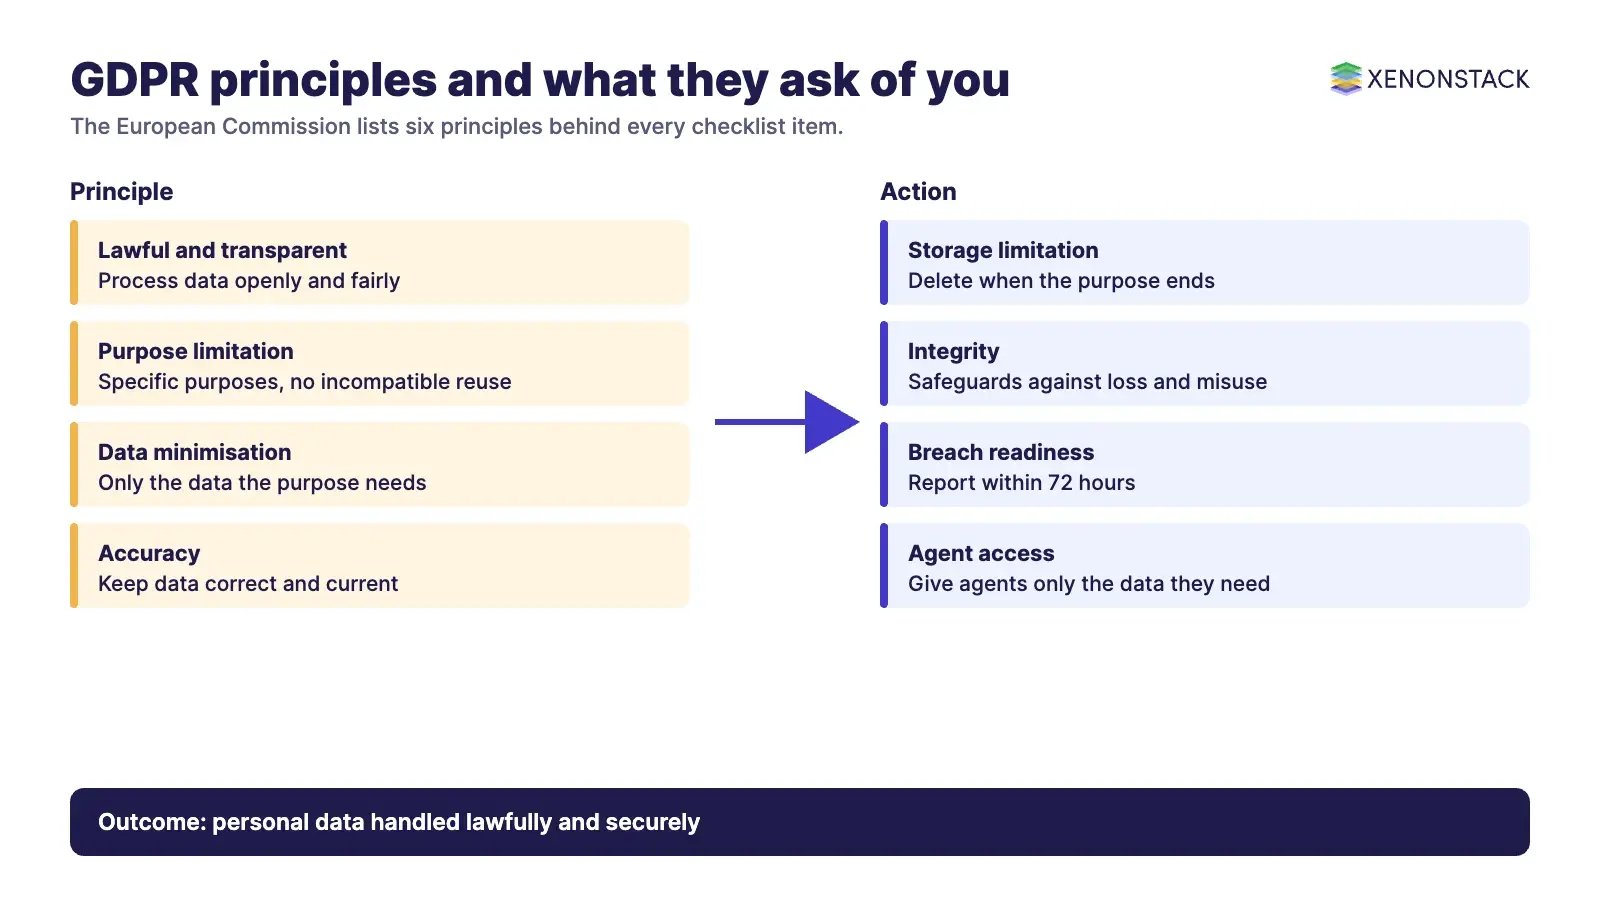
The European Commission says the type and amount of personal data an organisation may process "depends on the reason for processing it". Its overview of the principles lists six: lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; and integrity and confidentiality. Every item on a compliance checklist traces back to one of them. Read the Commission's overview of the GDPR principles for the plain-language version.
| Principle | What it means for your team |
|---|---|
| Lawfulness, fairness and transparency | Process data lawfully and openly, and fairly for the people concerned |
| Purpose limitation | Have specific purposes, tell people what they are when you collect data, and do not reuse data for incompatible purposes |
| Data minimisation | Collect and process only the data needed for the stated purpose |
| Accuracy | Keep data accurate and up to date, and correct it when it is not |
| Storage limitation | Keep data no longer than the purpose needs |
| Integrity and confidentiality | Use technical and organisational safeguards against unauthorised or unlawful processing, loss, destruction or damage |
What data does GDPR protect?
GDPR covers personal data: information relating to an identifiable person. Basic identity details such as name, address and identification numbers are the obvious cases. Online identifiers such as location data, IP addresses and cookie data can also identify people. Some categories, including health, genetic and biometric data, political opinions and sexual orientation, need extra care, so check the regulation's rules on special categories before processing them.
Who is responsible for GDPR compliance?
- Data controller: decides why and how personal data is processed, and is responsible for making sure outside contractors comply.
- Data processor: processes personal data on the controller's behalf, which can be an internal team or an external provider.
- Data protection officer (DPO): an oversight role that some organisations must appoint, for example when they process large amounts of personal data or special categories. Check the regulation to see whether it applies to you.
What does a GDPR compliance checklist include?
| Checklist item | What to do |
|---|---|
| Consent | Where you rely on consent, make it clear and in plain language, not buried in complex terms |
| Individual rights | Be able to give people access to their data, and handle requests to erase it or move it to another service |
| Privacy by design | Build safeguards into systems from the start |
| Breach readiness | Have a process to detect, assess and report breaches on time |
| Records and agreements | Document your processing and have data processing agreements with processors |
| Oversight | Decide whether you need a DPO and who owns compliance |
Security practice supports several of these items: see continuous security with DevSecOps tools for building security into each step of delivery, and customer data platform benefits for how a unified customer database can help you see where personal data sits.
What are the GDPR breach notification rules?
The data breach guidance on the European Commission website says an organisation must report a breach to the supervisory authority "without undue delay, and at the latest within 72 hours after having become aware of the breach". If the breach poses a high risk to the people affected, they should also be informed. Notifying individuals is not required if effective technical and organisational protection measures were in place, or if other measures mean the risk is no longer likely to materialise. Read the full breach guidance before you write your own procedure.
Other regimes have their own rules. Healthcare organisations in the United States should read our HIPAA compliance checklist, and for wider threats see botnet detection and prevention techniques and artificial intelligence in cyber security.
How do AI agents change GDPR compliance?
Agents that read customer records, draft replies or trigger actions are processing personal data, so the same principles apply to them. Purpose limitation and data minimisation mean an agent should only see the data its task needs. Accuracy and transparency mean you should be able to say what data an agent used and why. Agents can also support compliance work: locating where personal data is stored, preparing responses to access requests for human review, and flagging unusual access. ElixirData is XenonStack's Context OS, built to hold the data and policy context that governed agent decisions depend on. XenonStack's cyber security services and solutions cover the security side.
What should you do first?
- List the personal data you hold, where it sits and why you collected it.
- Check each purpose against the six principles and remove data you do not need.
- Write down who is controller and processor for each system, including AI agents.
- Draft and rehearse a breach procedure that meets the 72 hour reporting window.
- Review consent wording and your process for access and erasure requests.
For questions about how XenonStack handles personal data, read the privacy statement on xenonstack.com or get in touch.
To map one decision your agents make with personal data, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is GDPR?
GDPR is the General Data Protection Regulation, a European Union law that sets rules for how organisations collect, use, store and protect personal data about people in the EU.
Who must comply with GDPR?
Organisations in the EU must comply, as must organisations outside the EU that offer goods or services to people in the EU.
What are the GDPR principles?
The European Commission lists six: lawfulness, fairness and transparency; purpose limitation; data minimisation; accuracy; storage limitation; and integrity and confidentiality.
How quickly must a data breach be reported?
Organisations must report a breach to the supervisory authority without undue delay and at the latest within 72 hours of becoming aware of it. People affected must also be told if the breach poses a high risk to them.
Does GDPR apply to AI agents?
Yes, where an agent processes personal data. The same principles apply, so agents should only access the data their task needs, and you should be able to explain what data they used.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE