Key takeaway
- What a security operations center (SOC) does, how to structure one, which tools it needs and how to build it, using NIST CSF 2.0 and MITRE guidance.
A security operations center (SOC) is the team, process and tooling that watches an organisation's systems for signs of attack, decides which signals matter, and leads the response. It is how a company turns a flood of logs and alerts into a small number of decisions someone owns.
This guide is for CISOs, CIOs and architects deciding how to build, buy or improve a SOC. It covers what a SOC does, which operating model fits, what tools it needs, how it links to NIST guidance, and where AI agents fit when humans stay in control. For the automation side, read SOC systems and the future of cybersecurity.
What is a security operations center?
A security operations center is a function that continuously monitors and assesses an organisation's security posture and works with incident response teams so that problems are handled as soon as they are found. It looks at networks, servers, endpoints, databases, applications, websites and cloud services for unusual behaviour that could signal a compromise.
NIST lists the SOC as a defined term in its glossary and cites several of its own publications for it, including SP 800-53 Rev. 5 and SP 800-61 Rev. 3 (NIST glossary entry, read 13 November 2026). Because each NIST definition depends on its source document, read the wording in the publication you plan to cite.
How does a SOC work from alert to response?
A SOC works as a loop: collect data, detect suspicious activity, triage it, respond, then learn. The NIST Cybersecurity Framework 2.0 (published 26 February 2024) gives the same loop its language. It defines Detect as "possible cybersecurity attacks and compromises are found and analyzed", Respond as "actions regarding a detected cybersecurity incident are taken", and Recover as "assets and operations affected by a cybersecurity incident are restored" (NIST CSWP 29).
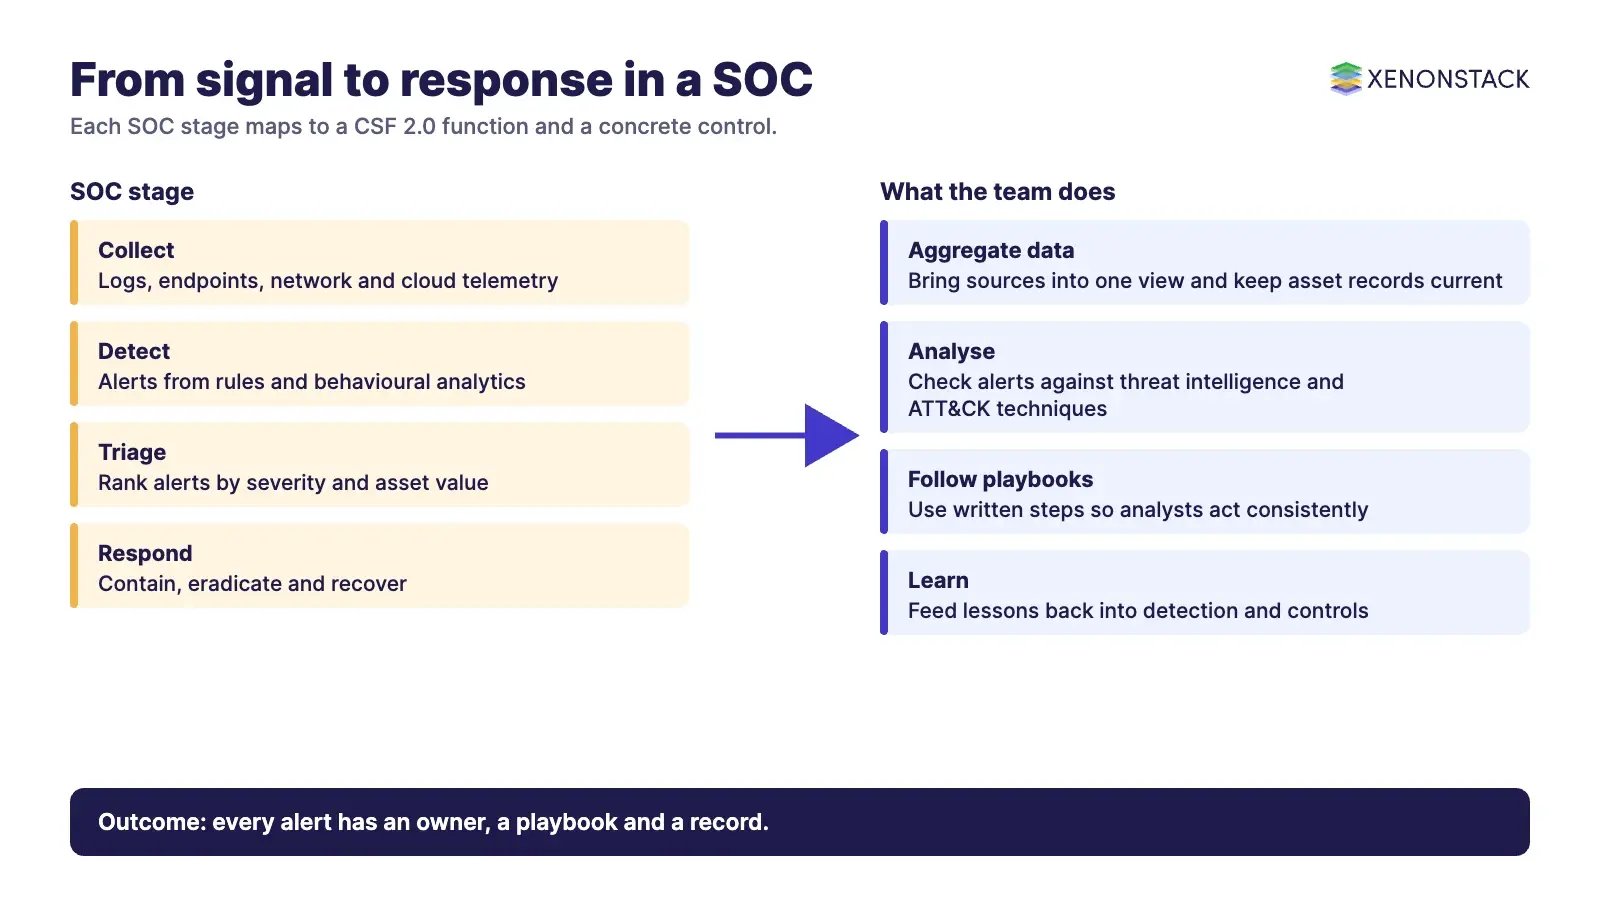
| SOC stage | What the team does | CSF 2.0 function |
|---|---|---|
| Collect and aggregate | Bring logs and telemetry from across the estate into one view and keep asset records current | Identify, Detect |
| Detect | Raise alerts from rules, analytics and threat intelligence | Detect |
| Triage | Rank alerts by severity and asset value, discard false positives | Detect |
| Respond | Contain and remove the threat, following written playbooks | Respond |
| Recover and learn | Restore systems, then improve detection from what the incident showed | Recover |
NIST SP 800-61 Rev. 3, published in April 2025, replaces Rev. 2 from 2012. It is written as a CSF 2.0 Community Profile, so incident response is treated as part of overall cybersecurity risk management and not as a separate activity (NIST SP 800-61 Rev. 3).
What does a SOC do day to day?
- Know the assets: keep an accurate view of hardware, software and data so threats and weak points are spotted early.
- Monitor continuously: watch for malicious activity around the clock so damage is limited before it spreads.
- Rank alerts by severity: analysts decide which alerts are most critical and handle those first.
- Respond and recover: contain the incident, restore data and systems, apply updates and confirm backups.
- Support compliance: collect the evidence and reports that audits and internal policies require.
- Use behavioural baselines: compare activity with normal patterns to find unusual behaviour. See behavioural analytics for SOC automation.
- Improve continuously: use lessons from each incident to tighten controls and detection.
How does compliance fit into SOC work?
A SOC is often the team that produces the evidence auditors ask for: what was monitored, what was detected, what was done and when. It does this by aligning its policies with recognised frameworks such as the NIST CSF, by reporting on incidents, and by supporting access controls under a zero trust security architecture. Regular audits then check that analysts follow the written policies. Where a regulation applies to you, confirm the exact obligations on the regulator's official page.
Do not confuse a SOC with SOC 2. SOC 2 is an assurance report about a service provider's controls, not a security team. For that topic, see SOC 2 compliance and best practices.
What challenges do SOCs face?
- Alert volume: more events than analysts can review, so unclear priorities hide the alerts that matter.
- Threat intelligence: data has to be relevant, timely and joined to your own telemetry to be useful. See threat intelligence for security monitoring and incident response.
- Skills: experienced analysts are hard to hire and keep, which slows triage and response.
- Vulnerability management: without automated scanning and clear ownership, fixes take longer and exposure stays open.
- Breach response: the team must find the source, contain the attack and start recovery in a coordinated way.
Which SOC model should you choose?
MITRE's guide to running a SOC covers choosing a structure and set of functions that fit the organisation, along with staffing, data and metrics (11 Strategies of a World-Class Cybersecurity Operations Center, read 13 November 2026). The models below are the ones organisations commonly choose between.
| Model | What it is | When it fits |
|---|---|---|
| Dedicated (self-managed) | In-house team running its own facility and tools | Large estates with strict control needs |
| Distributed (co-managed) | In-house team working with an external provider | You own detection logic but need extra coverage |
| Managed SOC or MDR | Provider runs monitoring and response | Small teams without 24/7 staffing |
| Command SOC | Central team that supplies threat intelligence and guidance to other SOCs | Groups with several regional teams |
| Fusion centre | Security joined with IT, DevOps and other teams | When incidents cross team boundaries |
| Virtual SOC | No dedicated facility; staff work remotely on cloud tooling | Distributed teams |
Which model is right depends on your risk, budget, regulation and how many analysts you can hire and keep. A hybrid approach has made SOC capability available to mid-sized firms that once assumed it was only for large enterprises.
What tools does a SOC need?
Buy by capability, not brand. Whichever tools you choose, keep them patched, configure them for the threats that matter to you, test them against simulated incidents, and integrate them so they share data.
| Capability | What it is for |
|---|---|
| Log and event aggregation (SIEM) | One searchable view of events across the estate |
| Endpoint and network detection | Spotting malicious activity on devices and in traffic, including intrusion detection |
| Vulnerability scanning | Finding exposed or unpatched assets, especially internet-facing ones |
| Threat intelligence | Context on adversary behaviour; MITRE ATT&CK is an open knowledge base of adversary tactics and techniques based on real-world observations (MITRE) |
| Digital forensics | Capturing and examining evidence without altering the original |
| Orchestration and playbooks | Automating repeatable response steps |
Playbooks are written procedures for common attack scenarios. They give analysts a consistent structure and improve both response time and the quality of investigations.
How do you build a security operations center?
- Assess risk: use a formal risk assessment to find gaps in detection and response coverage and to guide investment.
- Define mission and model: agree what the SOC protects, who it reports to and which model fits.
- Collect and combine data: instrument the assets that matter and bring the data together to improve detection and situational awareness.
- Prioritise: set clear rules for triage so critical alerts are not buried.
- Write playbooks: start with the incidents you see most often.
- Automate carefully: automate data collection and routine response first, so analysts can focus on harder cases.
- Measure and report: show the SOC's value with metrics such as mean time to detect.
Teams that already run SOC automation for IoT security or human-in-the-loop SOC automation can reuse the same sequence: pilot on one alert type, review, then widen.
What are the benefits and trade-offs of a SOC?
| Benefit | Trade-off or when to think twice |
|---|---|
| Faster, more consistent incident response | Round-the-clock coverage needs people, shifts or a provider |
| Shorter gap between compromise and detection | Poorly tuned tools create alert fatigue |
| One view of security activity and consolidated assets | Integration and data costs rise with every source |
| Evidence for audits and clearer accountability | A SOC without owners and playbooks only produces reports |
If you are small, a managed or co-managed service may serve you better than an in-house build. If you are large, a dedicated team still needs automation to cope with volume.
Where are SOCs heading?
The direction is clear even where timing is not: more automation of routine triage, more use of behavioural analytics and threat intelligence, closer work with managed providers, and continuous monitoring across cloud and edge estates. AI agents can draft triage notes, enrich alerts and propose responses, but containment decisions that affect the business should keep a named human approver and a record of what the agent saw and did. AgentGRC offers governance, risk and compliance controls for autonomous agent actions, and ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
Summing up
A SOC is worth building when you can say who owns each alert, which playbook applies and how the result is recorded. Pick the model that matches your risk and staffing, start with the data and use cases that matter most, and add automation where a human still approves the high-impact steps. Explore our cyber security services for support.
To map one security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is a security operations center?
It is the team, process and tooling that continuously monitors an organisation's systems for security threats, triages alerts and leads incident response.
How does a SOC relate to the NIST Cybersecurity Framework?
SOC work maps mainly to the Detect, Respond and Recover functions of CSF 2.0, published on 26 February 2024. NIST SP 800-61 Rev. 3 (April 2025) applies CSF 2.0 to incident response.
What is the difference between a SOC and SOC 2?
A SOC is a security team. SOC 2 is an assurance report on a service provider's controls.
Which SOC model should we choose?
It depends on your risk, regulation, budget and ability to staff 24/7 coverage. Small teams often start with a managed or co-managed service; large estates tend to run a dedicated SOC.
What does a SOC need before it adds AI agents?
Clean data, written playbooks, clear alert ownership and a rule that high-impact actions need human approval. Automate routine triage first.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE