Key takeaway
- Implement zero trust in sequence: NIST SP 800-207 tenets, CISA's five pillars and four maturity stages, plus how AI agents change identity and policy.
Zero trust is a security approach in which no user, device or workload is trusted because of where it sits on the network. Every request is authenticated and authorised against policy before access is granted, and trust is checked again as conditions change. NIST defines it in SP 800-207 as a shift of protection away from fixed network perimeters and towards users, assets and resources.
For a CISO or enterprise architect, implementing zero trust is a sequenced programme, not a product purchase. You start with identity and the data that matters most, add device and network controls, and measure progress against a maturity model. This guide sets out the principles, the architecture, an adoption sequence, the trade-offs, and how AI agents change the identity question. For the insider-risk side, see our post on the impact of insider threats in cyber security.
What does zero trust actually require?
NIST SP 800-207 (final, August 2020) states seven tenets. In plain terms they are:
| Tenet | What it means in practice |
|---|---|
| All data sources and services are resources | Inventory every application, API, dataset and service, not only servers |
| All communication is secured | Network location alone never implies trust |
| Access is per session and least privilege | Trust is checked before each session, with the minimum access needed |
| Access is decided by dynamic policy | Identity, device state and behavioural and environmental attributes feed the decision |
| Assets are monitored, none inherently trusted | Posture of owned and associated assets is watched continuously |
| Authentication and authorisation are dynamic and enforced before access | Trust is continually reevaluated, not granted once |
| Collect data to improve posture | Telemetry on assets, traffic and access requests feeds policy improvement |
Source: NIST SP 800-207, paraphrased.
Why is the perimeter model no longer enough?
The castle and moat model assumes that anyone inside the firewall can be trusted. NIST describes zero trust as a response to remote work, bring-your-own-device policies and cloud-hosted assets that sit outside the organisation's network boundary. Once data and users live outside the perimeter, location tells you nothing about risk. A compromised internal account also inherits whatever the network allows it to reach, which is why zero trust and insider-risk controls overlap.
What does a zero trust architecture look like?
NIST SP 800-207 describes logical components that separate the decision from the enforcement:
| Component | Role |
|---|---|
| Policy Engine (PE) | Makes the final decision to grant, deny or revoke access to a resource, and logs it |
| Policy Administrator (PA) | Opens or closes the communication path between subject and resource based on the PE decision |
| Policy Enforcement Point (PEP) | Enables, monitors and ends the connection to the resource |
The PE and PA together form the policy decision point. For cloud-native estates, NIST SP 800-207A (September 2023) extends the model to multi-cloud and hybrid environments. It moves controls from IP addresses and subnets to application and service identities, enforced through API gateways, sidecar proxies and an application identity framework. Our guide to cloud native security tools and architecture covers the container, cluster and cloud layers where those controls run.
How should an enterprise sequence its zero trust adoption?
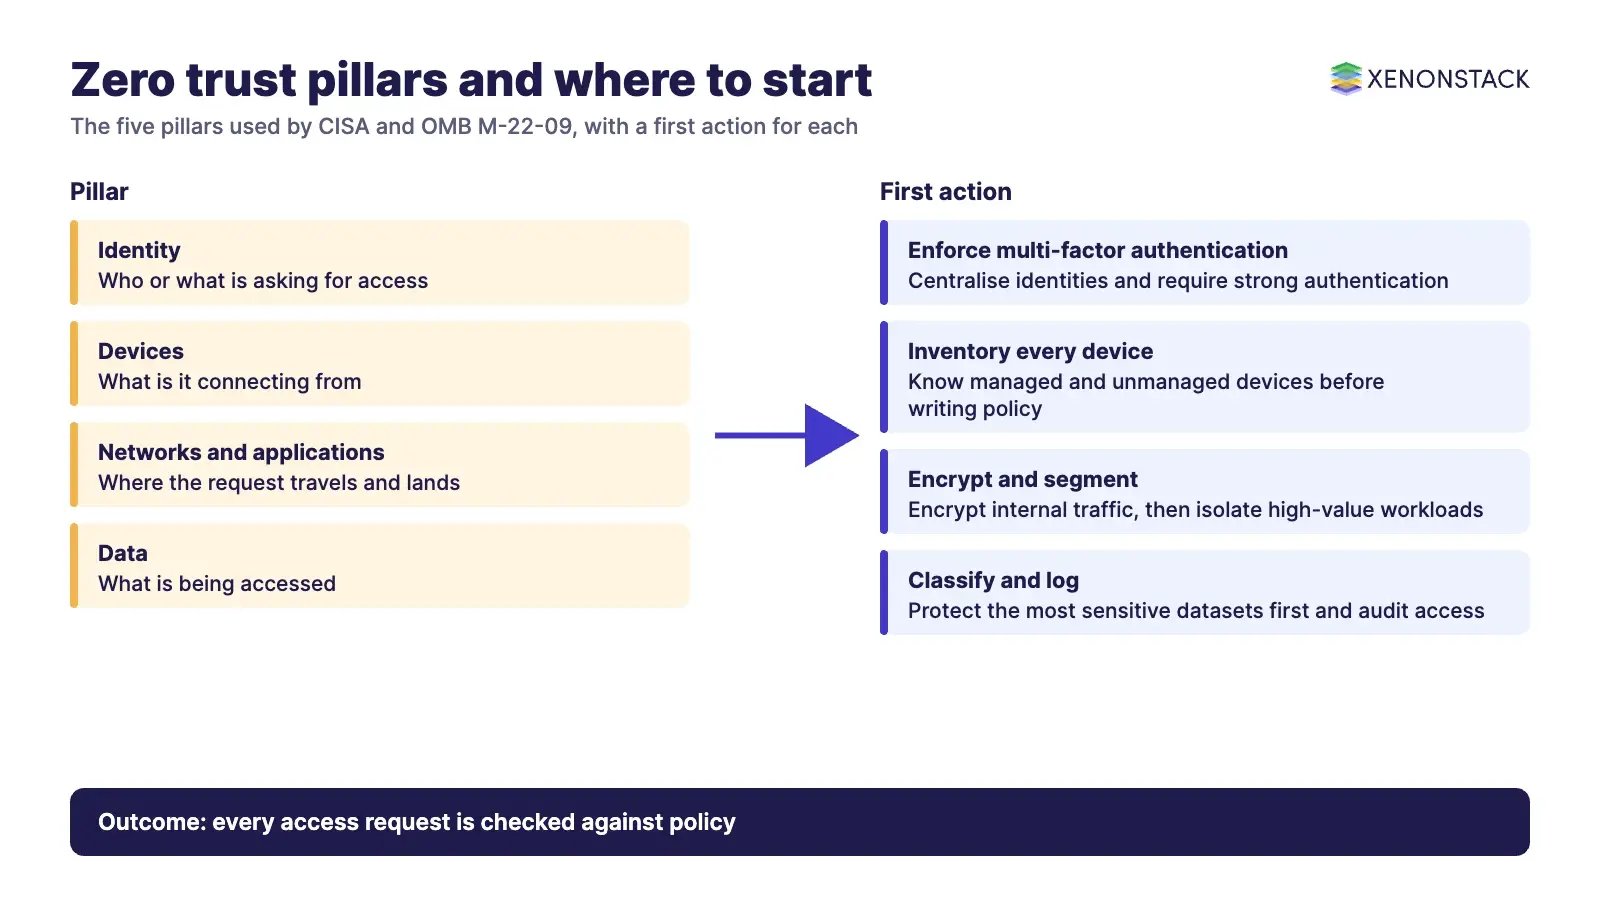
CISA's Zero Trust Maturity Model organises the work into five pillars and three cross-cutting capabilities, with four maturity stages for each pillar: traditional, initial, advanced and optimal. The US federal strategy in OMB memorandum M-22-09 (26 January 2022) uses the same five pillars, which makes them a useful planning checklist for any enterprise. The table below shows the pillars with the actions M-22-09 sets for US agencies. The memo was written for the US federal government and is a reference point, not a requirement for private companies.
| Pillar | Federal action in M-22-09 | Enterprise starting point |
|---|---|---|
| Identity | Centralised, enterprise-managed identities; phishing-resistant multi-factor authentication; at least one device signal in access decisions | Consolidate identity providers and enforce multi-factor authentication first |
| Devices | Complete asset inventory; endpoint detection and response across the agency | Know every managed and unmanaged device before writing device policy |
| Networks | Encrypted DNS where supported; HTTPS for all web and API traffic, including internal; plan to isolate environments | Encrypt internal traffic, then segment by workload |
| Applications and workloads | Dedicated application security testing, third-party testing, public vulnerability disclosure; work towards immutable workloads | Build testing into delivery; see security testing in DevOps |
| Data | Automate categorisation and protection of sensitive documents; audit access to encrypted data through key management logs; comprehensive logging | Classify the few datasets that matter most and protect those first |
A practical sequence for most enterprises is: inventory assets and data, fix identity and multi-factor authentication, encrypt traffic, segment the highest-value workloads, then add continuous monitoring and automated policy decisions. To see where your own environment stands, the cloud security posture assessment is a quick starting point.
How do AI agents change the zero trust identity question?
AI agents call tools, read data and act on behalf of people, so each one is a non-human identity that needs the same checks as a user. In our own architecture work, the pattern we use is a zero trust policy engine that makes dynamic, context-based access decisions for human-to-agent, agent-to-agent and agent-to-tool calls, with a human owner named for every agent and an audit trail for every action. That is our design approach, not a standard. AgentGRC is ElixirData's agent that enforces policy on autonomous AI actions and records audit-ready evidence of each decision, and ElixirData Context OS is a governance layer that checks policy and authority before agents act. For security operations, MetaSecure describes turning a SOC into an adaptive defence system powered by modular AI agents.
What are the governance, security and cost considerations?
- Governance: assign an executive owner, a policy owner per pillar, and an agreed maturity target for each pillar.
- Security: the policy engine becomes a critical dependency, so design it for availability and log every decision it makes.
- Cost: the main costs are identity consolidation, telemetry volume and staff time, not a single licence. Budget per pillar and phase the spend.
- User experience: per-session checks add friction if policy is badly tuned. Pilot with one user group before wide rollout.
What are the trade-offs, and when is zero trust not the answer?
Zero trust is a direction, not a finished state, and NIST itself calls it a developing set of approaches. It will not fix weak asset inventories, poor patching or unmanaged data; it depends on them. Legacy systems that cannot support modern authentication may need a gateway or isolation instead of full enforcement. A small organisation with a single cloud and a managed identity provider can often reach a good position with multi-factor authentication, least privilege and logging, without a large architecture programme.
To map one access decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is zero trust in one sentence?
A model in which access is never granted because of network location or device ownership; authentication and authorisation happen before each session with a resource (NIST SP 800-207).
Is zero trust a product I can buy?
No. NIST describes it as a set of approaches and an architecture, built from identity, device, network, application and data controls.
Where should we start?
With asset and data inventory, then identity and multi-factor authentication, which is also the first pillar in the US federal strategy (OMB M-22-09).
What are the five pillars?
Identity, devices, networks, applications and workloads, and data, as used in CISA's maturity model and OMB M-22-09.
How do we measure progress?
CISA's Zero Trust Maturity Model rates each pillar at one of four stages: traditional, initial, advanced or optimal.
Does zero trust apply to AI agents?
Yes. An agent acts with credentials and tool access, so it needs an owner, least-privilege access and an audit trail, like any other identity.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE