Key takeaway
- Continuous security for CTOs and CISOs: controls by pipeline stage, NIST SSDF and SLSA, container hardening, myths, trade-offs and an adoption sequence.
Continuous security means running security checks, evidence collection and monitoring at every stage of delivery, from commit to runtime, instead of testing once before release. It is the operating model that sits behind DevSecOps: the same controls run on every change, and the results feed one view of risk. NIST describes information security continuous monitoring as giving visibility into assets, awareness of threats and vulnerabilities, and insight into how well controls are performing (NIST SP 800-137).
This guide is for CTOs, CISOs and platform leads who already run CI/CD and microservices on containers. It sets out which controls belong at which stage, what the NIST Secure Software Development Framework and SLSA ask for, how to harden containers and clusters, where continuous security does not fit, and how AI agents change the picture. It stays distinct from our guides to SecDevOps, the DevSecOps checklist and DevSecOps in CI/CD.
What is continuous security, and how is it different from DevSecOps?
DevSecOps is the culture and the toolchain that moves security into development. Continuous security is the outcome you run and measure: every commit, image, deployment and running workload is checked automatically, and the findings are kept as evidence. NIST SP 800-218 (SSDF version 1.1, February 2022) makes the same point from the development side. Most software development life cycle models do not address security in depth, so secure development practices have to be added to them.
| Guide | Question it answers | Best for |
|---|---|---|
| SecDevOps | Should security come first in the lifecycle, and do we need that label? | Teams deciding how to frame the practice |
| DevSecOps checklist | What do we check at each stage, from pre-commit to deployment? | Engineers writing pipeline gates |
| DevSecOps in CI/CD | How do we build the checks into each pipeline stage? | Pipeline owners |
| This guide | How do we keep security assurance running continuously, across pipeline, containers and runtime, with evidence leaders can rely on? | CISOs, CTOs and platform leads |
Which security controls run at which stage of the pipeline?
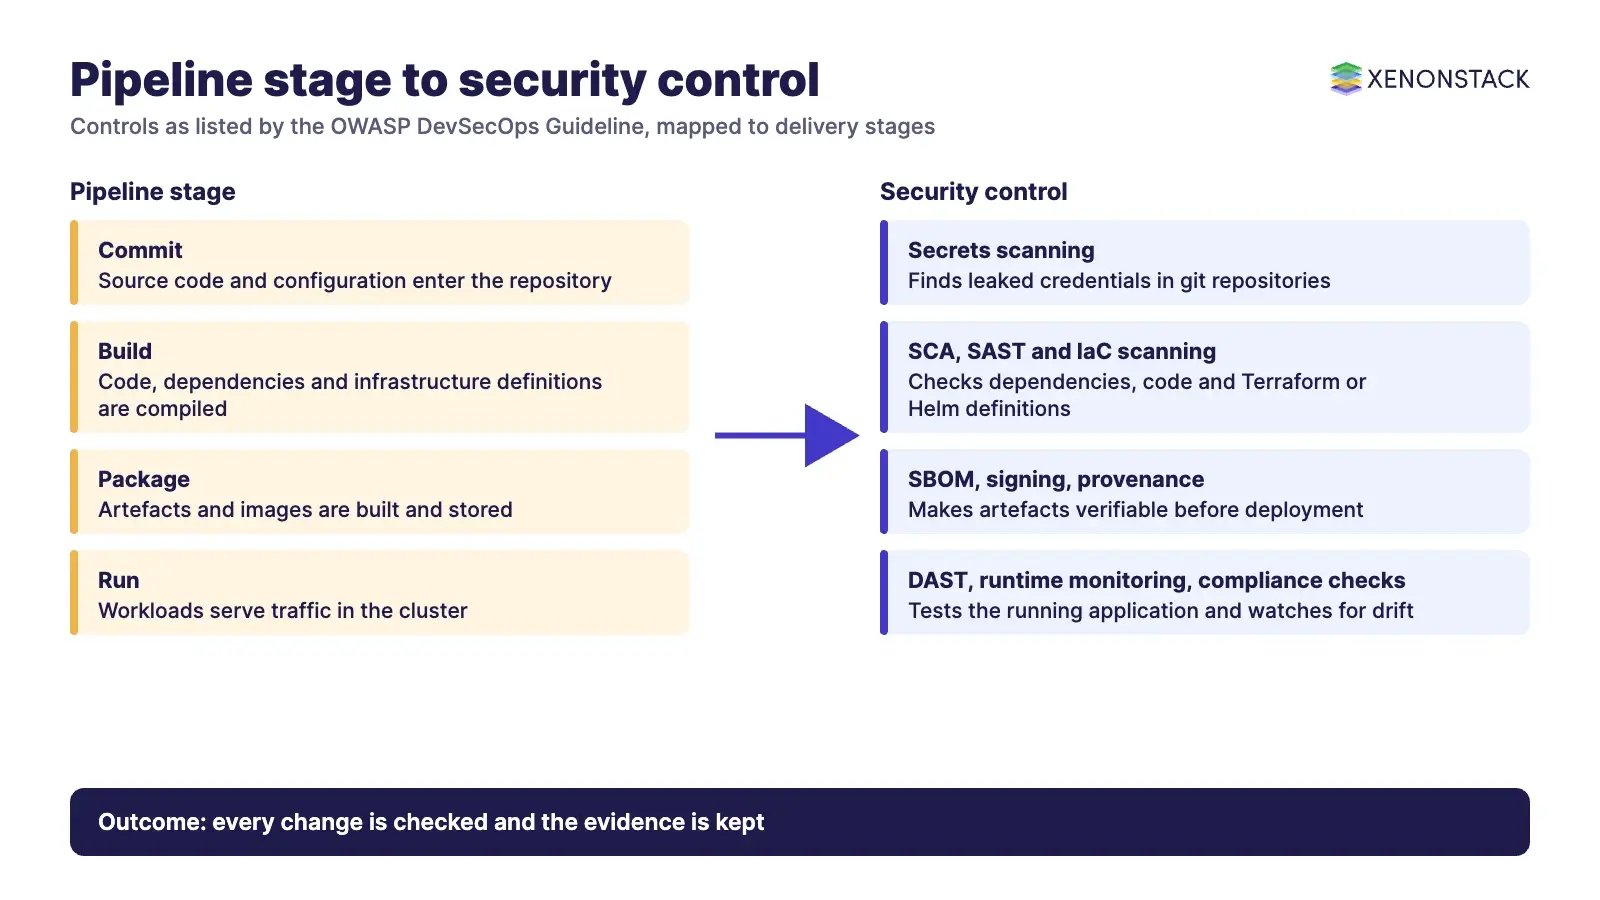
The OWASP DevSecOps Guideline lists the activities a basic secure pipeline can include and says teams can customise the steps and add automation progressively. The table maps them to stages.
| Stage | Control (as listed by OWASP) | What it catches |
|---|---|---|
| Commit | Secrets scanning of git repositories | Leaked credentials |
| Build | Software composition analysis (SCA) and static application security testing (SAST) | Vulnerable dependencies and insecure code patterns |
| Build | Infrastructure-as-code scanning, for example Terraform and Helm charts | Insecure infrastructure definitions before they are applied |
| Package | Supply-chain security: SBOMs, artefact signing and provenance, pipeline security | Tampered or unverifiable artefacts |
| Test | Dynamic (DAST) and interactive (IAST) application security testing, API security | Flaws that appear only in a running application |
| Deploy and run | Infrastructure scanning, cloud-native application protection, compliance checks | Drift from the approved configuration |
Source: OWASP DevSecOps Guideline, read 13 November 2026. The project describes itself as an Incubator Project. For the dynamic stage, the ZAP documentation describes an Automation Framework, which it recommends for most non-trivial automation, and Docker packaged scans as the easiest way to start. Our guides to security testing in DevOps and penetration testing cover the test methods in detail.
What do NIST SSDF and SLSA ask of a continuous security programme?
NIST SP 800-218 groups secure development practices into four sets. They give leadership a common vocabulary for audits and supplier questions.
| SSDF group | Intent (per NIST) | Continuous security example |
|---|---|---|
| Prepare the Organization (PO) | People, processes and technology are ready for secure development | Defined pipeline policies and trained teams |
| Protect the Software (PS) | Guard all parts of the software against tampering and unauthorised access | Signed artefacts, locked-down registries and build systems |
| Produce Well-Secured Software (PW) | Release software with as few vulnerabilities as possible | SAST, SCA and DAST gates on every change |
| Respond to Vulnerabilities (RV) | Find remaining vulnerabilities in released software, fix them and prevent recurrence | Runtime monitoring, triage and tracked remediation |
Source: NIST SP 800-218, read 13 November 2026; confirm on the NIST page whether a later revision applies to you. For build integrity, the SLSA specification describes itself as an industry-consensus way to describe and gradually strengthen supply chain security through levels. Its site states that version 1.2 is current, so check the version your auditors expect.
How do you secure containers and microservices continuously?
Microservices on Docker and Kubernetes change often, so controls have to attach to the image, the registry, the cluster and the running workload. NIST SP 800-190 (September 2017) is the reference guide to application container security concerns and recommended ways to address them. Our container security guide goes further.
| Layer | Practice | Why it matters |
|---|---|---|
| Image | Keep Dockerfiles in version control, pin explicit base image versions rather than latest, keep layers few | Reproducible, reviewable builds |
| Registry | Use a private registry and sign images | You can verify what is inside an image and which version runs |
| Container | Treat containers as immutable; keep code, configuration and data separate; run as a regular user, not root | Smaller blast radius and no drift |
| Cluster | Set resource requests and limits; separate dev, UAT and production; apply Kubernetes network policies | Limits resource exhaustion and lateral movement |
| Admission | Enforce Pod Security Standards (Privileged, Baseline, Restricted) | Unsafe pods are refused before they start |
| Runtime | Enable logging and alerting on security events | Detection and incident response depend on it |
According to the Kubernetes documentation, Baseline is a minimally restrictive policy that prevents known privilege escalations, and Restricted is a heavily restricted policy that follows current pod hardening best practices. Confirm the exact Restricted requirements on that page before you enforce it, because it can break workloads that run as root.
What are the common myths about continuous security?
| Myth | Reality |
|---|---|
| Security belongs to the security team alone | Developers, operations and security each own controls in the pipeline; the security team sets policy and reviews exceptions. |
| It slows delivery | Badly tuned gates do. Start with fast checks on every commit and run slower scans on a schedule or before release. |
| It is only about tools | Tools produce findings. Ownership, triage and a clear fix path decide whether anything changes. |
| It is a checkbox | Continuous means findings are reviewed, tracked and closed on an ongoing basis. |
| It only suits large organisations | Small teams can begin with secrets scanning, dependency checks and a hardened base image. |
When does continuous security not fit, and what does it cost?
- Alert volume: untuned scanners flood teams with low-value findings. Set severity thresholds and name an owner for each queue before you make any gate blocking.
- Pipeline time: running every scanner on every commit lengthens feedback loops. Split fast and slow checks.
- Legacy systems: applications without automated builds or tests cannot be gated continuously. Fix the delivery pipeline first.
- Tool sprawl: overlapping tools create overlapping findings. Choose by category (secrets, SCA, SAST, DAST, runtime) and confirm each product's current status on the vendor's own page.
- Compliance is not security: passing checks shows controls ran, not that the system is safe. Keep human review and testing for high-risk changes.
How do AI agents change continuous security?
When agents write code, open pull requests or change infrastructure, they become actors inside your pipeline and need the same controls as a human engineer: least privilege, policy checks and an audit trail. AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
How should you adopt continuous security in sequence?
- People first: agree who owns each class of finding and train teams on the controls they will meet.
- Then process: write the pipeline policy, map it to the SSDF groups and decide which gates block and which only warn.
- Then tools: add secrets scanning, SCA and SAST, then IaC and container scanning, then DAST, and finally runtime monitoring.
- Measure and alert: record findings, time to remediate and exceptions, and alert on security events in both infrastructure and applications.
- Protect secrets and traffic: use a secrets manager such as HashiCorp Vault and mutual TLS between services where your policy requires them.
To map one security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is continuous security?
It is the practice of running security checks, monitoring and evidence collection automatically at every stage of delivery, so assurance does not depend on a single pre-release test.
How is continuous security different from DevSecOps?
DevSecOps is the culture and toolchain that brings security into development. Continuous security is the running outcome: every change and workload is checked repeatedly and the results are kept as evidence.
Which framework should we map our pipeline to?
NIST SP 800-218 (SSDF) gives four practice groups, and SLSA covers build and supply chain integrity. Check the versions your auditors expect on the official pages.
Does continuous security slow down delivery?
It can if every scanner blocks every commit. Run fast checks on each commit, schedule slower scans and make only well-tuned gates blocking.
Where should we start in a microservices estate?
Start with secrets scanning, dependency checks, pinned base images, a private signed registry and non-root containers, then add cluster policy and runtime monitoring.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE