Key takeaway
- Penetration testing explained: what it is and is not, black, grey and white box types, the stages of a test, scoping, and how AI agents change it.
Penetration testing is an authorised, simulated attack on a system, carried out by skilled testers, to find out whether its security can be breached and how far an attacker could get. The result is a report of what was exploited, so the owner can fix it before a real attacker finds it.
This guide is for security leads, engineering managers and buyers who need to commission or understand a pen test. It covers what the test is and is not, the main test types, the stages of an engagement, how to scope and choose a provider, and how AI agents change the routine. Related reading: penetration testing tools and methodologies, website security and security testing in DevOps.
What is penetration testing, and what is it not?
The NCSC penetration testing guidance defines it as a method for gaining assurance in the security of an IT system by attempting to breach some or all of that system's security, using the same tools and techniques an adversary might use. The people doing this legally are often called ethical hackers.
The NCSC is clear about the limits. It says a penetration test is best seen as a way to check your vulnerability assessment and management processes, not as the primary method for identifying vulnerabilities. It confirms known issues only on the day of the test, and risk assessment and decisions on fixes remain your responsibility. It is not an appropriate technique for testing individual products, and routine security tests should continue alongside it.
What types of penetration test are there?
Tests are described by what the tester knows and where the tester starts. These definitions are widely used, but providers vary in their wording, so agree them in the scope.
| Type | Tester starts with | Simulates |
|---|---|---|
| Black box | Little more than a name or address, no internal knowledge | An outsider with no inside information |
| Grey box | Limited details about the environment | An attacker with partial access, such as a user account |
| White box | Full details such as architecture and source code | A deep review, or an insider |
| External | Internet-facing assets such as web applications, websites and DNS | An attacker outside the firewall |
| Internal | Access behind the firewall | A compromised employee account, for example after phishing |
| Social engineering | People and processes, such as help desks | An attacker who persuades someone to reveal information |
Other common targets are web applications, networks, wireless networks, client-side software and physical access. For web applications, the OWASP Web Security Testing Guide is an OWASP flagship project; its page says version 4.2 is the latest release and version 5.0 is in development.
What are the stages of a penetration test?
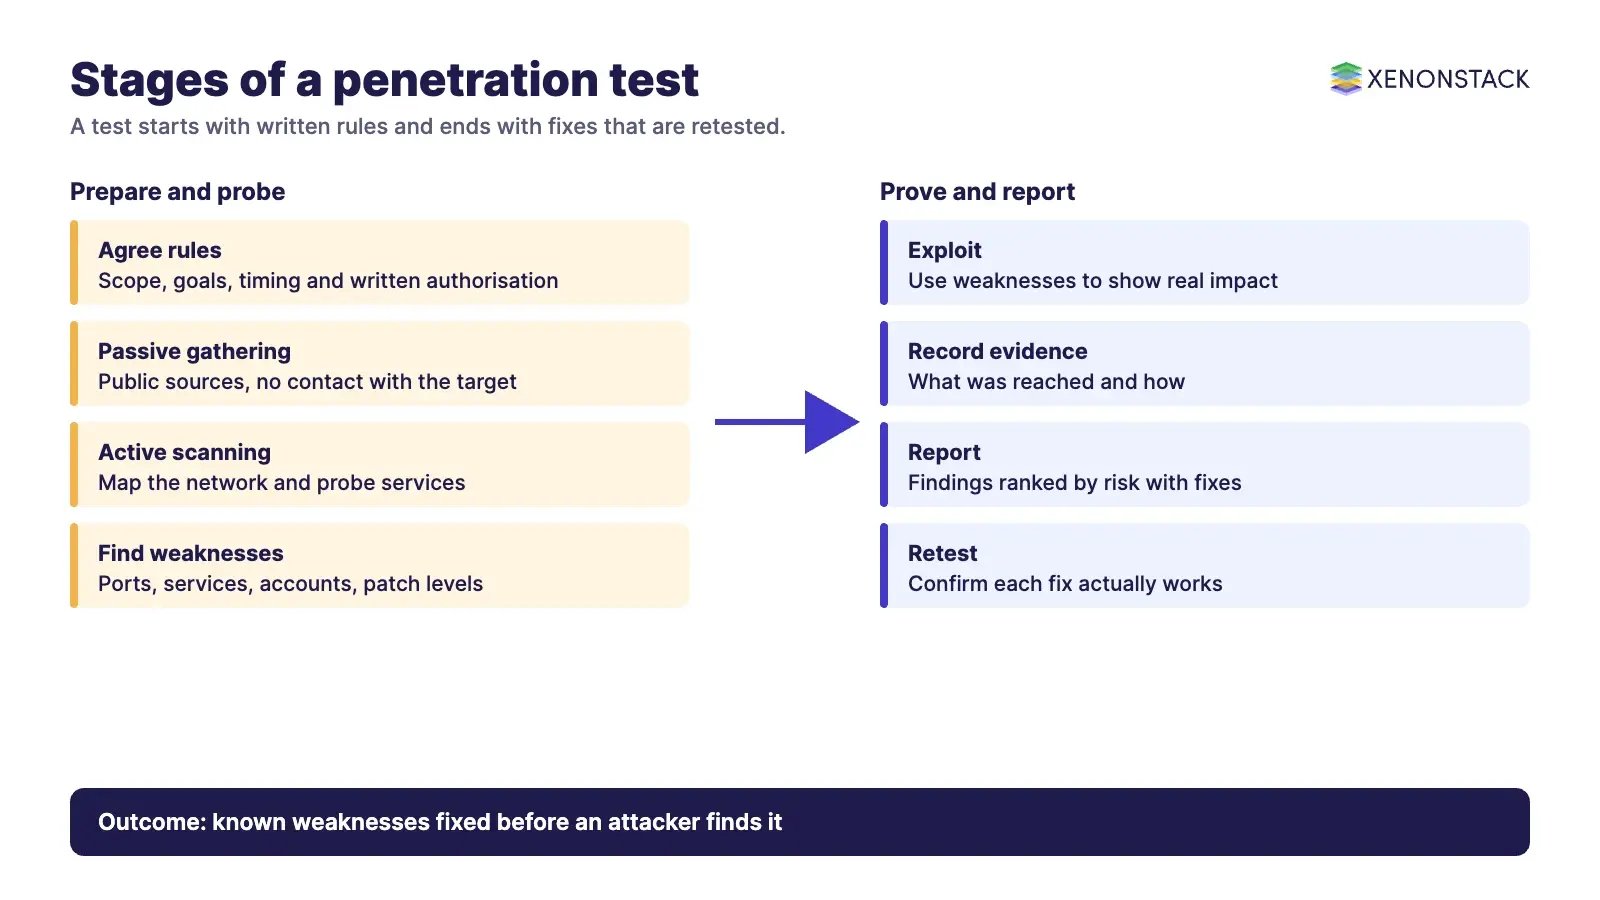
- Agree the rules. Define scope, goals, systems, methods, timing and written authorisation, so testing is legal and safe.
- Gather information. Passive work uses public sources without touching the target; active work probes it, for example by mapping the network.
- Find weaknesses. Identify open ports, running services, accounts and patch levels.
- Exploit. Try to use the weaknesses, for example through privilege escalation, to show real impact.
- Report. Record what was exploited, what data was reached and the fixes, ranked by risk.
The NIST SP 800-115 guide, Technical Guide to Information Security Testing and Assessment (September 2008), helps organisations plan and run technical security tests, analyse results and build mitigation strategies. It describes itself as an overview rather than a complete testing programme, so treat it as a reference point and check NIST for its current status.
How do you scope a test and choose a provider?
Following the NCSC, involve risk owners, technical staff who know the system and a representative of the test team. Risk owners flag areas of concern, technical staff define the boundaries of the estate, and testers propose what is needed for a full picture. Share your current vulnerability assessment so testers can judge its accuracy. The plan of action should cover technical boundaries, test types, timeframes, effort, use cases, tester requirements, compliance obligations and reporting needs. Use qualified, experienced testers, because quality depends heavily on their ability, and flag unusual systems early in the bid.
How do AI agents change penetration testing?
Agents can take over the repetitive work around a test: tracking scope and assets, running routine scans, collating findings, retesting fixes and keeping the evidence trail. They also create something new to test, because an agent with tools and credentials is itself an attack surface, so include agent permissions and prompt-injection paths in scope. Human testers still own authorisation, judgement on impact and the final report. ElixirClaw is XenonStack's AI agents computing platform for building and operating agents with governed access.
What should you do first?
- List the systems, data and agents that matter most and name a risk owner for each.
- Run your own vulnerability assessment so the test checks it rather than replaces it.
- Write the scope, test type, timing and written authorisation.
- Choose a qualified provider and agree the report format.
- Fix the findings, retest, and schedule the next test.
Further reading: smoke testing, sanity testing and system testing.
To map one decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is the difference between black box, grey box and white box testing?
They differ in what the tester knows at the start. Black box testers have almost no inside information, grey box testers have limited details, and white box testers have full details such as source code.
Is a penetration test the same as a vulnerability scan?
No. A scan looks for known weaknesses. A penetration test tries to breach the system as an adversary would. The NCSC says it should not be the primary way you find vulnerabilities.
How often should you run a penetration test?
The NCSC notes a test only confirms known issues on the day it is run, and tests can be a year or more apart, so keep vulnerability management running between tests.
Who should do the test?
Choose qualified, experienced testers. UK government organisations are advised by the NCSC to use testers and companies in the CHECK scheme.
Who is responsible for acting on the findings?
You are. The NCSC says risk assessment and decisions on fixes remain the organisation's responsibility and should not be wholly outsourced to the test team.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE