Key takeaway
- Compare penetration testing tools by job, map them to OWASP WSTG, PTES and NIST SP 800-115, and govern AI-assisted testing with approval gates and logs.
What are the best penetration testing tools for enterprises going into 2027?
There is no single best tool. Enterprises combine a network discovery tool, a web application proxy and scanner, and an exploitation framework, run them under written authorisation, and report against a standard such as NIST SP 800-115. Burp Suite, Nmap, Metasploit and ZAP are the usual starting set.
Tool choice matters less than method and control. This guide helps CISOs, security architects and engineering leads pick tools by job, map them to the OWASP Web Security Testing Guide, PTES and NIST, and govern AI-assisted testing. For the wider discipline, see our guides on penetration testing and ethical hacking versus penetration testing. It stays at method and selection level and does not give attack instructions.
How is a penetration test different from a vulnerability assessment?
A vulnerability assessment lists known weaknesses across many assets, usually with automated scanners. A penetration test is goal-led: an authorised tester tries to show which weaknesses lead to real impact. NIST SP 800-115 (September 2008, final) frames both as security testing techniques that an organisation plans, runs and interprets.
Use assessments for breadth and routine hygiene. Use penetration tests to validate that controls hold against a realistic goal, for example reaching a sensitive data store. Neither replaces the other, and both need a named owner for fixes.
Which standards and methodologies should guide the test?
Three official sources cover most enterprise needs. Confirm the current version of each on its own page before you cite it in a contract.
| Source | What it gives you | Best used for | Status to confirm |
|---|---|---|---|
| OWASP Web Security Testing Guide (WSTG) | A framework of best practices for testing web applications and web services, with tests grouped in categories such as Information Gathering | Web and API test plans | Latest versioned release on its page is v4.2 (3 December 2020); v5.0 is in development |
| Penetration Testing Execution Standard (PTES) | Seven sections: Pre-engagement Interactions, Intelligence Gathering, Threat Modeling, Vulnerability Analysis, Exploitation, Post Exploitation, Reporting | Engagement lifecycle and scoping | Official site is pentest-standard.org; v2.0 is described as planned |
| NIST SP 800-115 | Technical guide to information security testing and assessment, with guidance on planning tests, interpreting results and planning fixes | Planning, reporting and assurance evidence | Final, September 2008; confirm on csrc.nist.gov |
Many older pages teach a five-phase attacker model. It is not a published standard, so we use the three sources above as the reference points. A practical pattern: PTES for scoping and reporting structure, WSTG for web test cases, NIST SP 800-115 for governance and evidence.
How do you choose penetration testing tools by job?
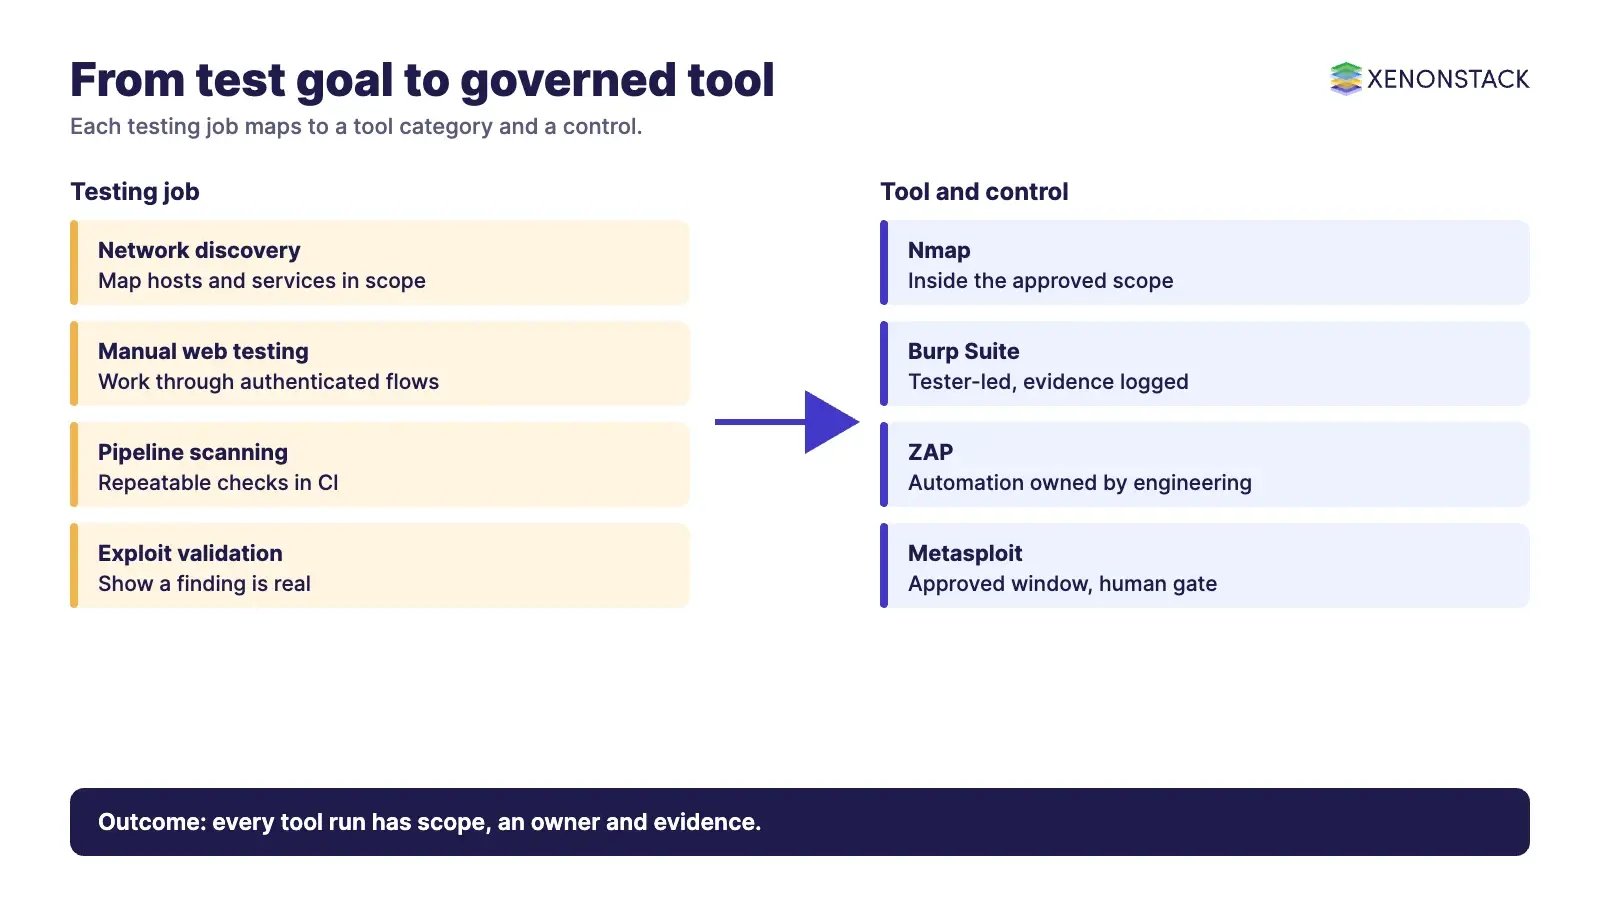
Pick tools from what the test must prove, not from a top-ten list. Each row below names the job, a well-known option and the one claim we can source from that tool's own page.
| Job | Tool and claim from its own site | Fits when | Do not rely on it for |
|---|---|---|---|
| Network discovery and inventory | Nmap: described on nmap.org as a free and open source utility for network discovery and security auditing | You need an accurate map of hosts and services before testing | Proving business impact on its own |
| Web application testing by hand | Burp Suite Professional: described by PortSwigger as a web penetration testing toolkit; Community Edition offers manual tools to start web security testing | Testers work through authenticated web flows and APIs | Unattended coverage of large estates |
| Automated web scanning in a pipeline | ZAP: describes itself as a free web app scanner and open source project, with automation documentation | Developers need repeatable checks in CI | Replacing a skilled tester on business-logic flaws |
| Controlled exploitation and validation | Metasploit: the docs call the Framework free and open source, with Metasploit Pro as a commercial edition | You must show a finding is exploitable, inside scope | Production systems without an approved window |
| Enterprise DAST | Burp DAST: described by PortSwigger as an enterprise-enabled dynamic web vulnerability scanner for AppSec and vulnerability management teams | A central team scans many applications | Manual abuse-case testing |
Licences, editions and product names change. Confirm on the vendor page before you buy, and check that a tool is still maintained. Open source does not mean unsupported, but ownership of updates should be named in your register.
What must be agreed before any tool runs?
Tools cause incidents when scope is vague. Agree these items in writing, which is what PTES calls pre-engagement and NIST calls planning:
- Scope and exclusions: named systems, environments and data classes.
- Authorisation: who signs, and for which dates and sources of traffic.
- Safety limits: no denial of service, rate limits, and a stop word.
- Data handling: where evidence is stored, who can read it and when it is destroyed.
- Third parties: cloud provider and vendor permissions to test.
- Reporting: format, severity scale, retest date and remediation owner.
How should AI-assisted penetration testing be governed?
AI agents now plan steps, call tools and draft findings. That raises the stakes, because an agent with tool access can act at machine speed. PortSwigger describes Burp AT as agentic AI that extends human-led pentesting, which is the model we recommend: assist the tester, keep a person in control.
| Control | What it means | Why |
|---|---|---|
| Scope allow-list | The agent can only reach named targets | Stops drift outside authorisation |
| Human approval gate | A person approves any action that changes a system | Keeps accountability with a named tester |
| Full logging | Every tool call and prompt is recorded | Gives evidence for audit and for the report |
| Least-privilege credentials | Test accounts with minimal rights and expiry | Limits damage if the agent misbehaves |
| Model and tool risk review | Assess the agent against the OWASP Top 10 for LLM Applications (2025) and the NIST AI RMF | Covers prompt injection and excessive agency |
For the controls in detail, read our guides on agentic AI risk management and agentic AI cybersecurity. AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need, according to its site.
What does a good report and retest look like?
A report is the product of the test. It should state scope and dates, method (which standard), each finding with evidence, affected asset, severity, a fix owner and a retest result. NIST SP 800-115 stresses interpreting results and planning remediation, not only finding issues.
Set an exit check: a finding closes only when a retest, by someone other than the fixer, shows the weakness no longer works. Track mean time to fix per severity and review it with engineering leaders each quarter.
What is the adoption sequence?
- Write rules of engagement and a scope register.
- Pick a standard set: PTES, WSTG and NIST SP 800-115.
- Choose tools by job from the table above and name an owner for each.
- Run a pilot on one non-production application.
- Add scanning to CI and keep manual testing for business logic.
- Introduce AI assistance only behind the controls above.
- Retest and report to risk owners on a fixed cycle.
When should you not run a penetration test?
Do not test without written authorisation, on systems you do not control, during unmanaged production peaks, or before basic hygiene exists. If asset inventory and patching are weak, a vulnerability assessment gives better value first. Consider the legal position in each country and confirm it with counsel, since this guide is not legal advice.
To map one security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, according to its site. See also our cyber security services.
What should you plan for in 2027?
Plan next year's testing around method, ownership and control rather than a tool ranking.
- Confirm standards versions: check the current version of the OWASP Web Security Testing Guide, PTES and NIST SP 800-115 on their official pages before you cite them in a contract.
- Name owners: write rules of engagement and a scope register, and name an owner for each tool and its updates, since licences, editions and product names change.
- Gate AI assistance: introduce AI assisted testing only behind a scope allow list, a human approval gate and full logging, and retest every fixed finding on a fixed cycle.
Frequently asked questions
What are penetration testing tools?
Penetration testing tools are software that helps an authorised tester discover hosts and services, probe web applications and APIs, and prove which weaknesses can actually be used. NIST SP 800-115 treats them as supporting techniques inside a planned test, not as the test itself.
Which penetration testing tools do enterprises use first?
Most programmes start with a network discovery tool such as Nmap, an intercepting proxy such as Burp Suite or ZAP for web applications, and an exploitation framework such as Metasploit for controlled validation. Choose by the scope in your rules of engagement, not by a ranking.
Is a vulnerability scanner the same as a penetration testing tool?
No. A scanner lists known weaknesses at scale. A penetration test adds human judgement to show which of them lead to real impact, within an agreed scope.
Can AI run a penetration test on its own?
Not safely without limits. Burp AT is described on PortSwigger's site as agentic AI that extends human-led pentesting, which fits the pattern we recommend: agents assist, people approve scope and any action that changes a system.
Which standards should a penetration test follow?
Use the OWASP Web Security Testing Guide for web applications, PTES for the engagement lifecycle and NIST SP 800-115 for planning and reporting, and confirm current versions on each official page.
How often should a penetration test be repeated?
Repeat after major releases or architecture changes, and always retest fixed findings. Set the frequency from your risk appetite and any contractual or regulatory requirement, which you should confirm on the official source.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE