Key takeaway
- Kubernetes architecture explained: control plane and node components, what changed since Docker and 1.9, security, operations and an adoption sequence.
What is Kubernetes architecture?
A Kubernetes cluster is split into a control plane that makes decisions and nodes that run the workloads. The control plane holds the kube-apiserver, etcd, kube-scheduler, kube-controller-manager and, where a cloud provider is involved, the cloud-controller-manager. Each node runs a kubelet and a container runtime, and usually kube-proxy. Add-ons such as cluster DNS, monitoring and logging sit on top.
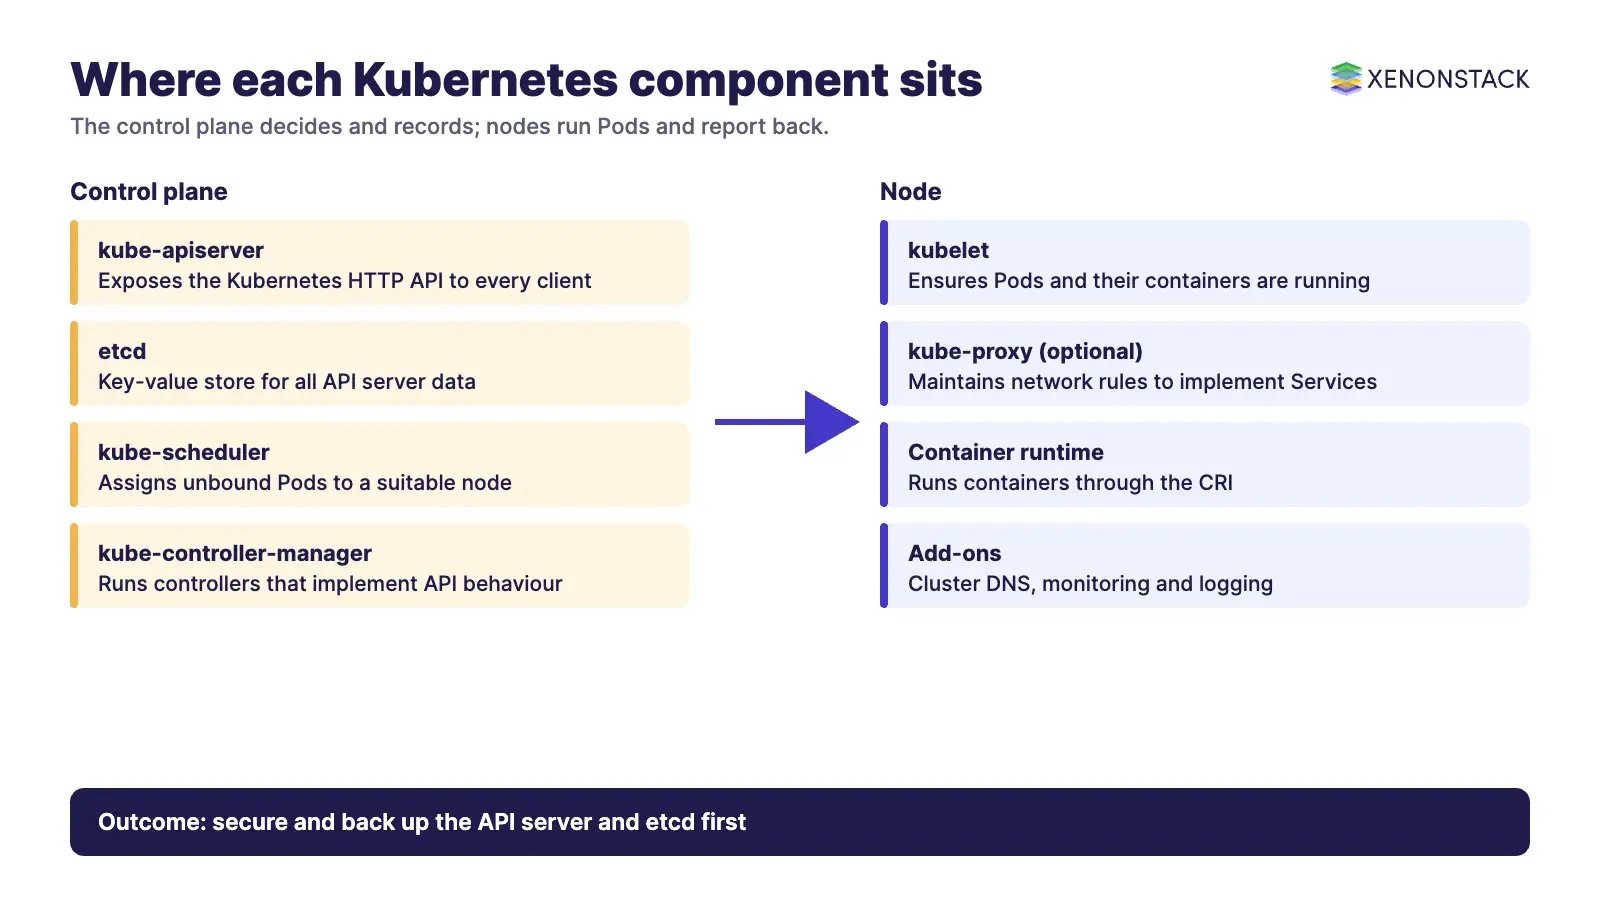
For an enterprise architect, the useful questions are which component holds state, which one is the single door into the cluster, and which ones you must secure, back up and monitor. This guide answers them, then shows what has changed since older Kubernetes tutorials were written, including the removal of Docker as a built-in runtime. If you are new to containers, start with our guide to Docker container architecture.
Which control plane components make the decisions?
The control plane manages the desired state of the cluster. Descriptions below follow the official Kubernetes components page (read 12 November 2026).
| Component | What it does | Why it matters to an enterprise |
|---|---|---|
| kube-apiserver | Exposes the Kubernetes HTTP API | Every client, including kubectl, goes through it, so it is the main point for access control and audit |
| etcd | Consistent, highly available key-value store for all API server data | It holds cluster state, so it needs a backup plan and restricted access |
| kube-scheduler | Finds Pods not yet bound to a node and assigns each to a suitable node | Placement decisions follow resource availability and scheduling policy |
| kube-controller-manager | Runs controllers that implement Kubernetes API behaviour | Keeps the actual state moving towards the declared state, for example the replica count |
| cloud-controller-manager (optional) | Integrates with the underlying cloud provider | Only needed when the cluster uses cloud-specific resources such as load balancers |
Older posts, including earlier versions of this one, call the machine that hosts these components the master node. The current documentation uses the term control plane.
Which node components run the workloads?
| Component | What it does | Status |
|---|---|---|
| kubelet | Ensures that Pods are running, including their containers | Runs on every node |
| kube-proxy | Maintains network rules on nodes to implement Services | Marked optional in the official components page |
| Container runtime | The software responsible for running containers | Must work with the kubelet through the Container Runtime Interface |
The Container Runtime Interface (CRI) is described by Kubernetes as a plugin interface that lets the kubelet use a wide variety of container runtimes without recompiling the cluster components. Nodes can be physical servers or virtual machines, on premises or in the cloud.
Is Docker still the Kubernetes runtime?
No. The dockershim, the built-in bridge between the kubelet and Docker Engine, was removed in Kubernetes v1.24. Older articles that list Docker or rkt as the node runtime are out of date. Check which CRI runtime your nodes use before you upgrade, and test your image build and scanning steps against it.
Which Kubernetes objects should architects understand?
Four objects carry most of the day-to-day design decisions.
- Pod: the smallest deployable unit. A Pod can hold more than one container that share namespaces and volumes.
- Deployment: you declare the desired state and the controller moves the cluster towards it at a controlled rate. Deployments and ReplicaSets supersede the older ReplicationController, which Kubernetes now documents as a legacy API.
- Service: a stable way to reach a set of Pods chosen by a label selector. kube-proxy maintains the network rules that implement it.
- Labels and annotations: labels are key and value pairs used to select objects, for example to roll out to one environment. Annotations hold non-identifying information.
You work with these through the API, the dashboard or the kubectl command line. For rollout patterns see our guide to blue-green deployment in Kubernetes, and for tooling see Kubernetes deployment tools and best practices.
What has changed since older Kubernetes guides?
| Older guidance | Current position | Source |
|---|---|---|
| Docker is the node runtime | Dockershim removed in v1.24; use a CRI runtime | Kubernetes dockershim FAQ |
| ReplicationController manages replicas | Superseded by Deployment and ReplicaSet | Kubernetes documentation |
| Kubernetes 1.9 features (apps/v1 GA, alpha CSI, Windows beta) | The current stable minor release is 1.37 (patch 1.37.1, 15 September 2026); the project maintains the three most recent minors | Kubernetes releases page |
| Traffic routing means Ingress only | Gateway API is a family of API kinds for dynamic infrastructure provisioning and advanced traffic routing | Kubernetes Gateway API page |
Patch support is about 12 months for versions from 1.19 onwards, so a cluster left on an old minor version drifts out of support within a year.
How should you secure and govern a cluster?
Start from the architecture. The kube-apiserver is the single door for all clients, and etcd holds all API server data. Restrict who and what can reach both, and treat an etcd backup plan as a requirement, because the Kubernetes documentation states that if your cluster uses etcd as its backing store you should have one.
Governance becomes harder when AI agents and automation call the cluster API as well as people. Each action should be tied to an identity, a policy and a record you can show an auditor. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. The ElixirData Audit Agent pulls decision history, policy versions, sign-offs and authority records into compliance-ready proof for auditors on request, and ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
What does day-to-day operation look like?
In the managed Kubernetes services our teams run, the routine is the same architecture seen from the outside: check node readiness, pod status and workload availability on the production cluster and on a standby cluster, investigate service connectivity and ingress routing when an application is unavailable, and trace Prometheus alerts with Grafana metrics and workload information. GitOps keeps cluster configuration in version control. Application-level guides to read next are PostgreSQL deployment in Kubernetes, large-scale application management with OpenKruise and blockchain deployment on Kubernetes.
When is Kubernetes the wrong choice?
- A single small application with one team may not justify running a control plane, upgrades and cluster monitoring. A managed service or a simpler platform may fit better.
- Teams without the capacity to patch minor versions inside the support window take on security and compatibility risk.
- Stateful systems need a tested etcd and storage recovery plan before they go in.
In what order should you adopt Kubernetes?
- Containerise one service and confirm it runs on a CRI runtime such as the one your nodes will use.
- Choose managed or self-run control plane, and decide the Kubernetes minor version policy.
- Set access to the kube-apiserver, and back up etcd if you run it yourself.
- Define Deployments, Services and labels as code and keep them in version control.
- Add monitoring and logging add-ons, then a standby cluster for critical workloads.
- Add policy and audit for human and agent actions on the cluster.
To map one Kubernetes operations decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What are the main components of Kubernetes architecture?
The control plane has kube-apiserver, etcd, kube-scheduler, kube-controller-manager and optionally cloud-controller-manager. Each node has a kubelet, a container runtime and optionally kube-proxy.
What does etcd do in Kubernetes?
etcd is a consistent, highly available key-value store for all API server data. Because it holds cluster state, you should have a backup plan for it.
Does Kubernetes still use Docker?
Not as a built-in runtime. The dockershim was removed in Kubernetes v1.24, and the kubelet now works with runtimes through the Container Runtime Interface.
Is kube-proxy required?
The official components page marks kube-proxy as optional. It maintains network rules on nodes to implement Services.
Which Kubernetes versions are supported?
The project maintains the three most recent minor releases. At the time of reading, the latest stable minor was 1.37, with patch support of about 12 months.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE