Key takeaway
- Learn how Spinnaker works with Kubernetes: pipelines, canary and blue/green, Halyard to Kustomize, and 2026.3 breaking changes, plus when to choose it.
Spinnaker is an open-source continuous delivery platform that takes a built artefact, such as a container image, and moves it through test, approval and production stages with deployment strategies and rollbacks. On Kubernetes it works from manifests, so you point it at a cluster, define a pipeline and let it deploy, verify and promote each release.
The short decision for enterprise leaders: Spinnaker earns its place when many teams release to several clusters or clouds and you need one governed release path, with approvals and canary checks. For a single cluster, Helm with a GitOps tool or the native Kubernetes Deployment is usually enough. Spinnaker's own install guide says Halyard is deprecated in favour of Kustomize, so plan new installs around that.
What does Spinnaker do on Kubernetes?
Kubernetes runs and scales containers, and a Deployment can roll out a new version gradually. By default a rolling update keeps at least 75% of the desired Pods up and creates at most 125% (the default 25% maximum unavailable and 25% maximum surge, per the Kubernetes Deployment documentation). Kubernetes does not, by itself, give you a release process across environments. Spinnaker adds that layer: triggers, stages, manual approvals, notifications and analysis of a new version before it takes all traffic.
According to its docs, Spinnaker's Kubernetes provider is manifest-based and is described as the recommended provider for deploying to Kubernetes. It uses the kubectl binary for all API access, so any authentication method or resource type kubectl supports is available to it. The older V1 provider is being deprecated, and there is no automatic pipeline migration, though a V2 account can be added next to a V1 account so teams move gradually (Spinnaker Kubernetes provider docs).
Which Spinnaker concepts matter for delivery?
Spinnaker's core concepts fall into two groups: managing what is running, and deploying new versions.
| Concept | What it means (per Spinnaker docs) | Why it matters |
|---|---|---|
| Application | A collection of clusters plus the firewalls and load balancers that expose them; usually one service | The unit your team owns and views |
| Cluster | A logical grouping of server groups. It does not map to a Kubernetes cluster | Avoids confusion when reading the dashboard |
| Server group | The deployable resource and its settings; at runtime a set of instances such as VMs or pods | What a release actually creates |
| Load balancer and firewall | Traffic distribution with health checks, and network access rules | Controls how traffic reaches a version |
| Pipeline | The main deployment construct, made of ordered stages, started manually or by triggers such as a Jenkins job, a new image, a cron schedule or another pipeline | Your repeatable release path |
| Stage | A higher-level action in a pipeline, such as Deploy, Resize, Disable or Manual Judgment | Where approvals and checks sit |
The docs also describe managed delivery, a declarative layer where you define the desired state of an app across environments and Spinnaker reconciles the actual state with it.
How do blue/green, canary and rolling updates compare?
| Strategy | How it works | When it fits | Trade-off |
|---|---|---|---|
| Rolling update (Kubernetes Deployment) | Replaces Pods gradually within one Deployment | Low-risk services with good health checks | Old and new versions run side by side during the rollout |
| Blue/green (red/black) | Two environments; traffic moves to the new one once it passes checks | Releases where a fast switch back matters | Needs capacity for two versions at once |
| Canary | Partially rolls out a change and compares it with the current deployment (the baseline) using chosen metrics | High-traffic services where you want evidence before full rollout | Needs good metrics; Spinnaker says it is not a substitute for other testing |
For canary analysis, Spinnaker's canary overview says you create a canary configuration, a reusable set of metrics with scoring thresholds and weights, then add canary stages to a pipeline. It says Stackdriver, Datadog, Prometheus, Signalfx and New Relic are supported as metric sources, and names Kayenta as the component that makes the judgment.
What does a Kubernetes deployment pipeline look like?
A typical flow keeps continuous integration and delivery separate. This example uses Jenkins and a container registry, but the same shape works with other CI tools.
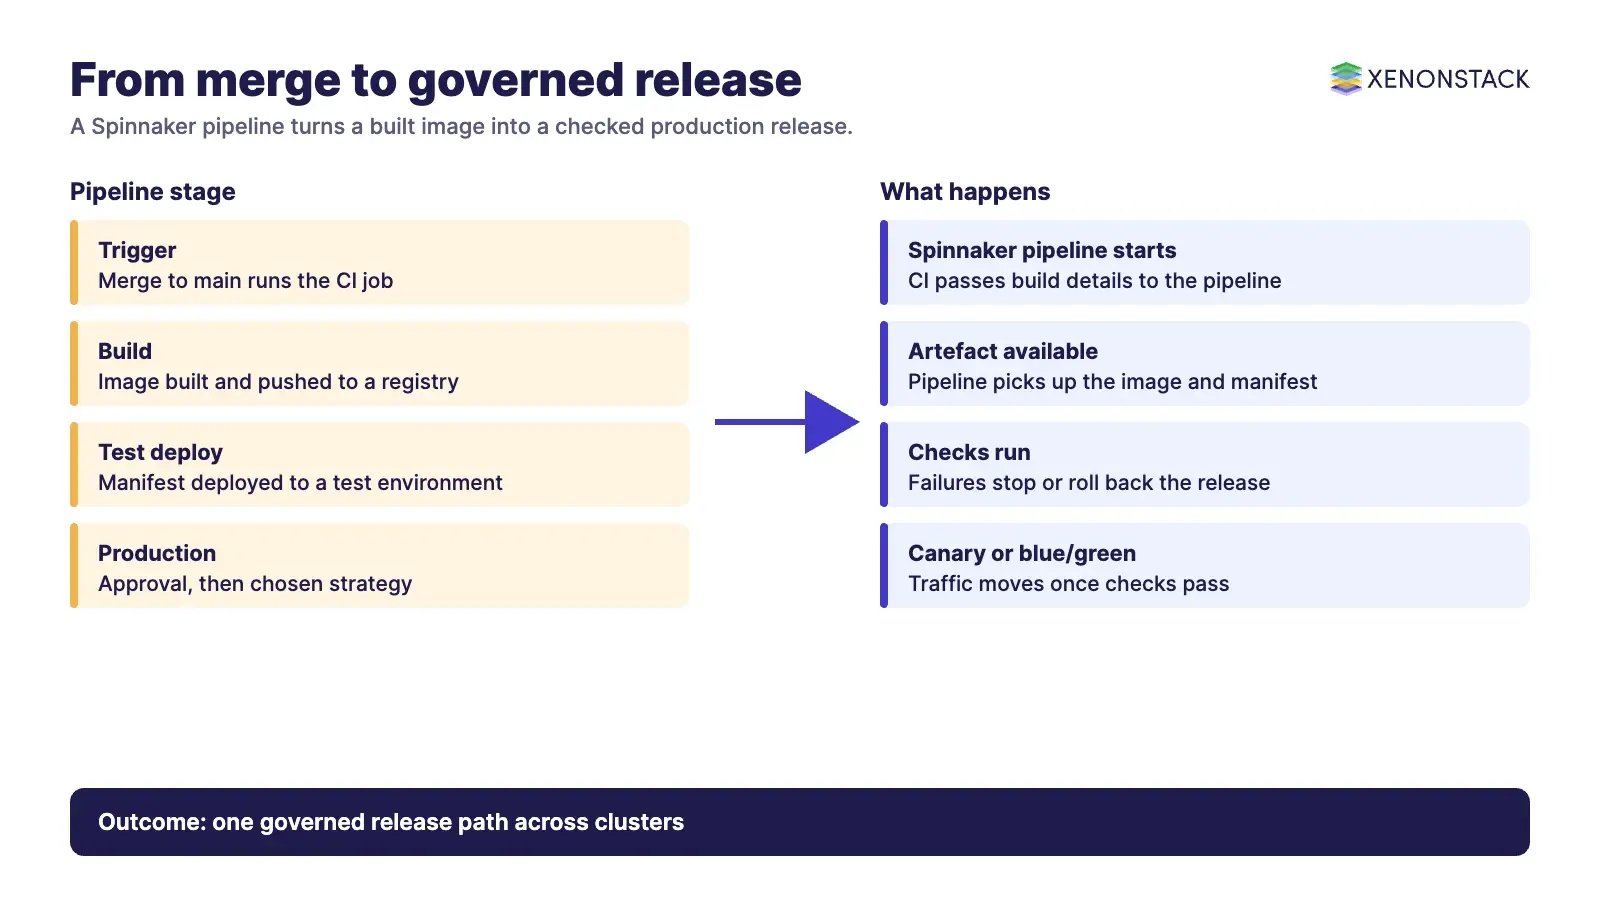
- A merge to the main branch of a Git repository triggers a Jenkins job through a GitHub webhook.
- Jenkins builds the code, builds the container image and pushes it to a registry.
- The job triggers a Spinnaker pipeline and passes build details, for example as a properties file used as an artefact.
- The pipeline deploys the Kubernetes manifest to a test environment, runs checks, waits for a manual approval if you require one, then deploys to production with your chosen strategy.
- If a check fails, the pipeline stops or rolls back, and notifications go to the team.
Prerequisites are a running Kubernetes cluster, a Spinnaker installation with your CI system connected, and a webhook from the repository. Typical stages beyond deploy include manual approval before production, a chat message to the team, a webhook call, or starting another pipeline. See our guides to Kubernetes deployment tools and best practices, Helm and Kubernetes Operators for the pieces that sit around Spinnaker.
What has changed in Spinnaker recently?
The Spinnaker 2026.3.0 changelog (published 7 September 2026) warns that the release has major breaking changes and should be validated carefully. Read the full page before upgrading, because it affects plugins and forks.
| Change | Status per the 2026.3.0 changelog | Action |
|---|---|---|
| UI framework | Angular removed from the UI, which moved to React | Plugin and fork owners must migrate |
| Halyard | Removed from the codebase; Halyard BOMs stop being published in 2027.0.0 | Move to Kustomize-based installs |
| AWS SDK | Clouddriver caching agents moved to AWS SDK v2; plugins using v1 stop working | Check AWS plugins |
| Kubernetes resource types | extensions/v1beta1 and networking.k8s.io/v1beta1 types removed | Update manifests and plugins |
| Pipeline storage | From 2027.0.0, Redis-based execution storage and non-SQL Front50 storage are removed; SQL only | Plan a SQL migration |
| Kustomize | Kustomize 3 removed in 2027.0.0; Kustomize 5 added | Move pipelines to Kustomize 4 or 5 |
Confirm dates and versions on the Spinnaker releases page before you plan an upgrade, as these items can change.
Spinnaker, Helm or a GitOps tool: which fits?
| Situation | Better fit | Why |
|---|---|---|
| One cluster, few teams | Kubernetes Deployment with Helm | Less to run and secure |
| Many teams, several clusters or clouds, approval gates | Spinnaker | One governed pipeline model and dashboard |
| Canary analysis against live metrics | Spinnaker with a metric source | Built-in canary stages |
| Small team without platform capacity | Simpler pipeline in your CI tool | Spinnaker is a system to operate in its own right |
Spinnaker needs real operations effort. Its install guide lists a Kubernetes cluster with at least 18GB of memory and 6 cores for the installation, so weigh that against the problem you are solving.
What should leaders govern around continuous delivery?
Decide who can approve a production stage, which pipelines can reach which clusters, and how a release is recorded. As AI agents start to raise pull requests and trigger releases, the same pipeline needs clear policy on what an agent may deploy and what needs a person. ElixirClaw describes itself as an agentic OS platform to build, orchestrate and govern AI agents. For agile delivery teams, Agent Scrum says it automates sprint planning and Scrum ceremonies and helps teams track blockers.
How should you adopt Spinnaker?
- Start with one service and one cluster, using a Kustomize-based install.
- Build a pipeline with deploy, verify and manual approval stages.
- Add a canary stage once you have trusted metrics.
- Add further teams and clusters, with account and namespace limits.
- Review upgrades against the changelog before each release.
More background: Kubernetes architecture and Amazon EKS, or our Kubernetes solution page.
To map one release decision your agents and pipelines should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is Spinnaker used for?
It is a continuous delivery platform that runs deployment pipelines, with stages, triggers, approvals and deployment strategies, across clusters and clouds.
Does Spinnaker replace Kubernetes Deployments?
No. Its Kubernetes provider deploys manifests through kubectl, so it sits above Kubernetes and adds a release process around it.
Is Halyard still the way to install Spinnaker?
No. Spinnaker's install guide says Halyard is deprecated in favour of Kustomize, and the 2026.3.0 changelog says it was removed from the codebase.
Which metric sources work for canary analysis?
Spinnaker's canary overview names Stackdriver, Datadog, Prometheus, Signalfx and New Relic as built-in sources.
Is Spinnaker worth it for one cluster?
Often not. Helm or your CI tool may be enough. It pays off with many teams, several clusters and a need for governed approvals.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE