Key takeaway
- OpenKruise extends Kubernetes with CloneSet, Advanced StatefulSet, SidecarSet and in-place updates. See what fits, how to install it and when to skip it.
OpenKruise is an open-source extension suite for Kubernetes that adds workload types such as CloneSet, Advanced StatefulSet, BroadcastJob and SidecarSet, plus in-place updates and availability protection, for teams running applications at scale. It is a CNCF incubating project, and its docs describe it as automated management of large-scale applications: deployment, upgrades, operations and availability protection.
For a CTO or platform lead, the decision is narrow: which gaps in native Deployments, StatefulSets and Jobs are costing you release time or uptime, and does OpenKruise close them without adding more risk than it removes. This guide covers the workloads, the progressive delivery component, installation, governance and when not to use it. For the wider tooling picture, see our guide to Kubernetes deployment tools and best practices.
What is OpenKruise and where does it fit in Kubernetes?
OpenKruise describes itself as an extended component suite for Kubernetes. Most of its features are built as custom resource definitions (CRDs) and need no other dependencies. It is not a platform as a service, but the docs say it provides essential building blocks for one. It originated at Alibaba, and the CNCF lists it as accepted on 10 November 2020 and promoted to the Incubating level on 2 March 2023.
The suite sits beside the native controllers rather than replacing Kubernetes. You keep the cluster, the API and your manifests, and adopt Kruise workloads only where a native one falls short.
Gartner
The global cloud management market is expected to reach $410 billion by 2025, significantly increasing from earlier valuations.
McKinsey
It is predicted that over 80% of organizations will employ AI and machine learning for automating application management processes
Which OpenKruise workloads solve which problem?
| Component | What it does | When it fits |
|---|---|---|
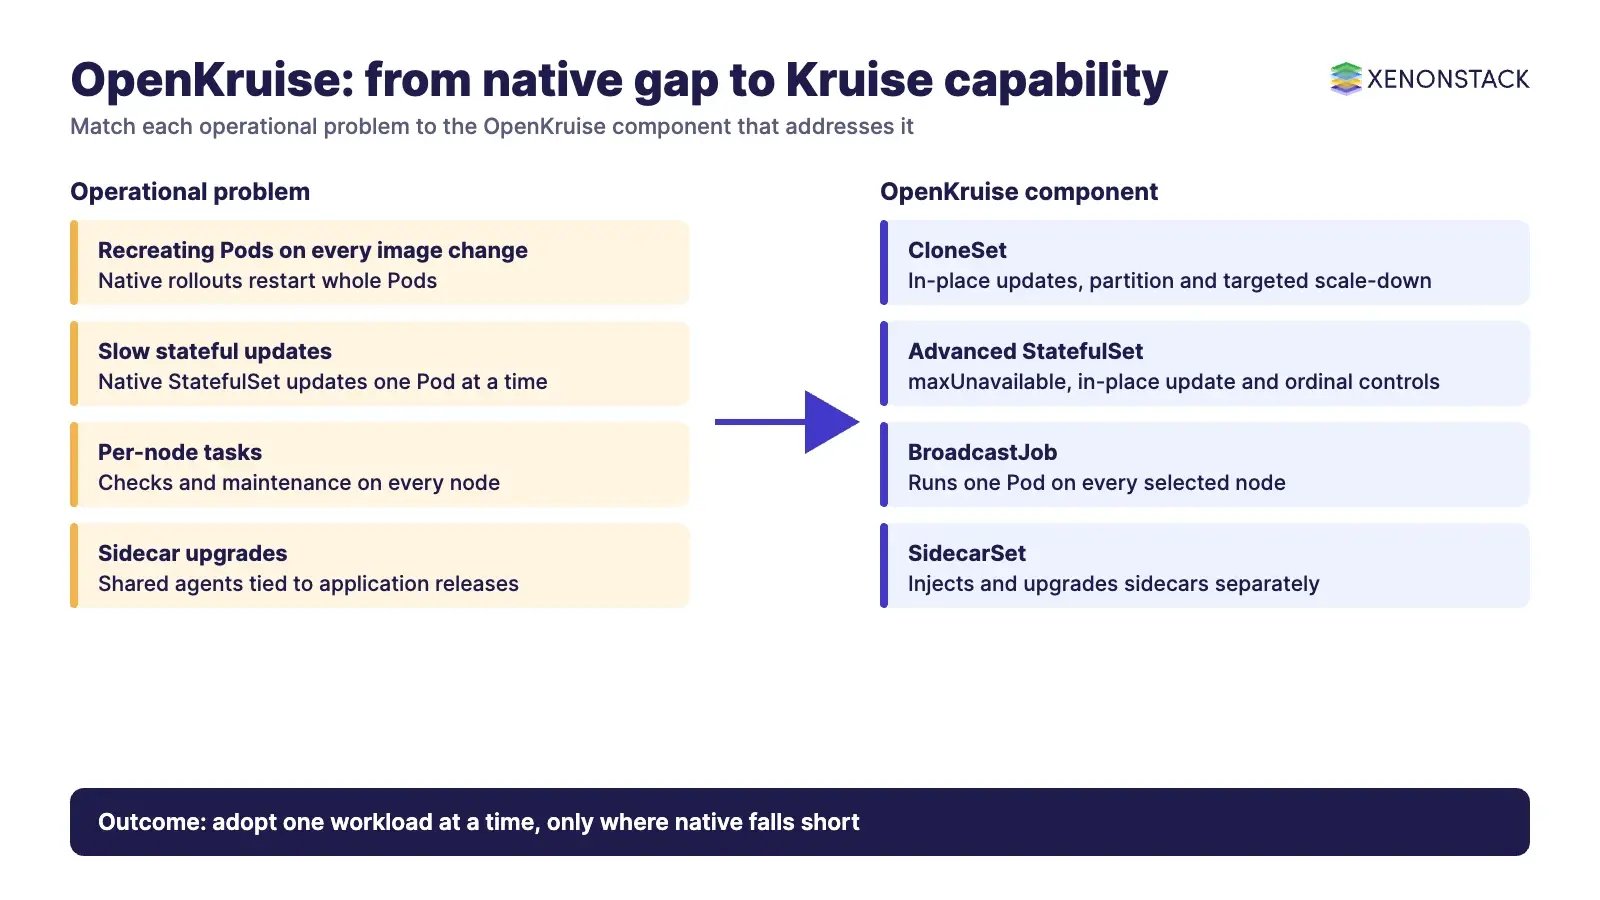
| CloneSet | Stateless workload, described in the docs as an enhanced Deployment | Large stateless fleets that need in-place updates, partition control and targeted scale-down |
| Advanced StatefulSet | StatefulSet with in-place update, maxUnavailable and ordinal controls | Stateful services where native one-at-a-time updates are too slow |
| BroadcastJob | Runs one Pod on every selected node, to completion | Node-level checks and cluster-wide maintenance tasks |
| AdvancedCronJob | Enhanced CronJob that can create Jobs, BroadcastJobs or ImageListPullJobs | Scheduled work that must run on every node |
| SidecarSet | Injects and upgrades sidecar containers apart from the application | Monitoring and operations agents shared across many applications |
| WorkloadSpread | Spreads Pods across subsets such as zones | Multi-zone and elastic deployments |
| PodUnavailableBudget | Limits unavailable Pods during voluntary disruptions | Applications with a strict availability target |
| ImagePullJob | Pre-downloads an image onto chosen nodes | Fast rollouts on large clusters |
The docs also list Advanced DaemonSet and UnitedDeployment among the workloads. Status: the docs show v1.9 as the current release, with v1.10 in progress.
CloneSet: stateless applications with in-place updates
CloneSet uses apps.kruise.io/v1alpha1 and manages Pods directly. Its updateStrategy.type defaults to ReCreate and also accepts InPlaceIfPossible, InPlaceOnly and, from v1.9.0, OnDelete. An in-place update restarts only the container whose image changed, so the Pod is not recreated. Only fields such as the image can be updated in place.
Rollout controls include partition (the number or percentage of Pods that stay on the old revision), maxUnavailable (default 20%) and maxSurge (default 0, not usable with InPlaceOnly). To scale down specific Pods, list them in scaleStrategy.podsToDelete or label them apps.kruise.io/specified-delete: "true". With volumeClaimTemplates, each Pod gets its own PVC, which in-place updates keep and recreate updates delete.
Advanced StatefulSet: faster, more controlled stateful updates
Advanced StatefulSet uses apps.kruise.io/v1beta1 and keeps the kind StatefulSet, so an existing manifest can migrate by changing the apiVersion once Kruise is installed. It adds podUpdatePolicy (ReCreate, InPlaceIfPossible or InPlaceOnly), rollingUpdate.maxUnavailable and unorderedUpdate, the last two only with podManagementPolicy: Parallel. The docs note that the native StatefulSet updates Pods one at a time even when Parallel is set. It also supports reserveOrdinals to skip chosen ordinals.
BroadcastJob and AdvancedCronJob: batch work across nodes
Earlier versions of this article called these "Job and CronJob". The OpenKruise resources are BroadcastJob and AdvancedCronJob. A BroadcastJob runs one Pod on every selected node and, with completionPolicy set to Never, can keep launching a Pod on each new node. The docs give kubelet upgrades, per-node validation and full-cluster inspection scripts as use cases. AdvancedCronJob schedules Jobs, BroadcastJobs or ImageListPullJobs, and since v1.3.0 it accepts spec.timeZone.
SidecarSet: manage sidecars separately from applications
SidecarSet injects a sidecar into matching Pods through an admission webhook and leaves the workload template untouched. Changing a sidecar image restarts only that container. For proxy-style sidecars such as Envoy, upgradeType: HotUpgrade injects two containers so the proxy is not restarted abruptly.
How do canary, blue-green and traffic routing work with OpenKruise?
These features belong to Kruise Rollouts, which the docs describe as a bypass component offering advanced progressive delivery. It is not part of the core workload set above, so plan to install and operate it separately. Per its documentation, canary is supported for Deployments only, and blue-green deployment for Deployments and CloneSets. A/B testing shifts traffic by HTTP header and cookie. Traffic routing integrates with NGINX, ALB and Higress ingress, and with service meshes through Gateway API. Multi-batch rollouts cover Deployment, CloneSet, StatefulSet, Advanced StatefulSet and Advanced DaemonSet.
Autoscaling is not listed among the OpenKruise workload features in its docs, so keep your existing autoscaler decision separate from this adoption.
How do you install OpenKruise and create a CloneSet?
The installation docs for v1.9 require Helm 3.5 or later. Check the current repository and version in the docs before you run these commands:
helm repo add openkruise https://openkruise.github.io/charts/
helm repo update
helm install kruise openkruise/kruise --version 1.9.0
Kruise 1.6.0 and later requires Kubernetes 1.18 or later, and 1.9.x is tested against Kubernetes 1.24 to 1.32. Features are switched with --set featureGates=.... KruiseDaemon, PodWebhook, WorkloadSpread and ResourcesDeletionProtection are on by default; PreDownloadImageForInPlaceUpdate, ImagePullJobGate, SidecarTerminator and InPlaceWorkloadVerticalScaling are off. Since v1.7.3, Helm uninstall is blocked while Kruise custom resources still exist.
A minimal CloneSet with three replicas and in-place updates:
apiVersion: apps.kruise.io/v1alpha1
kind: CloneSet
metadata:
  name: sample-cloneset
spec:
  replicas: 3
  selector:
    matchLabels:
      app: sample
  template:
    metadata:
      labels:
        app: sample
    spec:
      containers:
        - name: sample-app
          image: sample-image:1.0.0
          ports:
            - containerPort: 8080
          resources:
            requests:
              memory: "64Mi"
              cpu: "250m"
            limits:
              memory: "128Mi"
              cpu: "500m"
  updateStrategy:
    type: InPlaceIfPossible
    maxUnavailable: 1
Pin an image tag rather than using latest, so that an image change is a deliberate, reviewable in-place update.
What did Alibaba's Double 11 show about OpenKruise at scale?
In an Alibaba Cloud Community post dated 3 December 2020, Alibaba reported running nearly 100,000 OpenKruise workloads and managing millions of containers during the 2020 Double 11 Global Shopping Festival. It also reported that, in its environment, in-place upgrade publishing was at least 80% faster than a full re-creation upgrade, because the node already holds the old image and the Pod keeps its IP address and volumes. These are Alibaba's own figures, not a benchmark for your cluster.
What has changed in recent OpenKruise releases?
| Version | Change | Why it matters |
|---|---|---|
| v1.7.0 | Advanced StatefulSet ordinals.start (needs the StatefulSetStartOrdinal gate) | Control over the first ordinal |
| v1.8.0 | Advanced StatefulSet partition now means the number of Pods that keep the old version; in-place CPU and memory resize behind a feature gate | Partition behaviour differs from before, so review rollout manifests |
| v1.9.0 | CloneSet OnDelete type; AdvancedCronJob and ImagePullJob v1beta1; PodUnavailableBudget protection annotation | More control over when updates happen |
| v1.10 | Docs mark it as in progress | Check the changelog before upgrading |
How does OpenKruise affect governance, security and cost?
| Area | OpenKruise control | Note |
|---|---|---|
| Availability | PodUnavailableBudget intercepts Pod changes through a validating webhook | Protection is off by default and needs two feature gates |
| Accidental deletion | Docs list protection against cascading deletion of CRDs, Namespaces and most workload types | Confirm the gates in your install |
| Change surface | Admission webhooks and CRDs run in your cluster | Treat Kruise as critical infrastructure and test upgrades |
| Cost | ImagePullJob and in-place updates cut image pulls and Pod churn; WorkloadSpread places Pods by zone | Measure in your own cluster |
Rollout decisions made by people and automation, such as who approved a canary promotion and which policy applied, still need a record outside the cluster. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and its Audit Agent collects decision histories, policy versions in force and approval records for auditors.
In what order should you adopt OpenKruise?
- Install Kruise in a staging cluster with default feature gates and confirm your Kubernetes version is supported.
- Move one non-critical stateless service from Deployment to CloneSet with InPlaceIfPossible and a small partition.
- Add a PodUnavailableBudget (with its gates enabled) to a service that has an availability target.
- Migrate one stateful service to Advanced StatefulSet by changing the apiVersion, and test updates and rollbacks.
- Move shared agents to SidecarSet and node-level jobs to BroadcastJob.
- Add Kruise Rollouts only when you need canary, blue-green or header-based traffic shifting.
Set resource requests and limits on every workload, monitor with Prometheus and Grafana (the installation docs also reference a kruise-state-metrics chart), and rehearse update and rollback in staging. Delivery teams planning sprint work around such a migration can look at AgentScrum, which describes itself as agentic AI that automates sprint planning and Scrum ceremonies. See also our DevOps tools guide and Kubernetes architecture overview.
What are the trade-offs, and when should you not use OpenKruise?
- Extra moving parts: CRDs, controllers and webhooks add an upgrade and failure surface.
- Alpha API on CloneSet: the docs example uses
apps.kruise.io/v1alpha1, so check API stability against your policy. - Narrow in-place updates: only fields such as the image update in place; other changes recreate the Pod, or are blocked under InPlaceOnly.
- Canary scope: Kruise Rollouts supports canary for Deployments only.
- Skip it when native Deployments, StatefulSets and Jobs already meet your release and uptime targets, or the cluster is small.
To map one release decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about OpenKruise
Is OpenKruise a CNCF project?
Yes. The CNCF lists it as accepted on 10 November 2020 and at the Incubating level since 2 March 2023.
How is CloneSet different from a Deployment?
The docs describe CloneSet as an enhanced Deployment for stateless applications. It adds in-place updates, partition control, targeted scale-down and per-Pod PVCs.
Does OpenKruise provide canary and blue-green releases?
Through Kruise Rollouts, a separate bypass component. Canary is supported for Deployments only; blue-green for Deployments and CloneSets.
Which Kubernetes versions does it support?
Kruise 1.6.0 and later requires Kubernetes 1.18 or later, and 1.9.x is tested against 1.24 to 1.32.
What does an in-place update change?
It restarts only the container whose image changed, so the Pod is not recreated and keeps its IP address and volumes.
How does PodUnavailableBudget differ from a PodDisruptionBudget?
A native PDB constrains only evictions through the Eviction API. PodUnavailableBudget uses a validating webhook to reject Pod changes that would break the budget, and by default protects delete, evict and update.
Conclusion: is OpenKruise worth adopting?
OpenKruise earns its place where native workloads limit you: large stateless fleets that need in-place updates, stateful services that update too slowly, and node-level or sidecar operations. Adopt it one workload at a time, keep Kruise Rollouts as a separate decision, and measure results in your own cluster before standardising.
- Know more about Kubernetes Deployment
- Learn more about kubernetes security best practices
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE