Key takeaway
- Application security best practices: the OWASP Top 10:2025 risks, NIST SSDF practices, how SAST, DAST and pen testing differ, and how AI agents change it.
Application security is the set of practices, tools and decisions that keep an application and its data safe from design through build, release and operation. It works best when security checks run inside the normal development workflow, not at the end of it.
This guide is for engineering leads, security teams and architects who want a practical list of application security best practices. It covers the main risks, the practices that reduce them, how testing tools differ, and how AI agents change the work. Our application security checklist and complete guide to application security go deeper on individual steps.
What are the main application security risks?
The standard reference is the OWASP Top 10:2025, titled "The Ten Most Critical Web Application Security Risks". Its ten categories are Broken Access Control, Security Misconfiguration, Software Supply Chain Failures, Cryptographic Failures, Injection, Insecure Design, Authentication Failures, Software or Data Integrity Failures, Security Logging and Alerting Failures, and Mishandling of Exceptional Conditions.
Several risks that older guides treat separately sit inside these categories. The OWASP Injection page says injection includes cross-site scripting as well as SQL, NoSQL, OS command, ORM and LDAP injection, and that an injection flaw lets untrusted user input reach an interpreter. Its advice is to keep data separate from commands and queries, using safe interfaces such as parameterised queries or ORMs, with positive server-side input validation as a further layer and escaping only for residual dynamic queries.
| Risk | What happens | Main defence |
|---|---|---|
| Cross-site scripting (XSS) | Untrusted input runs as client-side code in another user's browser | Output encoding and input handling that keep data separate from code |
| SQL and code injection | Untrusted input is interpreted as a query or command | Parameterised interfaces, server-side validation |
| Cross-site request forgery (CSRF) | A logged-in user is tricked into sending a request they did not intend | Anti-forgery tokens and checks on state-changing requests |
| Denial of service | Traffic or requests exhaust a server or its infrastructure | Rate limiting, capacity planning and upstream protection |
| Broken access control | Users act outside their permissions | Server-side authorisation on every request, least privilege |
What are the application security best practices?
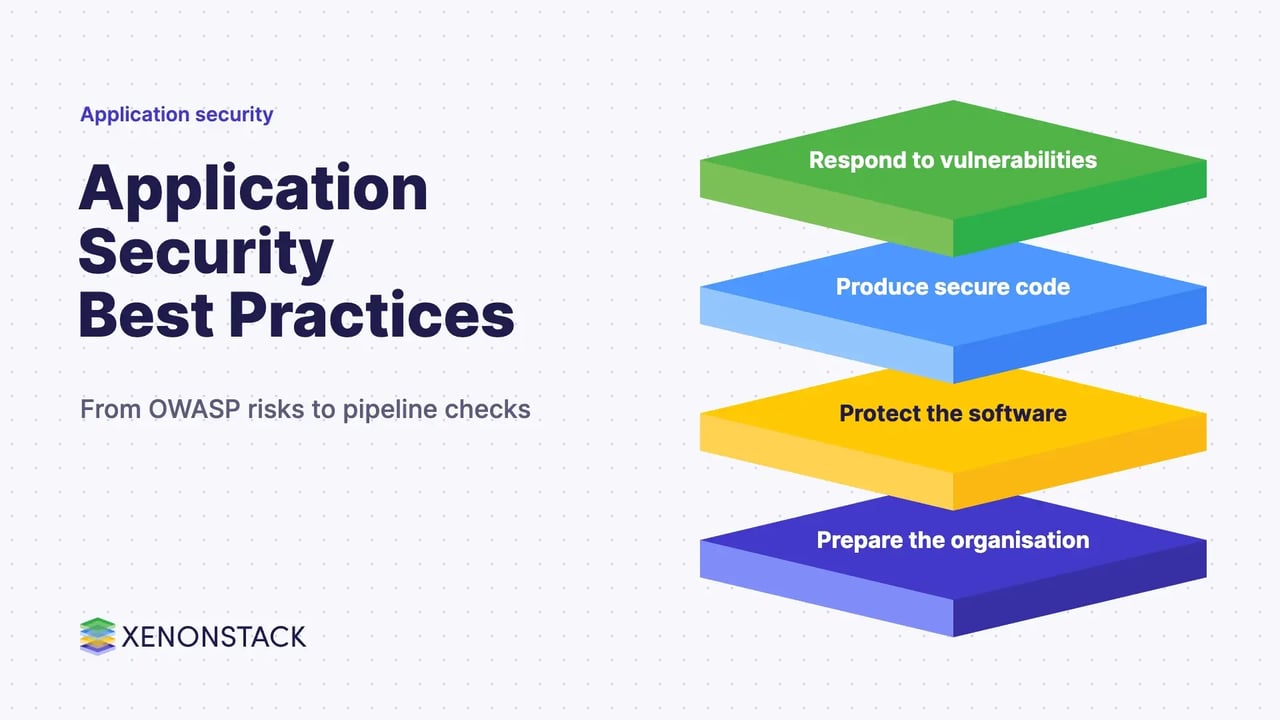
The NIST Secure Software Development Framework (SSDF), SP 800-218 version 1.1, groups secure development practices into four areas: Prepare the Organisation, Protect the Software, Produce Well-Secured Software and Respond to Vulnerabilities. NIST says its practices are meant to be integrated with existing development lifecycles and should help reduce the number of vulnerabilities in released software. The practices below follow the same shape.
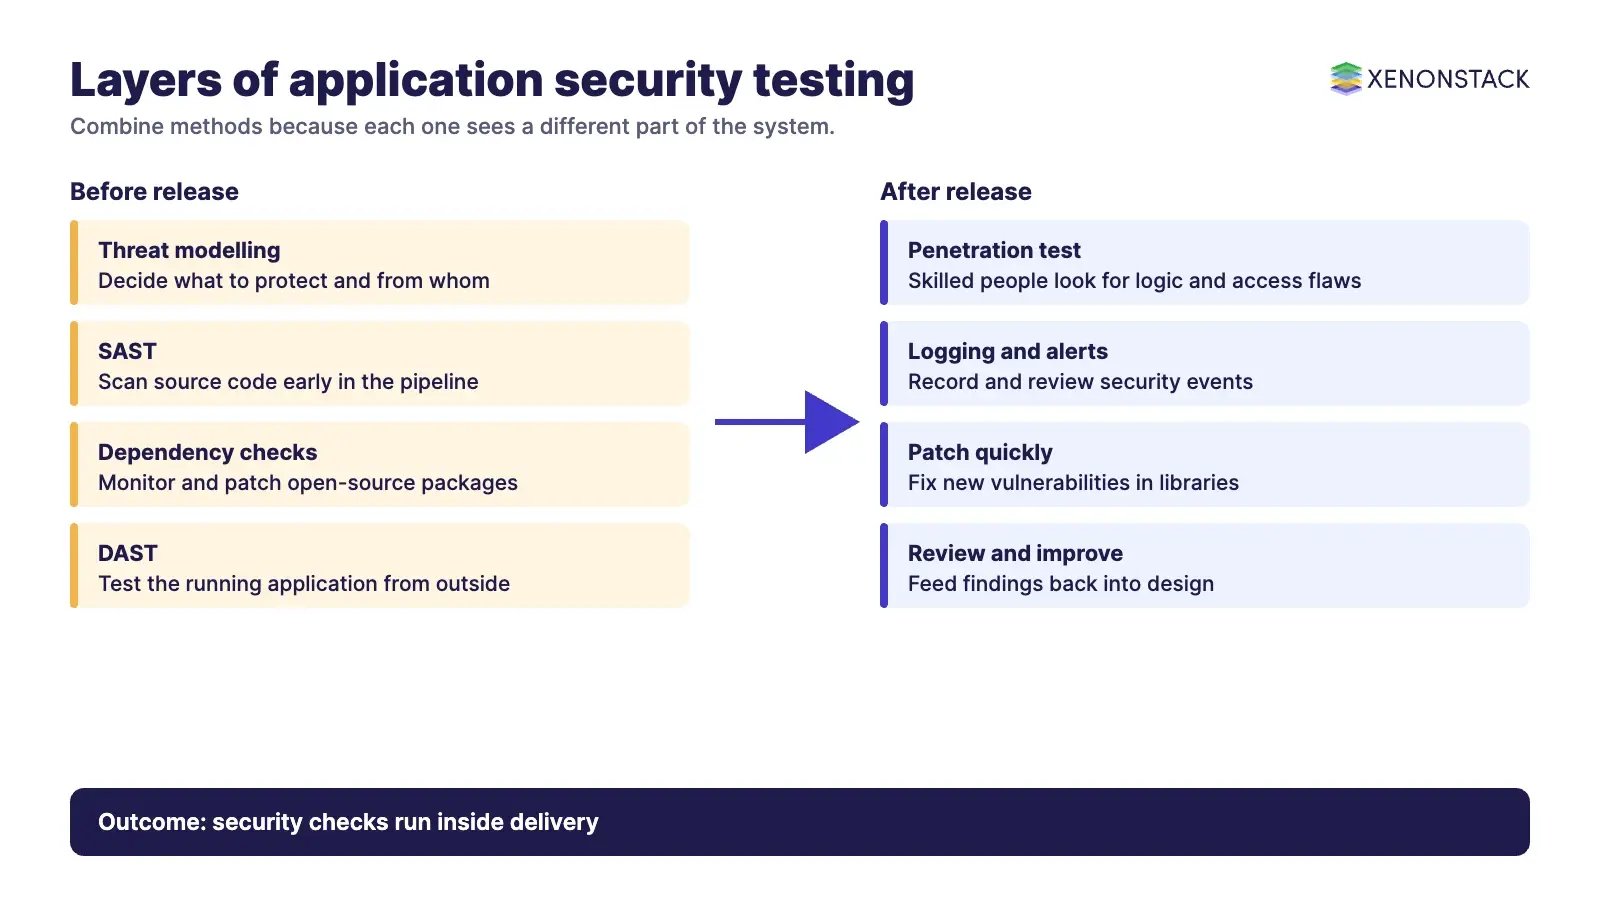
- Train developers. Developers push code to production, so they need to understand the vulnerability classes above and the secure coding methods that prevent them. A dedicated security team alone becomes a bottleneck.
- Threat model early. Decide what you protect and from whom before the design is fixed.
- Adopt a framework. Anchor your programme on a recognised one, such as the NIST CSF, CIS Controls or ISO/IEC 27001, so that web security is not managed in isolation. See our cybersecurity framework guide.
- Automate scanning in the pipeline. Integrate scanners with CI/CD and issue trackers so that no application ships unscanned and findings are handled like any other defect.
- Limit access. Apply least privilege and need-to-know: a user should hold only the permissions their current role requires.
- Protect data in transit and at rest. Use current TLS versions and well-reviewed algorithms, and never store passwords in plain text.
- Manage dependencies. Open-source packages bring cost benefits and vulnerabilities. Monitor them continuously and patch quickly.
- Log and review. Record security events and alert on them.
How do SAST, DAST, IAST and penetration testing differ?
No single tool gives complete protection, so teams combine them. Our guide to dynamic application security testing (DAST) covers one of them in detail.
| Method | What it examines | Limit to plan for |
|---|---|---|
| SAST | Source code, early, even on developer machines | Cannot see how a running system or third-party components behave |
| DAST | A running application from the outside | Finds issues late and needs a running target |
| IAST | A running application with instrumentation inside it | Needs test traffic to exercise the code |
| Penetration testing | A skilled person attacking the system | Point in time, and slower than automated scans |
| Web application firewall | Traffic in front of the application | Blocks attack routes but does not fix the flaw in the code |
A vulnerability scanner cannot find every logic flaw or access control bypass without human review, so scanning should complement penetration testing, not replace it. Tools should reduce the security team's workload by being integrated and automated, not add to it.
For cloud-hosted applications, extend the same thinking to infrastructure and containers with cloud security services.
How do AI agents change application security?
AI agents change application security in two ways. First, agents that write or review code shorten the time between a change and a release, so automated checks in the pipeline matter more. Second, an agent that calls tools, APIs and databases is itself an application: it takes untrusted input, holds credentials and acts with permissions, so the access control, injection and logging practices above apply to it directly. Give each agent its own identity, grant it the minimum access, and keep an audit trail of what it did. The AI agents computing platform, ElixirClaw, is where XenonStack builds and runs agents.
What should you do first?
- List your applications and the data each one holds, and rank them by impact.
- Add dependency and static scans to the build for the top-ranked applications.
- Check access control and input handling against the OWASP Top 10 categories.
- Schedule a penetration test for the application that holds the most sensitive data.
- Record AI agents and their tool access in the same inventory.
To map one decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is the OWASP Top 10?
It is OWASP's list of the ten most critical web application security risks. The current edition is OWASP Top 10:2025, which starts with Broken Access Control.
What is the difference between SAST and DAST?
SAST examines source code without running it, so it works early. DAST tests a running application from the outside. Teams usually use both because each misses issues the other finds.
Can a web application firewall replace secure coding?
No. A web application firewall blocks some attack routes in front of the application, but it does not fix the flaw in the code, so it should be one layer among several.
What is the principle of least privilege?
A user, service or agent is given only the access needed for its current job, which limits the damage if an account is compromised.
Which framework helps structure an application security programme?
The NIST Secure Software Development Framework groups practices into four areas, and broader frameworks such as the NIST CSF, CIS Controls and ISO/IEC 27001 help structure the wider programme.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE