Key takeaway
- Azure security services checklist for 2026: Defender for Cloud, Entra ID, Key Vault, Firewall, Private Link, Sentinel, mandatory MFA dates and MCSB.
Azure security services are the Microsoft controls you combine to protect identities, networks, data and workloads on Azure: Microsoft Entra ID for identity, Microsoft Defender for Cloud for posture and workload protection, Azure Key Vault for keys and secrets, Azure Firewall, Azure DDoS Protection and Azure Private Link for the network, Azure Policy for guardrails, Microsoft Purview for data governance and Microsoft Sentinel for detection and response. Microsoft secures the physical platform; you always own your data, identities, configurations and access management.
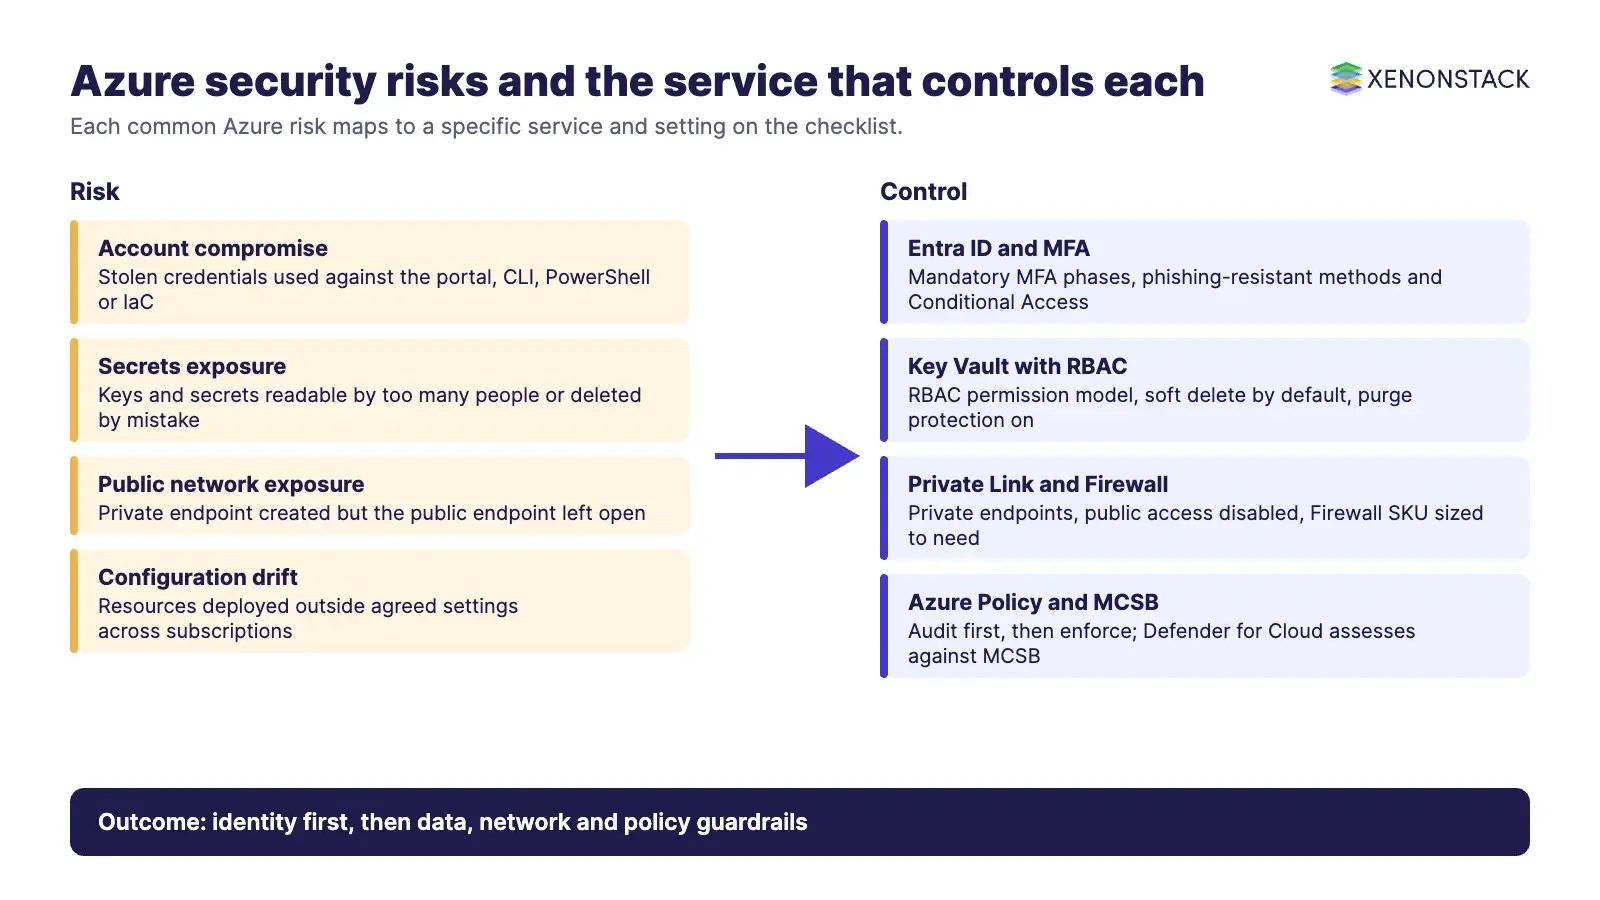
The practical checklist for 2026 starts with phishing-resistant multifactor authentication (Azure now enforces MFA for sign-in to its portals and management tools), then turns on Defender for Cloud and the Microsoft cloud security benchmark, removes public endpoints with Private Link, moves Key Vault to Azure RBAC with purge protection, and sends signals to Microsoft Sentinel in the Microsoft Defender portal. The tables below show what each service does, when it fits and its current status.
What are the core Azure security services in 2026?
The table maps each service to the job it does, the situation it fits and its status as documented on Microsoft Learn in November 2026. Several names changed in recent years, so the current product name is used throughout.
| Service | What it does | When it fits | Current status |
|---|---|---|---|
| Microsoft Entra ID (formerly Azure Active Directory) | Identity, single sign-on, MFA, Conditional Access, Privileged Identity Management | Every tenant; it is the authentication layer for Azure, Microsoft 365 and Key Vault | Plans are Microsoft Entra ID Free, P1 and P2; existing sign-in URLs, APIs and integrations were unchanged by the rename |
| Microsoft Defender for Cloud | Cloud-native application protection platform (CNAPP) covering posture management (CSPM), DevSecOps and workload protection (CWPP) | Any Azure estate; also Amazon Web Services, Google Cloud and on-premises machines | Foundational CSPM is free; Defender CSPM and workload plans are paid. Integration into the Microsoft Defender portal became generally available on 5 May 2026 |
| Azure Key Vault | Stores and rotates keys, secrets and certificates | Any application that would otherwise hold credentials or encryption keys | Azure RBAC is the recommended model and, from API version 2026-02-01, the default for new vaults; access policies are legacy |
| Azure Firewall | Managed, stateful network firewall with threat intelligence filtering | Hub virtual networks that control egress and east-west traffic | Basic, Standard and Premium SKUs; Premium adds TLS inspection and IDPS |
| Azure DDoS Protection | Adaptive mitigation of layer 3 and 4 attacks on public IP addresses | Internet-facing workloads that need attack telemetry and tuned protection | Two paid tiers (IP Protection and Network Protection) on top of free infrastructure protection |
| Azure Private Link | Private endpoints that bring a specific PaaS resource into your virtual network | Storage, databases, Key Vault and other PaaS services that should not be reachable from the internet | Generally available; network security perimeter is generally available in Azure public cloud regions |
| Azure Policy | Evaluates resources against rules and can audit, deny, modify or deploy settings | Landing zones and any estate that needs enforced guardrails | Core governance service; it also powers the benchmark checks in Defender for Cloud |
| Microsoft Purview (formerly Azure Purview) | Data discovery, classification, sensitivity labels, data loss prevention and data governance | Organisations that must know where sensitive data lives and prove compliance | Data Map scans metadata only; data stays in its original location |
| Microsoft Sentinel | Cloud-native SIEM for collecting, detecting, investigating and responding to threats | Security operations teams that need one place for Azure, Microsoft 365 and third-party signals | Generally available in the Microsoft Defender portal; not supported in the Azure portal after 31 March 2027 |
For a deeper look at Sentinel architecture, data lake tiers and cost, read our guide to Microsoft Sentinel SIEM. For teams moving towards AI-assisted security operations, MetaSecure provides an agentic SOC powered by modular AI agents and protocol-driven automation, with 24/7 coverage.
What has changed since the older Azure security checklists?
Many Azure checklists still name products and settings that have been renamed or replaced. Use the current names in policies, runbooks and audit evidence so that teams search the right documentation.
| Older reference | Current position | What to do |
|---|---|---|
| Azure Security Center and Azure Defender | Microsoft Defender for Cloud; some built-in policy definitions still carry the Security Center wording | Use Defender for Cloud plans and the Microsoft cloud security benchmark initiative |
| Azure Active Directory (Azure AD) | Microsoft Entra ID; the rename was announced on 11 July 2023 | Update documentation and licence names to Microsoft Entra ID P1 or P2 |
| Optional MFA for administrators | Mandatory MFA for Azure portals (Phase 1) and for Azure CLI, PowerShell, mobile app, IaC tools and REST API write operations (Phase 2) | Enforce MFA for every user and move user-based service accounts to workload identities |
| Key Vault access policies | Legacy model; Azure RBAC is recommended and is the default for new vaults from API version 2026-02-01 | Migrate vaults to RBAC and assign the "Azure Key Vault should use RBAC permission model" policy |
| Sentinel operated in the Azure portal | Sentinel runs in the Microsoft Defender portal; Azure portal support ends after 31 March 2027 | Plan the move to the Defender portal now |
| Grouped Defender for Cloud recommendations | Replaced by individual recommendations; grouped types were set for removal from the Azure portal on 31 July 2026 | Update queries, automation and governance rules that referenced grouped recommendation keys |
Who is responsible for what under the shared responsibility model?
Microsoft's shared responsibility model divides security tasks by service type. Whatever the model, the customer keeps responsibility for data, endpoints, accounts and access management, including RBAC, MFA and Conditional Access.
| Responsibility area | IaaS | PaaS | SaaS |
|---|---|---|---|
| Customer data, configurations, identities and users | Customer | Customer | Customer |
| Client devices | Customer | Customer | Shared |
| Applications | Customer | Shared | Shared |
| Network controls | Customer | Shared | Microsoft |
| Operating system | Customer | Microsoft | Microsoft |
| Physical hosts, network and datacentre | Microsoft | Microsoft | Microsoft |
The checklist below concentrates on the rows that stay with you. Microsoft also publishes separate shared responsibility models for generative AI workloads and for autonomous AI agents, which are worth reading before you put agents into production. Once agents are live, AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
What does mandatory MFA for Azure mean for your tenant?
Microsoft enforces mandatory multifactor authentication for Azure in two phases. There is no change for users who already sign in with MFA or with passwordless and passkey (FIDO2) methods.
| Phase | Start of enforcement | Applications covered | Operations that need MFA | Latest postponement allowed |
|---|---|---|---|---|
| Phase 1 | October 2024, rolled out gradually; Microsoft 365 admin center from February 2025 | Azure portal, Microsoft Entra admin center, Microsoft Intune admin center, Microsoft 365 admin center | Create, read, update and delete | 30 September 2025 |
| Phase 2 | 1 October 2025, rolled out gradually | Azure CLI, Azure PowerShell, Azure mobile app, infrastructure as code tools, REST API endpoints | Create, update and delete (read operations excluded) | 1 July 2026 |
Both postponement windows have now passed, so any automation that still signs in as a human user will fail on write operations. Microsoft recommends moving user-based service accounts to workload identities and deploying phishing-resistant methods such as FIDO2 security keys, passkeys, Windows Hello for Business and certificate-based authentication. Microsoft states that MFA can block more than 99.2% of account compromise attacks.
What belongs on an Azure security checklist?
Each table lists the check, the service that delivers it and why it matters. Most items map to a domain of the Microsoft cloud security benchmark, which Defender for Cloud assesses automatically.
Identity and privileged access
| Check | Service | Why it matters |
|---|---|---|
| Require MFA for every user, with phishing-resistant methods for administrators | Microsoft Entra ID (security defaults or Conditional Access) | Azure already enforces MFA for management sign-ins; extending it to all users closes the remaining gap |
| Give administrators just-in-time, approval-based role activation | Microsoft Entra Privileged Identity Management | Standing privileged access is a high-value target |
| Grant least-privilege roles at the narrowest scope | Azure RBAC | Limits the blast radius of a compromised account |
| Replace stored credentials with managed identities | Managed identities with Key Vault | Removes hard-coded secrets from code and pipelines |
For the principles behind these controls, see our introduction to identity and access management.
Network protection
| Check | Service | Why it matters |
|---|---|---|
| Disable public network access on PaaS resources and connect through private endpoints | Azure Private Link | A private endpoint maps to one resource instance, which protects against data leakage; creating it does not block the public endpoint by itself |
| Route internet egress through a central firewall | Azure Firewall | Centralises filtering, logging and threat intelligence |
| Restrict subnets to the ports and protocols they need | Network security groups | Limits lateral movement and exposure |
| Protect every internet-facing public IP | Azure DDoS Protection | Adds adaptive tuning, telemetry and mitigation reports |
| Put a web application firewall in front of public web apps | Azure Web Application Firewall on Application Gateway or Front Door | Handles layer 7 attacks that network controls do not see |
Choosing an Azure Firewall SKU is a cost and capability decision:
| Azure Firewall SKU | Maximum throughput | Threat intelligence | Distinguishing features | When it fits |
|---|---|---|---|---|
| Basic | 250 Mbps | Alert only | No DNS proxy, network FQDN filtering or web categories | Small and medium environments |
| Standard | 30 Gbps | Alert and deny | DNS proxy, network-level FQDN filtering, web categories | Most enterprise hubs |
| Premium | 100 Gbps | Alert and deny | Outbound and east-west TLS inspection, signature-based IDPS with more than 67,000 rules, URL filtering | Regulated workloads such as payment processing that need PCI DSS capabilities |
Azure DDoS Protection offers two paid tiers. DDoS IP Protection is priced per protected IP and suits a small number of addresses. DDoS Network Protection is priced per plan covering up to 100 public IPs and adds DDoS Rapid Response support, cost protection, a WAF discount and protection for Basic tier public IPs. Every Azure public IP already receives free infrastructure-level protection.
Data, keys and secrets
| Check | Service | Why it matters |
|---|---|---|
| Use the Azure RBAC permission model on every vault | Azure Key Vault with Azure Policy | With legacy access policies, a Contributor can grant themselves data-plane access |
| Turn on purge protection (soft delete is on by default and cannot be disabled) | Azure Key Vault | Purge protection is not on by default; it stops anyone, including Microsoft, purging a vault during the 7 to 90 day retention period |
| Automate rotation of keys, secrets and certificates | Key Vault autorotation | Shortens the useful life of a leaked credential |
| Discover and classify sensitive data, then apply labels and data loss prevention | Microsoft Purview | You cannot protect data you have not found |
| Enable soft delete on backup vaults and test restores | Azure Backup and Azure Site Recovery | Backups are a ransomware target and must be recoverable |
Posture, detection and response
| Check | Service | Why it matters |
|---|---|---|
| Enable Defender for Cloud on all subscriptions and track secure score | Defender for Cloud Foundational CSPM (free) | Gives a continuous view of misconfigurations against the benchmark |
| Add Defender CSPM for attack path analysis, cloud security explorer, governance rules and agentless scanning | Defender CSPM plan | Prioritises the misconfigurations an attacker could actually chain together |
| Enable workload plans for servers, containers, storage, databases, Key Vault, App Service and Resource Manager | Defender for Cloud CWPP plans | Generates real-time security alerts for each workload type |
| Connect Defender for Cloud, Entra ID and Azure activity logs to a SIEM | Microsoft Sentinel in the Microsoft Defender portal | Correlates signals into incidents and automates response |
| Connect AWS and Google Cloud accounts | Defender for Cloud multicloud connectors | One posture view across clouds |
How does the Microsoft cloud security benchmark tie the checklist together?
The Microsoft cloud security benchmark (MCSB) is the built-in standard that Defender for Cloud assigns to every subscription. It translates security principles into Azure-specific guidance and links each control to Azure Policy definitions, so the checklist above becomes measurable rather than a one-off review.
MCSB v2 is in preview. It adds an Artificial Intelligence Security domain with seven recommendations, more than 420 Azure Policy built-in definitions for automated monitoring, and mappings to NIST SP 800-53 Rev. 5, PCI DSS v4, CIS Controls v8.1, NIST CSF v2.0, ISO/IEC 27001:2022 and SOC 2. Microsoft notes that a mapping shows Azure features can help address a control, not that you are fully compliant with that framework. To keep compliance evidence current between audits, the ElixirData Compliance Agent monitors operations in real time, identifies risks and recommends actions.
| MCSB domain | Main Azure services |
|---|---|
| Network Security (NS) | Private Link, Azure Firewall, DDoS Protection, network security groups |
| Identity Management (IM) and Privileged Access (PA) | Microsoft Entra ID, Conditional Access, Privileged Identity Management, managed identities |
| Data Protection (DP) | Key Vault, Microsoft Purview, encryption at rest and in transit |
| Asset Management (AM) and Posture and Vulnerability Management (PV) | Azure Policy, Defender for Cloud |
| Logging and Threat Detection (LT) and Incident Response (IR) | Microsoft Sentinel, Defender for Cloud alerts |
| Backup and Recovery (BR) | Azure Backup, Azure Site Recovery |
| DevOps Security (DS), Endpoint Security (ES) and Artificial Intelligence Security (AI) | Defender for Cloud DevSecOps, Defender for Servers, AI security posture management |
In what order should enterprises adopt these controls?
A sequence that front-loads identity and visibility gives the biggest risk reduction for the least disruption.
| Step | Action | Outcome |
|---|---|---|
| 1 | Confirm MFA enforcement for all users, deploy phishing-resistant methods for administrators and move automation to workload identities | Stolen passwords stop being enough to reach the control plane |
| 2 | Enable Defender for Cloud on every subscription and review the MCSB secure score | A ranked list of misconfigurations |
| 3 | Assign Azure Policy in audit mode at management group level, then switch proven policies to deny or deployIfNotExists | Guardrails without breaking existing automation |
| 4 | Move PaaS resources behind private endpoints, centralise egress through Azure Firewall and add DDoS Protection to public IPs | A smaller external attack surface |
| 5 | Migrate Key Vault to RBAC, enable purge protection and autorotation, and classify data with Purview | Protected secrets and known sensitive data |
| 6 | Onboard Microsoft Sentinel in the Defender portal and build response automation | Detection and response across Azure and other clouds |
This sequence follows the principle of verifying every request explicitly, described in our guide to implementing Zero Trust security.
How do governance, security and cost interact?
Azure Policy is where security becomes governance. Microsoft advises starting with audit or auditIfNotExists effects before enforcement effects such as deny, modify or deployIfNotExists, because enforcement can break automation already in place. Policies with deployIfNotExists or modify need a managed identity with enough permissions to remediate, and a policy assigned at management group level evaluates resources in its subscriptions and resource groups. Our article on cloud governance challenges and best practices covers the operating model around these guardrails.
Cost rises with capability. Defender for Cloud's Foundational CSPM is free while Defender CSPM and workload plans are billed; Azure Firewall cost increases from Basic to Standard to Premium; and DDoS Network Protection is billed per plan while DDoS IP Protection is billed per IP. Microsoft points to its pricing pages and calculators for regional rates, so model these before you standardise on a tier.
What are the trade-offs, and when should you not use a service?
| Decision | Trade-off | When not to use it |
|---|---|---|
| Azure Firewall Premium | TLS inspection and IDPS add processing that can affect throughput, and Premium has the highest cost | Workloads without regulatory or inspection requirements, where Standard is enough |
| DDoS Network Protection | Plan-based billing pays off with many public IPs | Estates with only a few public IPs, where IP Protection or infrastructure protection may suffice |
| Deny-effect policies | Strong prevention, but they fail deployments that do not comply | Before you have audited the impact on pipelines and autoscaling scripts |
| Key Vault purge protection | Once on, it cannot be disabled, and a deleted vault name stays reserved until retention ends | Short-lived test vaults you need to recreate with the same name |
| Security defaults instead of Conditional Access | Simple tenant-wide MFA, but no per-user or per-app control | Organisations that need exclusions, location or device conditions |
If you want an independent view of where your estate stands, take our cloud security posture assessment.
To map one security or access decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
Is Azure Security Center the same as Microsoft Defender for Cloud?
Yes. Microsoft Defender for Cloud is the current product, and some built-in Azure Policy definitions still carry the older Security Center wording. Defender for Cloud is now a CNAPP covering posture management, DevSecOps and workload protection, with free Foundational CSPM and paid plans.
Is MFA mandatory for Azure?
Yes. Phase 1 enforcement began in October 2024 for the Azure portal, Microsoft Entra admin center and Intune admin center. Phase 2 began on 1 October 2025 for Azure CLI, PowerShell, the mobile app, IaC tools and REST API write operations, and the last postponement date was 1 July 2026.
Which Azure security tools are free?
Defender for Cloud Foundational CSPM, including secure score and the Microsoft cloud security benchmark, is free, as is Azure DDoS infrastructure protection for every public IP. Defender CSPM, workload protection plans, Azure Firewall and the DDoS Protection tiers are paid.
Where is Microsoft Sentinel managed now?
In the Microsoft Defender portal, including for customers without Defender XDR or an E5 licence. After 31 March 2027, Sentinel is no longer supported in the Azure portal.
Should Key Vault use access policies or Azure RBAC?
Azure RBAC. Microsoft describes access policies as a legacy model with known security weaknesses and no Privileged Identity Management support, and RBAC is the default for new vaults from API version 2026-02-01.
Does mapping to the Microsoft cloud security benchmark make us compliant with ISO 27001 or PCI DSS?
No. Microsoft states that the mappings only show which Azure features can fully or partially address a control requirement, which does not by itself mean full compliance with that framework.
For help putting this checklist into practice, explore our cyber security consulting services and Microsoft Azure managed services.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE