Key takeaway
- Microsoft Sentinel SIEM in 2027: the Defender portal move by 31 March 2027, data lake, analytics rules, playbooks, pricing tiers and Security Copilot.
Microsoft Sentinel is Microsoft's cloud-native SIEM (security information and event management) with built-in SOAR (security orchestration, automation and response). In 2026 it is also a security data platform: a data lake for long-term retention, a graph for relationship analysis and a hosted Model Context Protocol (MCP) server for AI agents, all operated from the Microsoft Defender portal.
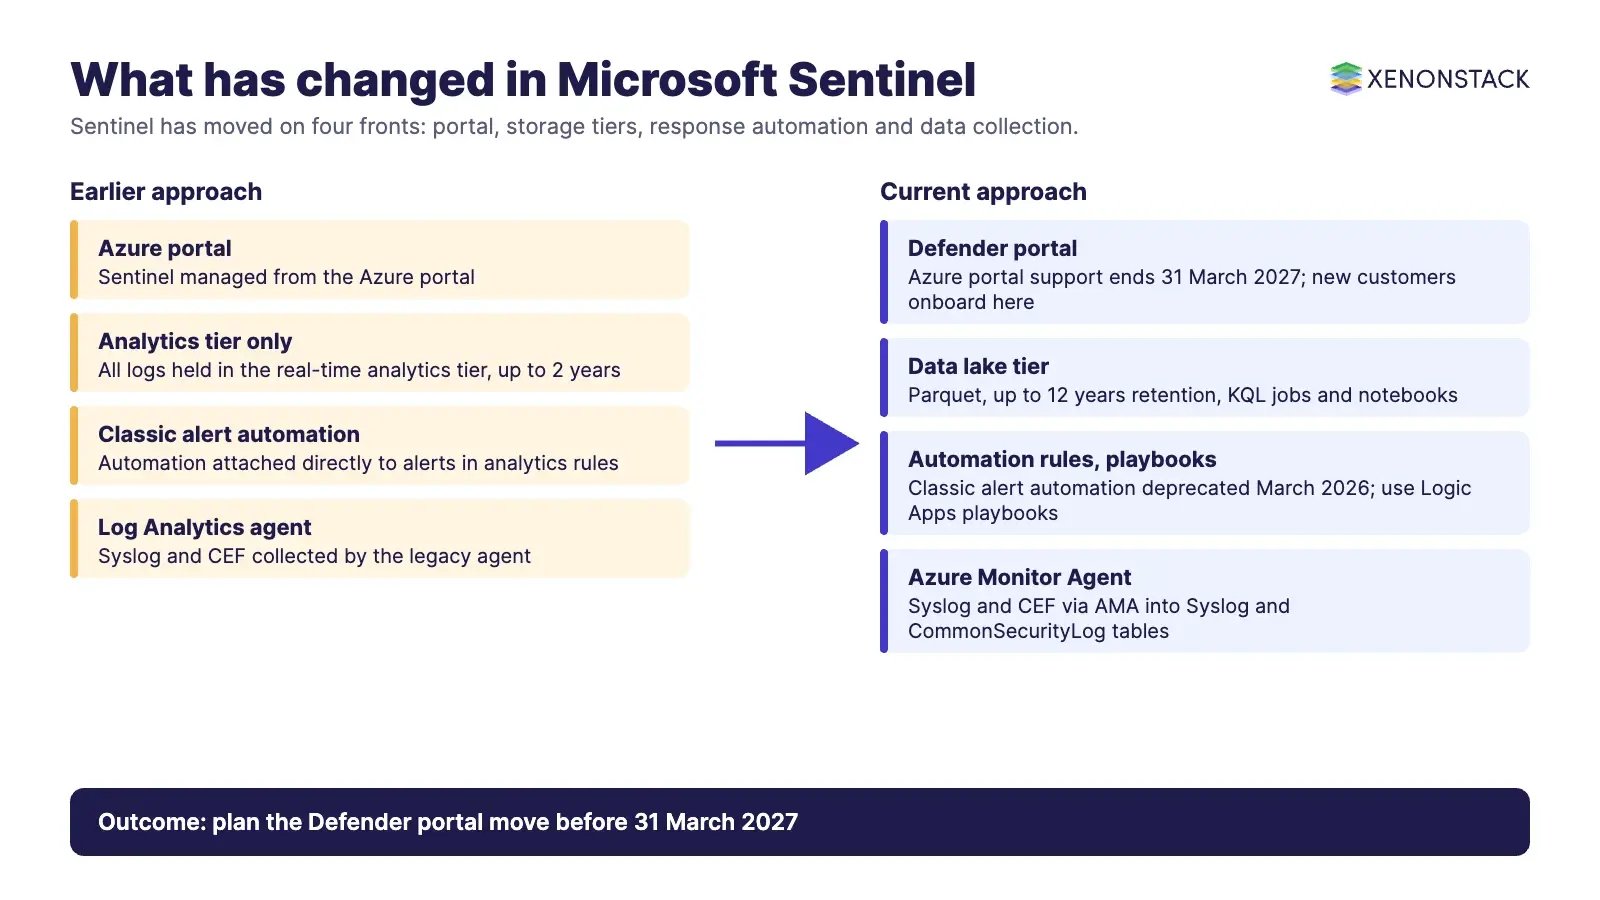
The decision most enterprises now face is not whether Sentinel can detect threats, but how to run it: Microsoft states that after 31 March 2027 Sentinel will no longer be supported in the Azure portal and will be available only in the Defender portal. This guide covers what changed, how the data tiers affect cost, and how to plan adoption or migration.
What is Microsoft Sentinel going into 2027?
Microsoft describes Sentinel as "a cloud-native Security Information and Event Management (SIEM) and unified security platform for agentic defense" (What is Microsoft Sentinel?). The SIEM side handles threat detection, investigation, hunting, response and automated attack disruption across multicloud and multiplatform environments. The platform side adds three components announced as part of the September 2025 update:
- Microsoft Sentinel data lake: a fully managed security data lake, generally available since September 2025, storing a single copy of data in open Parquet format with storage separated from compute.
- Microsoft Sentinel graph: graph analytics that model relationships between users, devices, cloud resources and attacker actions (preview at announcement).
- Microsoft Sentinel MCP server: a hosted interface that lets engineers query security data in natural language and build agents without schema knowledge (preview at announcement).
If you knew the product as Azure Sentinel, the core concepts still apply: data connectors feed a Log Analytics workspace, analytics rules raise alerts and incidents, and automation rules and playbooks respond. What has moved is where you operate it, how data is tiered and how AI is applied on top.
What has changed since the Azure Sentinel days?
| Change | What it means | Current status (per Microsoft Learn) |
| Defender portal becomes the home of Sentinel | SIEM and XDR incidents, hunting and automation in one console, with or without Defender XDR or an E5 licence | Generally available; Azure portal support ends after 31 March 2027 |
| Automatic onboarding for new customers | Tenants onboarding their first workspace from July 2025 (with Owner or User Access Administrator rights, not Lighthouse-delegated) are onboarded to the Defender portal automatically | In effect since July 2025 |
| Sentinel data lake | Low-cost lake tier with up to 12 years of retention, KQL jobs and Jupyter notebooks | Generally available since September 2025 |
| Graph and MCP server | Relationship analysis and agent tooling over Sentinel data | Announced in preview, September 2025 |
| Security Copilot integration | Natural language to KQL, incident analysis and agents that use Sentinel data | Sentinel and Security Copilot integration generally available, September 2025 |
| Classic alert automation | Playbooks attached directly to analytics rules must move to automation rules using the alert created trigger | Deprecated in March 2026 |
Sources: Sentinel SIEM overview, What's new in Microsoft Sentinel, What's new in Security Copilot and Scheduled analytics rules.
How does Microsoft Sentinel collect data?
Microsoft lists more than 350 out-of-the-box data connectors for first-party and third-party security solutions and cloud platforms, including AWS and Google Cloud, plus no-code and custom connector options and data normalisation into a uniform view (source). Connectors are installed as solutions from the Content hub, which also packages analytics rules, hunting queries, workbooks and playbooks.
- Service-to-service connectors: Microsoft 365, Microsoft Entra ID, Microsoft Defender XDR, Defender for Cloud, Purview, Intune and Azure activity. When Sentinel is onboarded to the Defender portal, the Defender XDR connector is enabled automatically.
- Syslog and CEF via the Azure Monitor Agent (AMA): firewalls, proxies and Linux hosts send messages to a log forwarder where the AMA streams them to the workspace, landing in the Syslog and CommonSecurityLog tables. The older Log Analytics agent approach described in earlier guides has been replaced by AMA-based connectors.
- Custom logs and APIs: custom log collection via AMA, the Logs Ingestion API and custom connectors for sources not yet listed.
Several data sources are free to ingest, including Azure Activity logs, Office 365 audit logs (SharePoint, Exchange admin and Teams activity) and security alerts from the Microsoft Defender family. Raw logs from some Defender and Entra ID data types are still charged, so check each data type before enabling it (free data sources).
How do analytics rules detect threats?
Analytics rules turn ingested data into alerts and incidents. Microsoft's threat detection documentation lists the following types:
| Rule type | How it works | When it fits |
| Scheduled | KQL query runs at a set interval over a lookback period; an alert fires when results pass a threshold | Most custom and template detections; the most common rule type |
| Near-real-time (NRT) | Runs every minute on events ingested in the preceding minute, with a two-minute delay instead of the five-minute delay of scheduled rules | High-priority detections where minutes matter |
| Anomaly | Machine learning anomaly templates shown on their own tab | Behavioural baselines and outlier detection |
| Microsoft security | Creates incidents from alerts raised by other Microsoft security products | Estates using Defender products |
| Threat intelligence, Fusion, ML behaviour analytics | Specialised templates that each create a single rule with limited configuration | Indicator matching and multistage attack correlation |
Rule templates come with nearly every Content hub solution. Entity mapping, custom details and alert grouping control how alerts become incidents, which matters for analyst workload. Note that the option to reopen closed incidents is not available once a workspace is onboarded to the Defender portal.
How do automation rules and playbooks handle response?
Sentinel's SOAR layer has two parts (Automation in Microsoft Sentinel):
- Automation rules centrally triage incidents without code: assign owners, tag, change status, suppress noise, add analyst tasks, close incidents, control action order and call playbooks.
- Playbooks are Azure Logic Apps workflows that run response and remediation actions across internal and external systems, for example raising a ticket in an ITSM tool or disabling a user. Logic Apps are separate resources, so additional charges might apply.
In the Defender portal, Microsoft also documents an AI-powered playbook generator that builds Python-based playbooks from natural language in an embedded VS Code environment, without a separate Security Copilot licence (source). Teams moving from the Azure portal should review automation behaviour: alert-trigger automation rules act only on Sentinel alerts, some manual playbook runs on alerts and entities are not supported in the Defender portal, and Defender incidents can take up to five minutes to appear in Sentinel. For a wider view of automated response, see our guide on AI-driven SOAR platforms for incident response. For an agentic SOC built on modular AI agents and protocol-driven automation, see MetaSecure.
How does Security Copilot work with Sentinel?
Security Copilot lets analysts work with Sentinel data in natural language. Documented capabilities include:
- Generating and running KQL hunting queries over Sentinel and Defender XDR tables in advanced hunting (not all Sentinel tables are supported yet) (source).
- Agents such as the Threat Hunting Assistant and the Dynamic Threat Detection Agent, which correlates alerts, events, anomalies and threat intelligence across Defender and Sentinel environments (source).
- Custom agents that use Sentinel MCP tools, such as the entity analyser, which is charged in Security Compute Units (SCUs) (source).
Sentinel commit units and Security Copilot SCUs are separate: one cannot pay for the other. Budget for them independently.
How is Microsoft Sentinel priced?
Microsoft publishes current prices on the Microsoft Sentinel pricing page; rates vary by region and currency, so use that page rather than figures quoted in older articles. The billing model itself is documented in Plan costs and understand Microsoft Sentinel pricing:
| Option | How you pay | When it fits |
| Analytics tier: pay-as-you-go | Per GB ingested, plus retention beyond the included period | Variable or modest volumes, early adoption |
| Analytics tier: commitment tiers | Fixed daily volume starting at 100 GB per day at a discounted effective rate; increase any time, decrease only after 31 days | Predictable, high-volume ingestion |
| Pre-purchase plan | Sentinel commit units bought for a one-year term that pay down eligible analytics tier costs | Organisations with an annual security budget |
| Data lake tier | Separate meters for lake ingestion, data processing, storage (billed at a 6:1 compression rate), queries per GB scanned and notebook compute hours | High-volume, lower-fidelity logs such as firewall, DNS, proxy and NetFlow, and long-term retention |
| Log Analytics dedicated cluster | Shared commitment tier across workspaces in a region ingesting 100 GB per day or more | Multi-workspace estates |
Workspaces created before July 2023 may still be on classic pricing, where Log Analytics charges are billed separately; Microsoft recommends switching to the simplified pricing tiers. Data lake capabilities are not covered by commitment tiers or pre-purchase plans.
How do the analytics and data lake tiers compare?
| Aspect | Analytics tier | Data lake tier |
| Purpose | Real-time detection, alerting, hunting and incident management | Cost-effective long-term storage and deep analytics |
| Retention | Sentinel solution tables can be kept 90 days at no extra retention charge; extendable to two years | Up to 12 years of total retention |
| Access | All Sentinel features, including analytics rules | KQL queries, KQL jobs, Spark and Jupyter notebooks; not used by real-time analytics rules |
| Data copy | Mirrored to the lake automatically | Single copy; jobs can promote data back to the analytics tier for investigations |
Sources: What is Microsoft Sentinel data lake? and Manage data tiers and retention. The data lake can also federate queries to Azure Databricks, ADLS Gen2 and Microsoft Fabric without moving data (preview).
What governance and access controls should you set?
Sentinel uses Azure built-in roles, ideally assigned at resource group level (Roles and permissions):
- Microsoft Sentinel Reader: view data, incidents and workbooks.
- Microsoft Sentinel Responder: Reader rights plus incident management.
- Microsoft Sentinel Contributor: Responder rights plus installing solutions and creating or editing rules and resources.
- Microsoft Sentinel Playbook Operator: list, view and manually run playbooks; Logic App Contributor is needed to create or edit them.
- Microsoft Sentinel Automation Contributor: assigned to the Sentinel service account, not users, so automation rules can run playbooks.
In the Defender portal, Sentinel Reader, Responder and Contributor map to Defender unified RBAC roles, and data lake permissions integrate with unified RBAC. Playbook Operator, Automation Contributor and Workbook Contributor are still managed in the Azure portal.
Two transition caveats matter for regulated organisations (source): customer-managed key (CMK) encryption is not fully supported for data in the Sentinel data lake, which uses Microsoft-managed keys, and alerts and incidents are no longer CMK-encrypted after onboarding; and where Log Analytics query access is restricted to private endpoints through Azure Monitor Private Link Scope, Defender portal experiences such as advanced hunting cannot query that Sentinel data. Keep non-security operational logs in a separate workspace so they do not incur Sentinel charges, and pair Sentinel with identity-focused detections, since insider threats rarely trip perimeter rules. Our Azure security services checklist covers the surrounding controls. When auditors ask how an automated response was approved, the ElixirData Audit Agent assembles decision lineage, policies and approvals for compliance traceability.
How should an enterprise adopt or migrate to Sentinel?
- Decide the portal path first. New deployments start in the Defender portal. Existing Azure portal users should follow Microsoft's transition guidance well before 31 March 2027.
- Classify data by fidelity. Put primary detection sources in the analytics tier and high-volume secondary logs in the data lake tier.
- Connect sources from the Content hub. Start with free Microsoft sources, then identity, endpoint, cloud and network logs via AMA.
- Enable rule templates, then tune. Map entities, group alerts and retire rules that have not fired in 6 to 12 months, as Microsoft's migration guidance suggests.
- Automate low-risk, well-defined steps. Use automation rules for triage and keep human approval for high-impact playbook actions.
- Set a cost baseline. Review ingestion per table, move to a commitment tier when volume stabilises and budget Security Copilot SCUs separately.
For a hands-on walkthrough of workspace and SOC set-up, see Setting up security operations using Azure Sentinel. If you prefer an operated service, our managed cloud SIEM services provide managed threat detection and response.
Sentinel vs Splunk: what does migration involve?
Microsoft provides a SIEM migration experience in the Defender portal that analyses exported Splunk and QRadar detections, including custom ones, and recommends matching Sentinel analytics rules, Defender XDR native detections and the data connectors needed to enable them. It requires Sentinel in the Defender portal and Security Copilot enabled in the tenant, but Microsoft states it does not consume SCUs (SIEM migration experience). Detections without a match are translated manually from SPL to KQL, and Splunk SOAR workflows map to automation rules and playbooks. A fair comparison should weigh your existing Microsoft licensing, the share of Microsoft data sources (some ingest free), query language skills (KQL vs SPL) and multicloud log volumes.
When is Microsoft Sentinel not the right fit?
- Your estate has little Microsoft or Azure footprint, so the free data sources, Defender correlation and unified portal add less value.
- Strict data residency needs fall outside the regions where Sentinel or the data lake are available; check Microsoft's geographical availability list first.
- You rely on Azure portal-only workflows, such as Workspace manager for multi-workspace content deployment (listed as not available in the Defender portal), and cannot rework them before the portal retirement. Microsoft positions the Defender multitenant portal as the replacement surface for cross-tenant incidents and hunting.
- Ingestion is high and unpredictable and you have not yet modelled analytics versus lake tiering; costs can rise quickly without that design work.
To map one incident response decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
Microsoft gives one dated deadline for 2027, and it shapes everything else.
- 31 March 2027: Microsoft states that after this date Sentinel will no longer be supported in the Azure portal and will be available only in the Defender portal.
- Date moved: the what's new page says this date supersedes the earlier July 2026 retirement date, so confirm any older plan against it.
- Start the transition now: Microsoft recommends planning early, and its transition guide covers the steps, including automation and encryption caveats to review before the date.
Frequently asked questions
Is Azure Sentinel the same as Microsoft Sentinel?
Yes. Azure Sentinel is the earlier name; the product is now Microsoft Sentinel, a cloud-native SIEM and security platform.
When will Microsoft Sentinel stop working in the Azure portal?
Microsoft states that after 31 March 2027 Sentinel will no longer be supported in the Azure portal and customers will be redirected to the Microsoft Defender portal.
Do I need Defender XDR or an E5 licence to use Sentinel in the Defender portal?
No. Microsoft says Sentinel is generally available in the Defender portal including for customers without Defender XDR or an E5 licence.
How long can Microsoft Sentinel retain data?
Analytics tier retention can be extended to two years, and total retention in the data lake tier can reach 12 years.
Does the Sentinel data lake replace Log Analytics workspaces?
No. The analytics tier remains the store for real-time detection and hunting; the data lake tier adds low-cost long-term storage, with analytics tier data mirrored to the lake.
Are Security Copilot costs included in Sentinel commitment tiers?
No. Sentinel commit units and Security Copilot Security Compute Units are separate and cannot be used for each other's workloads.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE