What is threat intelligence, and how does it improve security monitoring and incident response?
Threat intelligence is evidence-based knowledge about adversaries, their methods and the indicators they leave behind, turned into something a security team can act on. NIST describes cyber threat information as anything that helps an organisation detect, evaluate, track and respond to cyber threats, including indicators of compromise, attacker methods, recommended defensive steps and incident analysis findings (NIST SP 800-150). Used well, it tells your monitoring what to look for and tells your responders what they are dealing with.
For a CISO or SOC lead, the question is not whether to buy a feed. It is whether intelligence reaches the SIEM, the detection rules and the incident management process in a form people trust, with an owner, a sharing rule and a decision attached. This guide covers the intelligence types, a decision table for tooling, an integration sequence, governance, and where agentic AI changes the work.
Why is threat intelligence critical for security monitoring?
Monitoring without context produces alerts; monitoring with intelligence produces prioritised leads. A file hash, IP address or domain only matters if someone knows whether it is tied to current adversary activity against organisations like yours. Intelligence supplies that link, and detection engineers use adversary behaviour, not only static indicators, to write rules that survive when attackers change infrastructure.
The outcomes security leaders usually look for are:
- Better detection: indicators and behaviours from a STIX and TAXII feed are matched against logs in the SIEM, so known-bad activity is flagged automatically.
- Adversary insight: profiling threat actors and their tactics, techniques and procedures (TTPs) shows which attacks are plausible for your sector and estate.
- Faster, better-informed response: responders start with context on what an indicator means instead of researching it mid-incident.
- Prioritisation: vulnerability and alert queues can be ordered by what is being exploited or targeted, not only by severity scores.
The threat analytics use case describes the analytics layer that sits on top of this data.
What are the types of threat intelligence and the intelligence cycle?
The common split is by audience and time horizon. The labels below are widely used working categories rather than a formal standard, so treat them as a way to decide who consumes what.
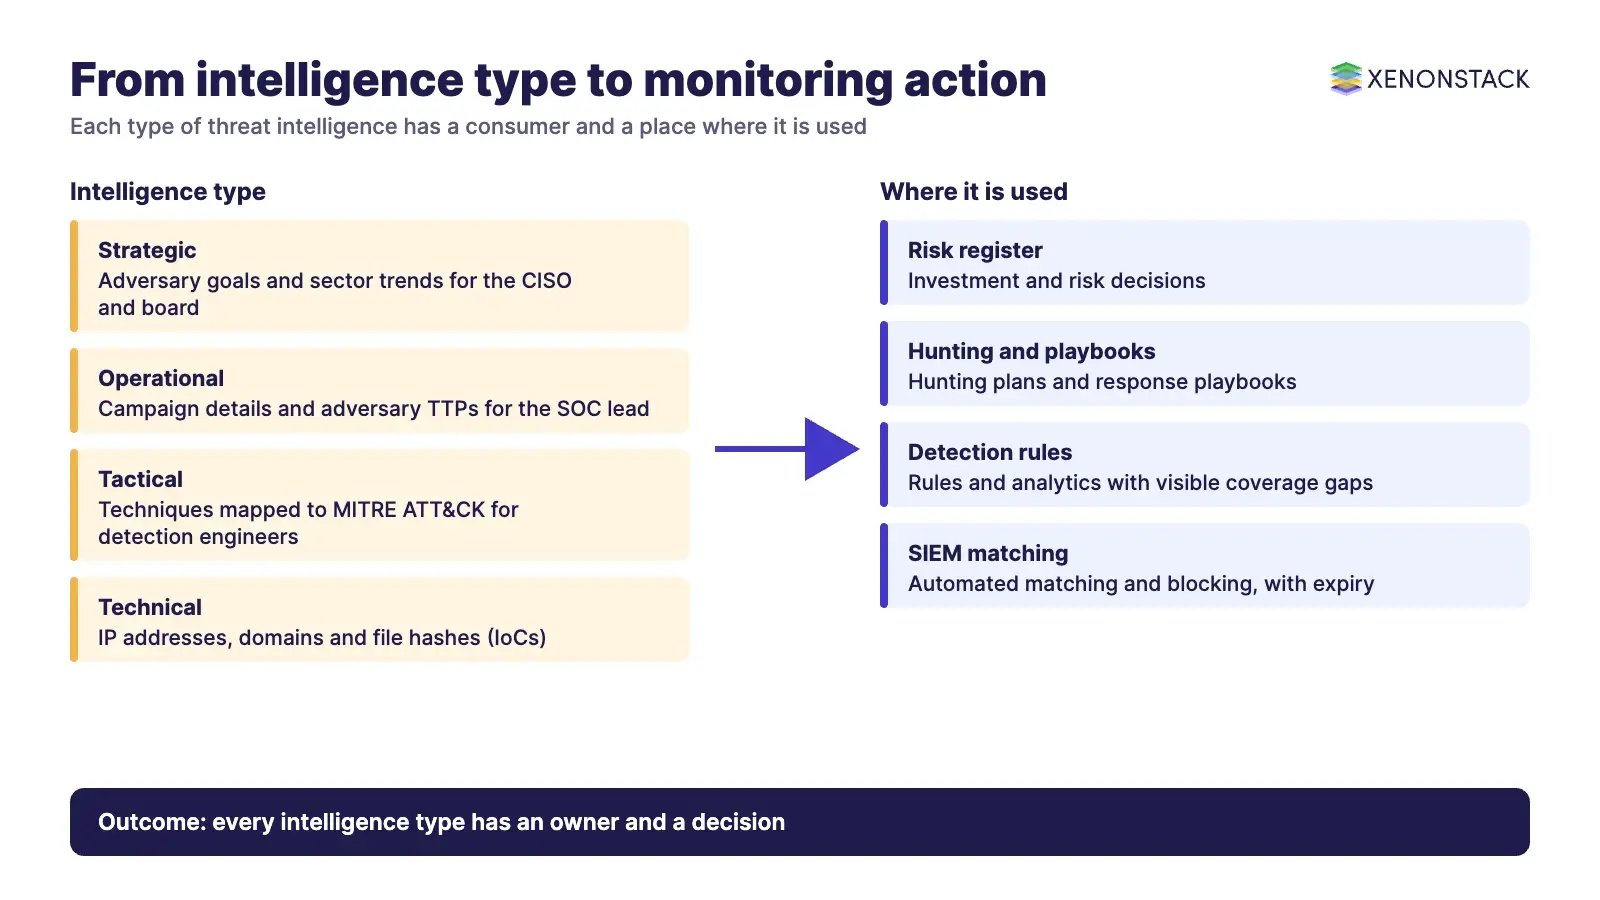
| Type | Typical consumer | Example content | Where it lands |
|---|---|---|---|
| Strategic | CISO, board, risk committee | Adversary goals and sector trends | Risk register, investment decisions |
| Operational | SOC lead, incident commander | Campaign details, adversary TTPs | Hunting plans, response playbooks |
| Tactical | Detection engineers | Techniques mapped to MITRE ATT&CK | Detection rules, analytics |
| Technical | SIEM, EDR, firewalls | IP addresses, domains, file hashes (IoCs) | Automated blocking and matching |
Behind every type sits the same cycle: decide what you need to know, collect from sources such as open-source intelligence, internal telemetry, commercial feeds and sharing communities, analyse the data into a judgement, and disseminate it to the people who must act, then collect feedback and refine. NIST SP 800-150 covers the practical side: setting sharing goals, choosing sources, defining the scope of sharing, publishing rules, joining sharing communities and using the information in a wider security programme.
Which open standards make intelligence usable?
- STIX 2 is a structured language for exchanging cyber threat intelligence in a consistent, machine-readable form; TAXII 2.1 is the application-layer protocol, run over HTTPS, that carries STIX between systems (OASIS CTI documentation).
- MITRE ATT&CK is described by MITRE as a knowledge base of adversarial techniques based on real-world observations, organised into tactics, techniques, sub-techniques and procedures. It gives analysts a shared vocabulary; according to its site, the current content release is v20.1.
- FIRST Traffic Light Protocol (TLP) 2.0 labels how widely a piece of intelligence may be shared: TLP:RED, TLP:AMBER (including AMBER+STRICT), TLP:GREEN and TLP:CLEAR. It is a sharing convention, not a formal classification scheme.
Which threat intelligence tools and platforms fit which need?
Threat intelligence platforms (TIPs) aggregate, deduplicate and score feeds, then push indicators to enforcement points. They are one part of a wider toolset, and the right choice depends on who consumes the output. Vendor features and pricing change often, so check each product against its own documentation before you shortlist.
| Capability | What it does | When it fits | Watch for |
|---|---|---|---|
| Threat intelligence platform | Aggregates and normalises feeds, often via STIX and TAXII | Several sources, several consumers | Feed noise and stale indicators |
| SIEM with intelligence matching | Matches indicators to logs and raises alerts | Central log monitoring already exists | Rules that match but nobody triages |
| Behavioural analytics | Flags unusual user or network activity without a known indicator | Attacks that reuse no known infrastructure | False positives without tuning |
| Vulnerability management | Finds and prioritises exposures | Patching capacity is limited | Needs exploitation context to rank |
| Threat hunting | Analysts test hypotheses drawn from adversary behaviour | Mature monitoring, skilled analysts | Hunts without a feedback loop |
XenonStack's guides on Microsoft Sentinel, the Security Operations Centre, behavioural analytics for SOC automation and AI-driven threat hunting go deeper on each layer, and machine learning in security covers the detection models behind several of them.
How do you integrate threat intelligence into security monitoring?
Sequence matters more than tool choice. A programme that starts with feeds and no use case tends to flood the SIEM with indicators nobody acts on.
- Define the requirements. Agree which decisions intelligence must support, for example which alerts to escalate, which vulnerabilities to patch first, which adversaries matter to your sector.
- Inventory your monitoring. Know which log sources, detection tools and alert routes exist, so intelligence has somewhere to land.
- Choose sources by fit, not volume. Combine internal incident data, open-source intelligence, sector sharing communities and commercial feeds, and record the reliability of each.
- Normalise and score. Use STIX 2 objects and a TIP or SIEM connector, and expire indicators so stale data does not generate alerts.
- Map to behaviour. Tag detections with MITRE ATT&CK techniques so coverage gaps are visible against the adversaries you care about.
- Set sharing rules. Apply TLP labels and decide what you receive and publish, following the scope guidance in NIST SP 800-150.
- Close the loop. Feed incident findings back into collection requirements, and review which sources actually led to detections.
What should you check before trusting an intelligence source?
- Relevance: does it cover your sector, technology stack and geography?
- Timeliness: how quickly are indicators published and retired?
- Accuracy: what is the false-positive rate once matched against your own logs?
- Integration: can it reach your SIEM and response tools in a machine-readable format?
- Sharing terms: what are the TLP or licence restrictions on use and onward sharing?
How does threat intelligence improve incident response and recovery?
NIST published SP 800-61 Revision 3 in April 2025 as a CSF 2.0 Community Profile, replacing the 2012 Revision 2. It frames incident response as part of cybersecurity risk management, with the aim of improving preparation, reducing the number and impact of incidents, and making detection, response and recovery more efficient and effective. Intelligence supports that at each step.
Faster detection and triage
Matching indicators and behaviours to telemetry gives early warning, and enrichment tells the analyst what an alert may mean before the first call is made.
Better scoping
Knowing an adversary's usual techniques helps responders decide which systems and data to check, and where else the same activity may be present.
More effective containment and recovery
Intelligence on how an attack progresses helps teams choose containment steps, and incident findings become new indicators and detections for the next time. For the operational side, see XenonStack's incident management guide.
What are the benefits and the trade-offs?
| Benefit | Trade-off or when it does not help |
|---|---|
| Earlier warning of relevant attacks | Generic feeds with no relevance filter add noise, not warning |
| Prioritised alerts and patching | Needs asset and exposure data to rank anything |
| Shared vocabulary across SOC, IR and risk teams | Needs ATT&CK mapping discipline to stay consistent |
| Sector and peer learning through sharing | Sharing needs rules (TLP) and legal review |
| Feedback that improves detections | Only if incident findings are recorded and reused |
If you have no central logging or no incident process, fix those first. Intelligence has nothing to enrich and no one to hand it to.
What governance and security controls should surround a threat intelligence programme?
Intelligence is data about adversaries and sometimes about your own incidents, so it needs the same controls as other sensitive data.
- Ownership: name a programme owner and the people accountable for each consuming system.
- Sharing rules: label with TLP 2.0, and record who approved publication outside the organisation.
- Source register: track provenance, licence terms and reliability for each feed.
- Retention and expiry: expire indicators on a schedule and log why detections were changed or retired.
- Audit trail: keep a record of what intelligence triggered which automated action, and who approved it.
How is agentic AI changing threat intelligence work?
The routine work (enriching an indicator, summarising a report, drafting a detection, proposing a containment step) is increasingly done by AI agents working alongside analysts. The open question for security leaders is control: an agent that can isolate a host or block a domain needs policy limits, an approval path and a record of why it acted. XenonStack's guides on agentic AI cybersecurity challenges and AI-driven threat hunting cover the risks and techniques.
According to its site, ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents. AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need, and the Audit Agent assembles the decision record, the policy version in force and the approval chain when an auditor asks why an action was taken.
What will change in threat intelligence over the next few years?
No reliable public forecast gives hard numbers here, so this is a direction of travel, not a prediction. Standards such as STIX 2.1 and TAXII 2.1 make machine-to-machine exchange routine, and NIST's 2025 incident response guidance ties response to wider risk management. Expect more automation in enrichment and triage, more emphasis on behaviour mapped to ATT&CK than on raw indicator lists, and closer links between SOC tooling and behavioural analytics. The control question, who approved the automated action, will matter as much as detection speed.
Key takeaways
- Threat intelligence is useful when it reaches a decision: a detection, an escalation, a patch order or a containment step.
- Start with requirements and monitoring coverage, then choose sources and tools.
- Use open standards (STIX 2.1, TAXII 2.1, MITRE ATT&CK, TLP 2.0) so intelligence moves between tools and teams.
- Govern sources, sharing and any automated action with owners and records.
- Where AI agents act on intelligence, keep policy limits and an audit trail in place.
To map one security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is cyber threat intelligence?
Per NIST SP 800-150, cyber threat information is anything that helps an organisation detect, evaluate, track and respond to cyber threats, including indicators of compromise, attacker methods, defensive recommendations and incident findings. Intelligence is that information analysed and made actionable.
What are indicators of compromise?
They are data points such as IP addresses, domains, URLs and file hashes associated with known malicious activity. They are useful for automated matching but go stale quickly, so pair them with behaviour-based detections.
What are STIX and TAXII?
STIX is a structured language for describing cyber threat intelligence, and TAXII is the HTTPS-based protocol that transports STIX between systems. Together they let tools exchange intelligence in a machine-readable way.
What is MITRE ATT&CK used for in threat intelligence?
MITRE describes it as a knowledge base of adversarial techniques based on real-world observations. Teams use it as a shared vocabulary to map adversary behaviour to detections and to see coverage gaps.
What does the Traffic Light Protocol do?
FIRST's TLP 2.0 uses four labels (RED, AMBER, GREEN, CLEAR) to tell recipients how far intelligence may be shared. It is a sharing convention, not a formal classification scheme.
How does the latest NIST guidance relate to incident response?
NIST SP 800-61 Revision 3 (April 2025) replaces the 2012 Revision 2 and is a CSF 2.0 Community Profile that places incident response inside cybersecurity risk management.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE