Key takeaway
- Agentic AI security for enterprises: where agents leak personal and confidential data, the controls that work, and what GDPR and the EU AI Act expect.
Agentic AI security is the discipline of stopping software agents from exposing, misusing or retaining data they should not touch while they act on your behalf. The privacy risk is larger than for a chatbot, because an agent holds credentials, calls tools, writes to memory and passes data to other agents. The practical answer has four parts: give each agent the least access it needs, enforce authorisation outside the model, require human approval for high-impact actions, and keep a record of every action that touched personal or confidential data.
This guide is written for CISOs, CIOs, data protection leads and architects who are moving agentic AI into production. It covers where agents leak data, what changed in standards and regulation during 2026, which controls matter first, and how to sequence adoption. For the wider threat picture (adversarial attacks, model theft, red teaming) read our companion post on cybersecurity challenges in agentic AI; this post stays on data protection and privacy.
Why is data privacy the hardest part of agentic AI security?
A traditional application reads the data its code was written to read. An agent decides at run time which tools to call and which records to pull, so its data footprint is set by its permissions rather than by a fixed design. OWASP names this directly as Excessive Agency: "the vulnerability that enables damaging actions to be performed in response to unexpected, ambiguous or manipulated outputs", with three root causes of excessive functionality, excessive permissions and excessive autonomy.
Privacy adds a second problem. Even a correct action can be unlawful if it uses personal data for a purpose nobody approved, or if an agent copies that data into memory, logs or another agent's context. Security teams therefore need to treat the agent's tool access, memory and message traffic as data stores in their own right.
What has changed in agentic AI security in 2026?
Three bodies moved from general AI risk to agent-specific guidance. The table lists what is published and what it means for a privacy programme.
| Source | What it says | Current status (read 12 Nov 2026) |
|---|---|---|
| OWASP Top 10 for Agentic Applications 2026 | A peer-reviewed list of the most critical risks for autonomous and agentic systems, developed with more than 100 experts. As reported by Giskard, it covers goal hijack, tool misuse, identity and privilege abuse, agentic supply chain, unexpected code execution, memory and context poisoning, insecure inter-agent communication, cascading failures, human-agent trust exploitation and rogue agents. | Published 9 December 2025 |
| OWASP Top 10 for LLM Applications 2025 | Includes LLM02 Sensitive Information Disclosure and LLM06 Excessive Agency, the two entries most relevant to data protection. | 2025 edition is current |
| NIST CAISI request for information on securing AI agent systems | Asks about agent-specific threats such as indirect prompt injection and data poisoning, and about deployment controls including limiting and monitoring agent access. NIST says responses will inform future voluntary guidelines. | Issued 12 January 2026; comments closed 9 March 2026 |
| EU AI Act | Governance and enforcement apply from 2 August 2026. High-risk obligations for Annex III use cases were extended to 2 December 2027 and for Annex I products to 2 August 2028. | In force; the AI Omnibus entered into force 27 July 2026 |
The common thread is that regulators and standards bodies now expect you to limit and monitor what an agent can reach, not only to test the model.
Where do AI agents leak personal and confidential data?
Most leaks come from five places. The mapping below ties each to the OWASP entry that describes it, so your security and privacy teams can use one vocabulary.
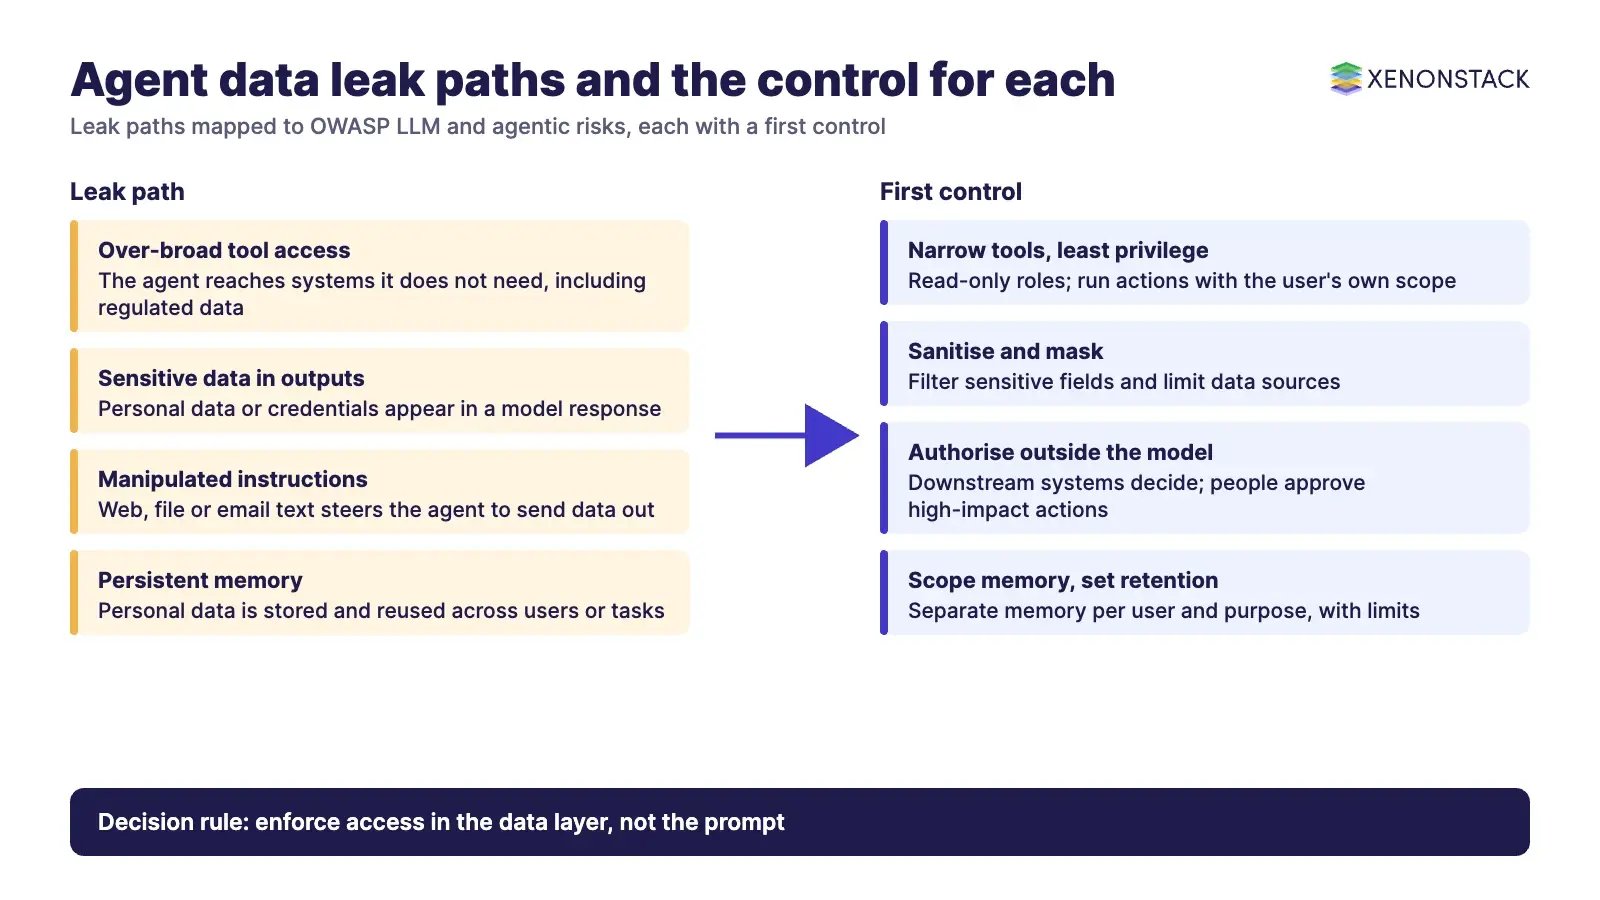
| Leak path | How it happens | First control | OWASP reference |
|---|---|---|---|
| Over-broad tool access | The agent can read or write systems it does not need, so one bad instruction reaches regulated data | Narrow, purpose-built tools; read-only roles where possible | LLM06 Excessive Agency; ASI03 Identity and Privilege Abuse |
| Sensitive data in outputs | The model returns personal data, credentials or confidential details in a response | Sanitise inputs, mask sensitive fields, apply least privilege on data sources | LLM02 Sensitive Information Disclosure |
| Manipulated instructions | Text in a web page, file or email steers the agent to send data elsewhere | Treat external content as untrusted; human approval for privileged actions | LLM01 Prompt Injection; ASI01 Agent Goal Hijack |
| Persistent memory and context | Personal data is stored in agent memory or retrieval stores and reused for other users or tasks | Scope memory per user and purpose; set retention limits | ASI06 Memory and Context Poisoning |
| Agent-to-agent and third-party links | Messages between agents, or plug-ins and skills from outside, carry data past your controls | Authenticate each agent; vet third-party tools before approval | ASI07 Insecure Inter-Agent Communication; ASI04 Agentic Supply Chain Vulnerabilities |
OWASP adds a caution that matters for privacy teams: restrictions written into a system prompt "may not always be honored and could be bypassed via prompt injection or other methods". A prompt is not an access control.
Which controls protect data in agentic AI systems first?
Limit what the agent can do
OWASP recommends offering only the functions an application needs, avoiding open-ended tools such as ones that run arbitrary shell commands, and limiting downstream access, for example with read-only database roles. Where possible the action should run under the user's own identity with the minimum scope. For the architecture behind this, see our post on zero trust security architecture, which treats every request as untrusted until verified.
Enforce authorisation outside the model
OWASP's guidance is to "implement authorization in downstream systems rather than relying on an LLM to decide if an action is allowed or not". In practice the data store or API decides, and the agent only asks. This one rule removes most of the damage from prompt injection.
Put a person in front of high-impact actions
OWASP recommends human-in-the-loop control so a person approves high-impact actions before they are taken. Define "high-impact" in policy: bulk export of personal data, changes to access rights, payments, and anything sent outside the organisation.
Keep an inventory, runtime monitoring and data loss prevention
The security guidance our own solution teams use starts with an inventory of every agent: authorised, unauthorised, employee-created and third-party, including agents embedded in SaaS tools. Technical controls then add runtime monitoring, security guardrails, isolation, data loss prevention and tool-level access control. OWASP notes that logging, monitoring and rate limiting do not prevent excessive agency but do limit the damage, so they complement the controls above rather than replace them.
What do GDPR and the EU AI Act mean for AI agents?
Two points apply to most enterprises. First, GDPR Article 22 gives individuals the right "not to be subject to a decision based solely on automated processing" where the decision has legal or similarly significant effects. Where the exceptions apply, the controller must provide safeguards that include "the right to obtain human intervention". An agent that approves credit, screens candidates or changes entitlements needs a documented human route. Source: GDPR Article 22.
Second, the EU AI Act's governance and enforcement provisions apply from 2 August 2026, while high-risk obligations for Annex III use cases now run to 2 December 2027, according to the European Commission. Teams should not treat the extension as a pause: the evidence you will need (decision records, approvals, policy versions) takes time to build. For sector rules such as HIPAA or CCPA and for cross-border transfers, ask your legal counsel to confirm the position for each agent use case. Our post on agentic AI in data governance and compliance covers the compliance workflow, and agentic AI for risk management covers the risk side.
How should enterprises govern agents that touch regulated data?
Governance means a named owner per agent, a policy that says what data it may use and for what purpose, and evidence that the policy was applied. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. For risk and compliance teams, AgentGRC provides governance, risk and compliance controls for autonomous agent actions, and the Audit Agent assembles decision lineage, policy versions, approvals and authority chains for compliance teams. XenonStack builds ElixirClaw, ElixirData and these agents, so treat this as a vendor view and check each claim against its product page.
| Governance question | Evidence to keep | Who owns it |
|---|---|---|
| Which agents exist and what can they reach? | Agent inventory with tools, data sources and permissions | CISO and platform lead |
| Was this use of personal data allowed? | Policy version, purpose and data category per action | Data protection lead |
| Who approved the high-impact action? | Approval record and authority chain | Business owner |
| Can we reconstruct what happened? | Logs of tool calls, inputs and outputs, retained to policy | Security operations |
What does agent governance look like in practice?
In what order should you secure agent adoption?
| Step | What to do | Done when |
|---|---|---|
| 1. Inventory | List every agent, tool, data source and credential, including shadow and third-party agents | No agent runs without an owner |
| 2. Classify | Mark which data categories each agent may read or write | Personal and regulated data are tagged |
| 3. Restrict | Apply least privilege, narrow tools and downstream authorisation | The agent fails safely when asked for more |
| 4. Approve | Add human approval for high-impact actions | Approval rules are written in policy |
| 5. Monitor and test | Run runtime monitoring, logging and adversarial tests such as prompt-injection assessments | Incidents can be traced to a tool call |
| 6. Review | Re-assess after each model, tool or regulatory change | Review cycle is scheduled |
What are the trade-offs, and when should an agent not have access?
Tighter controls slow agents down. Human approval adds latency, narrow tools reduce flexibility, and per-user memory limits personalisation. Accept those costs where the data is regulated or the action cannot be undone.
- Do not give an agent write access to systems of record until read-only operation has run cleanly.
- Do not let an agent make decisions with legal or similarly significant effects on individuals without a human route.
- Do not connect third-party tools or skills that nobody on your team has reviewed.
- Do not rely on a system prompt to protect data; enforce the rule in the data layer.
To map one decision your agents make on personal data, and the policy and access it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is agentic AI security?
It is the set of controls that stop AI agents from exposing or misusing data and systems while they act autonomously. It covers tool permissions, authorisation, memory, approvals and audit records.
What is excessive agency?
OWASP defines it as the vulnerability that enables damaging actions in response to unexpected, ambiguous or manipulated outputs. Its root causes are excessive functionality, excessive permissions and excessive autonomy.
Is a system prompt enough to stop an agent leaking data?
No. OWASP warns that system prompt restrictions may not always be honoured and can be bypassed through prompt injection. Enforce access in the downstream system.
Does GDPR apply to AI agent decisions?
Article 22 gives individuals the right not to be subject to a decision based solely on automated processing that has legal or similarly significant effects, with safeguards that include human intervention where the exceptions apply. Confirm the position for each use case with counsel.
When do EU AI Act obligations apply?
According to the European Commission, governance and enforcement apply from 2 August 2026, high-risk Annex III obligations were extended to 2 December 2027, and Annex I product obligations to 2 August 2028.
If you are also evaluating the security of the wider platform, our posts on zero trust and agentic AI cybersecurity are good next reads.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.