What are AWS security services, and who is responsible for what?
AWS security services are the managed tools AWS provides for identity, logging, configuration, threat detection, vulnerability management, data protection and posture reporting. The core set most enterprises start with is IAM, AWS CloudTrail, AWS Config, Amazon GuardDuty, Amazon Inspector, Amazon Macie, AWS KMS and AWS Security Hub. They protect your workloads only after you switch them on and configure them, because AWS secures the cloud and you secure what you put in it.
For CISOs and cloud architects, the practical question is which service closes which gap, in what order, and what AWS no longer expects you to do by hand. This guide answers that and pairs with our views on Azure security services and Google Cloud security, so a multi-cloud estate can be compared on the same terms.
How does the AWS shared responsibility model split security work?
Under the AWS shared responsibility model, AWS is responsible for protecting the infrastructure that runs its services: hardware, software, networking and facilities. Your share depends on the services you choose. For an EC2 instance you manage the guest operating system, the security group configuration, your data and its encryption options, and access through IAM. For abstracted services such as Amazon S3 and Amazon DynamoDB, AWS operates the infrastructure layer, the operating system and the platform, while you still own data, encryption choices and permissions.
AWS also separates controls into three groups, which is a useful way to build an audit matrix:
| Control type | Who owns it | Example from AWS |
|---|---|---|
| Inherited | AWS | Physical and environmental controls |
| Shared | Both, each in its own context | Patch management (AWS patches the infrastructure, you patch your guest OS and applications), configuration management, awareness and training |
| Customer-specific | You | Zone security and data routing, set by the application you deploy |
Source: AWS shared responsibility model page, read 12 Nov 2026.
Which AWS security service does which job?
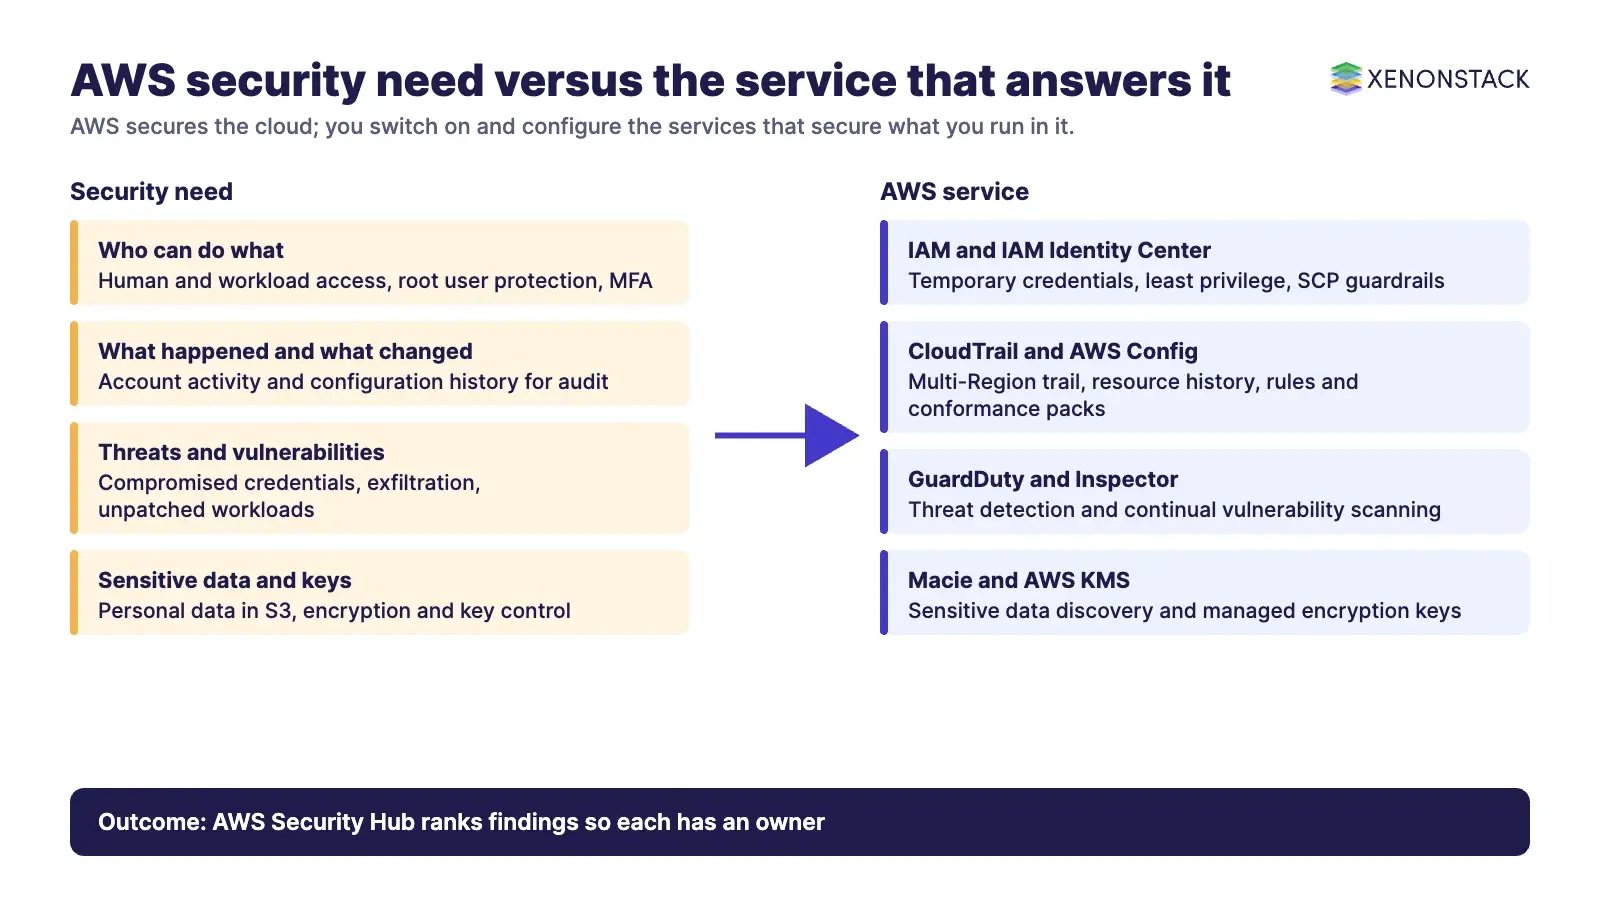
Use this table to match a need to a service. It covers the services most often asked about by enterprise teams, not every AWS security offering.
| Service | What it does | When it fits | Current status or note |
|---|---|---|---|
| AWS IAM and IAM Identity Center | Controls who can do what, with temporary credentials, MFA and policy guardrails | Always; it is the first control to get right | AWS recommends federation and IAM Identity Center for people, and IAM roles for workloads |
| AWS CloudTrail | Records account activity into S3, with optional delivery to CloudWatch Logs and EventBridge | Audit trail and investigation across all Regions and accounts | Multi-Region trails are recommended; organisation trails cover all member accounts |
| AWS Config | Records resource configuration history and evaluates it against rules and conformance packs | Detecting drift and misconfiguration; evidence for audits | An aggregator gives one view across accounts and Regions; Security Hub CSPM needs Config recording for most control findings |
| Amazon GuardDuty | Threat detection from CloudTrail management events, VPC flow logs and DNS logs, plus optional protection plans | Finding compromised credentials, data exfiltration, cryptomining and malware | Extended Threat Detection for multi-stage attacks is enabled automatically at no extra cost |
| Amazon Inspector | Continual vulnerability and network exposure scanning | EC2 instances, container images in Amazon ECR and Lambda functions | Rescans when a package or patch changes or a new CVE is published |
| Amazon Macie | Discovers sensitive data in S3 and monitors bucket security | Finding personal or regulated data and publicly accessible buckets | Uses machine learning and pattern matching |
| AWS KMS | Creates and controls encryption and signing keys | Customer-managed keys, key policies, separation of duties | Keys are protected by FIPS 140-3 Security Level 3 validated hardware security modules |
| AWS Security Hub | Correlates signals from GuardDuty, Inspector and Security Hub CSPM into prioritised risk | One place to rank and act on findings | Generally available from 2 Dec 2025; Security Hub CSPM remains the posture-checking component |
Sources: AWS documentation for each service, read 12 Nov 2026.
What GuardDuty protection plans add
Amazon GuardDuty starts with foundational data sources and then extends through protection plans: S3 Protection, EKS Protection, Malware Protection (EC2, S3 and AWS Backup), RDS Protection, Lambda Protection and Runtime Monitoring. On first enablement GuardDuty turns on all plans except Runtime Monitoring, and you can disable any plan. For multiple accounts, AWS recommends managing GuardDuty through AWS Organizations.
What has changed in AWS security recently?
| Change | What it means for you | Date or source |
|---|---|---|
| AWS Security Hub is now a unified service that correlates GuardDuty, Inspector and Security Hub CSPM signals | Plan around risk-based prioritisation instead of reading each service's findings separately. The older posture-checking product is now called Security Hub CSPM | Generally available 2 Dec 2025 (AWS announcement) |
| Exposure findings combine traits such as misconfiguration, vulnerability and reachability | A vulnerable resource that is reachable from the internet ranks higher. Findings include an attack path and can be exported in OCSF format | AWS Security Blog on exposure findings |
| New S3 object uploads are encrypted by default with SSE-S3 (AES-256) | Encryption at rest on S3 is no longer a switch you forget. Use KMS keys when you need key control and audit | Applied from 5 Jan 2023 (AWS S3 documentation) |
| Root user MFA is expected, and root access can be managed centrally in AWS Organizations | Remove root credentials from member accounts where possible and use an SCP if they remain | AWS root user best practices |
| GuardDuty Extended Threat Detection finds multi-stage attack sequences | Sequences that look harmless as single events can be reported as one attack sequence finding | AWS GuardDuty documentation |
Which compliance programmes does AWS support, and what remains yours?
AWS says it has dozens of assurance programmes. The AWS compliance programmes page lists, among others, SOC 1, SOC 2 and SOC 3, PCI DSS, FedRAMP, FISMA, ISO 27001, ISO 27017, ISO 27018 and ISO 9001. ISO 27017 covers security controls for cloud services and ISO 27018 covers protection of personal data in the cloud. These attestations cover the AWS infrastructure. Whether your workload meets a standard depends on how you configure it, so treat the reports as inputs to your own control mapping, not as proof of your compliance.
AWS Config conformance packs and AWS Security Hub CSPM standards (AWS Foundational Security Best Practices, CIS, PCI DSS and NIST) turn that mapping into automated checks. See our guide to cloud governance for how the policy layer sits above the tooling.
Which threats do AWS security services address, and which control answers each?
| Threat | First control to apply | Detection or evidence |
|---|---|---|
| Misconfigured S3 bucket or IAM role | Least-privilege policies, IAM Access Analyzer, SCP guardrails | AWS Config rules, Macie policy findings, Security Hub CSPM |
| Stolen or leaked credentials | Temporary credentials, MFA, no root access keys | GuardDuty credential findings, CloudTrail |
| Unpatched vulnerability or zero-day exposure | Patch management on your side of the shared model | Inspector scans and rescans; exposure findings |
| Data exfiltration | Encryption, bucket policies, private access paths | GuardDuty S3 Protection, Macie |
| Insider misuse | Least privilege, review and removal of unused credentials | CloudTrail, GuardDuty, access last used information |
| Third-party or supply chain compromise | Scan container images and functions; restrict cross-account access | Inspector for ECR and Lambda, IAM Access Analyzer |
Mappings are our synthesis of AWS documentation, not an AWS claim.
In what order should an enterprise adopt AWS security services?
The sequence below follows AWS guidance and keeps the early steps cheap and reversible.
- Secure identity first. Follow the root user best practices: use the root user only for tasks that need it, enable MFA, do not create root access keys, and remove root credentials from member accounts where Organizations allows it. For people, use federation or IAM Identity Center; for workloads, use IAM roles. See Identity and Access Management for the principles.
- Turn on logging. Create a multi-Region organisation trail in AWS CloudTrail and monitor root sign-ins and usage.
- Record configuration. Enable AWS Config, choose resource types and use an aggregator across accounts and Regions.
- Enable detection. Turn on Amazon GuardDuty and Amazon Inspector in every account through Organizations, then add Macie where sensitive data sits in S3.
- Protect data. Rely on S3 default encryption as the baseline and use AWS KMS where you need key policies and audit.
- Aggregate and prioritise. Use AWS Security Hub to rank risk across services and route findings to ticketing or response automation.
- Codify it. Put these settings in templates so every new account starts secure. See infrastructure as code on AWS and the DevSecOps pipeline on AWS.
Video: from detection to governed containment
ElixirData walkthrough of threat detection through governed response. It is a general illustration, not an AWS-specific demonstration.
What is an AWS security checklist for enterprises?
This checklist replaces the earlier two-part list. It is based on AWS IAM security best practices and the service documentation above. Each line is a control you can test.
- Humans sign in through federation with temporary credentials; workloads use IAM roles.
- MFA is required for the root user and for any IAM user, with phishing-resistant methods such as passkeys or security keys preferred.
- No access keys exist for the root user, and long-term access keys are rotated or removed when they are not needed.
- Permissions start from AWS managed policies and move towards least privilege, using IAM Access Analyzer to generate and validate policies.
- Unused users, roles, permissions and credentials are reviewed and removed regularly.
- SCPs and resource control policies set guardrails across accounts.
- A multi-Region organisation trail is on, with log delivery to a protected S3 bucket.
- AWS Config records resources, with rules or conformance packs for your required standards.
- GuardDuty and Inspector are enabled in every account and Region you use.
- Sensitive data in S3 is discovered and classified, and encryption keys are managed in KMS where you need control.
- Public and cross-account access is verified before it is granted.
- Findings reach a team or an automated workflow that has a named owner.
What are the trade-offs, and when are AWS services not enough?
- Dependencies. AWS Security Hub CSPM needs AWS Config recording to produce most control findings, and it only processes findings in the Region where it is enabled unless you aggregate.
- Noise and ownership. More detectors create more findings. Without an owner and a triage path, the extra signal is not acted on.
- Scope. These services see AWS. If you also run Azure or Google Cloud, you need a common control model; see Azure security services and Google Cloud security.
- Cost. Pricing differs by service and by usage. Use the AWS pricing pages and the Security Hub cost estimator before enabling every plan.
- Skills. If you lack a 24x7 team, managed security services can run triage while you keep policy ownership.
How do AI agents change AWS security governance?
Teams that run AI agents on AWS give those agents IAM roles, API access and data permissions. The same least-privilege and audit rules therefore apply to agents as to people, and an agent's decisions need a record. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. Use them alongside, not instead of, the native AWS controls above.
Key takeaways: AWS security services
Start with identity, logging and configuration, add detection with GuardDuty and Inspector, protect data with S3 default encryption and KMS, and use Security Hub to prioritise. Know what AWS owns and what you own, and keep a named owner for every finding. For related reading, see cloud security, big data security and DevSecOps pipeline on AWS.
- Discover more about Cloud Managed Services
- Explore More about Kubernetes Managed Platforms
- Know More about Managed Security Services
To map one cloud security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
The year ahead is best used to close basic gaps before adding more tools, following the adoption order set out above.
- Secure identity first. Require MFA for the root user, keep no root access keys, and use federation with temporary credentials for people and IAM roles for workloads.
- Switch on the core services in every account. Enable CloudTrail, AWS Config, GuardDuty and Inspector through Organizations, and give every finding a named owner and a triage path.
- Prioritise and codify. Use AWS Security Hub to rank risk across services, and put your settings in templates so each new account starts secure.
Treat AI agents on AWS like people: least privilege, a scoped role and an audit record.
Frequently asked questions about AWS security services
What are the main AWS security services?
The services most enterprises start with are IAM and IAM Identity Center, CloudTrail, AWS Config, GuardDuty, Inspector, Macie, KMS and Security Hub. Each covers a different job: identity, audit trail, configuration, threat detection, vulnerability scanning, sensitive data discovery, key management and risk prioritisation.
What does the AWS shared responsibility model mean in practice?
AWS protects the infrastructure that runs its services. You are responsible for what you deploy and configure, such as guest operating systems on EC2, security groups, your data and its encryption choices, and IAM permissions. AWS also describes inherited, shared and customer-specific controls.
What is the difference between AWS Security Hub and Security Hub CSPM?
Security Hub CSPM checks your environment against standards such as AWS Foundational Security Best Practices, CIS, PCI DSS and NIST. The generally available AWS Security Hub, announced on 2 Dec 2025, correlates signals from GuardDuty, Inspector and Security Hub CSPM to prioritise risk.
Is S3 data encrypted by default?
Yes. From 5 Jan 2023 AWS applies server-side encryption with Amazon S3 managed keys (SSE-S3, AES-256) to all new object uploads. Choose AWS KMS keys when you need control over key policies and key usage.
Does AWS compliance make my workload compliant?
No. AWS attestations such as SOC, PCI DSS, FedRAMP and ISO 27001 cover the AWS infrastructure. Your own configuration, access control and data handling must also meet the standard, and AWS Config and Security Hub CSPM can automate the checks.
What should we enable first in a new AWS account?
Secure the root user with MFA and no access keys, set up federated access with temporary credentials, create a multi-Region trail in CloudTrail, then enable AWS Config, GuardDuty and Inspector.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE