Key takeaway
- Multi-cloud security for CISOs and architects: shared responsibility on AWS, Azure and Google Cloud, zero trust, CSA CCM and what to fix first.
Multi-cloud security is the practice of applying one set of identity, data, configuration and monitoring controls across workloads that run on more than one cloud provider. The hard part is not any single cloud. Each provider's controls are sound on their own terms, but each uses different names, defaults and consoles, so gaps appear in the spaces between them.
This guide is for CISOs, cloud architects and platform leads. It sets out who is responsible for what on AWS, Azure and Google Cloud, how zero trust applies across clouds, which risks to rank first, and an order of adoption. It builds on our multi-cloud strategy guide and our overview of cloud security.
What is multi-cloud security and why is it harder than single-cloud security?
A multi-cloud estate runs workloads on two or more public clouds, sometimes alongside private or hybrid environments. Teams choose this for resilience, regional data rules or the best service for a job. Security then has to cover every provider at once, with the same intent, even though each provider exposes it differently.
Three things make it harder. Identity models differ between providers. Policy has to be written several times, so drift is likely. Logs arrive in different formats, so a single view of an incident takes extra work. The controls below are aimed at those three problems.
Who is responsible for what in each cloud?
All three major providers use a shared responsibility model: the provider secures the underlying platform, and the customer secures what it puts on it. The exact line moves with the service type, so a single internal policy has to be mapped to each provider's wording. The table summarises what each provider says on its own pages.
| Provider | What the provider says it secures | What stays with the customer |
|---|---|---|
| AWS | The infrastructure that runs its services: hardware, software, networking and facilities ("security of the cloud"). | Set by the services you choose ("security in the cloud"). AWS describes inherited, shared and customer-specific controls. |
| Microsoft Azure | More of the stack as you move from IaaS to PaaS to SaaS. Physical hosts and datacentres are Microsoft's in all cloud models. | Always data, endpoints, accounts and access management, in every deployment type. |
| Google Cloud | The underlying network and infrastructure, always. More controls shift to Google from IaaS to PaaS to SaaS. | Always access policies and your data. Regulation and data location rules also affect who handles which control. |
Sources: AWS shared responsibility model, Microsoft Learn, shared responsibility in the cloud and Google Cloud, shared responsibility and shared fate. Google describes shared fate as an ongoing partnership that builds on shared responsibility, with secure blueprints and guidance. Microsoft notes that its matrix is illustrative and does not change any agreement, so confirm the exact terms in your contracts.
How does zero trust apply across clouds?
Zero trust removes implicit trust based on network location or ownership. According to NIST SP 800-207 (August 2020), authentication and authorisation of users and devices happen before a session with a resource starts. For workloads, NIST SP 800-207A (September 2023) covers access control for cloud-native applications in multi-cloud environments. It moves enforcement from IP addresses and subnets to application and service identities, using API gateways, sidecar proxies and identity infrastructure such as SPIFFE.
In practice this means one identity source, short-lived credentials, least-privilege roles per cloud, and policy decisions that do not depend on which provider hosts the workload. Our zero trust architecture guide covers the NIST model in more depth, and our identity and access management primer covers the building blocks.
What are the main multi-cloud security risks?
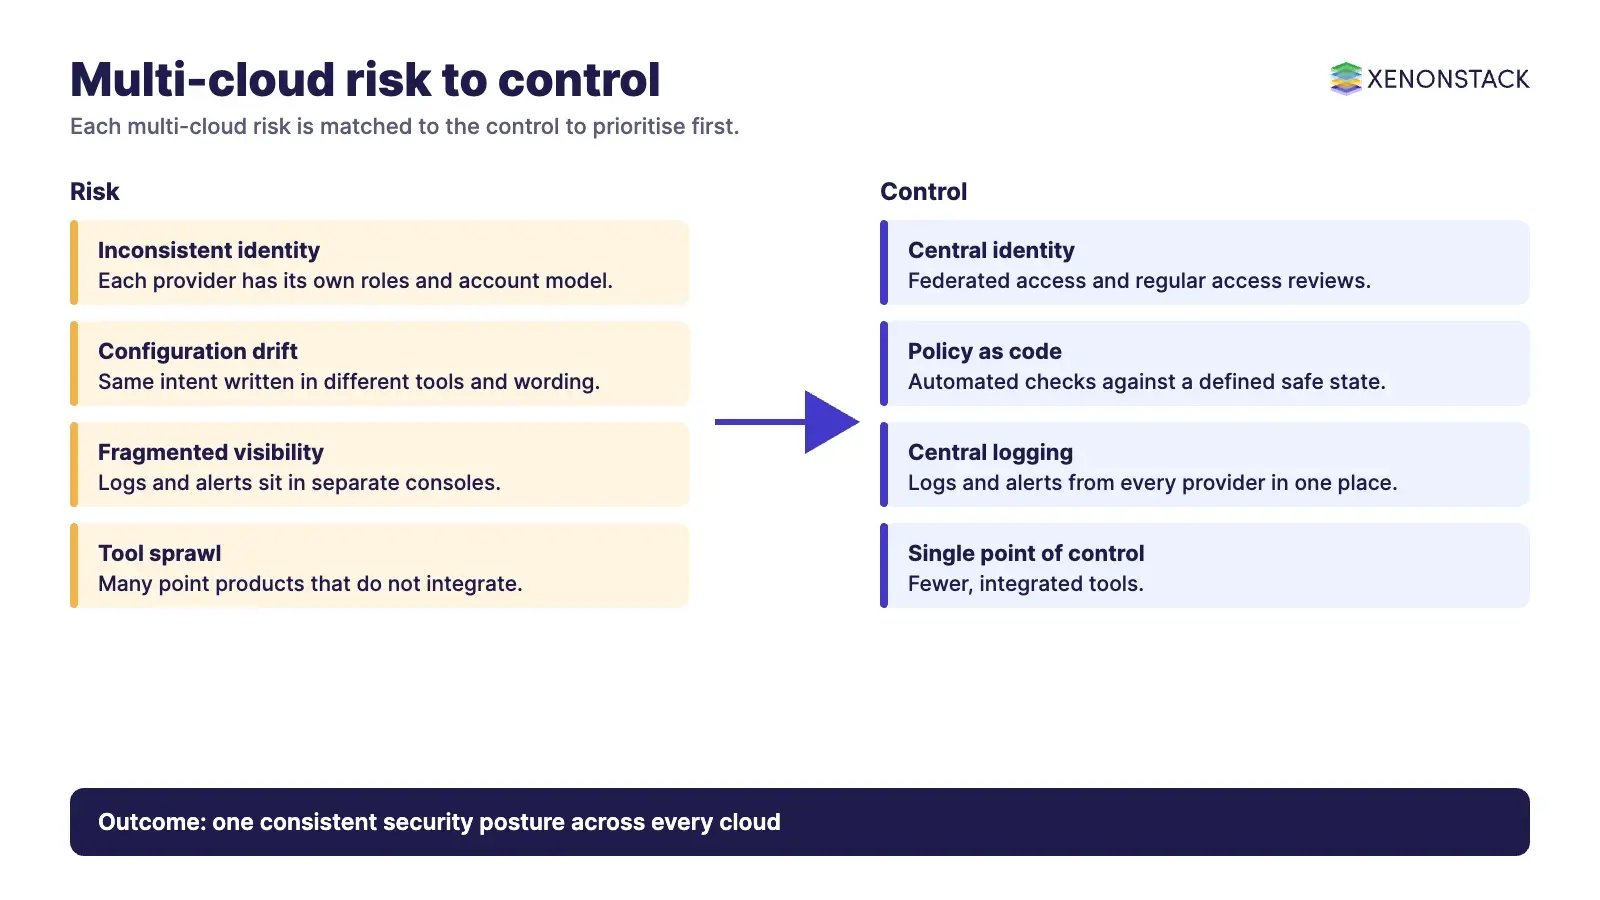
| Risk | Why it appears in multi-cloud | Control to prioritise |
|---|---|---|
| Inconsistent identity and permissions | Each provider has its own roles, policies and account model. | Central identity provider, federated access, regular access reviews. |
| Configuration drift | The same intent is written in different tools and wording. | Policy as code and automated checks against a defined safe state. |
| Fragmented visibility | Logs and alerts sit in separate consoles and formats. | Collect logs and alerts from every provider into one place. |
| Data governance gaps | Data residency and compliance duties differ by region and workload. | Classify data, choose where each class lives, manage encryption keys deliberately. |
| Tool sprawl | Many point products that do not integrate. | Fewer, integrated tools with a single point of control. |
| Skills gaps | Staff need depth in each provider's security model. | Role-based training and shared runbooks. |
Which controls should a multi-cloud security programme start with?
Identity and access
Use a framework that works with each provider's authentication model, so roles, policies and accounts are managed centrally. Grant only the privileges a person or service needs, and review them on a schedule. Strong API authentication matters for service-to-service calls.
Configuration and automation
Manual configuration is a common source of errors during deployments and updates. Define the desired safe state, check the environment against it continuously, and correct deviations automatically where the risk allows. The goal is fewer human mistakes, not only saved time.
Patching and hardening
Vulnerability handling differs between providers, so automate patching but test against the workload and its dependencies. Close unused ports, remove unneeded software and secure APIs and web interfaces.
Monitoring and threat detection
Consolidate logs, alerts and events from every provider so analysts see one timeline. Our guide to threat intelligence for security monitoring and incident response covers the detection side.
Data protection and backups
Classify data and keep sensitive data in the most protected location. Use encryption with clear key ownership and data loss prevention (DLP) where it fits. Keep backups in an immutable form so an attacker who reaches the cloud cannot encrypt or delete them, and scan them regularly.
Which frameworks help you govern multi-cloud security?
The Cloud Security Alliance Cloud Controls Matrix (CCM) is a cybersecurity control framework for cloud computing. According to the CSA, version 4.1 has 197 control objectives in 17 domains, and it shows which party in the cloud supply chain should implement which controls. The CSA also states that it helps align with standards including ISO, NIST and PCI. Because it is provider-neutral, it works as a common checklist across clouds.
| Source | Use it for |
|---|---|
| CSA Cloud Controls Matrix | A provider-neutral control list and responsibility mapping. |
| NIST SP 800-207 and 800-207A | Zero trust principles and multi-cloud, application-level access control. |
| AWS, Azure and Google Cloud shared responsibility pages | Mapping your policy to each provider's wording. |
In what order should you adopt multi-cloud security controls?
- Inventory: list every account, subscription and project, and who owns each.
- Identity: one identity source, federated sign-in, multi-factor authentication and least privilege.
- Baseline: a written safe configuration for each provider, mapped to the CCM.
- Visibility: centralised logs and alerts, with agreed response owners.
- Automation: policy as code, automated drift correction and patching.
- Resilience: immutable backups and a tested recovery plan.
- Review: regular internal and external vulnerability assessments, and updates to third-party tools.
When is multi-cloud security not worth the extra effort?
Every added provider adds identity models, policies and logs to secure. If a second cloud is there only because of history or a single small workload, the added risk can outweigh the benefit. Compare the reason for each cloud with the cost of securing it, and retire platforms that do not earn their place. Cost visibility belongs in the same review, and our multi-cloud FinOps guide covers it. AI agents that act across clouds add a further surface, covered in agentic AI cybersecurity.
Where does multi-cloud security pay off?
| Scenario | Security reason |
|---|---|
| Disaster recovery | Critical data is backed up across providers to limit downtime in an outage. |
| Data segmentation | Sensitive data sits where controls are strongest; other workloads run elsewhere. |
| Data residency | Data is stored in specific regions to meet regulatory duties. Confirm each rule on the official page. |
| Development and testing | Teams test on different services without affecting production security. |
| Threat detection | Security tools from several providers can be combined for wider coverage. |
Agents that act across clouds need governed context and an audit trail. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. To map one multi-cloud security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Multi-cloud security FAQ
What is multi-cloud security?
It is one set of identity, data, configuration and monitoring controls applied across workloads on more than one cloud provider.
Who is responsible for security in a multi-cloud setup?
Each provider secures its underlying platform, and the customer secures its data and access. According to the provider pages, data and access always stay with the customer, and the exact line moves with the service type.
Does zero trust work across clouds?
Yes. NIST SP 800-207A describes access control for cloud-native applications in multi-cloud environments, based on application and service identities rather than network location.
What is the Cloud Controls Matrix?
It is the Cloud Security Alliance's cybersecurity control framework for cloud computing. According to the CSA, version 4.1 has 197 control objectives in 17 domains.
What should we fix first?
Start with identity and visibility: one identity source with least privilege, and centralised logs from every provider. Then add configuration baselines and automation.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE