Key takeaway
- Multi-cloud strategy for 2027: how it differs from hybrid cloud, placement rules, current tools, security and FinOps governance, and an adoption plan.
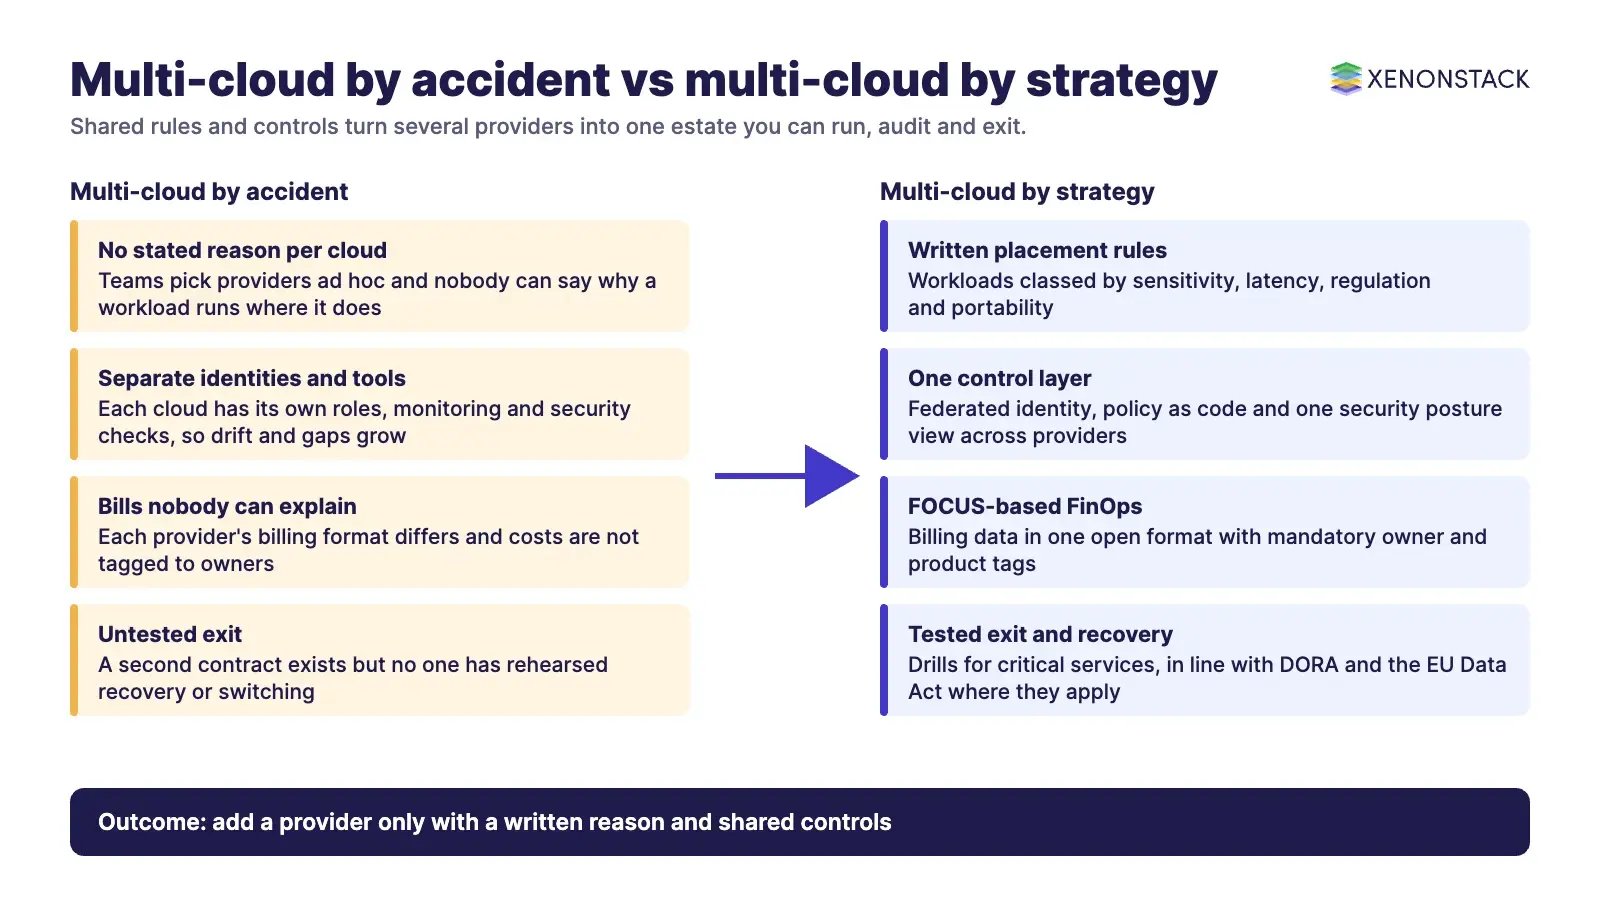
A multi-cloud strategy is a deliberate plan for running workloads on more than one public cloud provider, with clear rules for which workload goes where, how identity, security and cost are controlled across providers, and how you can move or exit if you need to. It is different from multi-cloud by accident, where teams adopt different providers without a shared model and end up with duplicated tools, gaps in security and bills nobody can explain.
In 2026 the case for a plan is stronger. Providers now offer managed private links between their clouds, EU rules on cloud switching and operational resilience are in force, billing data can be normalised with an open specification, and several well-known tools have been renamed, acquired or retired. This guide explains the models, the decisions, the current tools and an adoption sequence for enterprise leaders and architects.
What is a multi-cloud strategy?
Multi-cloud means using cloud services from two or more providers, such as AWS, Microsoft Azure, Google Cloud, Oracle Cloud Infrastructure or IBM Cloud, for different parts of your estate. A strategy turns that into policy: it names the reasons for using each provider, sets placement rules for workloads and data, and defines the shared controls that apply everywhere. Without those rules, multi-cloud raises cost and risk instead of reducing them.
Most enterprises also run private infrastructure, so the real decision is usually between the models below. NIST's definition of cloud computing, SP 800-145, still frames cloud as five essential characteristics, three service models and four deployment models, and remains a useful common vocabulary.
| Model | What it is | When it fits | Main watch-out |
| Single cloud | One public cloud provider for most workloads | Small or fast-moving teams that value depth of one platform over choice | Concentration on one provider's pricing, roadmap and outages |
| Multi-cloud | Two or more public cloud providers | Specific services, regions or commercial terms differ by provider, or regulators expect exit options | Duplicated skills and tooling; data transfer cost between clouds |
| Hybrid cloud | Private or on-premises infrastructure connected to one public cloud | Data that must stay on site, latency-sensitive plants or branches, or heavy legacy estates | Two operating models unless management is unified |
| Hybrid multi-cloud | Private infrastructure plus two or more public clouds | Large enterprises with regulated data, legacy systems and best-fit cloud services | Highest operational complexity; needs a strong platform team |
| Private cloud | Cloud infrastructure dedicated to one organisation, on premises or hosted | Strict control or sovereignty needs and steady, predictable demand | Capacity is finite and upgrades are your responsibility |
Why do enterprises adopt multi-cloud?
Good reasons are specific and can be written down. Weak reasons, such as "avoiding lock-in" with no plan to move, tend to add cost without adding options. The table shows the common drivers and when each one justifies the extra complexity.
| Driver | What it means in practice | When it justifies multi-cloud |
| Best-fit services | Use a provider's data, AI or industry service where it is clearly stronger for the workload | The service gives a measurable gain and the workload can live with that provider's tooling |
| Resilience and exit options | Reduce dependence on a single provider for critical services | Regulators or the board expect a tested exit or recovery plan, not just a second contract |
| Regulation and data location | Place data in regions or sovereign offerings that meet local rules | One provider cannot meet a data-location or sector requirement in every market you serve |
| Commercial leverage | Negotiate committed spend and pricing across providers | Spend is large enough that competition changes the terms |
| Mergers and acquisitions | Acquired businesses arrive on a different cloud | Migration cost or risk outweighs the cost of running two clouds well |
What has changed in multi-cloud since 2025?
Several changes affect architecture, compliance and tool choices. Each item below was checked against the provider's or regulator's own page on 11 November 2026.
| Change | What happened | What it means for your strategy |
| Managed links between clouds | AWS Interconnect - multicloud became generally available on 14 April 2026 with Google Cloud as the first partner, providing private, high-speed connections between AWS VPCs and other clouds. Oracle Cloud Infrastructure support reached general availability on 29 July 2026, and AWS says Microsoft Azure will follow later in 2026 | Cross-cloud networking no longer always needs VPNs or colocation; review designs that relied on them |
| EU Data Act | The Data Act has applied since 12 September 2025 and sets a framework for customers to switch between data processing service providers | Switching and portability become contractual and technical requirements, not just goals |
| DORA for financial entities | DORA has applied since 17 January 2025, covering ICT third-party risk management and an EU-wide oversight framework for critical ICT third-party providers to address concentration risk | Banks and insurers need documented third-party risk controls and exit strategies for critical providers |
| Common billing format | The FinOps Open Cost and Usage Specification (FOCUS) is at version 1.4, and AWS, Google Cloud, Microsoft Azure, Oracle Cloud and IBM Cloud are listed as producing FOCUS data | Cross-cloud cost reporting can start from one schema instead of custom mappings per provider |
| Google Cloud Deployment Manager | Google states that Deployment Manager reached end of support on 31 March 2026 and recommends Infrastructure Manager, which uses Terraform | Move remaining Deployment Manager templates to Terraform-based tooling |
| Security tool names | Azure Security Center and Azure Defender are now Microsoft Defender for Cloud; Palo Alto Networks announced that Prisma Cloud customers move to Cortex Cloud | Update architecture documents, runbooks and procurement records to current product names |
| FinOps tool ownership | Flexera completed its acquisition of Spot from NetApp on 3 March 2025; Cloudability is now sold as IBM Cloudability by Apptio, an IBM company; CloudHealth is now CloudHealth by Broadcom | Check contracts, roadmaps and support terms after ownership changes |
How should you design and deploy across multiple clouds?
Design starts with placement rules, not tools. Decide which workloads are portable, which are allowed to use provider-specific services, and which data must stay in which region. Then standardise the layers that should be the same everywhere.
Workload placement
Classify workloads by data sensitivity, latency, regulatory scope and how much they depend on provider-specific services. Keep systems of record and their data close together, because moving data between clouds adds latency and transfer cost. Allow provider-specific managed services where the gain is clear, and record that choice so exit plans reflect it.
Identity and access
Use one corporate identity provider with federation into each cloud, short-lived credentials for workloads, and role definitions that map the same job to the same permissions in every provider. Identity drift between clouds is one of the most common causes of security findings.
Networking
Plan IP address ranges, DNS and egress once for all clouds. Use private connectivity for sustained cross-cloud traffic, such as the managed interconnects now offered between some providers, and keep the number of cross-cloud data paths small and documented.
Portability with Kubernetes and infrastructure as code
Kubernetes gives a common application runtime across providers, and control planes such as Azure Arc can attach Kubernetes clusters, servers and databases running outside Azure to one management and governance layer. For infrastructure, Terraform and its Linux Foundation fork OpenTofu describe resources across providers in one language. Choosing between containers and managed platforms is covered in our guide to CaaS vs PaaS, and an internal developer platform on hybrid and multi-cloud gives developers one self-service path to every environment. Where workloads, including AI agents, must run across on-premises, cloud and hybrid sites, NexaStack is an agentic operating platform for physical AI that runs across on-premises, cloud and hybrid environments.
Which tools manage a multi-cloud estate going into 2027?
No single product covers every layer. Most enterprises combine one tool per category and connect them through shared tagging, identity and reporting standards.
| Category | Examples | When you need it |
| Hybrid and multi-cloud management | Azure Arc; Flexera Snow Commander for self-service provisioning across AWS, Azure, GCP, Kubernetes and VMware | You need one inventory, policy and provisioning path across providers and on premises |
| Container platforms | Kubernetes, Red Hat OpenShift, Rancher | Applications must run the same way on more than one cloud |
| Infrastructure as code | Terraform, OpenTofu, Ansible; provider-native AWS CloudFormation and Azure Resource Manager | Always; use a cross-provider tool for shared patterns and native tools only where you accept the tie |
| Observability | Datadog, Dynatrace, New Relic, Splunk, Prometheus with Grafana | You need one view of health and incidents across clouds |
| Cost management (FinOps) | IBM Cloudability, CloudHealth by Broadcom, Flexera with Spot; provider tools such as AWS Cost Explorer; FOCUS as the shared data format | Spend crosses providers and finance needs one allocation model |
| Security posture and protection | Microsoft Defender for Cloud, which connects to AWS and GCP as well as Azure; Palo Alto Networks Cortex Cloud; AWS Security Hub for AWS findings | You need consistent posture checks and threat detection across providers |
For monitoring options and how they compare with full observability, see our guide to monitoring as a service in the cloud. Operations teams that want agents to take on routine incident work can look at AgentSRE, which uses a fleet of AI agents to automate detection, root cause analysis and remediation.
How do you govern security, compliance and cost across clouds?
Governance is where multi-cloud strategies succeed or fail. The aim is one set of rules, applied automatically in every provider, with evidence you can show to auditors and the board.
- Policy as code: express guardrails for regions, encryption, network exposure and tagging as code, and apply them at provisioning time in every cloud.
- One security posture view: use a posture management tool that covers all providers, so findings are ranked and owned in one place.
- Cost allocation: enforce mandatory tags for owner, product and environment, load billing data into a common format such as FOCUS, and review unit costs with product owners each month.
- Data location and switching: record where regulated data lives, and keep contracts and runbooks that support switching in line with the EU Data Act where it applies.
- Exit and recovery plans: for critical services, document and test how you would recover or move away from a provider, which DORA makes an explicit expectation for financial entities.
- Agent guardrails: when AI agents provision resources, change configurations or approve spend across clouds, record which context and policy each action used. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
How do you adopt a multi-cloud strategy step by step?
- Write down the reasons. For each provider, state the business reason, the workloads it hosts and the owner.
- Assess the current estate. Inventory applications, data, dependencies, contracts and current spend across all environments.
- Set placement rules. Classify workloads by sensitivity, latency, regulation and portability, and decide where each class may run.
- Build the shared foundation. Identity federation, network design, policy as code, tagging, logging and a FOCUS-based cost pipeline, before moving workloads.
- Standardise delivery. One infrastructure-as-code approach, one CI/CD pattern and a common container platform where portability matters.
- Move or build one workload at a time. Start with a workload whose reason for its cloud is clear, and measure cost, performance and incidents.
- Test exit and recovery. Run failover and restore drills for critical services and update the exit plan after each one.
- Run it as a product. A platform team owns the shared layers, and our cloud managed services can support operations across hybrid and multi-cloud environments.
What are the trade-offs, and when is multi-cloud the wrong choice?
| Choice | Benefit | Trade-off |
| Portable, lowest-common-denominator design | Easier to move workloads between providers | Gives up managed services that could save engineering time |
| Provider-native services per workload | Faster delivery and less to operate | Exit becomes a rebuild for those workloads; record it in the exit plan |
| Active-active across two clouds | Highest resilience to a provider outage | Double the run cost, complex data consistency and more testing |
| Primary cloud with a tested recovery target | Most of the resilience benefit at lower cost | Recovery takes longer and depends on regular drills |
Multi-cloud is the wrong choice when the team lacks the skills to run even one cloud well, when the only reason is a vague fear of lock-in, or when the workloads exchange large volumes of data that would cross provider boundaries. In those cases, go deep on one provider, keep infrastructure as code and data exports portable, and revisit the decision when a concrete driver appears.
To map one cross-cloud decision your agents should make, such as where a workload runs or which spend to approve, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Related on XenonStack
- CloudOps AI agents: cloud operations run by governed agents.
- NexaStack: agent runtime and inference for private cloud, on-prem and edge.
- ElixirClaw: run governed AI agents with decision boundaries and human approvals.
What should you plan for in 2027?
One dated change affects cross-cloud contracts and exit plans, and the rest of your 2027 plan should build on the controls described above.
- 12 January 2027: under Article 29(1) of the EU Data Act, providers may no longer charge fees for customers switching data processing services, after a period in which only costs directly linked to switching could be charged, according to Germany's Bundesnetzagentur. Review exit and portability clauses in your cloud contracts before that date.
- Exit and recovery: schedule a test of your exit plan for each critical service during the year.
- Shared foundation: keep identity, tagging and the common billing format in place before adding workloads to another provider.
Frequently asked questions
What is the difference between multi-cloud and hybrid cloud?
Multi-cloud uses two or more public cloud providers. Hybrid cloud connects private or on-premises infrastructure with a public cloud. Hybrid multi-cloud combines both: private infrastructure plus two or more public clouds.
Can you connect AWS directly to other clouds?
Yes. AWS Interconnect - multicloud became generally available on 14 April 2026 with Google Cloud and added Oracle Cloud Infrastructure on 29 July 2026. AWS says Microsoft Azure support will follow later in 2026.
Which regulations affect a multi-cloud strategy in Europe?
The EU Data Act, applicable from 12 September 2025, sets a framework for switching between data processing service providers. For financial entities, DORA has applied since 17 January 2025 and covers ICT third-party risk and oversight of critical ICT third-party providers.
How do you compare cloud costs across providers?
Use the FinOps Open Cost and Usage Specification (FOCUS), now at version 1.4, which AWS, Google Cloud, Microsoft Azure, Oracle Cloud and IBM Cloud are listed as supporting, together with mandatory tagging and a FinOps tool that reports unit costs.
Is Azure Security Center still the right tool name?
No. Azure Security Center and Azure Defender are now Microsoft Defender for Cloud, which can also connect to AWS and Google Cloud environments.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE