Key takeaway
- Cloud governance framework for enterprise leaders: policies, controls, AWS, Azure and Google Cloud guardrails, FinOps, challenges and an adoption sequence.
What is cloud governance and why does it matter?
Cloud governance is how an organisation controls its use of cloud services through guardrails: policies, procedures and tools that define acceptable and unacceptable cloud activity. Microsoft's Cloud Adoption Framework describes it as aligning cloud use with business objectives, mitigating risk, ensuring regulatory compliance and preventing unmanaged or unauthorised cloud actions, and as a continuous process rather than a one-time project (Microsoft Learn).
For a CIO, CISO or platform lead the practical question is who may create what, where, at what cost and with which evidence. This guide answers that with a framework, a decision table for the three major clouds, the challenges that hold programmes back and an adoption sequence. For the security side, read our cloud security overview and the guide to securing cloud native applications.
What has changed in cloud governance?
| Area | Older approach | Current practice | Source |
|---|---|---|---|
| Account structure | Many workloads in one account or subscription | Separate accounts per workload or environment, each an isolation boundary for identity and access, with billing separation to map cost to projects | AWS whitepaper |
| Policy enforcement | Spreadsheets and manual reviews | Policy as code enforced by the platform, for example Azure Policy, AWS Control Tower controls and Google Cloud organisation policies | See the table below |
| Cost control | Monthly bill review by finance | FinOps: an operational framework and cultural practice that creates financial accountability between engineering, finance and business teams | FinOps Foundation |
| Control catalogue | Home-made checklists | A shared control framework such as the CSA Cloud Controls Matrix v4.1, with 197 control objectives in 17 domains | Cloud Security Alliance |
| Scope | Human users and servers | Also autonomous AI agents acting inside cloud accounts, which need policy limits and audit trails | Product note, see AgentGRC below |
What does a cloud governance framework contain?
A framework turns principles into owned controls. Microsoft's governance process has five steps: build a cloud governance team, assess cloud risks, document policies, enforce them and monitor compliance, with the last four repeated in a cycle. The table maps the components most enterprises need to an owner and the evidence an auditor will ask for.
| Component | What it sets | Typical owner | Evidence |
|---|---|---|---|
| Policy management | Rules for cloud usage aligned to business goals, reviewed by executives, managers and IT experts | CIO, CISO | Approved policy register with review dates |
| Service catalogue | The approved cloud services and their security measures | Platform lead | Catalogue and exception log |
| Access management | Role-based access control over who reaches which resources | Security architect | Access reviews, role mappings |
| Security protocols | Encryption in transit and at rest, authentication and permission checks | CISO | Configuration and key-management reports |
| Cost management | Budgets, tagging, cost trend and commitment-discount policies | FinOps lead, finance | Showback or chargeback reports |
| Compliance monitoring | Regular assessment against laws and industry standards | Risk and compliance | Control test results, audit trail |
| Performance metrics | Monitoring of resources against service-level agreements | Head of engineering | SLA dashboards |
The policy set should cover infrastructure design standards, monitoring, security policy, programming standards and backup and recovery. It should also state how workloads move between providers and who evaluates each deployment. Policies apply at four levels: the infrastructure or virtualisation platform, operating systems, the platform or application, and business activity on that platform. Where agents act in these environments, ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
Which governance principles should you apply first?
Six principles form a practical starting set. Adjust each to your own regulatory and budget position.
| Principle | What it covers | Start with |
|---|---|---|
| Financial management | Budget policies and cost trend policies, which depend on each other | Budgets per account or project, with alerts |
| Cost optimisation | Committed-use discounts and spotting where they go unused | A monthly commitment utilisation review |
| Operational governance | System testing, ending unused (zombie) assets, and stop and start schedules for non-production instances | Automatic shutdown of development and QA environments |
| Performance management | Right-sizing assets for their workloads and keeping stored data in the most cost-effective location | Quarterly right-sizing review |
| Asset and configuration management | Consistent tagging for cost allocation and finding non-conforming assets, such as those launched outside an approved region | Mandatory tags and an allowed-regions rule |
| Security and incident management | Encryption, access controls, security groups, audit trails and application access rules | Central audit logging and an incident runbook |
Operational governance depends on good testing discipline. See our guide to system testing, and the guide on integrating threat intelligence into security monitoring and incident response for the incident side.
How do AWS, Azure and Google Cloud enforce governance?
Each major cloud has a native way to express guardrails. The right choice follows where your workloads run, and multi-cloud estates need a common control catalogue above these native tools.
| Cloud | Native mechanism | What it does (vendor wording) | When it fits |
|---|---|---|---|
| AWS | AWS Control Tower | Sets up and governs a multi-account environment using prescriptive best practices. A control, also called a guardrail, is a high-level rule for ongoing governance, and can be preventive, detective or proactive. | Many AWS accounts needing a landing zone and consistent controls |
| Azure | Azure Policy | Enforces organisational standards and assesses compliance at scale, with a compliance dashboard, bulk and automatic remediation, and effects such as audit and deny. Microsoft suggests starting with audit effects before enforcement effects. | Azure subscriptions, with policy assigned by management group |
| Google Cloud | Organization Policy Service | Gives centralised, programmatic control over resources through constraints applied to an organisation, folder or project and inherited below it. A policy can run in dry-run mode. | Google Cloud estates organised by folders and projects |
Sources: AWS Control Tower documentation, Azure Policy overview and Google Cloud Organization Policy overview. All three support the same pattern: start in audit or dry-run mode, learn what would break, then enforce.
Why separate accounts help
AWS advises isolating workloads in separate accounts. An account acts as an isolation boundary for identity and access management, access between accounts is denied by default, and billing separation maps cost to projects. That limits the security and financial blast radius of any one issue. AWS also notes that charges follow resource usage, not the number of accounts, and that a single account is fine while you are only experimenting.
How governance limits shadow IT
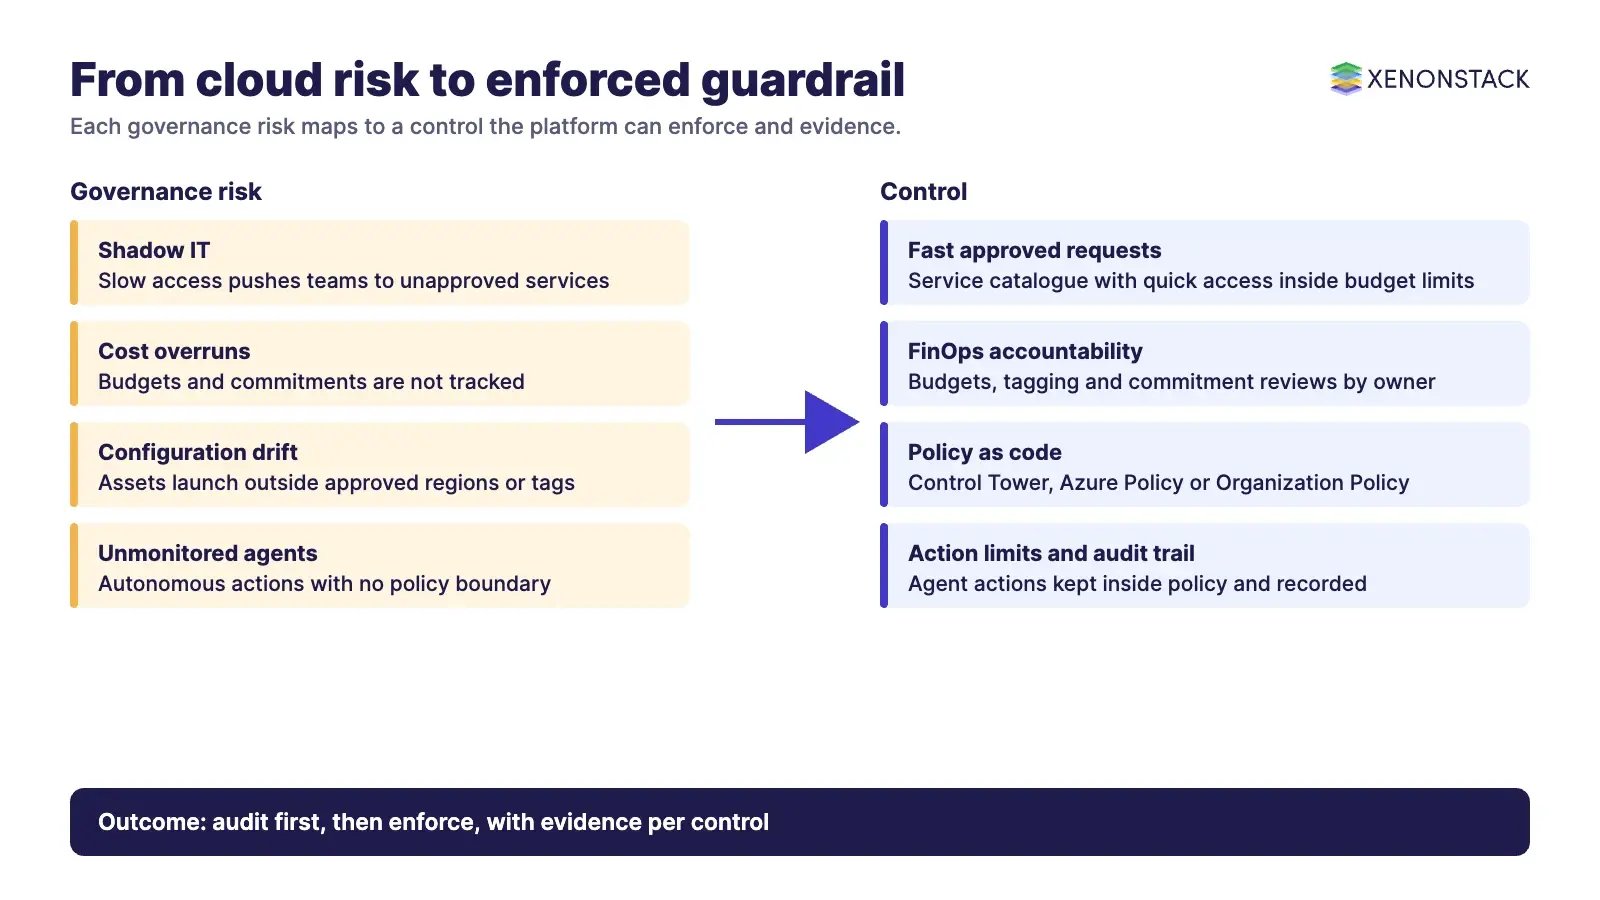
Shadow IT grows when approved access is slow. A governance model that lets teams request and receive allowed resources quickly, within compliance and budget limits, removes the reason to go around it. Guardrails set at the right point in the organisational hierarchy also replace manual tracking of accounts, cost and compliance, and enforcement actions remove repeated follow-up after an alert.
What are the main challenges in cloud governance?
| Challenge | What it looks like | Control that helps |
|---|---|---|
| Multi-cloud inconsistency | Different rules and tooling per provider | One control catalogue mapped to each cloud's native policy engine |
| Skills shortage | Few people who understand both cloud and governance | Platform team owning policy as code, with training for engineers |
| Fast-changing technology | Policies that lag new services | Scheduled policy review, audit-mode rollout for new rules |
| Data security risk | More data in the cloud means more exposure to breaches and unauthorised access | Encryption, least-privilege access, central logging |
| Integration gaps | Existing frameworks do not cover new cloud services | Service catalogue with an onboarding checklist for new services |
| Provider dependence | Provider outages lower your own performance | Documented exit and recovery plan, SLAs reviewed against policy |
| Autonomous agents | Agents act in cloud accounts without a clear policy boundary or audit trail | Action limits and decision records |
For that last row, AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
Which tools support cloud governance?
Choose by job rather than by brand. The older list in this guide (SpectralOps, Cisco Cloudlock, Bitglass, Cato SASE, Fugue, Perimeter 81, Illumio Core) has been removed because we could not confirm current product status for each vendor from their own pages; check any vendor you shortlist before buying.
| Need | Tool category | Example | Current status |
|---|---|---|---|
| Guardrails and landing zones | Native policy engines | AWS Control Tower, Azure Policy, Google Cloud Organization Policy | Documented by each vendor, see the table above |
| Control catalogue and audit mapping | Control framework | CSA Cloud Controls Matrix v4.1 | 197 objectives, 17 domains |
| Cost accountability | FinOps practice and tooling | FinOps Foundation framework | Practice, not a product |
| SaaS and data access control | CASB or SASE | Evaluate vendors individually | Verify with the vendor |
| Agent actions and audit | Agent governance | AgentGRC, ElixirData Context OS | See product pages |
In what order should you adopt cloud governance?
- Name the governance team and its owners across IT, security, finance and the business.
- Assess risk: inventory accounts, data locations and shadow IT.
- Document policy for the six principles above, starting with security, tagging and budgets.
- Enforce in audit mode first, then switch to deny or remediate once the findings are understood.
- Monitor and report compliance, cost and incidents on a fixed cadence.
- Automate and review: move repeat checks to code and review policy on a schedule. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
When is heavy cloud governance not the right move?
- A single team experimenting in one account does not need a multi-account structure yet. AWS says to plan it when you approach your first production workloads.
- Enforcing deny rules before running them in audit mode can break working deployments.
- Governance that is slower than the business creates the shadow IT it was meant to stop. Keep request paths fast.
- A tool is not a framework. Buying a platform without owners, policy and review leaves the gaps in place.
NIST's SP 800-144 (December 2011) remains a useful reminder that outsourcing data, applications and infrastructure to a public cloud brings considerations the organisation must still manage itself.
To map one cloud governance decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is cloud governance?
Cloud governance is how an organisation controls its use of cloud services through guardrails: policies, procedures and tools that define acceptable and unacceptable cloud activity, aligned to business objectives, risk and regulatory compliance.
What does a cloud governance framework include?
It includes policy management, a service catalogue, access management, security protocols, cost management, compliance monitoring and performance metrics, each with an owner and evidence.
How do I start cloud governance?
Name a governance team, assess cloud risks, document policies, enforce them and monitor compliance. Run new rules in audit or dry-run mode before enforcing them.
Why use separate cloud accounts?
Separate accounts act as isolation boundaries for identity and access, deny cross-account access by default and separate billing so costs map to projects. This limits the blast radius of an issue.
How does governance relate to FinOps?
FinOps, defined by the FinOps Foundation as an operational framework and cultural practice, creates financial accountability between engineering, finance and business teams. It supplies the cost side of cloud governance.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE