Key takeaway
- Cloud native architecture patterns for architects: database per service, event streaming, sagas, CQRS and circuit breakers, and when to avoid each one.
Cloud native architecture patterns are proven ways to build loosely coupled services that stay secure, resilient, manageable and observable when they run on containers, Kubernetes and managed cloud services. The core set covers how components own data (database per service), how they talk (event streaming and a three-interface API), how they record and read state (event sourcing and CQRS), how they keep work consistent across services (sagas) and how they contain failure (circuit breakers and service meshes).
For enterprise leaders the question is not which pattern is fashionable but which one fits a given workload, what it costs to run and when to leave it out. This guide maps each pattern to the problem it solves, the conditions where it fits and the cases where it adds complexity without value. For the wider tool landscape, see our overview of cloud native tools and solutions, and for the contrast with older designs, cloud native vs traditional applications.
What is cloud native architecture, according to CNCF?
The Cloud Native Computing Foundation (CNCF) publishes the reference definition. Version 1.1, approved on 26 February 2024, says cloud native practices let organisations develop, build and deploy workloads in public, private and hybrid clouds "at scale in a programmatic and repeatable manner", and that cloud native is "characterized by loosely coupled systems that interoperate in a manner that is secure, resilient, manageable, sustainable, and observable" (CNCF Cloud Native Definition v1.1).
The same definition lists the building blocks: "containers, service meshes, multi-tenancy, microservices, immutable infrastructure, serverless, and declarative APIs", and notes the list is not exhaustive. Combined with automation, these practices let teams "make high-impact changes frequently, predictably, with minimal toil". Patterns are how architects turn those building blocks into a working system.
CNCF's glossary describes a microservices architecture as one that "breaks applications into individual independent (micro)services", each focused on a specific function, so services can be deployed, updated and scaled separately. The glossary is also clear about the cost: it "creates operational overhead". Every pattern below is a way to get the benefit of independence while keeping that overhead under control.
Which cloud native architecture patterns should enterprises know?
The table summarises the patterns covered in this guide, what each one does, where it fits and where it does not.
| Pattern | What it does | When it fits | When to avoid |
| Database per service | Each service keeps its data private and reachable only through its API | Independent teams, different data shapes, need for a bulkhead between services | Workloads that need frequent cross-service joins or tightly coupled transactions |
| Event streaming (event-driven architecture) | Producers publish state changes as events; consumers react asynchronously | Many downstream consumers, uneven load, real-time data flows | Simple request and response flows with one caller and one callee |
| Event sourcing | Stores every change as an event in an append-only store and rebuilds state from it | Ledgers, audit-heavy domains, need to replay or reconstruct past states | Plain CRUD, short-lived systems, views that must be consistent in real time |
| CQRS | Separates commands (writes) from queries (reads) into different models | Read and write loads differ sharply, or reads need their own optimised views | Simple domains where a CRUD model is enough |
| Saga | Coordinates a sequence of local transactions with compensating steps on failure | Business processes that span several services, each with its own database | Work that fits inside one service and one database |
| Circuit breaker | Stops calls to a failing dependency and tests recovery before reopening | Synchronous remote calls that can hang or fail and cause cascading failures | Local in-memory calls, event-driven flows with dead letter queues, or where the platform already handles recovery |
| Three-interface (trilateral) API | Gives each component a synchronous command and query API, an outbound event API and an inbound event API | Event-first systems built from isolated, bounded components | Small systems with few integrations, where one synchronous API is enough |
| Service mesh | Manages traffic between services and adds reliability, observability and security uniformly | Large estates of services where per-service networking code is hard to keep consistent | A handful of services, where the mesh adds more operational load than it removes |
The "when to avoid" column draws on the published guidance for each pattern in the Microsoft Azure Architecture Center (event sourcing, CQRS, circuit breaker) and on microservices.io for database per service.
How do the patterns fit together in one architecture?
A useful way to read the patterns is in three groups. Foundation patterns create isolated, bounded components that do not call each other synchronously: database per service, event streaming and event sourcing. Boundary patterns govern where the system meets people and other systems: the three-interface API and CQRS read views. Control patterns govern how work flows between components and how failure is contained: sagas, circuit breakers and the service mesh.
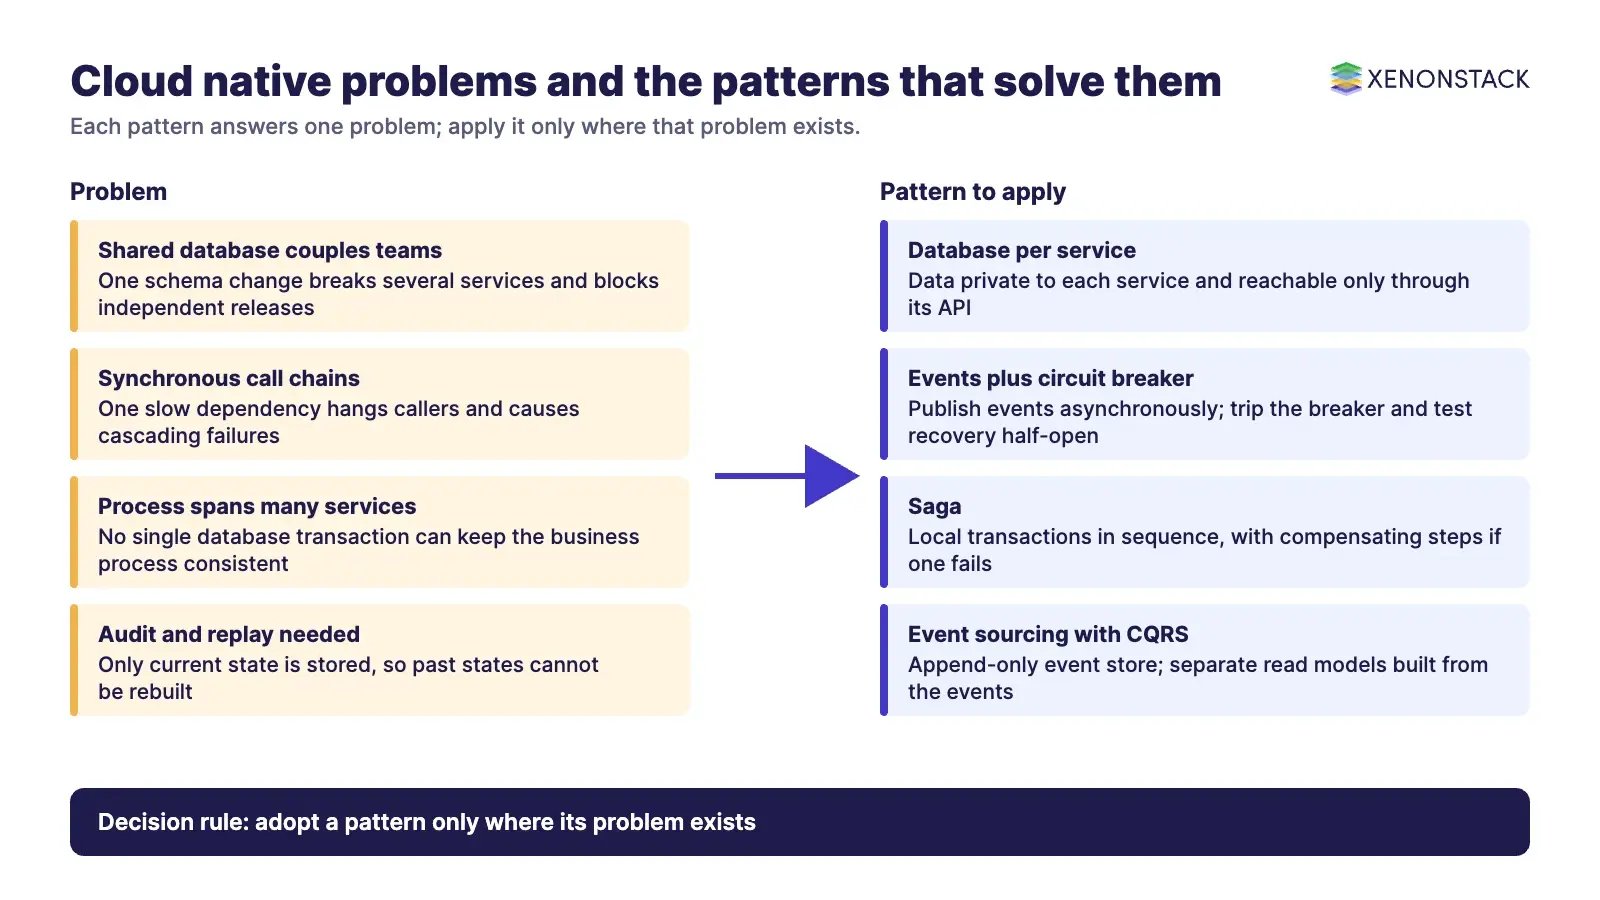
The reason for isolation is recovery. A cloud native system must recover quickly from human error made during development or deployment. When components are isolated, a fault in one does not stop the others, and the fix is limited to the component that failed. Asynchronous communication supports this: a calling service posts its request or event and carries on with other work, so the two services are decoupled in time as well as in code.
How does each cloud native pattern work?
Database per service
Each component gets its own data store, which acts as a bulkhead between services. In the words of microservices.io, the pattern keeps "each microservice's persistent data private to that service and accessible only via its API". The benefits are loose coupling and the freedom for each service to use the database type that suits it, for example a search engine for text search. The drawbacks are real: transactions that span services are not straightforward, queries that join data across databases are hard, and the team must run several SQL and NoSQL systems. Our guide to database types covers how to choose a store per workload.
Event streaming
CNCF defines event-driven architecture as "a software architecture that promotes the creation, processing, and consumption of events", where "an event is any change to an application's state". Upstream components hand work to downstream components by publishing domain events, and producers and consumers stay decoupled. A central event hub carries the events; CNCF names Apache Kafka, which describes itself as "an open-source distributed event streaming platform", as an example. See our deeper guide to event-driven architecture patterns, brokers and trade-offs.
Event sourcing
Event sourcing stores the full series of actions taken on an object in an append-only store, rather than only the current state. Microsoft describes the store as "the system of record that you can use to materialize the domain objects", which can improve auditability and write performance. Teams usually choose one of two variants:
- Event-first: the command writes nothing to a database; it wraps the data in a domain event and publishes it to one stream, and consumers build their own views.
- Database-first: the command writes to one service database, and a change stream from that database publishes the matching event.
Either way, the system is eventually consistent. Microsoft lists the costs plainly: events must be versioned and never updated, consumers must be idempotent because delivery is typically at least once, long streams need snapshots, and immutability conflicts with regulations that require deletion of personal data, which teams handle by keeping personal data outside the event store or by crypto-shredding. Event sourcing "doesn't have to be an all-or-nothing decision"; apply it to a ledger or audit-critical domain and use CRUD elsewhere.
CQRS
Command Query Responsibility Segregation separates writes (commands) from reads (queries) into different models so each can be optimised on its own. It pairs naturally with event sourcing, where read views are projections built from the event stream. Microsoft warns that CQRS "can introduce significant complexity", especially with event sourcing, and is not suitable when the domain is simple or a CRUD interface is sufficient.
Saga
Once every service owns its data, a business process that spans services cannot rely on one database transaction. The saga pattern coordinates "a sequence of local transactions across multiple services", and if a step fails, "a series of compensating transactions undoes the changes that the completed steps made". In choreography, services exchange events with no central controller, which suits short flows. In orchestration, a central orchestrator tells each participant what to do, which suits complex flows but becomes a point of failure that must itself be resilient.
Circuit breaker
Remote calls can fail or hang, and one slow dependency can trigger cascading failures across many services. A circuit breaker wraps the call in a proxy with three states, as described by Microsoft:
- Closed: calls pass through and the breaker counts recent failures. When failures pass a threshold within a set period, it opens.
- Open: calls fail immediately and an exception is returned, giving the dependency time to recover.
- Half-open: after a time-out, a limited number of calls are let through. If they succeed, the breaker closes and the failure counter resets; if any fails, it opens again.
The pattern is not universal. Microsoft notes it may not suit message-driven or event-driven flows, which route failed messages to a dead letter queue, or cases where failure recovery is already handled "at the infrastructure or platform level, such as with health checks in global load balancers or service meshes".
Three-interface (trilateral) API
A component in an event-first system needs more than one interface. The trilateral API pattern publishes three: an asynchronous API that emits events when the component's state changes, a synchronous API for commands and queries, and an asynchronous API that consumes events emitted by other components. Documenting all three makes the component's real contract visible to the teams that depend on it.
Service mesh
CNCF's glossary explains that a service mesh manages traffic between services and adds "reliability, observability, and security features uniformly across all services". The glossary notes this happens without code changes to each application, so some resilience patterns are now applied by the platform rather than written into each service.
Building Scalable Cloud Native Applications
Most cloud native applications are deployed on Kubernetes, which the project describes as "a portable, extensible, open source platform for managing containerized workloads and services" that facilitates "both declarative configuration and automation" (Kubernetes overview). The video walks through how these patterns come together when building scalable cloud native applications.
What has changed in cloud native architecture since these patterns were first described?
| Change | What it means for architects | Source |
| CNCF definition updated to version 1.1 (approved 26 February 2024) | The definition names five qualities: secure, resilient, manageable, sustainable and observable. Treat each as a design input, not an add-on | CNCF TOC |
| Kubernetes is the default runtime | CNCF's annual survey, published 20 January 2026, reports 82% of container users running Kubernetes in production | CNCF Annual Cloud Native Survey |
| Platforms as a product | CNCF defines a platform as "an integrated collection of capabilities defined and presented according to the needs of the platform's users", so patterns are increasingly offered as shared platform capabilities | CNCF Platforms White Paper |
| Resilience moves to the platform | Service meshes and load balancer health checks now handle some recovery that circuit breakers in code used to handle | Microsoft Learn |
| Event sourcing meets data protection law | Immutable event stores need a plan for deleting personal data, such as storing it outside the store or crypto-shredding | Microsoft Learn |
How should leaders govern security, reliability and cost in a cloud native architecture?
Patterns multiply moving parts, so governance has to be designed in. Four controls matter most:
- Security: treat service-to-service traffic as untrusted, use a mesh or equivalent for uniform encryption and identity, and keep each service's data private behind its API. Our guide to cloud native security tools and architecture goes deeper.
- Reliability: decide per dependency whether failure is handled in code (circuit breaker, retry) or by the platform (mesh, load balancer), and make every event consumer idempotent.
- Data governance: version event schemas, never edit stored events, and plan personal-data deletion before the first event is written.
- Cost: every database per service, stream and projection has a running cost. Track cost per service and retire projections nobody reads.
The same discipline applies as AI agents start acting on these systems, for example opening incidents or rolling back a deployment. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
In what order should an enterprise adopt cloud native patterns?
- Draw service boundaries first. Split by business capability and give each service its own data store before adding anything else.
- Put the runtime and delivery pipeline in place. Containers, Kubernetes, declarative configuration and continuous deployment for cloud native applications.
- Introduce event streaming where several consumers need the same change, and replace synchronous chains between services.
- Add sagas for the business processes that cross service boundaries, with compensating steps written and tested.
- Contain failure. Add circuit breakers on synchronous remote calls, or adopt a service mesh once the number of services makes per-service code inconsistent.
- Apply event sourcing and CQRS selectively, only in domains that need audit, replay or separate read models.
- Make it observable and operable. Trace requests and events end to end and give on-call teams clear runbooks. AgentSRE applies agentic AI to incident management and observability for teams that cannot afford downtime.
What are the trade-offs, and when should you not use these patterns?
Cloud native patterns are a response to scale and change. If a system is small, stable and owned by one team, a well-structured modular application on managed services may be cheaper and easier to run. The common traps are:
- Distributed monolith: services that share a database or call each other synchronously in long chains get the cost of microservices without the independence.
- Event sourcing everywhere: Microsoft advises against it for plain CRUD, prototypes, short-lived systems and teams without event-driven experience.
- Eventual consistency surprises: users and downstream systems must be designed to tolerate views that lag behind writes.
- Operational load: each extra database, stream and mesh component needs patching, monitoring and skills. CNCF's own glossary names this operational overhead as the trade-off of microservices.
If you need help choosing patterns for a specific estate, talk to a cloud native applications specialist. Teams running network workloads should also read our guide to cloud native network functions.
To map one operational decision your agents should make across a cloud native estate, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about cloud native architecture patterns
What is cloud native architecture?
CNCF defines cloud native as practices for building and deploying workloads in public, private and hybrid clouds at scale in a programmatic and repeatable manner, characterised by loosely coupled systems that are secure, resilient, manageable, sustainable and observable. Typical building blocks are containers, service meshes, microservices, immutable infrastructure, serverless and declarative APIs.
Which cloud native pattern should we adopt first?
Start with clear service boundaries and a database per service, because every other pattern assumes isolated components. Add event streaming next, then sagas for cross-service processes and circuit breakers or a service mesh to contain failure.
Do we need event sourcing for every service?
No. Microsoft's guidance says event sourcing does not have to be all or nothing and is a poor fit for plain CRUD, prototypes, short-lived systems and views that must be consistent in real time. Use it where audit, replay or reconstruction of past state matters.
Is a circuit breaker still needed if we run a service mesh?
Sometimes not. Microsoft notes a circuit breaker may not be suitable when failure recovery is already managed at the platform level, such as by service meshes or load balancer health checks. Decide per dependency where failure handling lives, and avoid doing it twice.
How do sagas keep data consistent without distributed transactions?
A saga runs a sequence of local transactions, one per service. If a step fails, compensating transactions undo the steps that already completed. Choreography uses events between services; orchestration uses a central controller.
How widely is Kubernetes used in production?
CNCF's annual cloud native survey, published on 20 January 2026, reports that 82% of container users run Kubernetes in production.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE