Key takeaway
- Infrastructure as Code security explained: key risks, secrets and state handling, Checkov and Sentinel checks, CI/CD gates and the role of AI agents.
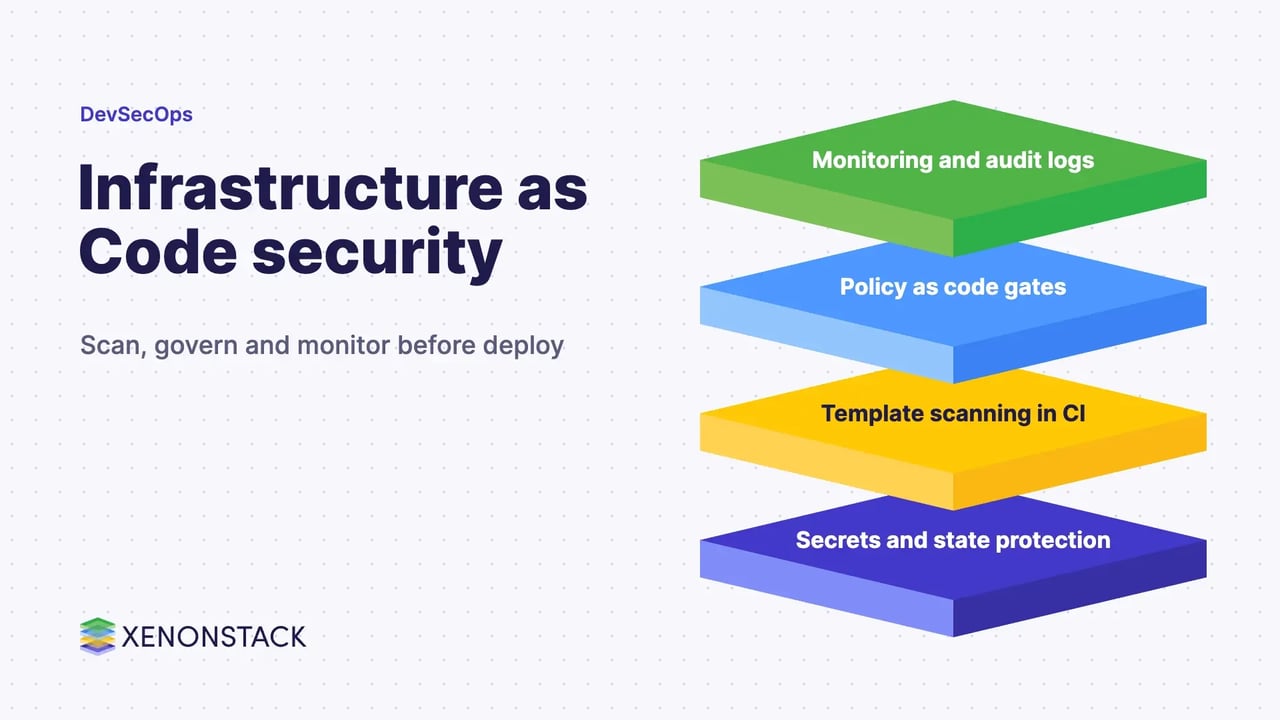
Infrastructure as Code (IaC) security is the practice of checking infrastructure definitions, such as Terraform, CloudFormation or Kubernetes files, for misconfigurations, exposed secrets and policy violations before they are deployed. Because the same files create every environment, one insecure line can be repeated everywhere.
This guide is for DevOps, platform and security teams that already use IaC and want security built into the pipeline. It covers the main risks, the controls that address them, secrets handling, automation tools, and how AI agents change the work. It builds on DevOps and DevSecOps, and on the practice of shifting left.
Why does IaC security matter?
IaC puts infrastructure in version control, so it can be reviewed, tested and rolled back like application code. That also means a mistake in a template, such as an open network rule, an unencrypted store or a hard-coded password, is deployed consistently. Checking templates before deployment, ideally inside the CI/CD pipeline, finds these problems earlier than a runtime scan and keeps live environments from drifting away from the reviewed definition. Teams working this way also benefit from security testing in DevOps and a clear CI/CD pipeline tooling.
What are the main IaC security risks and the controls for each?
| Risk | Control | What to check |
|---|---|---|
| Insecure defaults and open exposure | Static analysis of templates before apply | Open ports, public storage, missing encryption, over-broad access rules |
| Secrets in code or state | Secrets manager, short-lived credentials, protected state | Plain-text passwords and keys in templates, variables and state files |
| Excess privilege | Role-based access and least privilege for people and pipelines | Who can run templates and which permissions the created resources carry |
| Untrusted components | Approved images, modules and registries only | Container images and modules from unknown sources |
| Configuration drift | Change only through the pipeline | Manual edits made directly in production |
| Missing visibility | Logging and monitoring defined in the same templates | Audit logs and alerts for every deployed environment |
| Untagged resources | Mandatory tags and labels enforced by policy | Resources nobody owns or monitors |
How should you handle secrets in IaC?
The OWASP Secrets Management Cheat Sheet notes that many organisations keep secrets hardcoded in source code in plain text, and advises rotating secrets regularly so that stolen credentials work only for a short time. It also says secrets must have the minimum privileges needed for their role, and that pipelines should avoid static bootstrap credentials in favour of short-lived tokens, rather than storing high-value, long-term credentials in CI/CD variables.
State files need the same care. The Terraform documentation on sensitive data warns that secret values added directly to configuration are stored in the state and plan files, and that the sensitive argument only hides values in output while they are still stored. Ephemeral values are omitted from state and plan files entirely, and the page recommends treating state as sensitive: keep it out of Git workflows, store it remotely, encrypt it at rest, limit access and use audit logs.
Which tools automate IaC security checks?
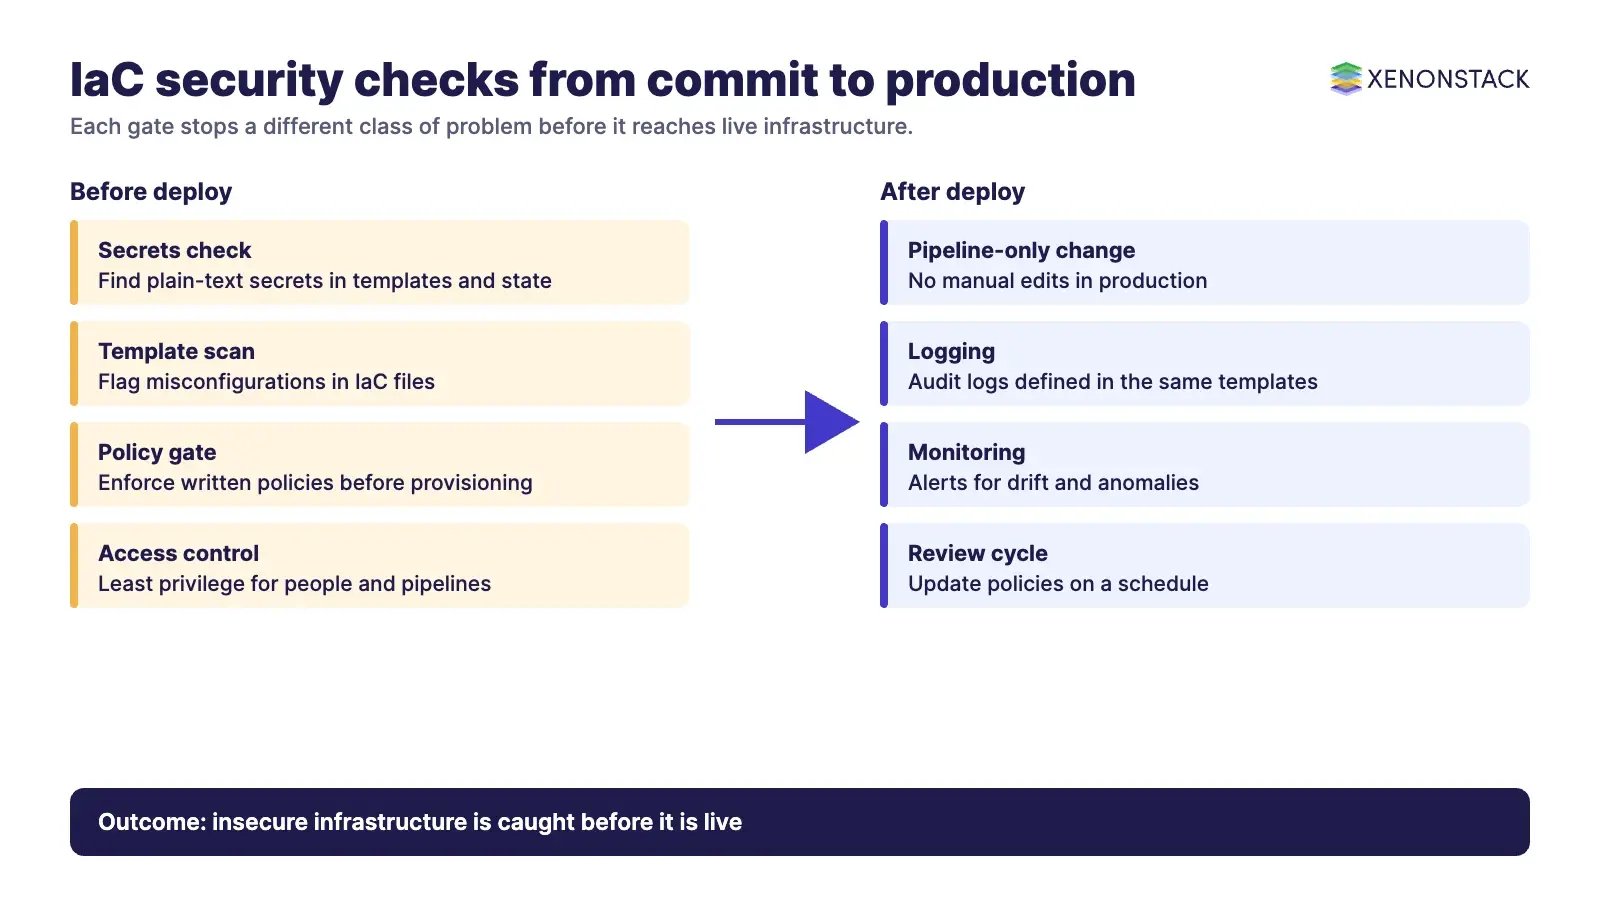
The Checkov documentation describes Checkov as a static code analysis tool that scans IaC files for misconfigurations that may lead to security or compliance problems. It ships with more than 750 predefined policies, supports custom ones, and covers Terraform, CloudFormation, Azure Resource Manager, the Serverless framework, Helm charts, Kubernetes and Docker. The Sentinel documentation defines policy as code as writing code in a high-level language to manage and automate policies, so policies can be versioned, tested and deployed automatically; Sentinel provides a CLI and test framework for this.
| Approach | What it does | Where it runs |
|---|---|---|
| Static template scanning (for example Checkov) | Flags misconfigurations in IaC files against predefined and custom policies | Pre-commit hooks and CI pipelines |
| Policy as code (for example Sentinel) | Enforces written policies before infrastructure is provisioned | Inside supported HashiCorp products such as Terraform |
| Secrets management | Stores, rotates and scopes credentials outside the code | Pipeline and runtime |
| Monitoring and alerting | Watches deployed infrastructure for drift and anomalies | Production |
Compliance mapping sits on top of these checks. Typical targets include ISO 27001, GDPR, SOC 2 and PCI DSS; confirm each control against the standard's official text.
How do AI agents change IaC security?
AI agents can now draft templates, open pull requests and apply changes, which makes the pipeline checks above the control point for machine-written infrastructure too. An agent should receive only the access its task needs, its changes should pass the same scans as a person's, and every action should be recorded. For teams building and running such agents, ElixirClaw is XenonStack's AI agents computing platform, and our DevOps services and solutions covers related automation work.
What should you do first?
- Inventory your IaC repositories and the state locations they use.
- Add a template scanner to the pull request pipeline and fail builds on high-risk findings.
- Search templates and state for plain-text secrets, then move them to a secrets manager and rotate them.
- Restrict who and what can apply changes, and route every change through the pipeline.
- Write your top policies as code, test them, and review them on a schedule.
To map one decision your agents make on your infrastructure, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
For wider infrastructure work, see our infrastructure services.
Frequently asked questions
What is Infrastructure as Code security?
It is the practice of scanning and controlling infrastructure definitions for misconfigurations, exposed secrets and policy violations before they are deployed.
How do you keep secrets out of IaC?
Keep them in a secrets manager, use short-lived credentials, rotate them regularly and protect state files, which can store secret values. The OWASP cheat sheet advises minimum privileges and short-lived pipeline tokens.
Which tools scan IaC for security problems?
Checkov is a static analysis tool for IaC files that covers Terraform, CloudFormation, Kubernetes and more, and Sentinel enforces policy as code in supported HashiCorp products.
What is policy as code?
Policy as code means writing policies in a high-level language so they can be versioned, tested and deployed automatically.
Does IaC security replace runtime security?
No. Template checks find problems before deployment, while logging, monitoring and runtime controls still watch what is actually running.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE