Key takeaway
- Cloud security best practices for 2027: shared responsibility, identity, data, network, detection, response, compliance and agent access, mapped to NIST.
What is cloud security and what are its pillars?
Cloud security is the set of controls, policies and practices that protect data, applications and identities running on cloud platforms. The major frameworks, the AWS Well-Architected Security Pillar, the Azure Well-Architected security principles, the Google Cloud Well-Architected Framework security pillar, the CSA Cloud Controls Matrix and NIST SP 800-53 Rev. 5, agree on the same core pillars: shared responsibility, identity, data protection, network and infrastructure, detection, incident response and compliance.
In 2026 one more thing needs an owner: the software agents and service accounts that now hold cloud credentials. This guide explains each pillar, maps it to the official frameworks, and shows how to govern agent and other non-human access. For the architecture view, read our guides to zero trust security architecture, multi-cloud security and cloud native security and observability.
What does the shared responsibility model mean for your team?
The provider secures the cloud platform itself. You secure what you build and configure on it: identities, data, network rules, workloads and logging. How the line moves between infrastructure, platform and software services differs by provider, so read each one: AWS shared responsibility model, Azure shared responsibility and the Google Cloud shared responsibility and shared fate page. Provider compliance certificates cover the provider's part only. Your workloads and data processing must still meet each standard.
What are the pillars of cloud security going into 2027?
Seven areas cover what an enterprise security team has to own. The table maps each to the controls the official frameworks name. The mapping is our reading of those pages, not a statement by the frameworks.
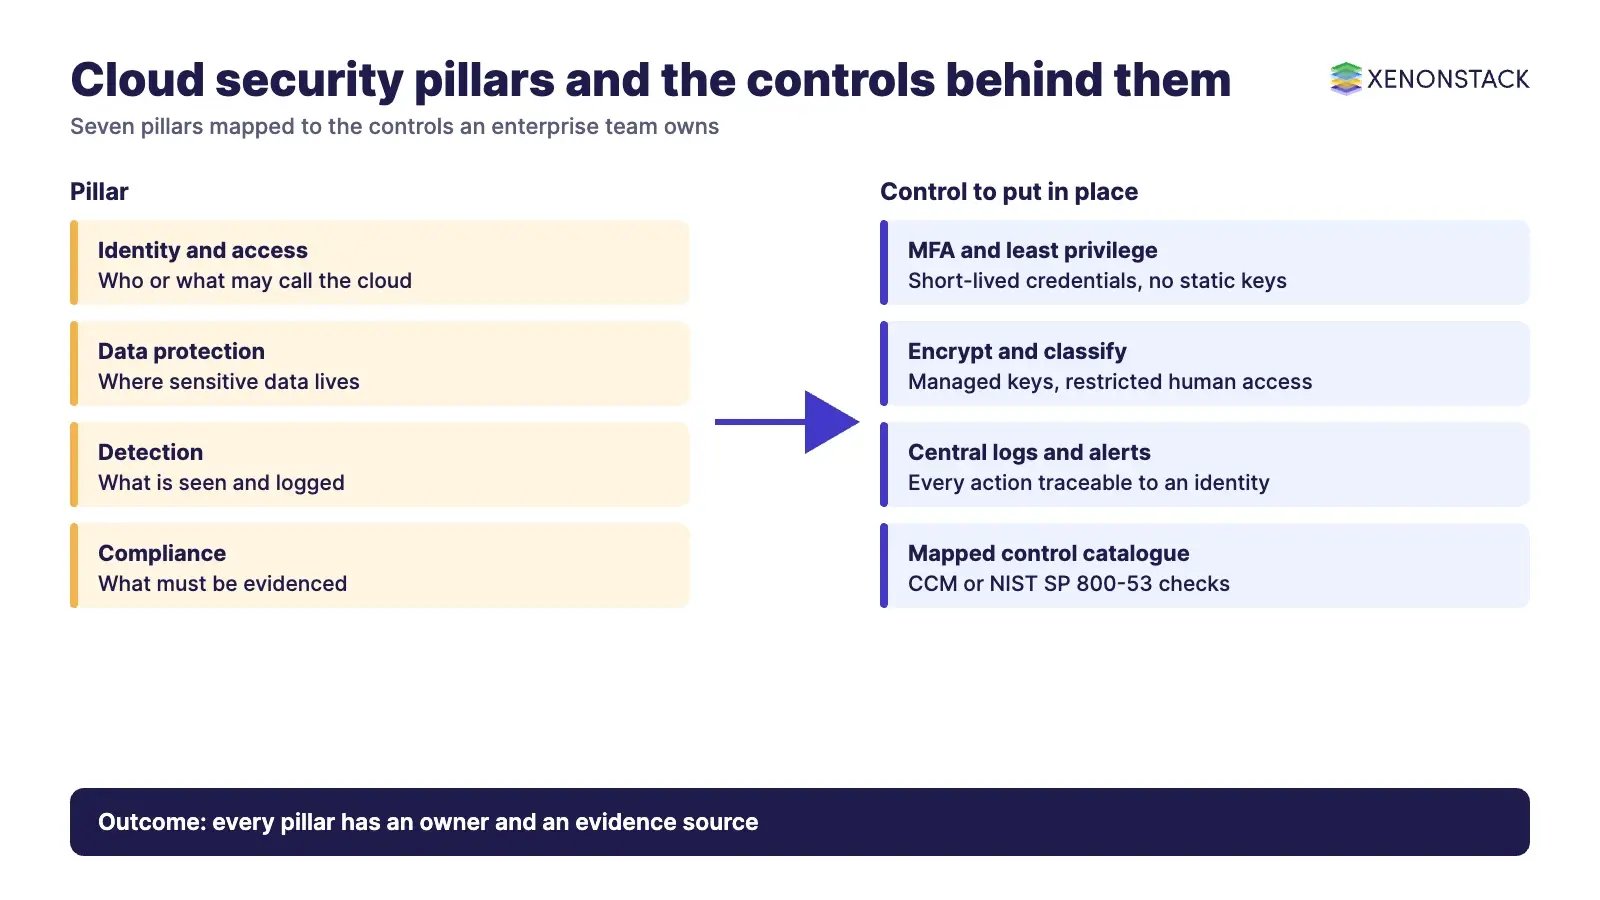
| Pillar | What to put in place | Where the frameworks cover it |
|---|---|---|
| Identity and access | Central identity, least privilege, MFA, no long-term static credentials | AWS: Identity and access management. Azure: use least-privilege access. NIST SP 800-53: Access Control, Identification and Authentication |
| Data protection | Classify data, encrypt in transit and at rest, manage keys, limit direct human access | AWS: Data protection. Azure: protect confidentiality and integrity. NIST SP 800-53: System and Communications Protection, Media Protection |
| Network and infrastructure | Isolate workloads, segment, apply defence in depth at every layer | AWS: Infrastructure protection. Google Cloud: implement zero trust. Azure: assume breach |
| Detection | Central logging, alerting, traceability of every action and change | AWS: Detection. NIST SP 800-53: Audit and Accountability. Google Cloud: preemptive cyber defence |
| Incident response | Written playbooks, simulations, automated containment and recovery | AWS: Incident response. NIST SP 800-53: Incident Response, Contingency Planning |
| Compliance and governance | Map controls to regulations, audit continuously, keep evidence | Google Cloud: meet regulatory, compliance and privacy needs. CSA CCM: GRC domain. NIST SP 800-53: Assessment, Authorization and Monitoring |
| Application and supply chain | Security by design, shift left, scan code, containers and dependencies | AWS: Application security. Google Cloud: security by design, shift-left security. NIST SP 800-53: Supply Chain Risk Management |
Share-ready point: a cloud security programme is seven areas with named owners, not one product.
How do the frameworks differ, and which should you start with?
They overlap more than they differ. The AWS pillar lists seven design principles, including a strong identity foundation, traceability, security at all layers and preparing for security events. Azure frames security around three zero trust principles (verify explicitly, use least-privilege access, assume breach) plus design areas for readiness, confidentiality, integrity, availability and sustaining your posture. The Google Cloud pillar lists seven principles, including security by design, zero trust, shift-left security, using AI securely and responsibly, and using AI for security.
| Framework | What it gives you | When it fits |
|---|---|---|
| AWS Well-Architected Security Pillar | Seven design principles and seven best practice areas | Workloads mainly on AWS, or as a neutral checklist for review workshops |
| Azure Well-Architected security principles | Zero trust principles and design areas | Microsoft-centred estates and teams that want a risk-led view |
| Google Cloud Well-Architected security pillar | Seven principles, including secure and responsible AI | Google Cloud workloads and AI-heavy estates |
| CSA Cloud Controls Matrix v4.1 | 197 control objectives in 17 domains, mapped to ISO, NIST and PCI | Vendor-neutral control baseline and supplier assurance |
| NIST SP 800-53 Rev. 5 | Catalogue of security and privacy controls in 20 families | Regulated sectors and audit-ready control libraries |
Our recommendation: use one provider framework per platform for design reviews, and one control catalogue (CCM or NIST SP 800-53) as the audit spine that all platforms map to.
How should you secure identity and access in the cloud?
Start with identity, because every cloud action is an authenticated call. Require MFA for people, grant only the access a task needs, and review privileges on a schedule. Cloud roles are often set too broadly, for example write or delete rights given to users who only read. The AWS pillar also advises centralising identity management and aiming to remove reliance on long-term static credentials. Prefer short-lived credentials issued per session over keys stored in code or configuration.
How do you protect data in the cloud?
Classify data by sensitivity first, then choose controls to match: encryption in transit and at rest, tokenisation where suitable, key management with separate duties, and access control. The AWS pillar adds a useful principle, keep people away from data, meaning automate handling so fewer humans touch sensitive records. Back up critical data and test restores, because recovery is part of data protection.
How do you secure the cloud network?
Place critical applications in isolated network segments, such as a virtual private cloud on AWS or a virtual network on Azure, and apply strict policy between segments. Add a web application firewall in front of web applications to watch traffic in and out. Do not trust a request because of its network location; decide each request by policy. The full model is in our zero trust security architecture guide, which follows NIST SP 800-207.
How do you detect threats and respond to incidents?
Collect cloud-native logs centrally, compare them with signals from vulnerability scanners, asset inventory, change management and threat intelligence, and alert on deviations. The AWS pillar calls this traceability: monitor, alert and audit actions and changes in near real time. Detection only helps if someone acts, so write incident playbooks, run simulations, and automate containment for the common cases. See threat intelligence for security monitoring and incident response and cloud native security and observability for the monitoring side.
How do you meet compliance requirements in the cloud?
Treat compliance as continuous evidence, not an annual audit. Pick a control catalogue, map each control to a cloud setting that can be checked automatically, and alert on drift. The CSA Cloud Controls Matrix v4.1 has 197 control objectives in 17 domains and is aligned to standards such as ISO, NIST and PCI. NIST SP 800-53 Rev. 5 organises its catalogue into 20 families, from Access Control to Supply Chain Risk Management. Regulations that apply to you (for example GDPR, HIPAA or PCI DSS) are your responsibility even when the provider holds a certificate; confirm current requirements on each regulator's official page.
How do you govern AI agents and other non-human access?
Service accounts, pipelines and AI agents now act in your cloud with real credentials, and they are not covered by MFA prompts or joiner and leaver processes. The frameworks above do not yet give agents a pillar of their own, so the practical approach is to apply the identity, detection and incident pillars to them. Treat this list as our recommendation, built on those pillars.
| Control | What to do for an agent or service identity | Pillar it extends |
|---|---|---|
| Inventory | Register every agent, service account and token with a named human owner | Identity and access |
| Least privilege | Give each agent its own role scoped to one task, never a shared admin role | Identity and access |
| Short-lived credentials | Issue credentials per session and expire them, in line with the AWS aim to avoid long-term static credentials | Identity and access |
| Action logging | Log every tool call and cloud action with the agent identity and the reason | Detection |
| Policy before action | Check each high-impact action against written policy before it runs, with human approval where the impact is high | Compliance and governance |
| Kill switch | Be able to revoke an agent's credentials in minutes and to roll back its changes | Incident response |
Platforms that keep governed context, versioned policy and decision traces in one layer above AI agents make the policy and logging rows easier to evidence; see ElixirData Context OS, and AgentGRC, which according to its site keeps autonomous agent actions inside policy, with the audit trail risk teams need.
What is a practical order for improving cloud security?
| Step | Action | Exit check |
|---|---|---|
| 1 | Inventory accounts, subscriptions, identities and agents | Every one has an owner |
| 2 | Enforce MFA and remove standing admin and static keys | No long-term keys found in a scan |
| 3 | Classify data and encrypt it, with managed keys | Sensitive stores listed with key owner |
| 4 | Segment the network and put a firewall in front of web apps | Critical workloads isolated |
| 5 | Centralise logs and alerting | One alert reaches a person within your target |
| 6 | Write and rehearse incident playbooks | One simulation completed and reviewed |
| 7 | Map controls to CCM or NIST SP 800-53 and automate checks | Drift alerts raised automatically |
What are the main challenges of cloud security?
The challenges that recur in cloud programmes are a larger attack surface, limited visibility below the provider's boundary, workloads that appear and disappear quickly, over-broad privileges and keys, complex multi-cloud and hybrid estates, and keeping compliance continuous. Each maps to one pillar above: visibility to detection, privileges to identity, complexity to the audit spine, and fast-changing workloads to automated controls defined as code.
When are these best practices not enough?
Checklists do not replace a threat model. Regulated workloads may need controls beyond the provider baselines, and multi-cloud estates need a shared control layer rather than three separate ones. If you cannot name an owner for each pillar, fix that before buying tools.
To map one decision your agents should make in the cloud, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
If you use the CSA Cloud Controls Matrix as your audit spine, one date matters for next year. Check these points against your own assurance plans.
- December 2027: per the Cloud Security Alliance transition timeline, only submissions based on CCM and CAIQ version 4.1 will be accepted for STAR Level 1 and Level 2, and Level 1 surveillance audits and recertifications must use CAIQ v4.1.
- January 2028: the same page says CCM v4.0.x and CAIQ v4.0.x will be withdrawn, so plan the move to v4.1 mappings during 2027.
- Review identity, agent access and logging controls on a schedule, so evidence is ready before any audit window.
Frequently asked questions
What are the pillars of cloud security?
Seven areas: identity and access, data protection, network and infrastructure, detection, incident response, compliance and governance, and application security, with the shared responsibility model underneath. They follow the AWS Well-Architected Security Pillar best practice areas and the Azure and Google Cloud frameworks.
What is the shared responsibility model?
The provider secures the cloud platform itself and the customer secures what it builds and configures on it, including identities, data, network rules and logging. The split varies by service model, so check each provider's page.
Which framework should we use for cloud security?
Use the provider's own well-architected security guidance for design reviews and one control catalogue, such as the CSA Cloud Controls Matrix (197 control objectives, 17 domains) or NIST SP 800-53 Rev. 5 (20 control families), as the common audit baseline.
How do you secure AI agents and service accounts in the cloud?
Give each its own owner, a narrowly scoped role and short-lived credentials, log every action with the agent identity, check high-impact actions against policy before they run, and be able to revoke access quickly.
Does a provider's compliance certificate make our workloads compliant?
No. It covers the provider's part. You remain responsible for how your workloads, data and identities meet each regulation or standard.
What is the most important first step?
Inventory your identities, including service accounts and agents, then enforce MFA and least privilege, because every cloud action depends on an authenticated identity.
Related reading: multi-cloud security, zero trust security architecture and cloud native security and observability.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE