Key takeaway
- ISO 27001 explained: what the ISMS standard requires, how clauses 4 to 10 and Annex A fit, what certification means and the first steps to take.
ISO/IEC 27001 is the international standard that sets out the requirements for an information security management system (ISMS), a managed framework for protecting the confidentiality, integrity and availability of an organisation's information. It is built on risk management: you find the risks to your information, then decide and record how to treat them.
This guide is for security, compliance and technology leaders who are deciding whether to adopt the standard or seek certification. It covers what the standard requires, how it is structured, what certification means, how it connects to other frameworks, and what to do first. It is a plain-language overview, and the standard itself remains the authority.
What is ISO/IEC 27001?
The ISO page for ISO/IEC 27001 says the standard defines requirements an ISMS must meet, and that it gives organisations of any size and from any sector guidance on establishing, maintaining and improving one. The current edition is ISO/IEC 27001:2022, the third edition, published in October 2022. ISO lists one amendment, from 2024, covering climate action changes, and notes that the 2013 edition has been withdrawn. If you still work from a 2013 checklist, update it.
The scope clause in the preview of ISO/IEC 27001:2022 states that the standard specifies requirements for establishing, implementing, maintaining and continually improving an ISMS within the context of the organisation, and that it includes requirements for assessing and treating information security risks, tailored to the needs of the organisation.
What does ISO 27001 protect?
The standard centres on three properties of information, and the ISMS exists to preserve them by applying a risk management process.
- Confidentiality: information is not made available or disclosed to unauthorised people, entities or processes.
- Integrity: information is complete and accurate, and protected from corruption.
- Availability: information is accessible and usable when authorised users need it.
Technology controls such as firewalls and backups help, but they do not on their own decide which risks matter. The ISMS adds people, process and policy around the technology, so protection is managed consistently across paper, digital and cloud records.
How is the standard structured?
According to the contents of the preview of ISO/IEC 27001:2022, the standard has clauses 0 to 10 and a normative Annex A of reference control objectives and controls. Clauses 4 to 10 are the ones that set out what an organisation works through.
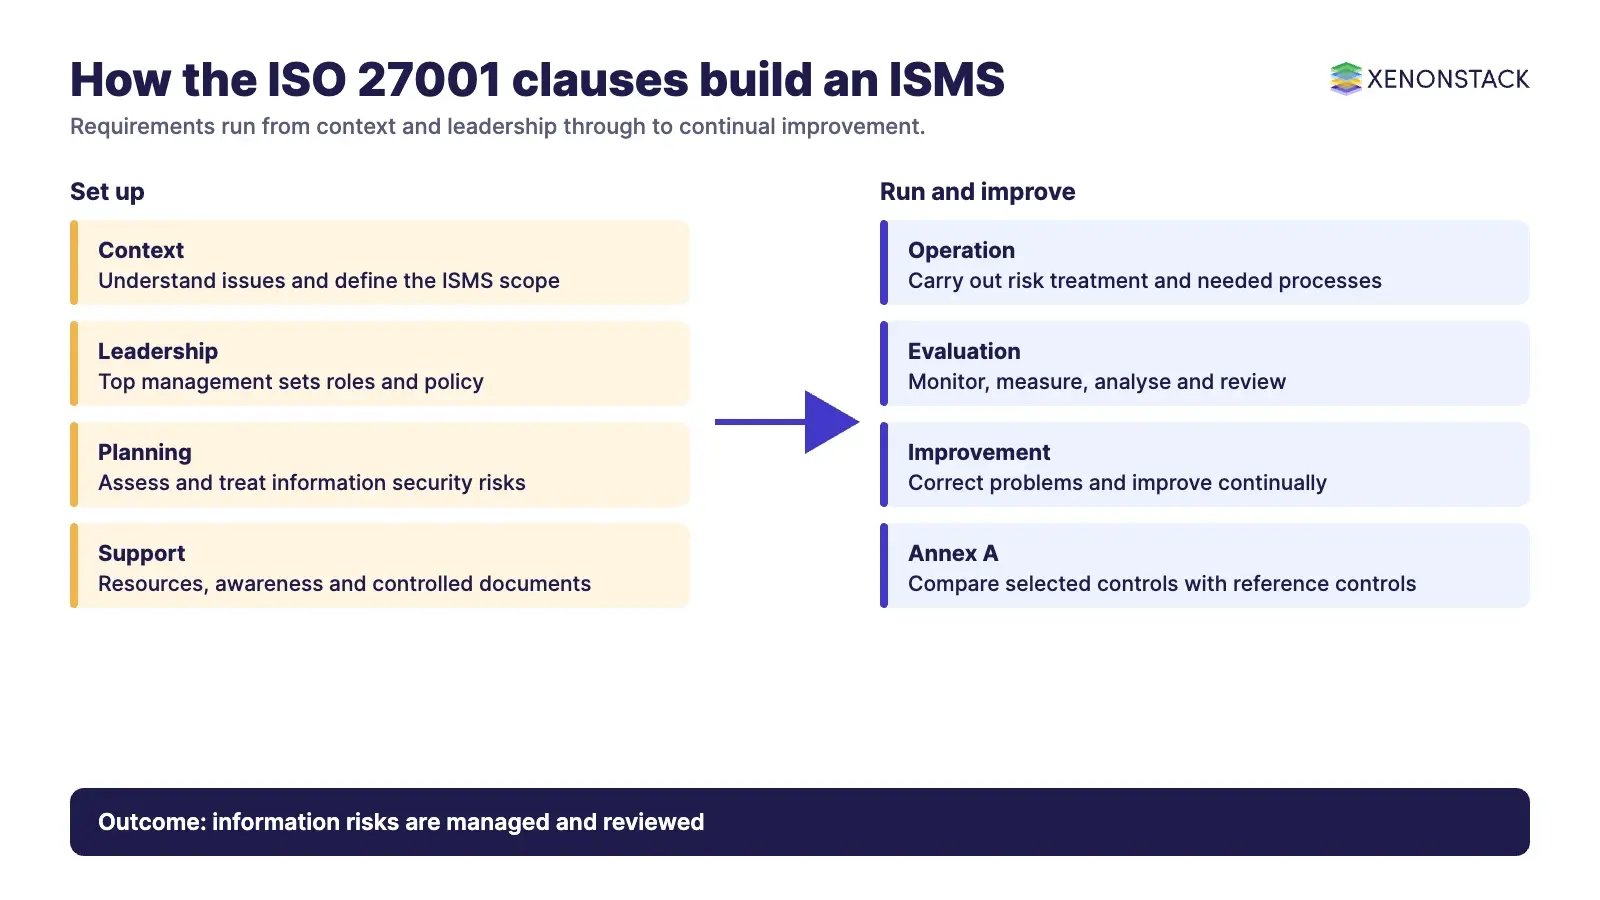
| Clause | Title | What it asks for |
|---|---|---|
| 4 | Context of the organization | Understand internal and external issues and define the ISMS scope |
| 5 | Leadership | Top management sets roles, responsibilities and policy |
| 6 | Planning | Assess and treat risks and set information security objectives |
| 7 | Support | Provide resources, awareness, communication and controlled documents |
| 8 | Operation | Carry out the risk assessment and treatment and the processes the objectives need |
| 9 | Performance evaluation | Monitor, measure, analyse and review |
| 10 | Improvement | Correct problems and improve continually |
Annex A provides the reference controls that you compare against the controls your risk treatment selects. Read the current text for the exact list.
Who needs ISO 27001 certification?
Any organisation that collects, processes or stores information can adopt the standard. ISO states that certification is optional: you can implement the standard for its practices without certifying, or certify to reassure customers. A certificate from an accredited certification body adds independent confidence. ISO also advises describing it as "certified to ISO/IEC 27001:2022" rather than "certified to ISO 27001".
| Route | What you do | When it suits |
|---|---|---|
| Implement without certifying | Build the ISMS and follow the standard's practices | You want a structure and are not asked for proof |
| Implement and certify | Build the ISMS, then have an accredited body assess it | Customers or partners ask for independent assurance |
What are the benefits of an ISMS?
- One managed framework for information security, instead of separate tools and habits.
- A documented, repeatable way to find and treat risk across the organisation.
- Clear leadership accountability and a record of decisions.
- A basis for answering customer security questions from evidence.
- A cycle of review and improvement, so the system keeps pace with change.
How do AI agents change ISO 27001 work?
The organisation sets the ISMS scope, so AI agents that read, write or act on information inside that scope belong in the risk assessment like any other system. Each agent adds questions: what information it can reach, which actions it may take, who approves them, and how its decisions are recorded for review. The standard does not prescribe an agent design, so you translate its risk and control logic into rules for agents. ElixirData, XenonStack's Context OS, is where decisions and the context behind them can be governed.
What should you do first?
- Obtain the current edition of the standard and confirm which edition your policies cite.
- Define the ISMS scope and name the leader who owns it.
- Run a risk assessment, list the risks and choose treatments.
- Compare your selected controls with Annex A and record gaps.
- Decide whether you will certify, and plan the review cycle either way.
Related reading: GDPR compliance and PCI DSS compliance. For wider help, get in touch with us.
To map one decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
Which edition of ISO/IEC 27001 is current?
ISO/IEC 27001:2022 is the current third edition of the standard, published in October 2022. ISO states that the 2013 edition has been withdrawn.
Is ISO 27001 certification mandatory?
No. ISO states that certification is optional, and organisations can implement the standard for its practices without seeking certification.
Who can use ISO 27001?
ISO says the standard gives organisations of any size and from all sectors of activity guidance on establishing, maintaining and improving an information security management system.
Which clauses contain the requirements?
Clauses 4 to 10 contain the requirements, covering context, leadership, planning, support, operation, performance evaluation and improvement. Annex A lists reference controls.
What three properties does an ISMS protect?
Confidentiality, integrity and availability of information.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE