Key takeaway
- Cyber-physical systems explained: NIST CPS Framework aspects, examples, architecture layers, OT security standards and a practical adoption path.
What is a cyber-physical system?
A cyber-physical system (CPS) is a system in which computing, communication and control are tied to a physical process in a closed loop. NIST describes cyber-physical systems as interacting digital, analog, physical and human components engineered for function through integrated physics and logic. A sensor reads the physical world, software decides, and an actuator changes it. Smart grids, industrial control systems and autonomous vehicles are the usual examples.
For enterprise leaders the practical point is that a CPS fails differently from a business application. A wrong answer can move a valve, a vehicle or a medical device. That is why this guide leans on the NIST CPS Framework, the NIST guide to operational technology security and ISA/IEC 62443 rather than on generic IoT advice. If you only need the connectivity layer, read our IoT workings guide and IoT edge analytics trends first.
How is a CPS different from IoT and an ordinary IT system?
NIST lists cyber-physical systems and the Internet of Things as related terms, and the Framework abstract says both could affect energy, manufacturing, transportation, buildings and healthcare. The difference for design is where the weight sits.
| Dimension | Ordinary IT system | IoT deployment | Cyber-physical system |
|---|---|---|---|
| Main concern | Data and transactions | Connecting devices and moving data | Controlling a physical process through a feedback loop |
| Cost of a wrong output | Rework or loss of data | Bad analytics | Physical consequence, so safety and resilience are design inputs |
| Timing | Usually tolerant | Varies by use | Often strict, so synchronisation and latency are first-class concerns |
| Security guidance to start with | General IT frameworks | Device baseline and vendor guidance | NIST SP 800-82 Rev. 3 and ISA/IEC 62443 |
The table is our own working comparison, not a NIST classification. Pick the guidance that matches the process you are protecting and confirm current revisions on the official pages.
What does the NIST CPS Framework say about aspects and facets?
The Framework for Cyber-Physical Systems, NIST Special Publication 1500-201, was published by NIST on 26 June 2017, developed with the CPS Public Working Group. It gives a structured way to analyse a CPS using facets and aspects. The three facets are modes of the engineering process: conceptualization, realization and assurance. The nine aspects are the concerns to examine in each facet.
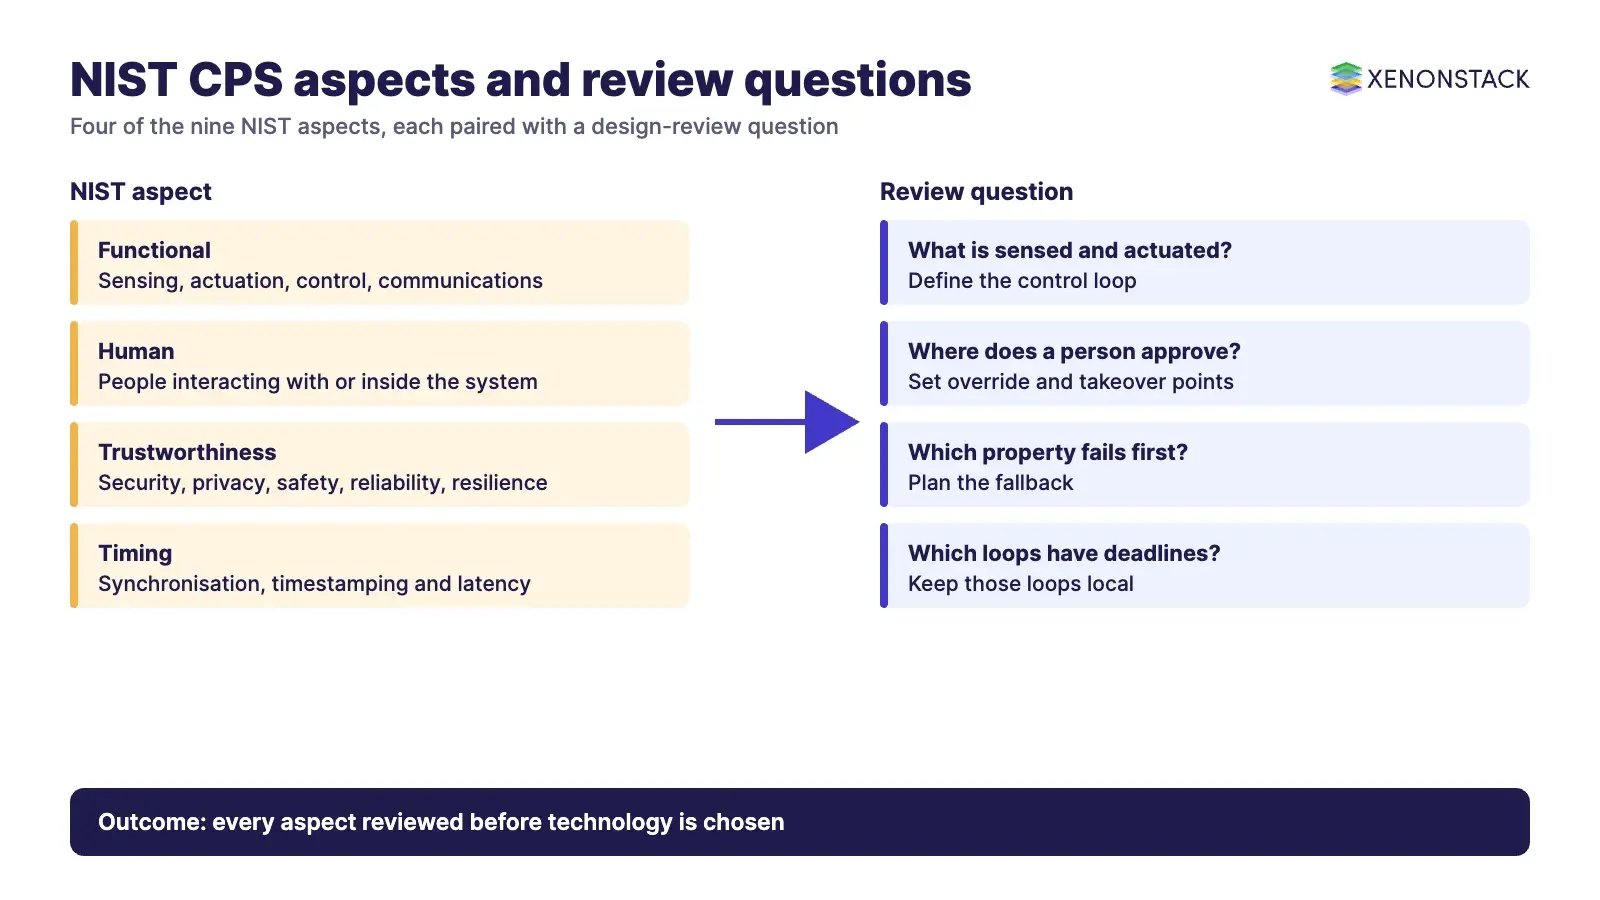
| Aspect (NIST) | What it covers | Question to ask in a design review |
|---|---|---|
| Functional | Sensing, actuation, control and communications | What does the system sense, decide and actuate? |
| Business | Enterprise, cost, regulation, time to market, environmental impact | Who owns the outcome and which rules apply? |
| Human | How people interact with and act as part of the system | Where does a person approve, override or take over? |
| Trustworthiness | Security, privacy, safety, reliability and resilience | Which of the five fails first, and what is the fallback? |
| Timing | Time and frequency, including synchronisation, timestamping and latency | Which loops have hard deadlines? |
| Data | Interoperability, such as semantics, identity and fusion | Do all components agree on what the data means? |
| Boundaries | Demarcations between topological, functional or organisational interactions | Where does our responsibility end and a supplier's begin? |
| Composition | Deriving system properties from component properties | Does a safe part make a safe whole? |
| Lifecycle | The system and its components across their full lifespan | How are updates, ageing hardware and retirement handled? |
Source: NIST, Framework for Cyber-Physical Systems: Volume 1, Overview, and the aspect definitions in SP 1500-201. The review questions in the third column are our own working prompts, not NIST text.
Where are cyber-physical systems used?
The same loop appears across sectors. The table pairs each with the CPS element that usually matters most. Sector pairings are illustrative.
| Sector | Typical CPS | Aspect that usually dominates |
|---|---|---|
| Manufacturing | Industrial control systems and machine monitoring; see edge AI in smart factories | Timing and safety |
| Transportation | Autonomous vehicles and rail or bus control; see edge AI for autonomous vehicles | Trustworthiness and timing |
| Energy | Smart grids that adapt to demand and conditions | Resilience and boundaries |
| Healthcare | Ventilators and patient monitoring | Safety and human |
| Agriculture | Irrigation control and crop monitoring through sensors | Data and lifecycle |
| Buildings | Building automation and environmental monitoring, both named in NIST SP 800-82 Rev. 3 | Functional and lifecycle |
What are the layers of a CPS architecture?
There is no single standard layer count, so treat this as a working model that maps to the NIST functional aspect.
| Layer | Role | Design note |
|---|---|---|
| Physical process | The plant, vehicle, grid or patient | Defines the safety envelope |
| Sensing and actuation | Reads and changes the process | Calibration and failure modes matter |
| Control | Deterministic logic that closes the loop | Keep it local when latency is tight; see edge computing |
| Communication | Networks and protocols between layers | Segment by function and trust |
| Data and analytics | Telemetry, real-time analytics and models | Advisory unless validated for control |
| Operations and governance | Monitoring, change control, audit | See observability and the trace of every decision |
What are the main risks and how do the standards help?
Interconnection widens the attack surface, and failures can have physical consequences. Four challenges recur: cybersecurity, interoperability between components, scalability, and safety-critical behaviour. Two official sources give a practical starting point.
NIST SP 800-82 Rev. 3, Guide to Operational Technology (OT) Security (September 2023): covers programmable systems that monitor or control physical processes, including industrial control, building automation, transportation, physical access control and environmental monitoring. It describes typical OT layouts, common threats and vulnerabilities, and recommended countermeasures, with performance, reliability and safety needs in mind. NIST states that an initial public draft of Revision 4 is open for comment, so check the current revision. NIST CSRC page.
ISA/IEC 62443: a series of standards for industrial automation and control system security, covering people, processes and technology across the lifecycle, with requirements for asset owners, product suppliers, integrators and service providers. ISA page.
Controls that follow from this guidance are familiar: continuous verification of users and devices (see zero trust security architecture and implementing zero trust), anomaly detection on telemetry, patching and compensating controls for legacy equipment, and feedback loops that watch both performance and security. For IoT-heavy estates, see SOC automation for IoT security and cybersecurity with agentic AI.
How should an organisation adopt a CPS?
A sequence that holds up in practice:
Pick one process: Choose a physical process where a better decision has a clear value, such as quality, uptime or energy use.
Map the loop: List sensors, actuators, timing needs and the consequence of each failure.
Apply the NIST aspects: Run the nine aspects as a design-review checklist before choosing technology.
Decide where control lives: Keep time-critical control local; use cloud or edge analytics for advice and optimisation.
Pilot in simulation, then in a limited zone: Validate performance and reliability before scaling.
Operate with monitoring and audit: Monitor behaviour, security and drift, and keep a trace of changes.
When is a CPS the wrong choice?
When the process has no physical effect that needs closing a loop. Plain analytics is cheaper and safer.
When the team cannot own the safety case, patching and lifecycle of the physical equipment.
When latency or connectivity cannot be guaranteed and no local fallback exists.
When a model would sit directly in a safety-critical control path without independent validation.
Where do AI agents fit in a CPS?
Machine learning and agents are most useful above the control loop: triaging alerts, forecasting, preparing maintenance and change requests, and explaining anomalies to operators. Safety-critical control should remain in deterministic, validated systems, with humans approving any action that could affect safety, starting with reversible actions. See agentic workflows for governed patterns. NexaStack is an agentic operating platform for physical AI that runs across on-premises, cloud and hybrid environments, and ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents. For audit evidence, the Audit Agent page covers audit trails and compliance evidence.
To map one operational decision your agents should make in a physical process, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
FAQ about cyber-physical systems
What is a cyber-physical system in simple terms?
A cyber-physical system combines digital, analog, physical and human components that work together through physics and logic, which is how NIST describes it. A sensor reads the physical world, software decides, and an actuator changes the physical world.
Is a cyber-physical system the same as the Internet of Things?
No. NIST lists cyber-physical systems and the Internet of Things as related terms, but the emphasis differs. IoT is mainly about connecting devices and moving data. A CPS is defined by a closed loop in which computation controls a physical process, so timing, safety and failure behaviour matter far more.
What are the NIST CPS Framework aspects?
NIST Special Publication 1500-201 lists nine aspects: functional, business, human, trustworthiness, timing, data, boundaries, composition and lifecycle. Trustworthiness covers security, privacy, safety, reliability and resilience.
Which standards cover CPS security?
NIST SP 800-82 Rev. 3 is the guide to operational technology security, covering systems that monitor or control physical processes. ISA/IEC 62443 is the series of standards for industrial automation and control system security. Confirm the current revision of each on the official page before citing it in a design or audit.
Can AI agents control a cyber-physical system?
They can advise and prepare actions, but in safety-critical loops the control logic should stay in certified, deterministic systems. Agents are better placed above the loop, in triage, planning and change preparation, with policy limits, human approval for anything that could affect safety, and a decision trace.
Where should an organisation start?
Start with one physical process where a better decision has a clear value, map its sensors, actuators, timing needs and failure consequences, and apply the NIST aspects as a checklist before choosing technology.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE