Key takeaway
- Kubernetes security automation for enterprise teams: what to automate at build, admission and runtime, which tools fit, and what has been retired.
What is Kubernetes security automation, and what should you automate first?
Kubernetes security automation means turning security rules into checks that run on their own at build time, at admission and at runtime, so that no cluster depends on a person remembering a step. Start with the controls that stop a bad change before it runs: image scanning in the pipeline, admission policy on the API server, and least-privilege access. Then add runtime detection and compliance reporting. For the cluster components these controls attach to, see our guide to Kubernetes architecture and its components.
The reason to automate is scale and drift. A cluster changes every time someone deploys, and a manual review cannot keep up. Automation gives security and platform teams one set of rules, applied the same way in every cluster, with evidence of what was allowed or blocked. It fits a wider zero trust approach, where nothing is trusted by default.
Which security controls belong at which stage of the pipeline?
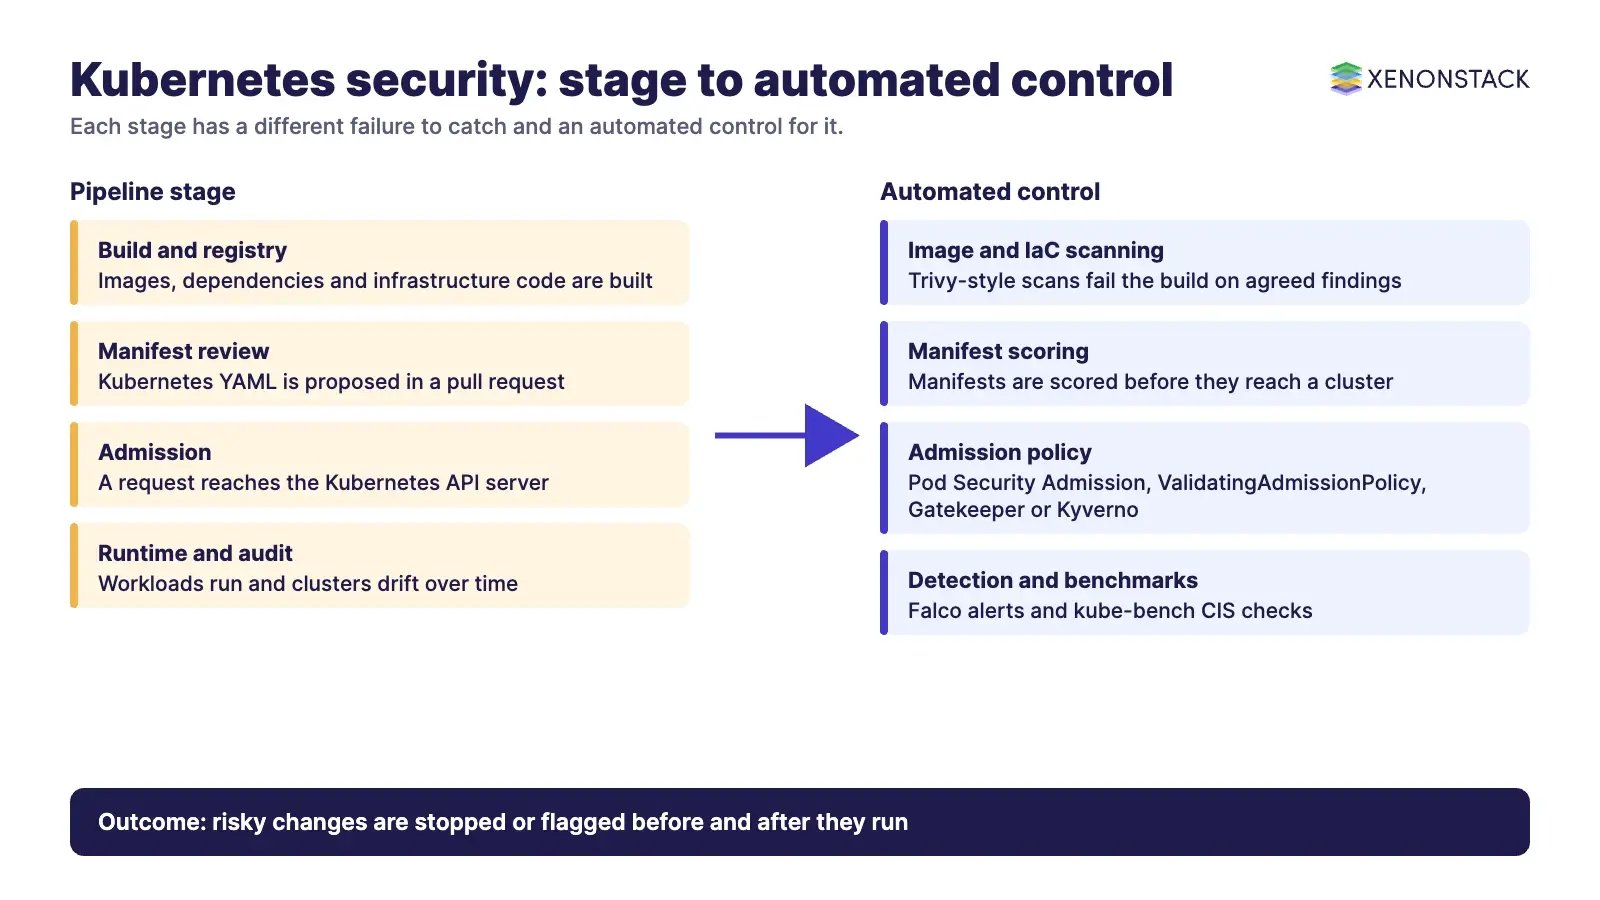
Think in four stages. Each one has a different failure to catch, and a different owner. The tools named are examples from the projects read for this guide, not a recommendation list.
| Stage | What to automate | Example tools | When it fits |
|---|---|---|---|
| Build and registry | Scan images, dependencies, secrets and infrastructure code; fail the build on agreed findings | Trivy (project page) scans images, filesystems, Git repositories and Kubernetes for vulnerabilities, misconfigurations, secrets and licences | Every pipeline, before an image is pushed |
| Manifest review | Score or lint Kubernetes YAML before it reaches a cluster | kubesec (kubesec.io) scores resource manifests; its v1 API is deprecated, so check the current release | Pull requests that change manifests or Helm output |
| Admission | Reject or warn on workloads that break policy at the API server | Pod Security Admission, ValidatingAdmissionPolicy, Gatekeeper, Kyverno | Every cluster that accepts changes from more than one team |
| Runtime and audit | Detect abnormal behaviour; check the cluster against a benchmark | Falco for runtime detection; kube-bench for CIS Kubernetes Benchmark checks | Production clusters and regulated workloads |
Infrastructure code deserves the same treatment as application code. When cluster and network settings are defined as infrastructure as code, the same scanners and reviews apply to them before anything is provisioned. The pipeline view is covered further in our DevOps pipeline on AWS guide.
What has changed in Kubernetes security tooling?
Several tools named in older guides, including an earlier version of this one, are no longer current. Check these before you copy an older design.
| Item | Current status | Source |
|---|---|---|
| PodSecurityPolicy | Deprecated in Kubernetes 1.21 and removed in 1.25 | Kubernetes blog |
| Pod Security Admission | Built-in replacement for PodSecurityPolicy; applied per namespace with enforce, audit and warn modes against the Privileged, Baseline and Restricted standards | Kubernetes docs |
| ValidatingAdmissionPolicy | Stable since Kubernetes 1.30; declarative rules written in the Common Expression Language (CEL) that run inside the API server | Kubernetes docs |
| Trireme | Repository archived by its owner on 12 May 2025 and now read-only | GitHub |
| Supported releases | Latest stable minor is 1.37 (1.37.1, released 2026-09-15); the three most recent minors are maintained | Kubernetes releases |
The practical lesson is to plan upgrades as a security control. A cluster on an unsupported minor release stops receiving patches, and removed features such as PodSecurityPolicy fail silently into gaps if the replacement was never configured.
How do admission control and policy as code work together?
Admission control runs when a request reaches the Kubernetes API server, before the object is stored. Policy as code means the rules live in version control, are reviewed like application code, and are applied by the cluster itself. The four options below overlap, so choose by who writes the rules and how much custom logic you need.
| Option | What it does | When it fits |
|---|---|---|
| Pod Security Admission | Applies the Privileged, Baseline or Restricted pod standard to a namespace through labels | A first, built-in baseline with no extra components |
| ValidatingAdmissionPolicy | Runs CEL validation rules in-process, with no webhook service to deploy | Teams that want declarative rules without running a separate policy service |
| OPA Gatekeeper | Validating and mutating admission webhook that evaluates Open Policy Agent policies; reusable ConstraintTemplates and Constraints, plus audit of existing resources (docs) | Organisations that already use OPA and Rego, or need audit of existing resources |
| Kyverno | Policy engine that can validate, mutate, generate and clean up resources and verify container images; policies are written in YAML or CEL (docs) | Platform teams that prefer Kubernetes-style policy files over a separate policy language |
Run new policies in audit or warn mode first, read the violations for a sprint, and only then switch to enforce. Enforcing on day one is the most common reason teams switch automation off.
What configuration baseline should every cluster have?
Tools help only when the underlying settings are sound. The Kubernetes security documentation covers these areas, and each can be checked automatically.
- Access control: Use role-based access control with least privilege, and follow the RBAC good practices page. Review service account permissions as carefully as user permissions.
- Network policy: Restrict which pods can talk to each other. The network policy documentation states that your cluster must use a network plugin that supports NetworkPolicy enforcement, so confirm this before relying on any policy.
- Secrets: The encryption at rest guide says that all Kubernetes APIs that persist resource data support encryption at rest, in addition to any system-level encryption of etcd or host filesystems.
- Privileged workloads: Use the Restricted pod standard for application namespaces and keep Privileged only for system and infrastructure namespaces.
- Benchmarks: Run kube-bench against the CIS Kubernetes Benchmark. Its README notes there is no one-to-one mapping between Kubernetes releases and Benchmark releases, so match the benchmark version to your cluster (kube-bench).
How do you detect and respond at runtime?
Falco is a graduated CNCF project that reads Linux system call activity, enriches it with container and Kubernetes metadata and evaluates it against YAML rules (Falco docs). Its default rules cover behaviours such as privilege escalation through privileged containers, shell execution and changes to sensitive directories. Alerts can be forwarded to a SIEM or data lake. Pair detection with cloud-native observability so that a security alert arrives with the metrics and logs an engineer needs to judge it.
Detection is only useful if someone acts on it. Decide in advance which alerts page a person, which open a ticket, and which trigger an automatic action such as isolating a workload. Keep automatic action for well understood cases.
How do you govern automation and AI agents that change clusters?
Security automation is itself a change agent: it blocks deployments, opens tickets and, increasingly, proposes fixes. The risk moves from the misconfigured pod to the automated action nobody can explain later. Each automated decision should record which policy applied, what evidence it used and who approved the exception. Teams that run Kubernetes as a managed service already see this in practice. For example, our own operations team automates a weekly security report with a Kubernetes CronJob, which shows how routine reporting can move off manual effort.
For agent-driven operations, ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. The Audit Agent covers audit trails and compliance evidence, and ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
In what order should you adopt Kubernetes security automation?
- Inventory clusters, owners and Kubernetes versions, and upgrade any that are unsupported.
- Add image and manifest scanning to the pipeline, report-only at first.
- Apply Pod Security Admission in warn and audit mode, then enforce on new namespaces.
- Add one policy engine (ValidatingAdmissionPolicy, Gatekeeper or Kyverno) for rules the built-in standards do not cover.
- Run benchmark checks on a schedule and send results to the owners of each cluster.
- Add runtime detection with a clear response path, then review what automation did each month.
What are the trade-offs, and when should you not automate?
Every added policy engine is one more component to run, upgrade and understand. Webhook-based engines add a network dependency to the API server path, so decide what happens when the webhook is unreachable. Overly strict scanners fail builds for findings nobody can fix, which trains teams to bypass them. Do not block automatically on a rule you cannot explain to a developer in one sentence, and do not automate response on a service whose behaviour you have not yet baselined. Automation also does not replace threat modelling or access reviews.
To map one Kubernetes security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
Is Kubernetes secure by default?
Not on its own. Security depends on configuration: access control, network policy, pod standards and secrets handling all need to be set. The Kubernetes security documentation treats these as settings to apply and review, which is why automating the checks matters.
Is PodSecurityPolicy still available?
No. It was deprecated in Kubernetes 1.21 and removed in 1.25. Use Pod Security Admission for the built-in baseline and add ValidatingAdmissionPolicy, Gatekeeper or Kyverno for custom rules.
What is the difference between ValidatingAdmissionPolicy and Gatekeeper or Kyverno?
ValidatingAdmissionPolicy is stable since Kubernetes 1.30 and runs CEL rules inside the API server with no webhook. Gatekeeper evaluates Open Policy Agent policies through an admission webhook, and Kyverno can also mutate, generate and clean up resources and verify images.
What does Falco do?
Falco is a graduated CNCF runtime security tool. It reads system call activity, adds container and Kubernetes context, checks it against YAML rules and raises alerts that can be forwarded to a SIEM.
How do you check a cluster against the CIS benchmark?
kube-bench runs the checks in the CIS Kubernetes Benchmark. Match the benchmark version to your Kubernetes version, because releases do not map one to one.
Which Kubernetes versions are supported?
As read on 12 November 2026, the latest stable minor is 1.37, and the three most recent minors are maintained.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE