Key takeaway
- Agentic AI risk management for enterprises: how to tier agents, map NIST AI RMF functions to controls, limit agency, and plan for the EU AI Act.
Agentic AI risk management is the discipline of deciding what an AI agent may do, with which data and permissions, under whose approval, and how every action is recorded. It covers two questions: how to govern the risks agents create, and where agents can safely take on work inside your own risk, fraud and compliance processes. Both need the same foundation: an inventory of agents, a risk tier for each, and controls that match the tier.
This guide is for CROs, CISOs, CIOs and Chief AI Officers who need a working structure rather than a principle list. It maps the NIST AI Risk Management Framework to agent controls, uses OWASP's guidance on excessive agency for permission limits, sets out the EU AI Act dates as the European Commission now states them, and gives a phased adoption sequence. For the threat side in depth, see our companion piece on agentic AI cybersecurity; this one stays at the level of the risk programme.
What is agentic AI risk management?
A conventional model produces a score or a draft that a person acts on. An agent plans, calls tools and changes records, so the risk moves from "is the output right?" to "what did it do, and could it have done more than it should?" Risk management therefore has to sit at the point of action, not only at model testing.
In practice the programme has four parts: know which agents exist, classify each by the harm it could cause, limit what it can reach, and keep evidence of what it decided. Our overview of agentic workflows explains how agents chain steps and tools, which is where these controls attach, and agentic AI security covers data protection and privacy risks.
Which risks do AI agents add?
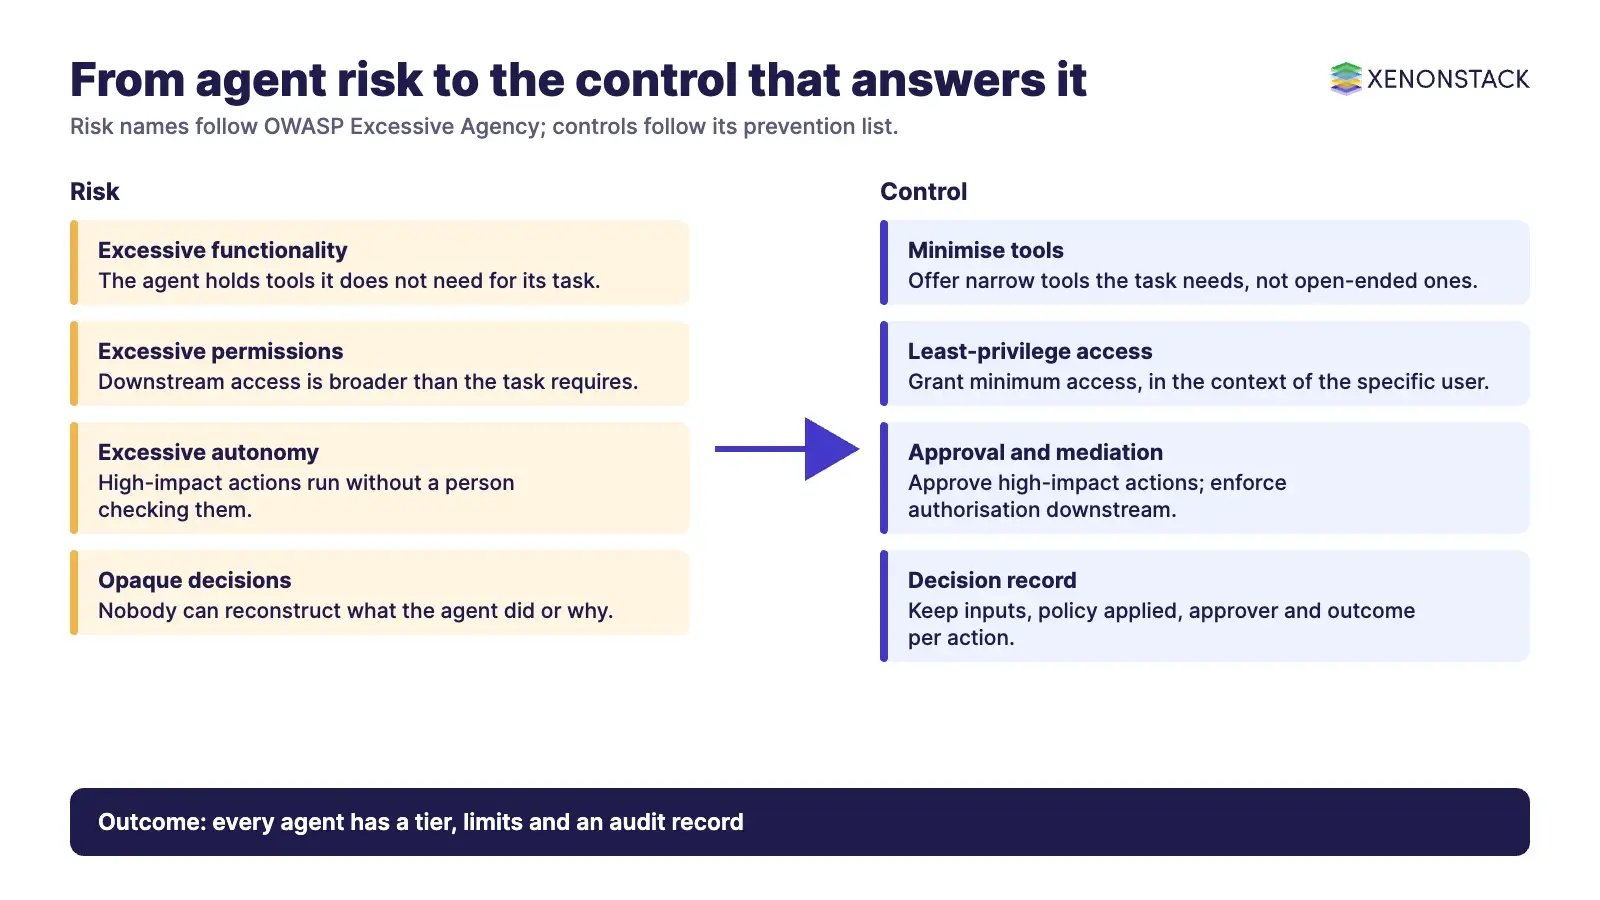
OWASP defines Excessive Agency as the vulnerability that enables damaging actions to be performed in response to unexpected, ambiguous or manipulated model output, whatever causes the malfunction. Hallucination and prompt injection are named as common triggers. OWASP says the root cause is typically one or more of excessive functionality, excessive permissions or excessive autonomy. That gives risk teams a usable vocabulary.
| Risk | How it arises | Control to apply |
|---|---|---|
| Excessive functionality | The agent holds tools it does not need for its task, such as send or delete rights on a mailbox it only reads. | Offer only the tools the task needs; prefer narrow tools over open-ended ones such as arbitrary shell execution. |
| Excessive permissions | Downstream access is broader than the task, for example write access to a database that only needs reads. | Grant the minimum level of access and run actions in the context of the specific user. |
| Excessive autonomy | High-impact actions run without a person checking them. | Require approval for high-impact actions and enforce authorisation in the downstream system rather than relying on the model to decide. |
| Opaque decisions | Nobody can reconstruct what the agent did or why. | Keep a record of each decision, its inputs and the policy applied, as NIST's accountable and transparent characteristic expects. |
The first three rows and their controls come from OWASP's Excessive Agency page. The fourth reflects NIST's list of trustworthy AI characteristics, which includes accountable and transparent, explainable and interpretable, and privacy-enhanced. Related threats such as prompt injection are covered in securing DeepSeek and AI models with Microsoft Security and in the cybersecurity companion above.
How does the NIST AI RMF map to agent controls?
NIST released AI RMF 1.0 (NIST AI 100-1) on 26 January 2023 and the Generative AI Profile on 26 July 2024. NIST's page says AI RMF 1.0 is being revised as part of the White House AI Action Plan, and the page does not mention agents. The mapping below is our reading of how its four functions apply to agent programmes, not NIST guidance.
| NIST function | What NIST says it does | What it means for agents |
|---|---|---|
| Govern | Cross-cutting; builds a risk management culture and the processes and structures behind the other functions. | Name an owner for each agent, set an autonomy policy, and decide who can approve higher tiers. |
| Map | Establishes context and frames risks, including intended uses and potential impacts. | Inventory agents, their tools, data and the decisions they influence. |
| Measure | Analyses, assesses, benchmarks and monitors AI risks. | Test behaviour against edge cases and adversarial inputs; monitor actions and exceptions in production. |
| Manage | Allocates resources to mapped and measured risks, with response, recovery and communication plans. | Define rollback, shutdown and escalation paths for agent incidents. |
How should you tier agents by risk?
Not every agent needs the same scrutiny. A practical way to classify them uses four factors: the agent's level of autonomy, its access privileges, the sensitivity of the data it touches, and the potential impact of a wrong action. The tiers below are a working pattern we use with enterprise teams, not a regulatory category.
| Tier | What the agent may do | Typical controls | When it fits |
|---|---|---|---|
| 1. Recommend | Read data and propose; a person acts. | Read-only access, logging. | Triage, research, drafting a risk note. |
| 2. Act with approval | Prepare an action; a named approver releases it. | Approval step, scoped credentials, decision trace. | Payments review, access changes, account holds. |
| 3. Act within limits | Execute low-impact actions inside policy. | Policy checks before execution, thresholds, sampling review. | Routine, reversible, well-measured tasks. |
| 4. Act autonomously | Execute broad actions with after-the-fact review. | Full monitoring, rollback, independent audit. | Rarely; only after traces prove accuracy at lower tiers. |
Where do agents help inside risk, fraud and compliance work?
Agents also work as part of the risk function. The table states the human checkpoint for each use case, because several of these actions (freezing an account, changing a control) are consequential.
| Use case | What the agent does | Where a person stays in the loop |
|---|---|---|
| Fraud review | Flags suspicious transaction patterns and assembles the case. | Approve account freezes or blocks. |
| Security monitoring | Correlates alerts and proposes containment. See self-healing SOC systems. | Approve isolation of production systems. |
| Regulatory change | Scans sources and drafts impact notes on internal controls. | Compliance owner decides which control changes to adopt. |
| Third-party risk | Collects vendor evidence and flags gaps. | Risk team decides on onboarding or exit. |
| ESG reporting | Gathers and reconciles data from multiple sources. | Reviewer signs off disclosures. |
Agents that operate screens and applications directly add their own exposure; see GUI agents for enterprise automation. Agents that take over rule-based processes are covered in agentic process automation.
What does the EU AI Act require, and when?
The European Commission's AI Act page lists the following dates. It says the AI Omnibus entered into force on 27 July 2026 and delayed the high-risk rules.
| Date | What applies |
|---|---|
| 1 August 2024 | AI Act enters into force. |
| 2 February 2025 | Prohibited practices and AI literacy obligations apply. |
| 2 August 2025 | Governance rules and obligations for general-purpose AI models apply. |
| 2 August 2026 | The Act becomes applicable, with some exceptions. |
| 2 December 2027 | High-risk rules for Annex III use cases, such as biometrics, education, employment, critical infrastructure and migration. |
| 2 August 2028 | High-risk rules for AI embedded in regulated products (Annex I). |
For high-risk systems the Commission lists risk management, data quality, logging, documentation, human oversight and robustness as obligations. Whether a given agent is high-risk depends on its use case, so classify it with legal counsel; an agent that scores credit or screens candidates is a different case from one that drafts internal summaries.
How do you adopt agent risk controls in sequence?
- Inventory. List every agent, including those built by employees or supplied by third parties, with an owner, tools, data and credentials.
- Tier. Score each agent on autonomy, privileges, data sensitivity and impact, and assign a tier.
- Limit. Remove unused tools, narrow permissions and enforce authorisation in downstream systems.
- Run in shadow mode. Let the agent propose beside people before it acts, and raise autonomy as decision traces show accuracy.
- Review. Sample decisions, track exceptions and review policy against practice on a fixed cycle.
- Prepare for incidents. Agree rollback, shutdown and escalation, and test them.
This is where governed context matters. ElixirData Context OS, according to its site, is a control layer for enterprise AI agents that gathers relevant business information, checks policy and permissions at two points before an action runs, and keeps a record of each decision. AgentGRC is described on its page as keeping agent actions within policy with an evidence trail for audit and risk teams, and as starting in shadow mode before autonomy is raised.
Video: ElixirData example of authorised, policy-checked fixes by an agent.
What review evidence do auditors and boards need?
The evidence that persuades a risk committee is a record per action: what the agent was asked, the context it used, the policy that applied, who approved, and what happened. The Decision Review Agent reviews records of what each AI agent decided and looks for inconsistent treatment of similar cases and gaps between practice and policy, according to its page. Whatever tool you use, review for those patterns on a schedule. For perimeter and identity design around agents, see zero trust security architecture, and for ethics and fairness standards see AI governance and ethical standards.
What are the trade-offs, and when should you not automate?
- Speed against control. Approval steps slow actions. Reserve them for high-impact or hard-to-reverse actions and let lower tiers run faster.
- Coverage against effort. An inventory is only as good as discovery. Agents built by employees or bought as SaaS features are the usual gap.
- Do not automate decisions with legal or significant effects on individuals until the use case is classified under the rules that apply to you, a human reviewer is named, and you can reproduce the decision from its record.
- Do not treat a framework as proof. NIST's AI RMF is voluntary guidance that is itself being revised; evidence from your own testing and monitoring is what shows control.
To map one decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is agentic AI risk management?
It is the practice of inventorying AI agents, classifying them by potential harm, limiting their tools and permissions, requiring approval for high-impact actions and keeping a record of every decision. It also covers using agents inside fraud, compliance and security work with people kept in the loop.
Which framework should we start with?
The NIST AI RMF 1.0 (26 January 2023) is a common starting point, with its Govern, Map, Measure and Manage functions. NIST's page says it is being revised and does not mention agents, so add agent-specific controls such as OWASP's guidance on excessive agency.
What is excessive agency?
OWASP defines it as the vulnerability that enables damaging actions to be performed in response to unexpected, ambiguous or manipulated model output. Its typical root causes are excessive functionality, excessive permissions and excessive autonomy.
When do the EU AI Act high-risk rules apply?
According to the European Commission's page, Annex III high-risk use cases apply from 2 December 2027 and AI embedded in regulated products (Annex I) from 2 August 2028, following the AI Omnibus that entered into force on 27 July 2026.
How do we decide how much autonomy an agent gets?
Score it on autonomy, access privileges, data sensitivity and potential impact, then start at the recommend or act-with-approval tier. Raise autonomy only when decision records show the agent is accurate and within policy.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE