

Key takeaway
- Responsible AI principles for enterprises, and how the EU AI Act, NIST AI RMF and ISO/IEC 42001 fit together, with the 2026 EU Omnibus dates explained.
Responsible AI is the set of principles, controls and records that let an enterprise show an AI system is fair, explainable, secure and under human oversight. In 2026 it is less a statement of values than a governance task, because three official references now shape it: the EU AI Act, the NIST AI Risk Management Framework and ISO/IEC 42001. This guide gives enterprise leaders the principles first, then the governance layer that makes them auditable.
The most useful change this year is on the calendar. Regulation (EU) 2026/1744, the Digital Omnibus on AI, entered into force on 27 July 2026 and moved the high-risk rules to 2 December 2027 for Annex III use cases and 2 August 2028 for AI embedded in regulated products. Plan to those dates, but do not wait for them: the principles below are what regulators and customers will ask you to evidence. For the wider debate, see our guides on Responsible AI in government and the ethics of artificial intelligence.
What are the principles of responsible AI?
Eight working principles guide how teams design, build and run systems that learn from data. Each one maps to a characteristic in the NIST AI RMF 1.0, which lists seven traits of trustworthy AI: valid and reliable, safe, secure and resilient, accountable and transparent, explainable and interpretable, privacy-enhanced, and fair with harmful bias managed. The mapping in the table is our own reading, not NIST text.
| Principle | What the team does | Closest NIST trait |
|---|---|---|
| Human augmentation | Assess the cost of a wrong prediction before automating a task, especially in finance, health and transport, and keep a human able to intervene. | Safe; accountable and transparent |
| Bias evaluation | Document bias in data and features, test inference results, and put mitigation procedures in place. Bias cannot be removed completely, so it must be measured and recorded. | Fair, with harmful bias managed |
| Explainability by justification | Choose features and models so that a prediction can be explained. Accept a small accuracy cost where transparency matters for the decision. | Explainable and interpretable |
| Reproducible operations | Version models, data and inputs so a model can be rolled back or an input replayed to debug a failure. | Valid and reliable; secure and resilient |
| Displacement strategy | Plan change management for the people and roles affected by automation, and document it. | Accountable and transparent |
| Practical accuracy | Define accuracy and cost metrics in the language of the business use case, not only on benchmark data. | Valid and reliable |
| Trust by privacy | Tell stakeholders what data is held and how it is protected, and build privacy in at every layer. | Privacy-enhanced |
| Data risk awareness | Treat autonomous decision systems as a new attack surface: set data handling rules, train staff and assess risks such as ML backdoors. | Secure and resilient |
When these are ignored the failures are visible. Models trained on skewed data can reproduce stereotypes, and an explanation is not optional where a decision affects a person: a clinician cannot tell a patient "the system said so". The practical test is simple. If you cannot explain an automated decision to the person it affects, the system is not ready for that decision. Our guide on real-life ethical issues of AI covers more examples.
How do the EU AI Act, NIST AI RMF and ISO/IEC 42001 fit together?
They do different jobs, so most enterprises use all three. The EU AI Act is law with deadlines and penalties. The NIST AI RMF is a voluntary risk framework. ISO/IEC 42001 is a certifiable management system standard. A common sequence is to use NIST to structure risk work, ISO/IEC 42001 to run it as a repeatable system, and the EU AI Act to decide which systems need the most evidence.
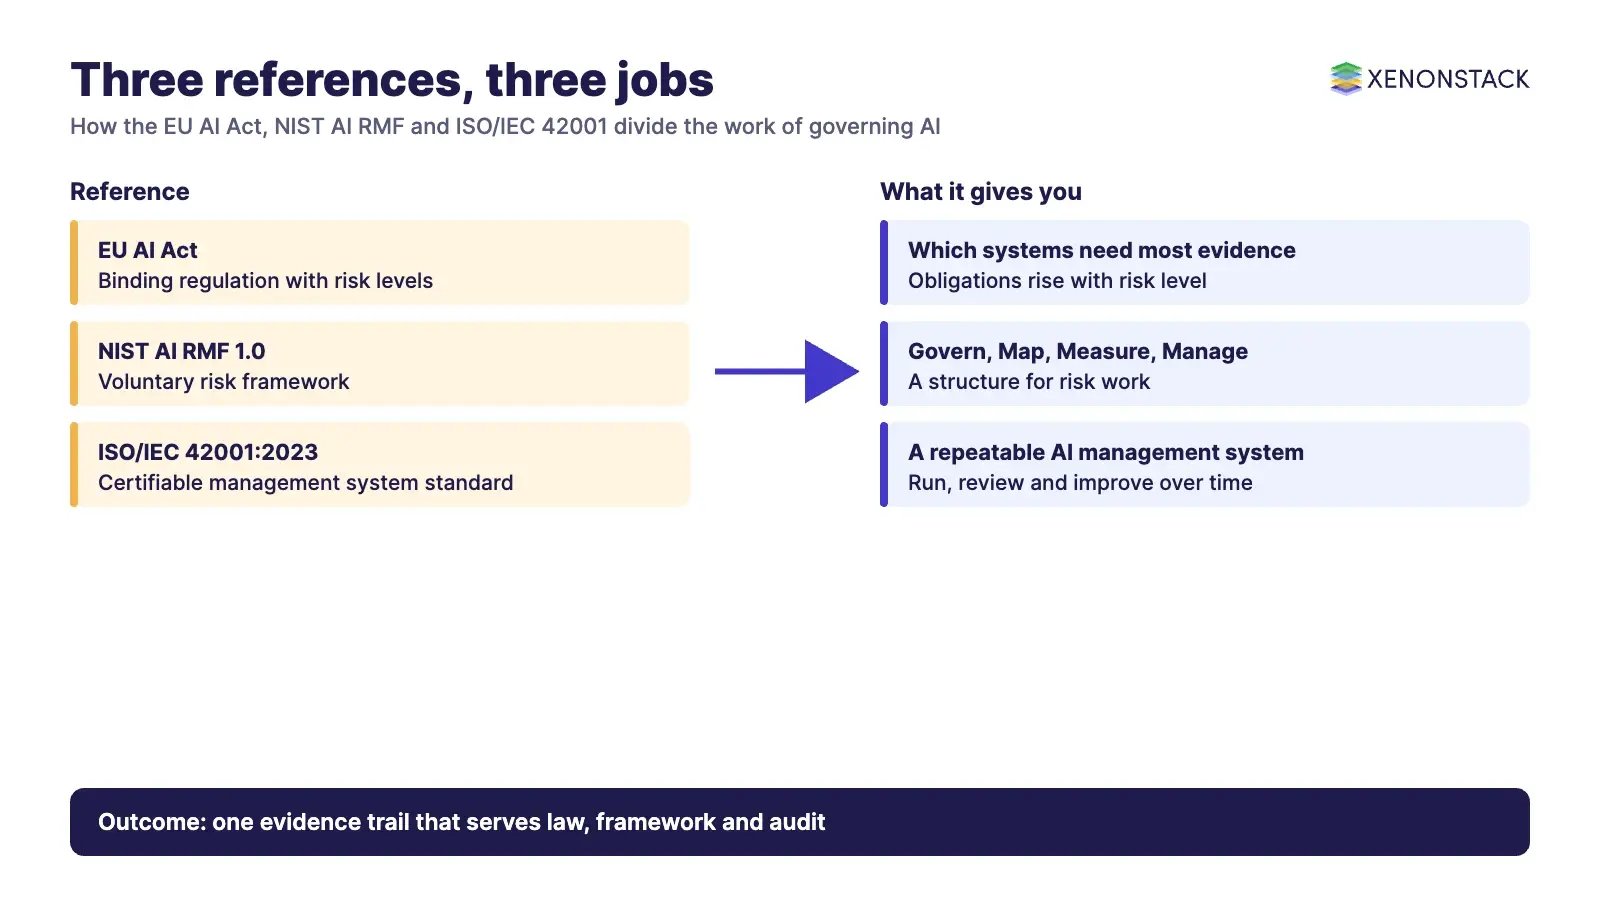
| Instrument | Type | What it gives you | Current status (official source) |
|---|---|---|---|
| EU AI Act, Regulation (EU) 2024/1689 | Binding regulation | Four risk levels (unacceptable, high, transparency and minimal) with obligations that rise with risk, such as risk management, data quality, logging, documentation and human oversight for high-risk systems. | In force since 1 August 2024. Amended by Regulation (EU) 2026/1744 from 27 July 2026. See European Commission AI Act page. |
| NIST AI RMF 1.0 | Voluntary framework | Four functions: Govern (risk culture and structures), Map (context and impacts), Measure (assess and track risk) and Manage (prioritise and respond to risk). | Released 26 January 2023. A Generative AI Profile followed on 26 July 2024. NIST says the framework is being revised. See NIST AI RMF page. |
| ISO/IEC 42001:2023 | Certifiable management system standard | Requirements for establishing, implementing, maintaining and continually improving an AI management system in organisations that provide or use AI. | Published 18 December 2023, edition 1, International Standard. See ISO standard page. |
What changed in the EU AI Act in 2026?
The Official Journal text of Regulation (EU) 2026/1744 amends the AI Act and Regulations (EU) 2018/1139 and (EU) 2023/1230. The dates below combine the Official Journal text with the Commission's AI Act page. Check them against your own legal advice, because delegated acts and guidelines are still to come.
| Date | What applies | Why it matters to you |
|---|---|---|
| 2 February 2025 | Prohibited practices and AI literacy obligations | Already in effect. Under the Omnibus, the literacy duty is framed as taking measures to support staff AI literacy. |
| 2 August 2025 | Governance rules and obligations for general-purpose AI models | Already in effect. Check which model providers you rely on. |
| 2 August 2026 | General application of the Act, with supervision by the AI Office and national authorities | Already in effect. Transparency rules start to apply. |
| 2 December 2026 | New prohibitions on non-consensual sexually explicit content and child sexual abuse material, plus the date by which generative AI systems already on the market before 2 August 2026 must meet the Article 50(2) marking duty | Review generative AI products for marking and for misuse controls. |
| 2 December 2027 | High-risk rules for Annex III use cases (for example employment, education, biometrics) | Moved later by the Omnibus. Use the extra time for risk management and logging, not for delay. |
| 2 August 2028 | High-risk rules for AI embedded in regulated products (Annex I) | Align with product safety conformity work. |
What are the main responsible AI challenges for enterprises?
Six challenges recur in enterprise programmes. Each one needs a named owner rather than a general policy.
Explainability and transparency: Opaque systems cannot justify results, which weakens trust and makes review harder.
Safety: Autonomous systems such as vehicles and robots can harm people, so safety cases must precede deployment.
Automation and human control: As people offload tasks, their skill to check the system fades. Design the point where a human can still intervene.
Bias and discrimination: Systems reflect their training data, including human and cognitive bias and gaps in coverage.
Accountability and regulation: Expectations of liability rise with use. Decide who answers for a system's outputs before it goes live.
Security and privacy: Systems that learn from large data sets raise the stakes for data protection and for protecting models from attack.
Business leaders often say responsible AI is incompatible with business, because the principles are agreed but the implementation is unclear, and stakeholders find a new discipline hard to fund. The answer is to treat it as operating practice with owners, metrics and evidence. See our guide to transparent AI challenges and solutions for the explainability side.
How should an enterprise deploy responsible AI?
Responsible AI at scale calls for organisational change, not only model tooling. The sequence below works as a starting point.
Define responsible AI for your business: Board members, executives and senior managers agree what appropriate use means, what value AI should add and which risks must be mitigated, such as brand reputation and unfair customer outcomes.
Develop organisational skills: Train staff and consider an internal centre of AI excellence to pilot adoption and training.
Promote cross-functional collaboration: Risks are contextual, so include product, privacy, risk and compliance views when prioritising them. Manage risk while the system operates, because learning systems behave unexpectedly.
Use broader performance metrics: Average benchmark performance is a narrow test. Monitor behaviour against your own responsible AI standards on a regular basis.
Set clear lines of accountability: Add a vetting step to pre-launch assessment, map team responsibilities, define an escalation route for disagreements between product and privacy leads, and recognise staff who report problematic use cases.
What do best practices look like in operation?
Design for people first and disclose appropriately to users.
Test before deployment across a diverse set of users and use cases.
Select metrics that reflect the context and business goals, and include end-user feedback.
Validate data on a schedule for missing or inappropriate values, bias, training skew and drift.
Use unit, integration and statistical tests, then track and log deployed model performance.
State limitations and known flaws to stakeholders.
For agentic AI, the same controls need to run at the point of action. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
Video: AgentGRC, AI agent governance, risk and compliance on the Elixir Platform.
Does responsible AI slow innovation, and when is it not enough?
It can slow a release, but it does not have to slow innovation. Systems that work against human rights, ethics or the rule of law lose their users, and rework after launch costs more than review before it. Building relationships with partners and stakeholders takes time, and it leads to human-centric AI that people keep using.
There are limits. Principles do not replace a risk assessment for a specific system, a certification does not prove a given model is fair, and a framework does not decide who is accountable. Treat NIST and ISO/IEC 42001 as ways to organise evidence, and ask legal counsel which EU AI Act category each system falls into.
Which tools support responsible AI practice?
No single tool covers responsible AI. The categories below cover the technical checks that the principles call for.
| Technique or toolkit | What it checks | Principle it supports |
|---|---|---|
| What-If Tool (TensorFlow ecosystem) | Model behaviour across parameter ranges, and the effect of changing individual data points, with fairness views | Bias evaluation |
| AI Fairness 360 (LF AI) | Open-source toolkit to examine and mitigate bias | Bias evaluation |
| AI Explainability 360 (LF AI) | Open-source toolkit for model interpretability | Explainability by justification |
| Adversarial Robustness Toolbox (LF AI) | Evaluates and defends models against adversarial attacks | Data risk awareness |
| SHAP | Game-theoretic explanation of any model output using Shapley values | Explainability by justification |
| LIME | Local, model-agnostic explanation of individual predictions | Explainability by justification |
| Counterfactual explanations | The smallest change to inputs that would change a prediction, such as a declined credit application becoming approved | Explainability by justification |
What comes next for responsible AI?
Two moves are worth tracking. NIST says the AI RMF 1.0 is being revised, and on 7 April 2026 it released a concept note for a profile on trustworthy AI in critical infrastructure. In the EU, the Commission guidelines on high-risk compliance are due by 1 August 2027, per the Official Journal text. Organisations that keep records of decisions, data and model versions now will find each new requirement easier to meet.
To map one decision your AI systems make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What are the principles of responsible AI?
Eight working principles: human augmentation, bias evaluation, explainability by justification, reproducible operations, displacement strategy, practical accuracy, trust by privacy and data risk awareness. NIST AI RMF 1.0 lists seven traits of trustworthy AI, including safe, secure and resilient, explainable and interpretable, privacy-enhanced, and fair with harmful bias managed.
When do the EU AI Act high-risk rules apply after the Digital Omnibus?
Regulation (EU) 2026/1744 entered into force on 27 July 2026. High-risk rules for Annex III use cases apply from 2 December 2027, and for AI embedded in regulated products under Annex I from 2 August 2028.
What is the NIST AI RMF?
A voluntary framework from NIST that helps organisations manage AI risk and build trustworthiness into design, development, use and evaluation. AI RMF 1.0 was released on 26 January 2023 and has four functions: Govern, Map, Measure and Manage. NIST says it is being revised.
What is ISO/IEC 42001?
An International Standard published on 18 December 2023 that sets requirements for establishing, implementing, maintaining and continually improving an AI management system in organisations that provide or use AI-based products or services.
Does responsible AI slow down innovation?
It can add review time before release, but it reduces rework and loss of trust after launch. Treat it as operating practice with owners, metrics and evidence.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE


