Key takeaway
- White box testing checks a program's internal structure. Learn the steps, coverage types, tools such as JUnit and JaCoCo, benefits, limits and AI agents.
White box testing is a way of testing software by looking at its internal structure: the code, the branches and the paths a program can take. The ISTQB glossary defines it as "testing based on an analysis of the internal structure of the component or system". Testers and developers use that knowledge to design tests that run every statement, decision and path they care about.
For engineering leaders the practical question is where it earns its cost. It is strongest at unit and integration level, where it finds logic errors early and shows which code no test has ever run. It does not replace testing against requirements. See our guides to unit testing and system testing for the levels on either side.
What is white box testing?
White box testing derives test cases from the program's logic instead of from its external behaviour alone. The tester can see the code, so tests can target a specific condition, loop or data flow. It is often called structural testing, and the original names for it include open box, logic-driven and path-driven testing. White box security testing applies the same code-level view to security weaknesses.
How is white box testing done, step by step?
The usual sequence for a component under test is:
- Identify the features, components and programs to be tested.
- Read the code and draw a flow graph of its statements, decisions and loops.
- List the paths through the flow graph that matter for the risk you are covering.
- Write test cases with inputs and expected outputs for each chosen path.
- Run the tests, measure coverage, review the code that no test reached, and repeat.
Which coverage criteria does white box testing use?
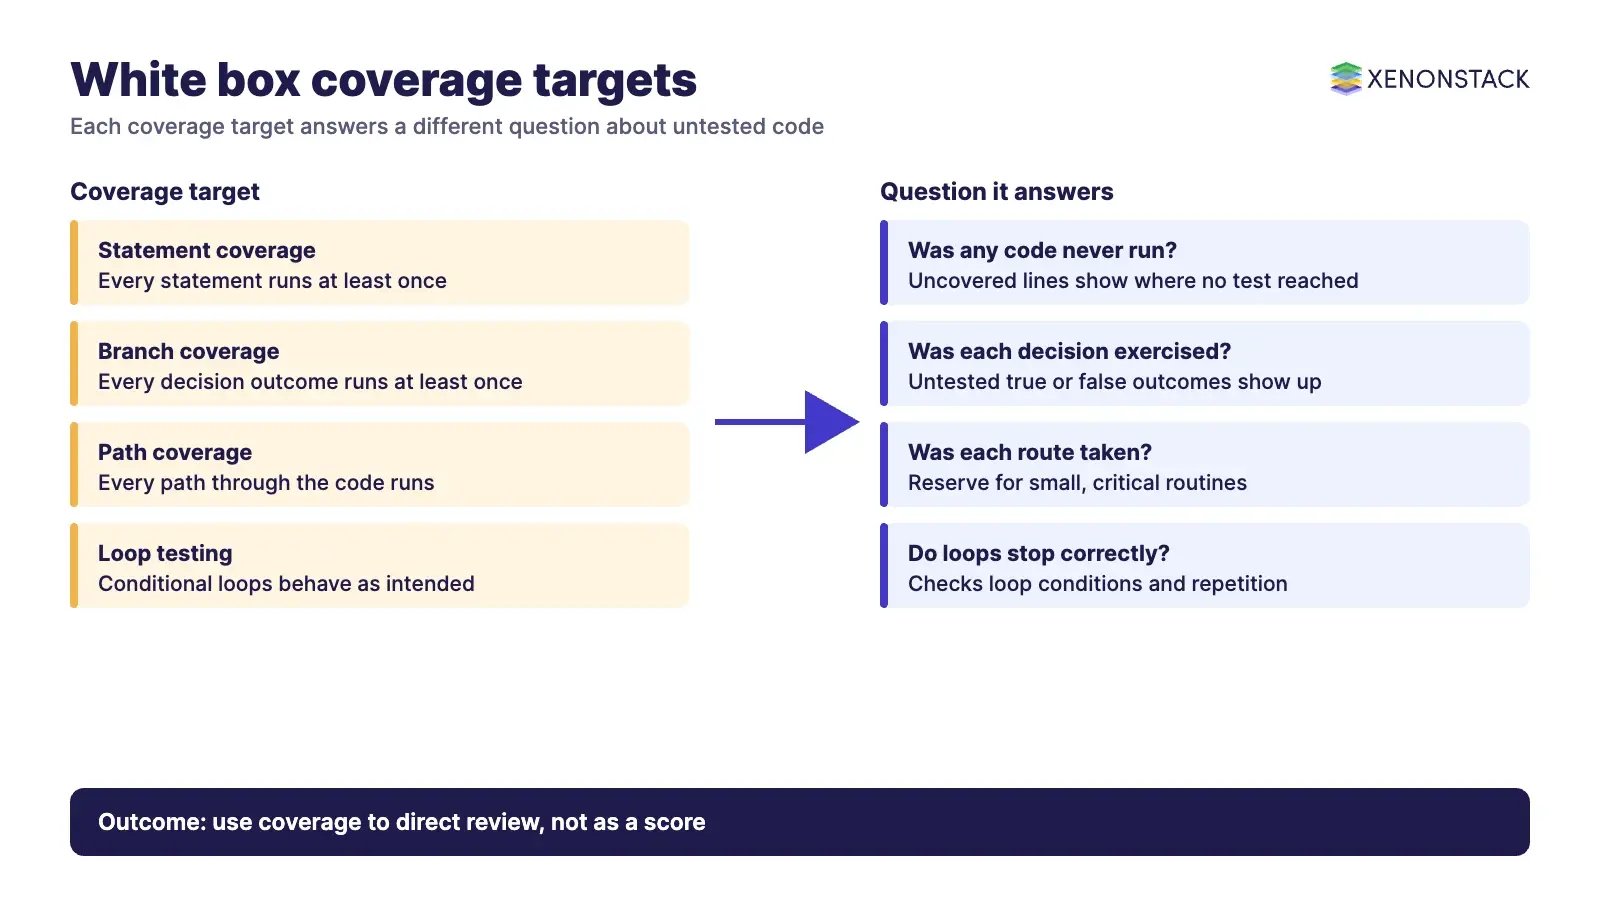
Coverage criteria say how much of the structure your tests must exercise. Pick the one that fits the risk of the code, and read the number as a pointer to untested code, not as a score.
| Criterion | What it requires | Usual formula | When it fits |
|---|---|---|---|
| Statement coverage | Every statement runs at least once | Statements exercised / total statements x 100 | A baseline for any code |
| Branch coverage | Every outcome of every decision runs at least once | Decision outcomes tested / total outcomes x 100 | Business rules, validation, error handling |
| Path coverage | Every path through the code runs | Paths exercised / total paths x 100 | Small, critical routines only, because path counts grow quickly with loops and decisions |
The tools define these counters precisely. According to its docs, JaCoCo counts the branches in if and switch statements and treats cyclomatic complexity as the minimum number of paths that can, in linear combination, generate all possible paths through a method. Coverage.py measures line (statement) coverage by default and can also measure branch coverage.
Martin Fowler's note on test coverage gives the caution that matters for management: coverage is useful for finding untested code, a numeric target invites low-quality tests, and a figure near 100% can be a warning sign. Our test coverage guide covers how coverage differs from test coverage.
How does white box testing differ from black box testing?
| Question | White box | Black box |
|---|---|---|
| What the tester uses | Source code and design | Requirements and observable behaviour |
| Typical finders | Logic, data flow and conditional errors, unreachable code | Missing or wrong behaviour, usability and integration gaps |
| Typical levels | Unit and integration, also system level with code access | System and acceptance |
| Main risk | Tests mirror the code, so a wrong assumption is tested as correct | Untested internal paths stay hidden |
Most teams use both. White box tests keep the code honest; black box tests keep the product honest. The integration testing guide shows the middle level where the two approaches meet.
At which levels does white box testing apply?
- Unit level: small units are checked individually against their logic. This is where white box testing is cheapest and fastest. See What Is Unit Testing? and test-driven development.
- Integration level: tests follow data and control flow across modules and interfaces. See integration testing.
- System level: tests are usually black box, but code-level checks still help on critical paths. See system testing.
Because it does not wait for a user interface, white box testing can start as soon as the code compiles, which fits the shift-left approach. In a CI/CD pipeline the tests and the coverage report run on every build.
Which tools support white box testing?
| Tool | Role | Status according to its site |
|---|---|---|
| JUnit 5 | Test framework for developer-side testing on the JVM | Targets Java 8 and newer releases |
| JaCoCo | Free code coverage library for Java | Latest release listed: 0.8.16, dated 2026/10/24 |
| Coverage.py | Reports which parts of Python code ran, with optional branch coverage | Latest release shown: 7.17.3 |
Confirm versions on each project page before you standardise on one. A framework runs the tests and a coverage tool reports what they reached, so you normally need one of each.
What are the benefits and limits of white box testing?
| Benefit | Limit or trade-off |
|---|---|
| Finds hidden logic, data flow and conditional errors that behaviour-only tests can miss | Needs testers who can read the code |
| Shows exactly which code no test has run | Coverage says the code ran, not that the result was checked |
| Starts early, before a user interface exists | Tests can break when code is refactored |
| Helps tidy loops and remove unreachable code | Cannot find requirements that were never built |
Do not rely on white box testing alone when the risk sits in requirements, integration with other systems or user experience. For security work, NIST SP 800-218 (the Secure Software Development Framework, version 1.1, February 2022) describes high-level secure development practices; confirm on the official NIST page which practices cover code review and testing.
Where do AI agents fit in white box testing?
The same idea applies to AI agents: you can test the visible outputs, or you can inspect the steps, tool calls and policies behind them. Unit-level checks on prompts, tools and routing logic are white box tests of an agent. Teams that build agents on ElixirClaw, an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control, can pair those checks with continuous testing of agent outputs. According to its site, AgentQA offers automated quality assurance for AI. Our guide to agentic software testing explains the controls.
What is a sensible adoption sequence?
- Start with statement coverage on new code and review the uncovered lines in each pull request.
- Add branch coverage for business rules, validation and error handling.
- Reserve path-level analysis for small, critical routines.
- Run tests and the coverage report in the build, and treat the number as a prompt for review.
To map one decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about white box testing
What is white box testing?
It is testing based on an analysis of the internal structure of a component or system, according to the ISTQB glossary. Test cases are derived from the code, its branches and its paths.
What is the difference between white box and black box testing?
White box tests use the code and design to choose test cases. Black box tests use requirements and observable behaviour. Most teams use both.
What are the main coverage types?
Statement coverage runs every statement, branch coverage runs every decision outcome, and path coverage runs every path through the code. Path coverage grows quickly, so it is kept for small, critical routines.
Which tools help with white box testing?
JUnit 5 runs Java tests, JaCoCo reports Java coverage, and Coverage.py reports line and branch coverage for Python, according to their own sites.
Is 100% code coverage the goal?
No. Martin Fowler notes that coverage is useful for finding untested code, that numeric targets invite weak tests and that a figure near 100% can be a warning sign. Use it to direct review.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE