Key takeaway
- AI TRiSM explained for enterprise leaders: trust, risk and security controls, NIST AI RMF and EU AI Act timelines, an adoption sequence and FAQs.
What is AI TRiSM and why does it matter to enterprise leaders?
AI TRiSM is AI trust, risk and security management. Gartner describes it as a programme that builds governance into AI from the start, so that AI systems stay compliant, fair, reliable and protective of data privacy. For a CIO, CISO or Chief AI Officer it is the operating discipline that decides whether a model or agent may go to production, and who answers when it misbehaves.
Gartner projects that by 2026, organisations that operationalise AI transparency, trust and security will see a 50% improvement in adoption, business goals and user acceptance (Gartner, September 2023). Treat that as a vendor forecast, not a measured result. This guide is the TRiSM view; for the wider principles of fairness, accountability and ethics, read our responsible AI principles guide.
What are the three parts of AI TRiSM?
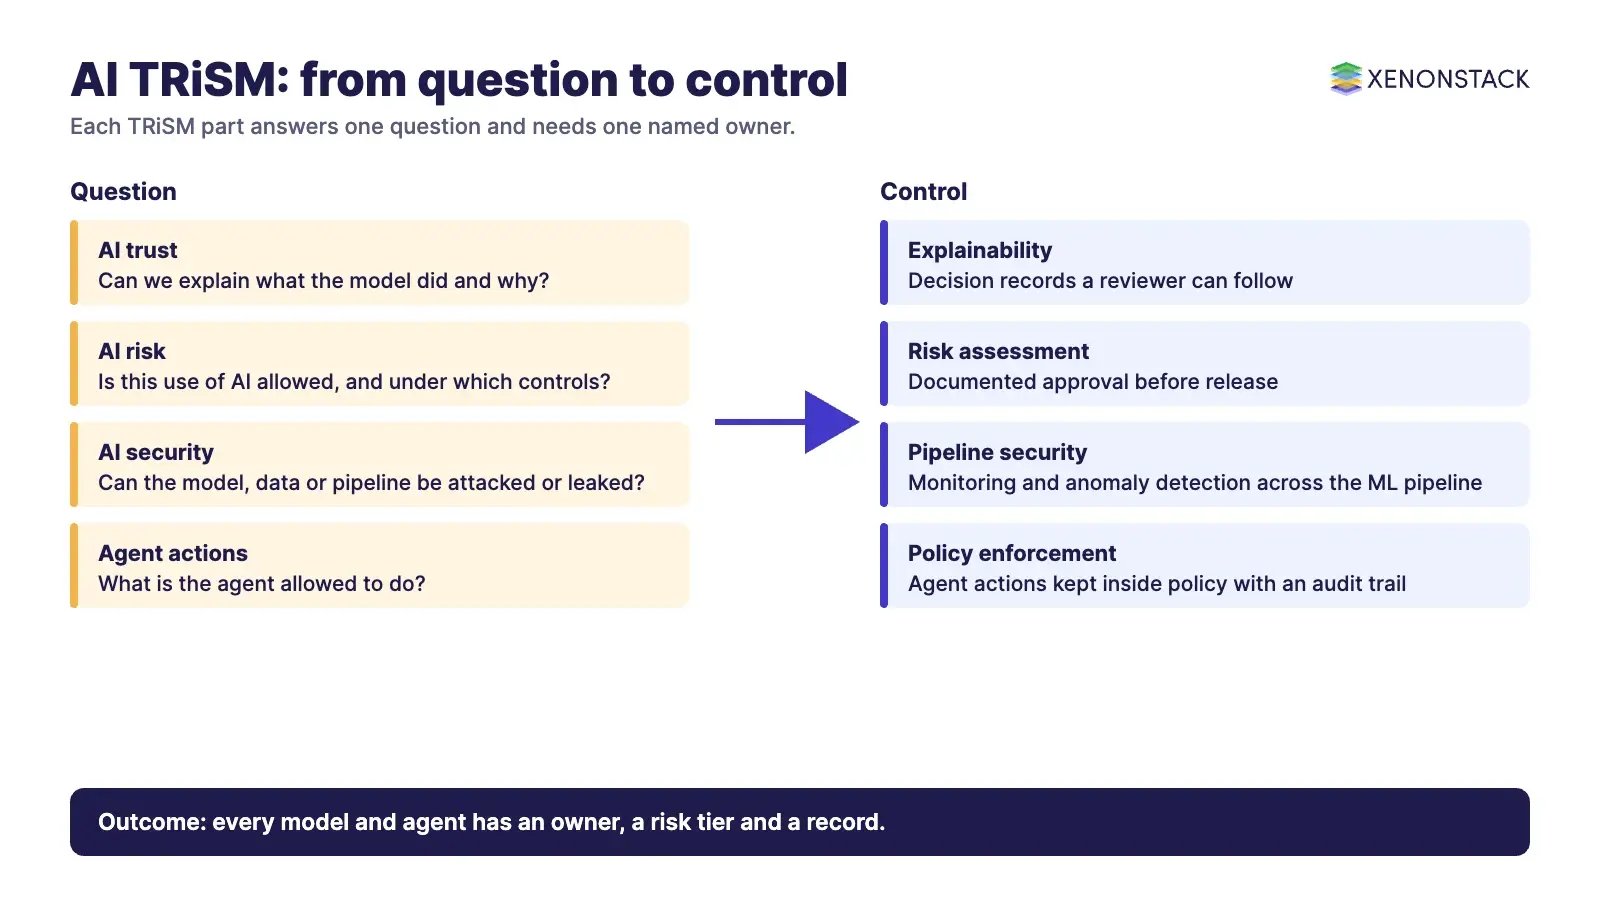
Trust, risk and security are three different questions, and each needs a named owner.
| Part | Question it answers | Typical owner | What good looks like |
|---|---|---|---|
| AI trust | Can we explain what the model did and why? | Chief AI Officer, model owners | Explanations and decision records a reviewer can follow |
| AI risk | Is this use of AI allowed, and under which controls? | Risk, compliance and legal | Documented risk assessment and approval before release |
| AI security management | Can the model, its data and its pipeline be attacked or leaked? | CISO, platform security | Controls and monitoring across the whole ML pipeline |
Our earlier view of these parts still holds: trust is about transparency and explainability, risk is about strict governance of enterprise AI and a record of every development and release stage, and security is about protecting each stage of the ML pipeline, spotting anomalies and scanning for vulnerabilities.
How do the capabilities of an AI TRiSM programme fit together?
The capabilities below are our working view of what a TRiSM programme has to cover. They are not an official Gartner list.
| Capability | What it covers | When it matters most |
|---|---|---|
| Explainability | Showing how a model reached an output, and whether it met its target | Regulated decisions, customer-facing outputs |
| ModelOps | Managing the lifecycle of every AI model, including analytics, knowledge graph and decision models | Many models in production, frequent releases |
| Data anomaly detection | Finding data issues that distort model behaviour | Pipelines fed by many sources |
| Adversarial attack resistance | Detecting and responding to attacks that use data to disrupt or alter model behaviour | Public-facing models and agents |
| Data protection | Keeping training and inference data private and compliant, for example with GDPR | Personal or confidential data |
What has changed since 2023?
Agents now take actions, not just produce predictions. The OWASP Gen AI Security Project lists risks such as prompt injection, sensitive information disclosure, data and model poisoning, excessive agency and unbounded consumption in its 2025 Top 10 for LLM applications (source: genai.owasp.org). A TRiSM programme therefore has to cover what an agent is allowed to do, not only what a model predicts.
Which standards and regulations should AI TRiSM map to?
| Source | What it is | Current status (as read 11 Nov 2026) |
|---|---|---|
| NIST AI Risk Management Framework | Voluntary US framework for managing AI risk; four functions: Govern, Map, Measure, Manage | AI RMF 1.0 released 26 January 2023; Generative AI Profile (NIST-AI-600-1) released 26 July 2024; NIST says AI RMF 1.0 is being revised as part of the White House AI Action Plan |
| EU AI Act | Binding EU regulation on AI systems | In force since 1 August 2024; prohibitions and AI literacy from 2 February 2025; general-purpose AI obligations from 2 August 2025; general application from 2 August 2026 |
| EU AI Act, high-risk rules | Obligations for high-risk systems | Extended by the AI Omnibus (in force 27 July 2026): Annex III use cases from 2 December 2027, and AI embedded in regulated products from 2 August 2028 |
| OWASP Top 10 for LLM Applications | Security risk list for LLM and generative AI applications | 2025 edition is current |
Use these as the control catalogue for your TRiSM programme. Confirm dates with your legal team before planning around them, because the high-risk timetable has already moved once.
Why build AI TRiSM into AI models before release?
Does it reduce risk earlier?
Yes. Governance added at design time costs less than a control retrofitted after an incident. Risk assessment, bias checks and data protection decisions are recorded before the model ships.
Does it make AI easier to trust?
Transparent decisions and documented behaviour give users, auditors and regulators something to check. Trust follows evidence, not assurances.
Does it help with compliance and security?
A single set of controls can be mapped to several regimes at once. Security controls guard the model, its data and its pipeline, and respect privacy rights.
How do you implement AI TRiSM in your organisation?
Start small and sequence the work.
| Step | What to do | Output |
|---|---|---|
| 1. Inventory | List every model, agent and AI vendor in use, with an owner for each | AI register |
| 2. Classify | Rate each use by impact and data sensitivity, and map it to NIST AI RMF and the EU AI Act | Risk tiers |
| 3. Document | Record data sources, intended use, limits and release approvals | Model documentation |
| 4. Test | Check for bias, failure modes and adversarial weaknesses before release | Test evidence |
| 5. Monitor | Watch drift, anomalies and policy breaches in production, and keep an incident path | Alerts and decision records |
| 6. Review | Re-assess on every material change and on a fixed cycle | Updated register |
For agents, tools like ElixirData Context OS keep governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
Where does transparency fit?
Consumers and staff question AI because decisions happen out of sight. Showing the decision structure builds trust, as the walkthrough below shows.
Video: how decision traces build trust in AI agents (ElixirData).
What challenges slow AI adoption, and when is TRiSM not enough?
| Challenge | Why it happens | Response |
|---|---|---|
| Bias | Skewed data or unexamined assumptions | Bias checks before release and on a schedule |
| Lack of human participation | Automation without review points | Define where a person must approve or override |
| Insufficient understanding | Teams deploy models they cannot explain | Training and model documentation |
| Unexpected behaviour | Drift, new inputs or attacks | Production monitoring and an incident path |
TRiSM does not replace good engineering or ethics policy. It will not fix a model that is wrong for the job, and a heavy process for a low-risk internal tool is waste. Match the control to the risk tier. Related reading: ethics of artificial intelligence, compliance as code, AIOps for IT operations and the future of generative AI for enterprises.
For continuous checking against policy, the Compliance Agent watches operations against regulatory, contractual and internal policy requirements and keeps findings with their decision lineage.
To map one AI decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about AI TRiSM
What does AI TRiSM stand for?
AI trust, risk and security management. Gartner describes it as a programme that adds governance early so AI stays compliant, fair, reliable and protective of data privacy.
What does Gartner predict for AI TRiSM?
Gartner projects that by 2026, organisations that operationalise AI transparency, trust and security will see a 50% improvement in adoption, business goals and user acceptance. It is a forecast, not a measured result.
Is AI TRiSM the same as the NIST AI RMF?
No. TRiSM is a Gartner-described programme. The NIST AI RMF is a voluntary framework with four functions: Govern, Map, Measure and Manage. Many organisations use NIST as the control catalogue inside a TRiSM programme.
When do the EU AI Act high-risk rules apply?
After the AI Omnibus, which entered into force on 27 July 2026, Annex III high-risk use cases apply from 2 December 2027 and AI embedded in regulated products from 2 August 2028.
Who should own AI TRiSM?
A named executive, often the Chief AI Officer, with risk, legal and the CISO each owning their part: risk and approval, regulation, and security.
Does TRiSM cover AI agents?
It should. Agents act, so controls must cover what an agent may do, for example excessive agency and prompt injection, both listed in the OWASP 2025 Top 10 for LLM applications.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE