Key takeaway
- Govern and secure SAP Databricks: Unity Catalog controls, ABAC tags, audit logs, GDPR and HIPAA evidence, and AI agent oversight, in an adoption sequence.
SAP Databricks is the managed Databricks service included in SAP Business Data Cloud, and governance and security for it mostly sit in one place: Unity Catalog. According to the Databricks launch post, SAP Databricks became generally available on 30 April 2025. For a CISO or CDO the practical question is which controls apply to SAP data once it is shared into that environment, and who owns each one.
This guide answers that question in order: where the control points are, what the SAP Databricks governance documentation says Unity Catalog manages, how to map risks to controls, how AI agents change the picture, and what to adopt first. It builds on our guides to SAP Business Data Cloud with Databricks and data governance for business-ready data, and the Databricks service page.
Where do governance and security sit in SAP Databricks?
The Databricks launch post describes SAP Databricks as "a fully managed version of Databricks included natively as a service in SAP Business Data Cloud". It says data products in SAP Business Data Cloud reach SAP Databricks through Delta Sharing, with "secure, bidirectional data access without physically copying data between systems". The SAP Databricks documentation describes receiving shares over an open sharing protocol it calls OpenSharing. The SAP Business Data Cloud page says SAP Business Data Cloud "unifies and governs all SAP data" and keeps its original business context and semantics.
In practice this gives three control points, each with a different owner.
| Control point | What it governs | Typical owner | Source |
|---|---|---|---|
| SAP Business Data Cloud data products and shares | Which SAP data is published and shared into SAP Databricks | SAP data and platform team | SAP and Databricks pages above |
| Unity Catalog in SAP Databricks | Access to catalogs, schemas, tables, volumes and models; lineage; audit; profiling | Data platform and governance team | SAP Databricks governance documentation |
| Identity, agents and applications on top | Who or what calls the data, and what it may do with the answer | Security, risk and AI platform team | NIST SP 800-207, OWASP LLM Top 10 |
A gap at any of the three undermines the others. For example, fine-grained policy in Unity Catalog does not decide what an AI agent does with a result. That is why the rest of this guide treats data policy and agent policy as separate layers. Our guide to an open and unified metadata platform covers the metadata side in more depth.
What does Unity Catalog manage in SAP Databricks?
The SAP Databricks governance documentation lists the following. Where the page gives no detail we say so rather than fill the gap.
| Capability | What the documentation says | What it means for you |
|---|---|---|
| Centralised access control | Administrators manage permissions for teams and individuals across workspaces; privileges are managed with access control lists through UIs or SQL | One place to grant and review access, instead of per-workspace rules |
| Securable objects | Schemas, tables, volumes (non-tabular data), registered ML models, external locations and credentials | Files and models need the same review as tables |
| Lineage | Captured at runtime down to column level, including notebooks, jobs and dashboards | Impact analysis before a change; evidence for reviewers |
| Auditing | The page names auditing; the audit log system table (system.access.audit) records user identity, service, action, request parameters and response | Feeds investigation and access reviews; retention is not stated on the page |
| Data profiling | Monitors statistical properties and quality of tables | Early warning on quality drift in governed tables |
| External locations | Administrators can make external locations read-only to prevent data exfiltration | A simple guardrail for data leaving through storage |
Sources: SAP Databricks governance documentation and audit log system table documentation, read 12 November 2026. Details of each privilege are on separate pages that we did not read, so confirm them against your own metastore before you design roles.
Which newer controls matter for SAP data?
Two changes in the April 2026 release notes matter most. On 2 April 2026 governed tags became generally available, letting administrators define a controlled set of tags for access control, data classification and cost tracking. On 6 April 2026, when you mount an SAP Business Data Cloud share to a catalog, SAP semantic metadata (table and column comments, keys and governance tags) syncs into Unity Catalog, and the SAP governance tags can be used in ABAC policies.
According to the Unity Catalog ABAC documentation, attribute-based access control evaluates attributes on securable objects. Policies attach at catalog, schema or table level and take effect automatically on anything carrying the targeted governed tags. It supports row filter policies, column mask policies, and GRANT and DENY policies. At the time we read it, metastore-level policies, policies on views and DENY policies were marked Beta, so check status before relying on them for regulated data.
How do you map risks to controls?
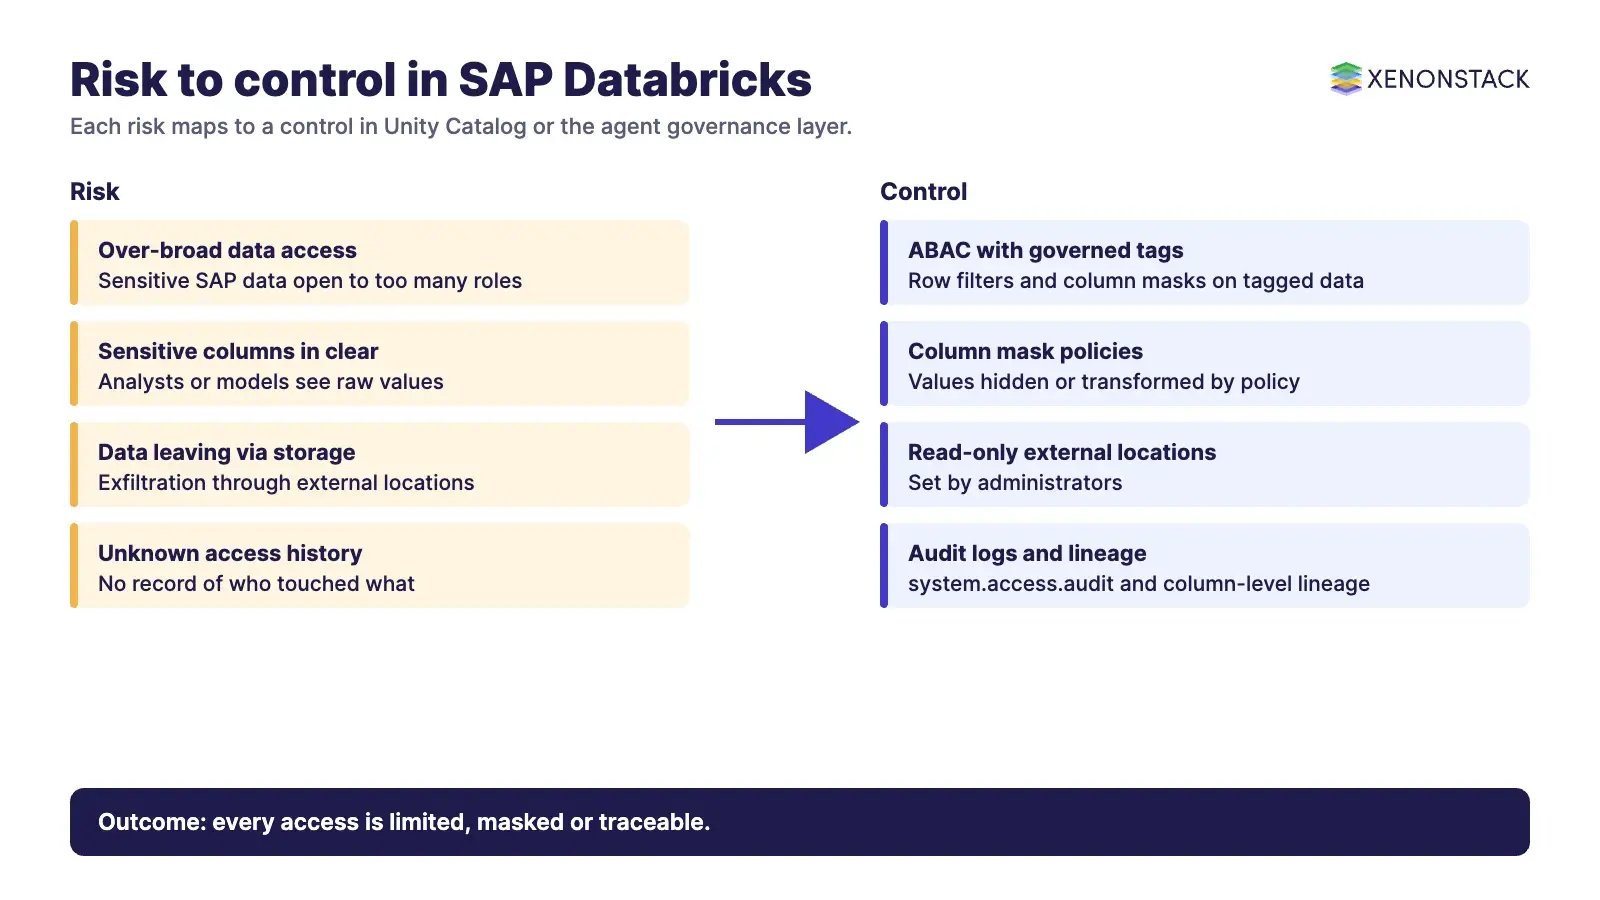
Start from the risk, not the feature. The mapping below is a design aid. The control column names Unity Catalog features from the documentation above; the risk column is editorial.
| Risk | Control to apply | Where it lives |
|---|---|---|
| Over-broad access to sensitive SAP data | Least-privilege grants; ABAC with governed tags and SAP governance tags; row filters and column masks | Unity Catalog |
| Sensitive columns reaching analysts or models in clear | Column mask policies on tagged columns | Unity Catalog (ABAC) |
| Data leaving through storage | Read-only external locations | Unity Catalog |
| Not knowing who touched what | Audit log system table and column-level lineage | Unity Catalog and system tables |
| Implicit trust in a user, device or agent | Authenticate and authorise before each session; no trust from network location | Identity layer; see NIST SP 800-207 |
| An agent doing more than intended | Scoped agent identity, approvals and decision traces outside the data platform | Agent governance layer |
The zero trust row follows NIST SP 800-207, which says zero trust "assumes there is no implicit trust granted to assets or user accounts" and that authentication and authorisation happen before a session with a resource begins. Our guides to zero trust security architecture and SOC systems cover how this connects to monitoring and response.
Which regulations apply, and what does the platform do about them?
No platform makes an organisation compliant on its own. The platform supplies controls; your policies, evidence and processes decide compliance. Two regimes come up most often with SAP data.
| Regime | What the official source says | What to evidence |
|---|---|---|
| GDPR | See the GDPR text on EUR-Lex; we cite it as a link only and have not summarised articles here | Access limits, lineage and audit records for personal data |
| HIPAA | The HHS HIPAA Security Rule page says the Security Rule sets standards for electronic protected health information and requires fitting administrative, physical and technical protections | Who can reach ePHI, and a record of access |
Neither source names SAP Databricks, so confirm scope with your counsel and your SAP and Databricks contracts.
What changes when AI agents query governed SAP data?
Agents add a decision layer above the data platform. The OWASP Top 10 for LLM Applications (2025) lists risks that apply here, including Sensitive Information Disclosure (LLM02) and Excessive Agency (LLM06). Unity Catalog can limit what an identity reads, but it does not record why an agent acted or whether a person approved it.
Teams therefore add a separate layer. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. For the security side see cybersecurity challenges in agentic AI, GUI agents and securing AI models with Microsoft Security.
What is a sensible adoption sequence?
| Step | Action | Done when |
|---|---|---|
| 1 | Inventory which SAP data products are shared into SAP Databricks and who owns each | Every shared product has a named owner |
| 2 | Classify sensitive data with governed tags, using SAP governance tags where they sync | Sensitive columns carry tags |
| 3 | Replace ad hoc grants with group-based least-privilege grants | No direct user grants on sensitive tables |
| 4 | Add column mask and row filter policies on tagged data | Policy tests pass for each role |
| 5 | Route audit logs and lineage into a regular access review | A review has run at least once |
| 6 | Put agents behind scoped identities, approvals and decision traces | Each agent action can be traced to a policy |
Our guide to Data DevOps covers how to test and deploy such policy changes safely.
Video: data governance in the enterprise
XenonStack video: data governance and enterprise information management.
What are the trade-offs, and when should you hold back?
Beta features. Metastore-level ABAC, ABAC on views and DENY policies were marked Beta when read. Use them in non-regulated scopes first.
Two catalogs of truth. SAP-side authorisations and Unity Catalog grants are separate mechanisms. Decide which is authoritative for each dataset. We have not verified how SAP-side authorisations map to Unity Catalog, so treat that as an open design question.
Tag discipline. ABAC is only as good as the tags. Untagged data is unprotected by tag-based policy.
Do not start with agents. If access, lineage and audit are not in place, adding agents multiplies the exposure.
Context Workshop. To map one decision your agents should make on SAP and Databricks data, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
Where is governance enforced in SAP Databricks?
Mainly in Unity Catalog, which the SAP Databricks documentation describes as providing centralised access control, lineage and auditing across workspaces. SAP Business Data Cloud governs which SAP data products are shared in.
Can SAP governance tags be used in access policies?
Yes. The April 2026 release notes say that when an SAP Business Data Cloud share is mounted to a catalog, SAP semantic metadata including governance tags syncs into Unity Catalog and the tags can be used in ABAC policies.
Is ABAC generally available in Unity Catalog?
Governed tags became generally available on 2 April 2026. The ABAC documentation marks metastore-level policies, policies on views and DENY policies as Beta, so check the current status before relying on them.
Does SAP Databricks make us GDPR or HIPAA compliant?
No platform does that alone. It supplies controls such as access limits, lineage and audit logs. Compliance depends on your policies and evidence, and on the official texts for each regime.
How should we govern AI agents that use this data?
Treat agent policy as its own layer. Give each agent a scoped identity, require approvals for risky actions and keep decision traces. OWASP lists Excessive Agency among the top risks for LLM applications.
Related reading
Continue with data governance for business-ready data and the open and unified metadata platform.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE