Key takeaway
- What a service mesh is, how proxies and the control plane work, sidecar vs ambient, Istio vs Linkerd, adoption steps and when not to use one.
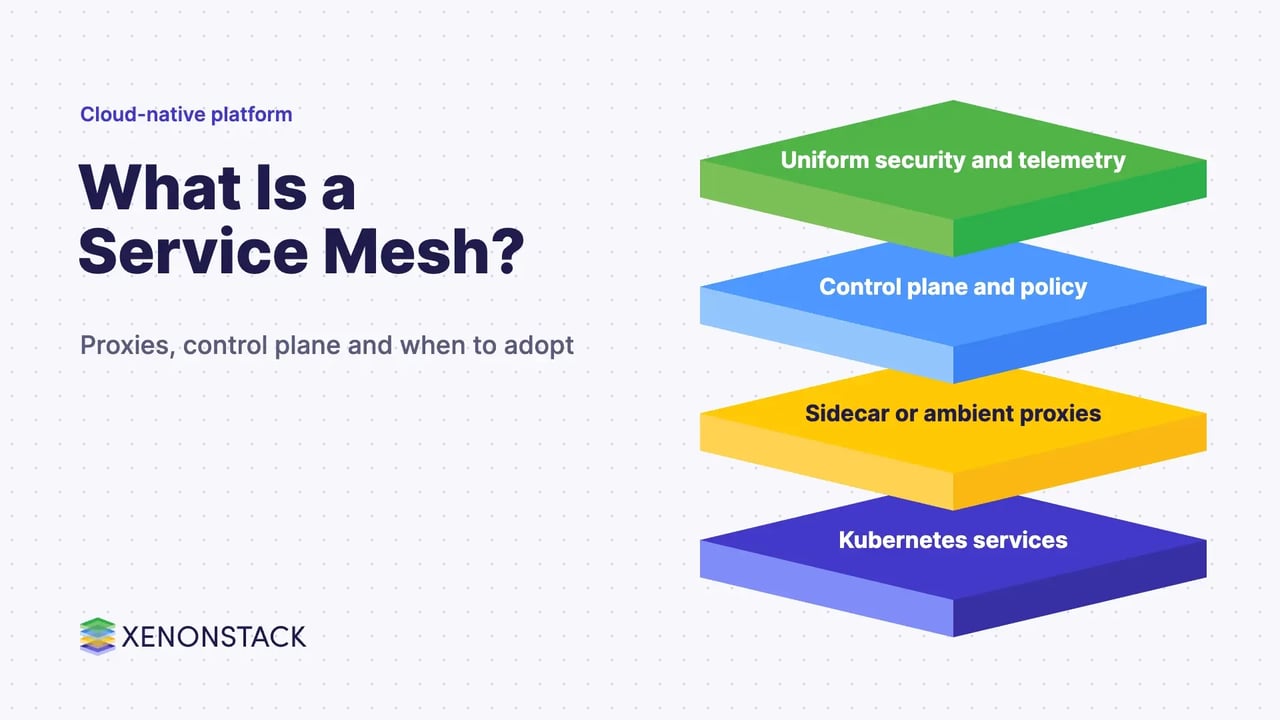
A service mesh is a dedicated infrastructure layer that handles service-to-service communication, so that mutual TLS, retries, timeouts, routing and telemetry are applied by the platform and not coded into every application. Traffic passes through proxies that a central control plane configures. Envoy describes itself as "an L7 proxy and communication bus designed for large modern service oriented architectures" (Envoy docs), and it is the data-plane proxy in Istio.
For enterprise architects the decision is rarely "mesh or no mesh". It is where to enforce identity and policy for east-west traffic, and what operating cost you accept for it. This guide covers how a mesh works, the sidecar and ambient models, Istio and Linkerd, a decision table, and when not to adopt one. For related reading see our guides to Istio service mesh architecture, Linkerd and service-oriented architecture versus microservices.
What problem does a service mesh solve?
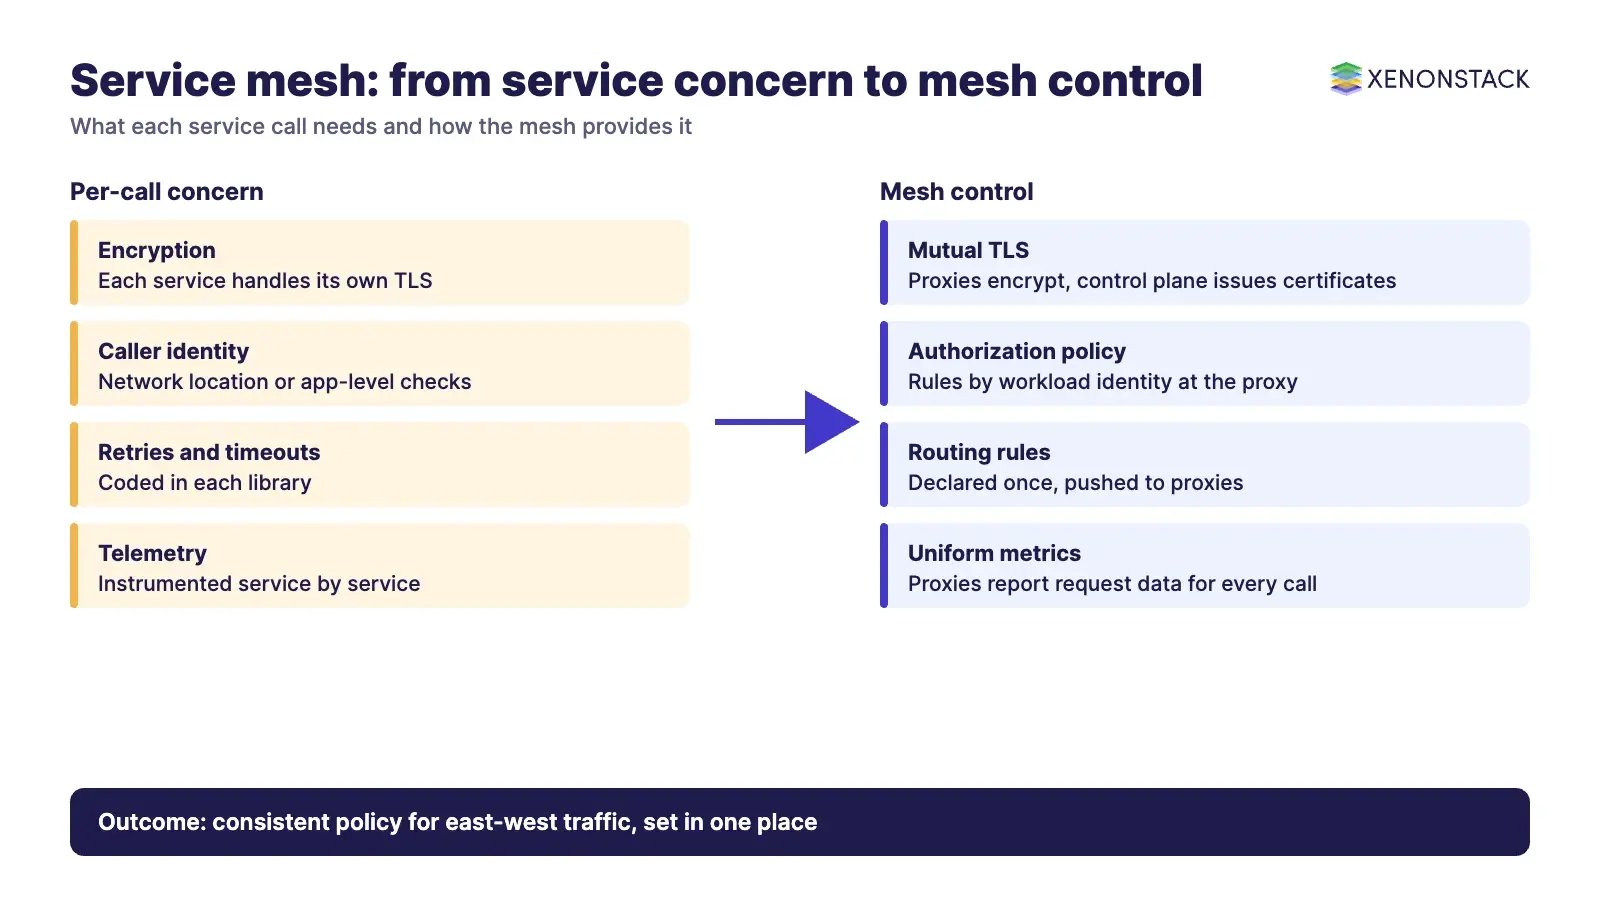
When an application is split into many services, every call between them needs the same things: encryption, caller identity, timeouts, retries, load balancing and a record of what happened. Without a mesh each team re-implements these in its own language and library, and they drift apart. A mesh moves them into the platform so that they are configured once and applied the same way everywhere, usually without changes to service code.
| Concern | Without a mesh | With a mesh |
|---|---|---|
| Encryption between services | Each service manages its own TLS | Proxies perform mutual TLS and the control plane issues workload certificates |
| Caller identity and access | Network location or app-level checks | Policy by workload identity, enforced at the proxy |
| Retries, timeouts, traffic splitting | Libraries in each codebase | Declared as routing rules and pushed to proxies |
| Telemetry | Instrumentation per service | Proxies emit request metrics, logs and traces uniformly |
How does a service mesh work?
A mesh has two parts. The data plane is the set of proxies that carry the traffic. The control plane configures them. In Istio, according to its architecture documentation, the control plane (istiod) provides service discovery, configuration and certificate management, converts high-level routing rules into Envoy configuration and acts as a certificate authority for mutual TLS. Linkerd takes the same split: you install a control plane on the cluster, then add its data plane to workloads, which its docs call "meshing" or "injecting" (Linkerd overview).
Envoy, according to its docs, offers L3/L4 filtering, HTTP L7 routing, service discovery, dynamic configuration through APIs and statistics for its subsystems. That is why a mesh can route by path, retry failed calls and report per-route metrics without touching the application.
Which proxy models does a service mesh use?
There are three common places to put the proxy, and the choice shapes cost, isolation and upgrade effort.
| Model | How it works | Where it fits | Trade-off |
|---|---|---|---|
| Sidecar per pod | A proxy runs beside every application instance and handles its traffic | Strong per-workload isolation; the default data plane in both Istio and Linkerd | Extra containers per pod, and proxies are upgraded with workload restarts |
| Per-node proxy | One proxy per node serves all workloads on it | Simple L4 needs | Shared by many workloads, so less isolation |
| Ambient (Istio) | A per-node L4 proxy (ztunnel), plus optional per-namespace L7 waypoint proxies | Teams that want mTLS first and L7 features only where needed | Newer model; check the Istio docs for the current support status of each feature |
Istio's ambient overview says it uses "a per-node Layer 4 (L4) proxy, and optionally a per-namespace Layer 7 (L7) proxy". The ztunnel is written in Rust and handles mTLS, authentication, L4 authorization and telemetry, but does not parse HTTP. Waypoint proxies are Envoy deployments that run outside application pods and are needed for L7 features such as L7 authorization and VirtualService routing. Sidecar and ambient workloads can co-exist in one mesh, so adoption can be gradual.
What does a service mesh add for security and observability?
A mesh is most often adopted for two reasons: identity-based security and uniform telemetry.
Security: identity and mutual TLS
According to the Istio security documentation, proxies perform a mutual TLS handshake, Istio provisions each workload with X.509 certificates and rotates them automatically, and mutual TLS can be enabled without changing service code. PeerAuthentication has PERMISSIVE (accepts mutual TLS and plain text, suited to migrations), STRICT (mutual TLS only) and DISABLE modes. Authorization is expressed as AuthorizationPolicy with ALLOW, DENY and CUSTOM actions, and a matching DENY takes precedence over ALLOW. The same page notes that workloads with no authorization policy allow all requests, and that mesh-wide peer authentication defaults to PERMISSIVE when unset. A mesh therefore gives you the controls, but you still have to configure and test them. It is one building block of a zero trust security architecture, not a substitute for one.
Observability: uniform request telemetry
Because every request crosses a proxy, the mesh can report request rates, errors and latency per service pair, and support distributed tracing, without each team adding instrumentation. Envoy documents statistics for all subsystems and tracing through third-party providers. You still need a backend to store and view the data, and the application must propagate trace headers for traces to join up.
Which service mesh should you choose?
| Option | What it is | Status (read from its own site) | Fits when |
|---|---|---|---|
| Istio | Mesh built on Envoy; sidecar and ambient data-plane modes | CNCF graduated on 12 July 2023 (CNCF project page) | You need rich L7 traffic management, a large feature set and can staff its operation |
| Linkerd | Kubernetes mesh with Rust micro-proxies; does not use Envoy | CNCF graduated on 28 July 2021; open source under Apache v2, created by Buoyant (Linkerd docs and CNCF) | You want a smaller surface and a Kubernetes-focused mesh; confirm current release and licensing terms on linkerd.io |
| Kubernetes Gateway API for mesh (GAMMA) | Route resources such as HTTPRoute attach to a Service to configure mesh traffic | Support in the Standard Channel since v1.1.0 and considered GA (Gateway API docs) | You want mesh routing expressed in a portable Kubernetes API; check which mesh implements it |
| No mesh | Libraries, ingress and network policy | Not applicable | You run a handful of services and do not need uniform mTLS or L7 policy |
Sources: CNCF Istio, CNCF Linkerd, Gateway API mesh guide.
How do you adopt a service mesh?
Check the prerequisites. Workloads should already run on Kubernetes with health endpoints, and your team should have a clear first goal, such as mutual TLS or request telemetry.
Start with observability and permissive mode. Mesh one non-critical namespace and watch the telemetry before enforcing anything.
Turn on enforcement gradually. Move from permissive to strict mutual TLS only when every client of a service is meshed, then add authorization policy.
Automate injection and upgrades. Use automatic proxy injection in the CI/CD path and plan how proxy and control-plane versions are upgraded.
Add L7 routing only where it earns its place. Retries and traffic splitting can hide or amplify failures, so set timeouts and retry budgets deliberately.
Kubernetes itself already provides service discovery and basic load balancing, so the mesh builds on the platform described in our guide to Kubernetes architecture and components. For smaller footprints, see how services are deployed in microservices at the edge.
When should you not use a service mesh?
| Situation | Why a mesh may not help | Alternative |
|---|---|---|
| A small number of services | Proxies and a control plane add operating cost for little gain | Ingress, TLS at the edge, Kubernetes network policy |
| Teams without platform skills | Mesh upgrades, policy and debugging need skilled owners | Managed offering or start with libraries |
| Latency-critical paths | Each proxy hop adds work; measure it in your environment | Test with your own workload before committing |
| Governance of AI agent actions | A mesh governs network calls, not the business meaning of a decision | A decision layer above agents, see below |
A mesh answers "may service A call service B, and was the call encrypted?". It does not record why an automated decision was made. Teams running AI agents on top of microservices often pair network controls with a decision layer. ElixirData describes its Context OS as keeping governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC as keeping autonomous agent actions inside policy, with the audit trail risk teams need. ElixirClaw is described as an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
To map one service-to-service decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
FAQ
What is a service mesh in simple terms?
A service mesh is an infrastructure layer in which proxies handle service-to-service traffic and a control plane configures them, so security, routing and telemetry are applied by the platform and not by each application.
What is the difference between a sidecar and ambient mode?
In sidecar mode a proxy runs beside every pod. In Istio ambient mode, according to its docs, a per-node L4 proxy (ztunnel) handles mTLS and L4 functions, and optional per-namespace waypoint proxies provide L7 features. Both can co-exist in one mesh.
Is Istio or Linkerd better?
It depends on your needs. Istio is built on Envoy and offers broad L7 traffic management. Linkerd uses its own Rust micro-proxies and focuses on Kubernetes. Both are CNCF graduated projects. Confirm current releases and licensing on each project site.
Does a service mesh replace an API gateway?
No. A gateway manages traffic entering the platform from outside, while a mesh manages traffic between services inside it. Kubernetes Gateway API also defines how routes can attach to Services for mesh use (GAMMA).
Does a mesh enforce mutual TLS by default?
Not necessarily. According to the Istio docs, mesh-wide peer authentication defaults to PERMISSIVE when unset, and workloads without authorization policy allow all requests. Move to STRICT and add policies deliberately.
When is a service mesh not worth it?
When you run only a few services, lack platform skills to operate the control plane, or only need TLS at the ingress. Start with the simplest control that meets the requirement.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE