Key takeaway
- How ServiceNow AI agents fit a SOC: products listed, what has changed, a staged adoption plan and where to keep analysts in control of actions.
ServiceNow AI agents can take over part of the routine work in a security operations centre (SOC): sorting incidents, enriching them and preparing a response for an analyst to approve. ServiceNow describes its AI agents as agents that "act autonomously to get work done", and its Security Operations page says Now Assist helps "scale" incident response and exposure management with AI agents. The decision for a CISO is not whether to use them but which actions an agent may take alone and which need a human sign-off.
This guide is for CISOs, SOC leads and security architects who run ServiceNow already. It lists what ServiceNow documents for security, what has changed since Now Assist first appeared, how to adopt agents in stages, and where to keep people in the loop. For the wider platform, see our ServiceNow solutions page and the companion guide on autonomous incident resolution with ServiceNow AI agents.
What do ServiceNow AI agents do in security operations?
On its Security Operations page, ServiceNow lists the products that agents work with: Security Incident Response, Unified Security Exposure Management, Threat Intelligence Security Center, Security Posture Control and Identity Security (Veza from ServiceNow). The page says AI agents are available "out of the box" and can also be built as custom agents. It does not name individual security agents or give technical detail on Now Assist security features, so ask your ServiceNow account team for the agent list in your release before you plan scope.
| ServiceNow product (as listed) | Security job it covers | Where an agent fits | Status |
|---|---|---|---|
| Security Incident Response | Respond to evolving threats and manage security incidents | Triage, summary and response preparation | Listed on ServiceNow Security Operations page; agent coverage to be confirmed per release |
| Unified Security Exposure Management | Identify, prioritise and remediate vulnerabilities | Prioritising exposure and routing fixes | Listed; named by ServiceNow as an AI agent use case with Now Assist |
| Threat Intelligence Security Center | Threat hunting, modelling and analysis | Enriching incidents with threat context | Listed; agent coverage not stated on the page |
| Security Posture Control | Security for assets on premises and in the cloud | Posture checks feeding incident and fix workflows | Listed; agent coverage not stated on the page |
| Identity Security (Veza from ServiceNow) | Risk across human, non-human and AI agent identities | Governing the identities agents themselves use | Listed |
ServiceNow also publishes customer-story figures on that page, such as "1 minute from threat detection to response" and "7X faster closing incidents with AI agents". They are vendor-reported, come without a stated method, and should not be used as a planning baseline. Measure your own mean time to respond before and after a pilot.
What has changed since Now Assist first targeted the SOC?
The early framing was a single assistant that summarises and recommends. ServiceNow now describes teams of agents. According to its AI agents page, the AI Agent Orchestrator coordinates agents toward a shared goal, AI Agent Studio lets teams set guardrails on agents in natural language, and the Super Intelligence Control Tower manages strategy, governance and performance for AI across the enterprise. The page names Brazil as the latest release at the time of reading (12 November 2026).
For a SOC this shifts the design question. An assistant that drafts a summary is low risk. An agent that can change an endpoint, a firewall rule or a ticket state needs the same controls as a human with that access: scoped permissions, an approval step for high-impact actions and a record of what it did and why.
How should a SOC adopt ServiceNow AI agents in stages?
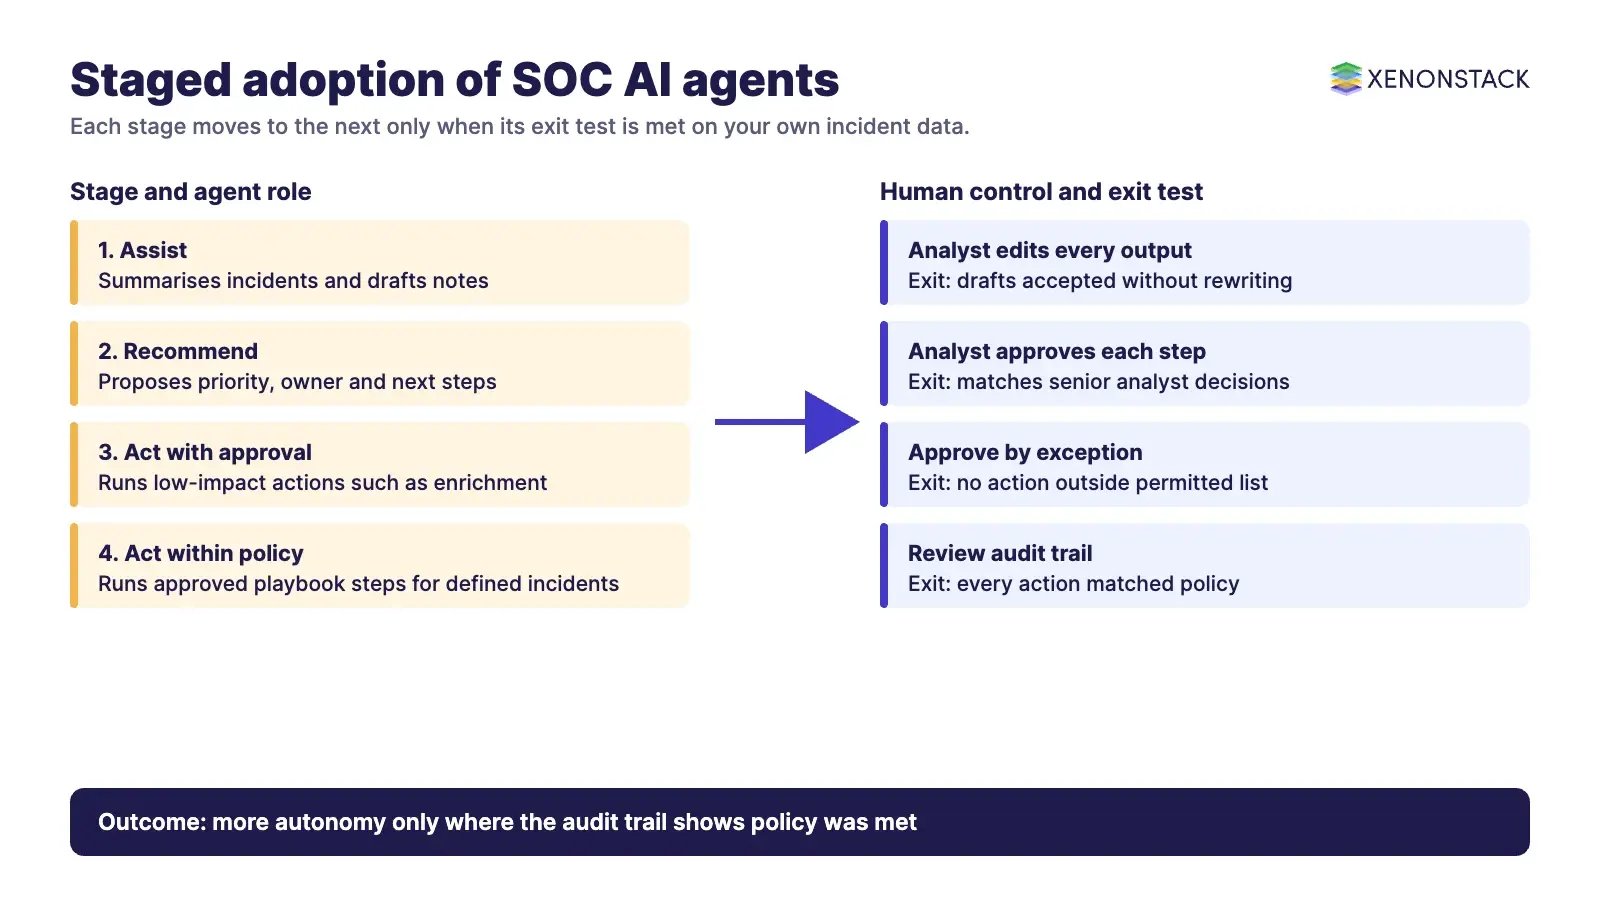
| Stage | What the agent does | Human role | Exit test |
|---|---|---|---|
| 1. Assist | Summarises incidents and drafts notes for the analyst | Analyst reads and edits every output | Analysts accept most drafts without rewriting |
| 2. Recommend | Proposes priority, owner and next steps | Analyst approves each step | Recommendations match senior analyst decisions on a sample |
| 3. Act with approval | Runs low-impact actions such as enrichment or ticket updates | Approves by exception; reviews a sample | No action outside its permitted list |
| 4. Act within policy | Runs approved playbook steps alone for defined incident types | Reviews audit trail and outcomes | Audit shows every action matched policy |
Move to the next stage only when the exit test is met on your own incident data. Do not widen scope for incident types where a wrong action is costly or hard to reverse, such as isolating production servers.
How do you govern autonomous security agents?
Treat each agent as a privileged identity. Give it the minimum access it needs, log every action, and review the log on a schedule. ServiceNow lists Identity Security among its security products specifically for risk across human, non-human and AI agent identities, which is relevant when agents hold credentials.
Platform guardrails cover the ServiceNow side. Many SOCs also act across SIEM, endpoint and identity tools outside ServiceNow. For that layer, AgentGRC is ElixirData's control layer for AI agents, enforcing policy on what autonomous systems can do and recording the evidence that audit and risk teams need. The Audit Agent assembles a decision's history, applicable policy version and approvals into a package an auditor can review. For routine security-centre work outside ServiceNow, MetaSecure AI offers cooperating AI agents that sort alerts, investigate incidents, check compliance and coordinate responses.
What does it cost and what are the trade-offs?
This post does not quote prices, because ServiceNow licensing for AI agents varies by contract and release. Ask for the entitlement list in writing. The main trade-offs are: agents depend on clean incident and asset data in your ServiceNow instance; each extra integration adds a permission to manage; and more autonomy means more review work on the audit trail, not less. Keep human control where an action is hard to undo, where it touches regulated data, or where the data behind the decision is incomplete.
When should you not automate a security action?
Hold back when the incident type is rare and your team has no history to test against, when the affected system is business critical and a wrong isolation would cause an outage, or when the evidence needed for the decision sits outside ServiceNow and cannot be read by the agent. In these cases use the agent to prepare context and leave the action to an analyst.
Continue with related guides: ServiceNow AI agents for HR service delivery, ServiceNow AI agents for banking and ServiceNow AI agents for IT service management.
To map one security decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
Frequently asked questions
What are ServiceNow AI agents?
ServiceNow describes them as agents built into the ServiceNow AI Platform that act autonomously to get work done across areas such as IT, customer service and HR. Security Operations is one of the areas it lists.
Can ServiceNow AI agents respond to security incidents on their own?
ServiceNow says AI agents help scale incident response and exposure management. How much an agent does alone is set by your configuration and guardrails, so start with recommendations and approvals before autonomous actions.
What is the AI Agent Orchestrator?
According to ServiceNow, it coordinates teams of AI agents so they work together toward a shared goal.
How do you set guardrails on a ServiceNow agent?
ServiceNow says AI Agent Studio, its tool for building agents, lets teams set guardrails on agents using natural language.
Are ServiceNow customer-story figures a safe planning baseline?
No. Figures such as faster incident closure are vendor-reported with no stated method. Measure your own response times before and after a pilot.
Which ServiceNow products does security operations use?
ServiceNow lists Security Incident Response, Unified Security Exposure Management, Threat Intelligence Security Center, Security Posture Control and Identity Security (Veza from ServiceNow).
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE