Key takeaway
- DevOps trends for 2027 backed by DORA 2025: AI in delivery, platform engineering, supply chain security and metrics, with a decision table for leaders.
DevOps trends in 2026 centre on one question: how do you keep delivery fast and safe when AI writes more of the code? The 2025 DORA research finds that AI amplifies what a team already does well or badly. Teams with strong testing, version control and fast feedback gain from it. Teams without them see more instability.
This guide replaces our 2023 trends list. It covers five shifts that matter to CTOs, platform leads and engineering heads: AI across the delivery lifecycle, internal developer platforms, software supply chain security, everything as code with governed automation, and measurement beyond tool counts. Each section says what has changed, when it fits and where it can go wrong. For the base practices, see our guide to the DevOps process and operating model.
What are the DevOps trends that matter going into 2027?
| Trend | What has changed since 2023 | When it fits | Main risk |
|---|---|---|---|
| AI in the delivery lifecycle | 90% of DORA 2025 respondents report using AI at work | Teams with strong tests and fast feedback | Higher change volume exposes weak downstream stages |
| Platform engineering | 90% of organisations report an internal developer platform; 76% have dedicated platform teams (DORA) | Many teams repeating the same setup work | A poorly managed platform can reduce throughput and stability |
| Supply chain security | SLSA v1.2 is listed first on slsa.dev; EU CRA reporting duties apply from 11 September 2026 | Any organisation shipping software or running third party code | Controls added late slow every release |
| Everything as code with governed automation | Policy, infrastructure and pipelines are all versioned and reviewed | Multi cloud or regulated estates | Drift between code and what actually runs |
| Measuring outcomes | DORA now uses five metrics, including deployment rework rate | Leaders who need delivery evidence | Metrics used as targets get gamed |
How is AI changing the DevOps lifecycle?
The 2025 DORA report, based on responses from nearly 5,000 technology professionals, reports that more than 80% believe AI has increased their productivity and that 30% have little or no trust in AI generated code. Unlike the previous year, it observes a positive relationship between AI adoption and delivery throughput and product performance. It still observes a negative relationship with delivery stability. DORA attributes this to AI accelerating development and exposing weaknesses in testing, version control and feedback loops. Source: Google Cloud announcement of the 2025 DORA report.
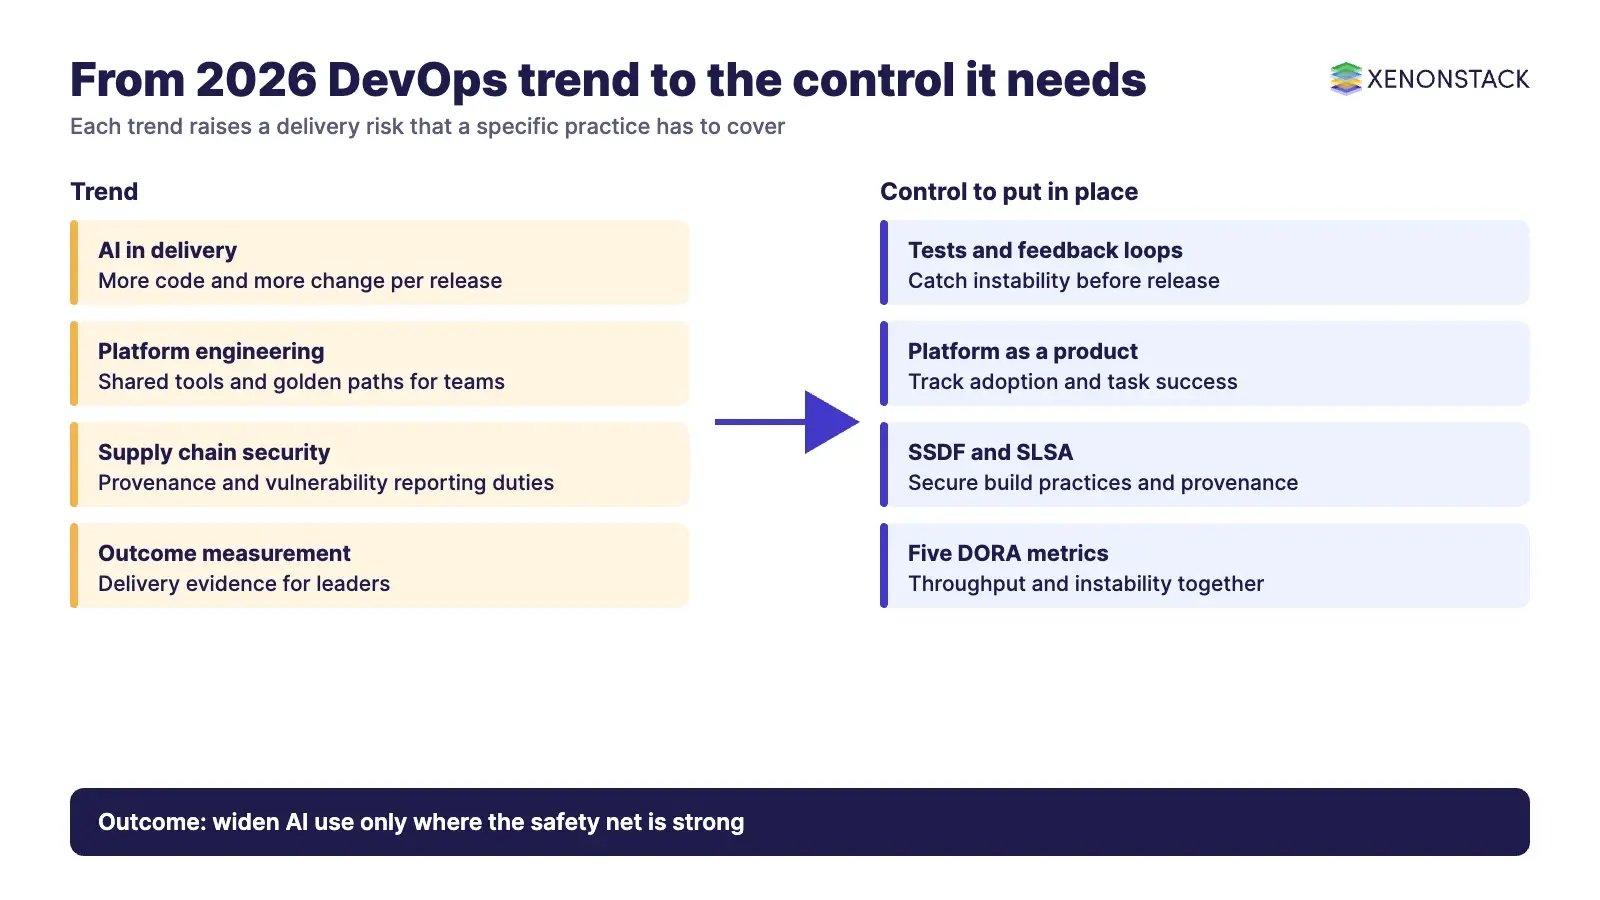
The practical reading for leaders is to strengthen the safety net before widening AI use. DORA's starting points include clarifying AI policies, connecting AI to internal context, prioritising foundational practices, fortifying safety nets and investing in the internal platform. Our earlier points on DevOps for machine learning still apply when the thing being shipped is a model.
Agentic AI adds a governance question: which actions may an agent take in a pipeline, and who can see why it acted? AgentGRC checks autonomous agent actions against policy and keeps records that audit and risk teams can review. For sprint planning and Scrum ceremonies, AgentScrum describes itself as automating them with agentic AI, which is one of the ElixirClaw agent sites; ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
Why is platform engineering replacing ad hoc DevOps teams?
DORA describes platform engineering as a sociotechnical discipline that combines collaboration with automation, self-service and repeatability. The platform is run as an internal product that gives developers shared tools and golden paths. DORA reports that 90% of organisations use an internal developer platform and 76% have dedicated platform teams. Where platform quality is high, the effect of AI adoption on organisational performance is strong and positive. Where it is low, the effect is negligible. Source: DORA platform engineering capability.
DORA also warns that a poorly managed platform may reduce throughput and change stability, and that progress often follows a J curve: an early gain, a dip, then a higher level as the platform matures. Platforms commonly sit on Kubernetes, so a solid grasp of Kubernetes architecture and components helps platform teams set sensible defaults.
| Option | When it fits | When not to |
|---|---|---|
| Dedicated platform team with golden paths | Many product teams repeat the same pipeline, cluster and security setup | Fewer than a few teams, where a shared template is enough |
| Shared pipeline templates only | Early stage, one or two delivery teams | Teams need self-service environments |
| Cloud provider native pipeline | Workloads concentrated on one cloud. See our AWS and GCP pipeline guides | Estate spans several clouds and needs one control plane |
What is changing in software supply chain security?
DevSecOps has moved from scanning at the end to proving where software came from and how it was built. Three official sources frame the work. The NIST Secure Software Development Framework is a set of secure development practices defined in NIST SP 800-218 (version 1.1), with SP 800-218A adding practices for generative AI and dual use foundation models. SLSA (Supply-chain Levels for Software Artifacts) is described as a checklist of standards and controls to prevent tampering, improve integrity and secure packages and infrastructure; v1.2 is listed first on its site.
Regulation is also moving. The EU Cyber Resilience Act entered into force on 10 December 2024. Reporting obligations for actively exploited vulnerabilities apply from 11 September 2026, and the main obligations apply from 11 December 2027. Manufacturers should check with counsel which of their products are in scope. For the wider framework, see our DevSecOps guide and our guide to implementing zero trust.
Which 2023 trends have faded or changed?
| 2023 trend | Status in 2026 | What to do |
|---|---|---|
| Serverless as the default | One option among containers, functions and managed services | Choose per workload, not as a standard |
| Golang as a DevOps language | Many core cloud native tools are written in Go; the trend is established, not new | No action beyond skills planning |
| Chaos engineering | Practice continues as a resilience test | Run it where you already have observability and rollback |
| Value stream management | Still useful for flow analysis; start with the DORA metrics | Use DORA metrics first, add flow measures where needed |
| AIOps and MLOps | Now part of the wider AI in delivery question | Link to governance and platform plans |
How should observability and operations adapt?
More frequent change and more AI assisted code raise the cost of slow diagnosis. Teams that cannot trace a failure from deployment to service behaviour will see rework rise. Start with cloud native observability tools for the tool landscape and full-stack observability for the operating model.
How should you measure DevOps performance going into 2027?
DORA now recommends five delivery metrics: change lead time, deployment frequency and failed deployment recovery time for throughput, and change failure percentage and deployment rework rate for instability. For platforms it recommends a balanced scorecard that adds developer satisfaction, adoption and retention, and task success. Read our DevOps metrics guide for definitions and what to add.
What is a sensible adoption sequence?
- Baseline the five DORA metrics for two or three services.
- Close the gaps AI will expose: automated tests, version control discipline and fast feedback.
- Set an AI policy for code and for agents, including what they may change in a pipeline.
- Stand up a thin platform with golden paths for the most repeated work, and measure its adoption.
- Add supply chain controls in order: provenance, dependency checks, then vulnerability reporting aligned to the rules that apply to you.
- Review quarterly and retire practices that no longer pay back. See the enterprise DevOps operating model for the wider plan.
Trade-offs to weigh: platform teams add cost and a dependency; AI speeds change but needs stronger tests; supply chain controls add friction. Do not start a platform programme before you have a baseline, and do not widen AI use where tests are thin.
To map one delivery decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
The European Commission page on the Cyber Resilience Act gives two dates that affect teams shipping software into the EU.
- 11 September 2026: manufacturers must report actively exploited vulnerabilities, so build that reporting path into your pipeline and incident process.
- 11 December 2027: the main obligations of the Act apply, including handling vulnerabilities across the lifecycle of a product. Use 2027 to put provenance records, dependency checks and clear ownership in place.
Check with counsel which of your products are in scope.
Frequently asked questions
What are the main DevOps trends in 2026?
AI across the delivery lifecycle, internal developer platforms, software supply chain security, governed automation as code, and outcome based measurement with the five DORA metrics.
Does AI make DevOps teams faster?
The 2025 DORA report observes a positive relationship between AI adoption and delivery throughput, but a negative one with delivery stability. DORA says AI amplifies existing strengths and weaknesses.
How common are internal developer platforms?
DORA reports that 90% of organisations use an internal developer platform and 76% have dedicated platform teams.
What supply chain security frameworks should DevOps teams know?
The NIST Secure Software Development Framework (SP 800-218) and SLSA. In the EU, the Cyber Resilience Act brings reporting duties from 11 September 2026 and main obligations from 11 December 2027.
Which DevOps metrics should leaders track?
The five DORA metrics: change lead time, deployment frequency, failed deployment recovery time, change failure percentage and deployment rework rate.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE