Key takeaway
- Azure DevOps pipeline guide for 2027: YAML stages, agent choices, deployment strategies, approvals and checks, secretless access and costs for enterprises.
An Azure DevOps pipeline is the Azure Pipelines service inside Azure DevOps that builds, tests and deploys code automatically from a version control system such as Azure Repos or GitHub. In 2026 the enterprise default is a YAML pipeline stored with the code, running on Microsoft-hosted agents, Managed DevOps Pools or self-hosted agents, and deploying to environments that are protected by approvals and checks.
This guide is for CTOs, platform leads and solution architects who own a delivery estate on Azure DevOps. It covers what has changed (classic pipelines off by default for new organisations, public projects retired, secretless service connections), how to choose agents and deployment strategies, how to govern pipelines and what they cost. If you are still choosing a platform, start with our comparison of Azure and AWS DevOps tools.
What is an Azure DevOps pipeline?
Microsoft describes Azure Pipelines as the part of Azure DevOps that combines continuous integration, continuous testing and continuous delivery to build, test and deploy code to any destination. It supports Node.js, Python, Java, PHP, Ruby, C#, C++, Go, Xcode, .NET, Android and iOS projects, runs on Linux, macOS and Windows, and can publish NuGet, npm, Maven or Python packages to Azure Artifacts or another feed. For the wider CI/CD picture, see our guide to CI/CD pipeline stages, tools and best practices.
A pipeline is built from a small set of parts. Knowing them makes design reviews and audits much faster.
| Concept | What it is | Why leaders care |
| Stage and job | A pipeline is one or more stages; each stage holds jobs, and each job runs steps on one agent | Stages map to your release gates (build, test, production) |
| Agent | Compute with agent software that runs one job at a time | Drives cost, speed and network reach |
| Artifact | Files or packages published by a run for later stages | Build once, deploy the same output everywhere |
| Deployment job and environment | A job that runs against a named environment and records deployment history | Audit trail of what went where, and when |
| Approvals and checks | Validations a stage must pass before it can use a protected resource | Your control point for production changes |
| Service connection | A stored connection to Azure or another external service | The most sensitive credential in the pipeline |
Source: Key Azure Pipelines concepts, Microsoft Learn.
What has changed in Azure Pipelines since 2023?
Many older Azure DevOps guides, including the first version of this post, describe click-through classic pipelines, public projects with unlimited free minutes and service connections that store a secret. Each of these has changed.
| Area | Current status (checked November 2026) | What to do |
| Classic build and release pipelines | Creation is disabled by default for new organisations (from Sprint 226); existing classic pipelines keep running and can be edited | Write new pipelines in YAML and plan migration of classic ones |
| Public projects | Retired in April 2026; no new public projects; existing ones convert to private in 2027 and move to the private free allocation | Move open-source work to GitHub; budget minutes for converted projects |
| Azure service connections | Workload identity federation is the recommended option and removes stored secrets; the Azure DevOps issuer for these connections retires on 1 July 2027 in favour of the Microsoft Entra issuer | Convert secret-based connections and check issuer status |
| Agent infrastructure | Managed DevOps Pools is generally available as the evolution of Virtual Machine Scale Set agent pools | Consider it before building new self-hosted fleets |
| Approvals and checks | Checks now run in a fixed order of five categories, from static checks to exclusive lock | Redesign gates so cheap checks fail first |
| Security scanning | GitHub Advanced Security for Azure DevOps is sold as Secret Protection and Code Security | Turn on push protection and dependency scanning in pipelines |
Sources: securing YAML pipelines, public projects retirement, Azure Resource Manager service connections, Managed DevOps Pools overview and approvals and checks, all on Microsoft Learn.
How does a YAML pipeline move code from commit to production?
A YAML pipeline lives in the repository, so it is reviewed through pull requests and versioned like any other code. A typical enterprise flow has five steps.
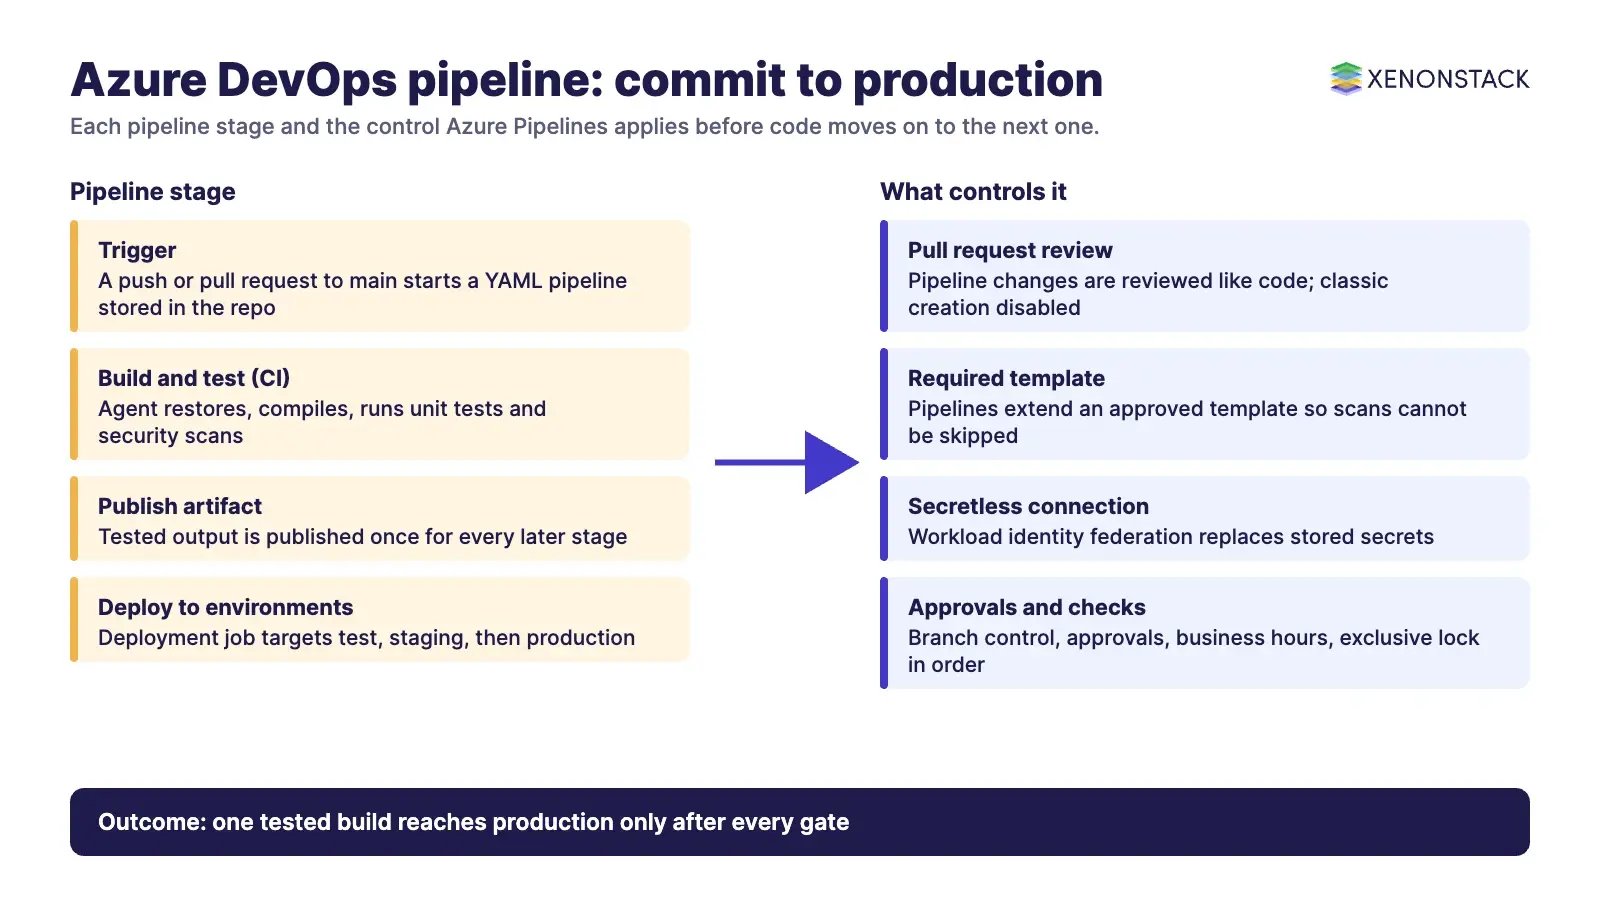
- Trigger: a push or pull request to a branch such as
mainstarts a run. - Build and test (CI): a job restores dependencies, compiles, runs unit tests and security scans, and fails fast on errors.
- Publish an artifact: the tested output is published once, so every later stage deploys the same build.
- Deploy to lower environments: a deployment job targets a test or staging environment and records history against it.
- Gate and release to production: the production environment's approvals and checks must pass before the stage runs, using a deployment strategy such as runOnce, rolling or canary.
A minimal two-stage pipeline looks like this:
trigger:
- main

stages:
- stage: Build
  jobs:
  - job: Build
    pool:
      vmImage: ubuntu-latest
    steps:
    - script: echo build and test

- stage: Production
  dependsOn: Build
  jobs:
  - deployment: Deploy
    environment: production
    strategy:
      runOnce:
        deploy:
          steps:
          - script: echo deploy
The approvals and checks for production are not written in this file. Resource owners set them in the Azure Pipelines web interface, so someone who edits the YAML cannot remove them. To create the first pipeline, open your project, select Pipelines and then New pipeline, choose GitHub or Azure Repos Git, pick a starter pipeline, and select Save and run, as described in Microsoft's classic-to-YAML guide.
Which agent model fits your workloads?
The agent choice decides how fast builds run, what they can reach on your network and how the bill grows.
| Agent model | What you get | When it fits | Limits |
| Microsoft-hosted | A freshly imaged VM for each job, 10 GB of storage, images updated about every three weeks | Standard builds with public dependencies | Cannot join your corporate network, no remote access, no larger machines |
| Managed DevOps Pools | Microsoft-managed agents with custom images, chosen region, scaling rules, agent state kept up to seven days, jobs up to two days | Large estates that need private network access or bigger machines without running the fleet | Configured and billed through an Azure subscription |
| Self-hosted | Your own machines with the agent installed | Special hardware, strict isolation or on-premises targets | You patch, secure and scale them yourself |
Sources: Microsoft-hosted agents and Managed DevOps Pools overview, Microsoft Learn.
Which deployment strategy should you use?
Deployment jobs in YAML support three strategies. Each runs lifecycle hooks (preDeploy, deploy, routeTraffic, postRouteTraffic) and then on: success or on: failure steps, which is where rollback logic belongs.
| Strategy | How it works | When it fits |
| runOnce | Runs each lifecycle hook once; the default and simplest strategy | App Service slots, functions, low-risk internal services |
| rolling | Replaces the old version on a rolling set of up to five target VMs per iteration, controlled by maxParallel |
VM fleets that must stay available during release |
| canary | Sends the change to a small share first (Microsoft's AKS example uses 10 per cent, then 20 per cent) and checks health before going to 100 per cent | Customer-facing Kubernetes services where errors are costly |
Source: Deployment jobs, Microsoft Learn. For the trade-offs between release patterns, read canary vs blue-green deployment.
How do you govern and secure Azure Pipelines at enterprise scale?
The pipeline holds the keys to production, so it needs the same controls as production. Microsoft's pipeline security guidance and our own delivery work point to six controls.
- YAML only: turn on the organisation settings that disable creation of classic build and classic release pipelines, because YAML and classic pipelines share resources such as service connections.
- Approved templates: make pipelines extend a central template and add the Required template check on protected resources, so scanning and policy steps cannot be skipped.
- Ordered checks: checks run in five categories: static checks (branch control, required template, evaluate artifact), pre-check approvals, dynamic checks (approval, Invoke Azure Function, Invoke REST API, business hours, Azure Monitor alerts), post-check approvals and exclusive lock. If one category fails, later ones do not run.
- Secretless access to Azure: use workload identity federation with an app registration or managed identity for Azure Resource Manager service connections. Azure Pipelines may disable connections unused for 100 days, and those events are written to the audit log.
- Code and secret scanning: GitHub Advanced Security for Azure DevOps adds secret push protection, repository secret scanning, dependency scanning and CodeQL code scanning for Azure Repos.
- Branch control: allow production resources to be used only by runs from protected branches.
The same pattern applies on other clouds; our guide to a secure DevSecOps CI/CD pipeline on AWS shows the AWS equivalents. As AI agents start to raise pull requests and trigger releases, the same gates have to cover their actions too. AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
What does Azure Pipelines cost?
Pricing is based on parallel jobs, not on users of Pipelines. The free grant applies only once the organisation is linked to a valid Azure subscription for billing.
| Tier | Job time limit | Monthly limit |
| Free, Microsoft-hosted (private projects) | One parallel job, up to 60 minutes per run | 1,800 minutes (30 hours) |
| Paid Microsoft-hosted parallel job | Up to 360 minutes per job | No monthly limit |
| Free self-hosted | One self-hosted concurrent job | No job length restriction |
New organisations can buy up to 25 Microsoft-hosted parallel jobs before they need to ask support for more. The Azure DevOps free tier also includes the first five Basic users and 2 GiB of Azure Artifacts storage. Current prices per parallel job are on the Azure DevOps pricing page. Sources: parallel jobs and billing overview, Microsoft Learn.
How should an enterprise adopt or modernise Azure Pipelines?
A sequence that keeps releases flowing while risk goes down:
- Inventory: list classic build pipelines, classic release pipelines, task groups, service connections and agent pools, with owners.
- Template first: build a central YAML template with build, test, scan and publish steps, and make new pipelines extend it.
- Migrate builds: export classic build pipelines with Export to YAML. Classic release pipelines cannot be exported, so rebuild them as deployment jobs and environments.
- Secure the edges: convert service connections to workload identity federation and add approvals, branch control and the required template check to production environments.
- Right-size agents: move private-network builds to Managed DevOps Pools and keep simple builds on Microsoft-hosted agents.
- Lock it in: disable creation of classic pipelines and review parallel job usage each quarter. Infrastructure belongs in the same flow; see what infrastructure as code is and how to apply it.
What we see in delivery work
In client programmes, Azure DevOps and GitHub stay the systems of execution, and the gap is usually visibility: delivery leads cannot see how work items, builds and blockers connect across teams. Our teams connect Azure DevOps work and delivery data to a context layer so agents can answer sprint and release questions from live data. AgentScrum automates sprint planning and Scrum ceremonies with agentic AI, tracking blockers and burndown to improve delivery predictability. Underneath, ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents.
A common modernisation pattern for containerised .NET services is to build the image in the CI stage, push it to a registry, and release it to Kubernetes through a deployment job with Helm charts, replacing manual builds and uploads that were slow and error-prone.
When is Azure Pipelines not the right choice?
- Public open-source work: Microsoft has retired public projects and is consolidating open-source collaboration on GitHub, so public repositories belong there.
- Builds that must sit inside your network on hosted agents: Microsoft-hosted agents cannot join a corporate network; use Managed DevOps Pools or self-hosted agents instead.
- Large classic release estates with no migration budget: classic pipelines still run, but they miss YAML-only controls such as pull-request review of pipeline changes and runtime parameters. Plan the migration rather than adding more classic pipelines.
- Very long jobs on the free tier: the 60-minute limit per run means long builds need paid parallel jobs, splitting into multiple jobs, or Managed DevOps Pools.
To map one release decision your pipelines and agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
Microsoft documents two dated changes that affect pipelines in 2027.
- 1 July 2027: for workload identity federation service connections in Azure public cloud, the Azure DevOps issuer retires and Microsoft standardises on the Microsoft Entra issuer. New connections already use Entra by default, and affected connections are flagged for conversion (Azure Resource Manager service connections). Multitenant applications and non public clouds are excluded.
- During 2027: remaining public projects convert to private automatically. Exact dates will be shared through in product banners, and free Microsoft hosted minutes then fall from unlimited to 1,800 a month (public projects retirement).
Inventory your service connections and any public projects now, so neither change arrives as an outage.
Frequently asked questions about Azure DevOps pipelines
What is an Azure DevOps pipeline?
It is a pipeline in Azure Pipelines, the Azure DevOps service that combines continuous integration, continuous testing and continuous delivery to build, test and deploy code from Azure Repos, GitHub or another version control system to any target.
Should we still build classic release pipelines?
No. Creation of classic build and release pipelines is disabled by default for new organisations, and Microsoft recommends YAML pipelines for security. Existing classic pipelines keep running, but new work should use YAML deployment jobs and environments.
How much does Azure Pipelines cost?
Once billing is linked to an Azure subscription, private projects get one free Microsoft-hosted parallel job of up to 60 minutes per run and 1,800 minutes a month, plus one self-hosted job. Paid parallel jobs run for up to 360 minutes with no monthly limit.
How do pipelines deploy to Azure without storing secrets?
Use an Azure Resource Manager service connection with workload identity federation, backed by an app registration or a managed identity. Microsoft recommends this option because it removes secrets and secret rotation.
Which agents should an enterprise use?
Microsoft-hosted agents suit standard builds. Managed DevOps Pools suit builds that need private network access, custom images or longer jobs without running your own fleet. Self-hosted agents suit special hardware or strict isolation.
What happens to public Azure DevOps projects?
Public projects were retired in April 2026. No new ones can be created, and existing public projects convert to private in 2027, when their free pipeline minutes move to the private allocation of 1,800 minutes a month.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE