Key takeaway
- Containers as a Service explained: how CaaS sits between IaaS and PaaS, how containers differ from VMs, what platforms provide and the security risks.
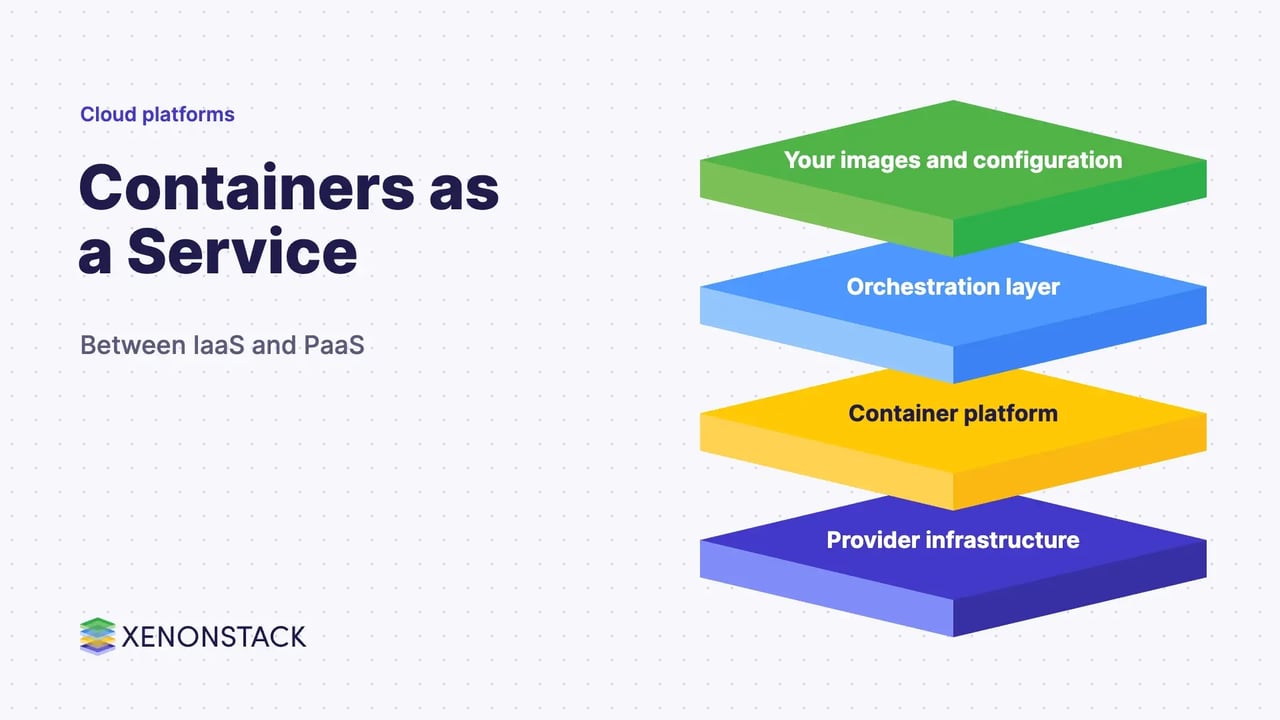
Containers as a Service (CaaS) is a cloud service that lets teams deploy and manage containerised applications on a provider's platform, usually with an orchestration layer that handles deployment, scaling and load balancing. IBM describes it as sitting between infrastructure as a service (IaaS) and platform as a service (PaaS).
This guide is for platform engineers, DevOps leads and architects choosing how to run containers. It explains what CaaS is, how it fits between IaaS and PaaS, how containers differ from virtual machines, what a CaaS platform provides, and what to settle first. Note that CaaS here means Containers as a Service, not Content as a Service, a different idea with the same initials.
What is Containers as a Service?
IBM's page on containers as a service defines CaaS as a cloud computing service that allows developers to manage and deploy containerised applications. Its orchestration layer facilitates automated container deployment, and IBM says it also covers load balancing, scheduling, scaling and lifecycle management. It names Kubernetes as the most popular orchestration platform and lists alternatives such as Amazon ECS, Google Kubernetes Engine and Docker Swarm.
Where does CaaS sit between IaaS and PaaS?
IBM places CaaS between the two. IaaS lets teams fully customise components, from application stacks to operating systems, while PaaS is simpler but limits user control of the operating system and portability across environments. CaaS gives control back by letting teams customise the container and its environment. For the neighbouring layers, see our guides to PaaS and to IaaS provisioning with Terraform.
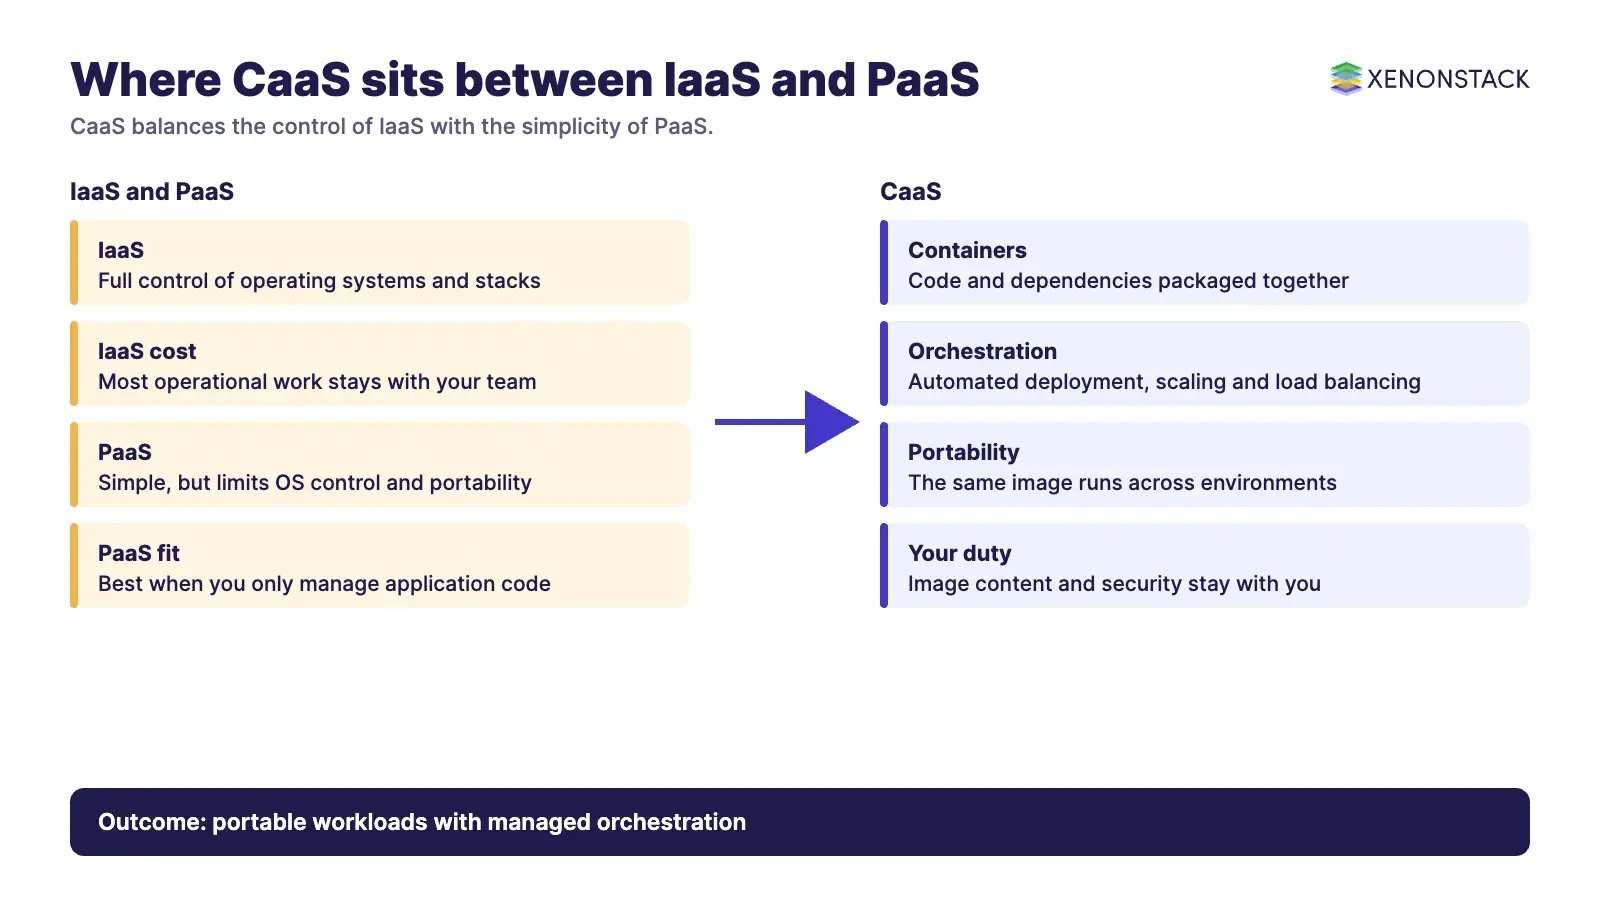
| Model | What the provider manages | What your team controls | Trade-off |
|---|---|---|---|
| IaaS | Compute, storage and network | Operating systems and application stacks | Most control, most operational work |
| CaaS | Container platform and orchestration | Container images and their configuration | Portable workloads, but you own the images |
| PaaS | Runtime and operating system | Application code | Simplest, least control and portability |
How do containers differ from virtual machines?
Docker says in its container overview that containers virtualise the operating system instead of hardware. A container packages code and dependencies together, and multiple containers on one machine share the OS kernel, each running as an isolated process in user space. A virtual machine, by contrast, includes a full copy of an operating system. Docker also says container images are typically tens of megabytes, while virtual machines take up tens of gigabytes. More on the practice is in our guide to containerisation in DevOps, and you can find the vendor's own description at Docker.
What does a CaaS platform provide?
IBM lists the benefits of CaaS as focus on core competencies, scalability, efficiency, cost, portability and collaboration. In practice the capabilities teams look for are:
- Orchestration. Automated deployment, scheduling, scaling and lifecycle management of containers. The Kubernetes project describes itself as an open source platform for managing containerised workloads and services; see its overview.
- Scaling on demand. IBM says users can add and remove containers based on demand.
- Pay-as-you-go pricing. IBM says CaaS providers offer pay-as-you-go models.
- Portability. IBM lists portability among the benefits of CaaS.
Stateful workloads need a storage plan; our guide to the Container Storage Interface for Kubernetes covers that layer. Teams moving from service-based designs will also find our overview of service-oriented architecture useful context.
What are the security risks of containers?
The NIST Application Container Security Guide (SP 800-190) identifies risks in five areas: images, registries, orchestrators, containers and host operating systems. Examples it names include vulnerable software in images, secrets stored in clear text, overly broad administrative access to orchestrators, and a shared kernel between containers on the same host. A CaaS provider can manage part of this, but image content and configuration remain your responsibility. Read our guide to the container security framework, mechanisms and strategy, and, for a related security topic about coordinated machines, botnet detection and prevention techniques.
How does CaaS support DevOps?
A container image behaves the same in development and production, which removes a common source of disagreement between developers and operations teams: the application that works in one environment and fails in another. A shared platform also gives both teams one place to define how applications are built, deployed and scaled. A CaaS platform does not create DevOps culture, but it gives it a common surface to work on.
How do AI agents change container operations?
AI agents can take on routine platform work: reading deployment health, proposing a scale change, checking an image against a policy or drafting a rollback. They need scoped permissions on the orchestrator and a record of each action, since the risks NIST lists, such as broad administrative access, apply to agents as much as to people. ElixirClaw is XenonStack's AI agents computing platform for building and running agents of this kind.
What should you do first?
- List the applications that would benefit from portable packaging and independent scaling.
- Choose an orchestration platform and decide who manages it, you or a provider.
- Define image standards: base images, scanning and secrets handling.
- Plan storage and networking for stateful services before migrating them.
- Set permissions for people and agents on the orchestrator, and log every action.
To map one decision your agents make on your container platform, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What does CaaS stand for?
In this context CaaS stands for Containers as a Service. It is not the same as Content as a Service, which shares the abbreviation.
How is CaaS different from PaaS?
IBM says PaaS is simpler but limits user control of the operating system and portability across environments, while CaaS gives control back through OS virtualisation and customisation.
How is a container different from a virtual machine?
Docker says containers virtualise the operating system instead of hardware and share the host kernel, while each virtual machine includes a full copy of an operating system.
Which tools orchestrate containers in CaaS?
IBM names Kubernetes as the most popular orchestration platform, with alternatives including Amazon ECS, Google Kubernetes Engine and Docker Swarm.
Are containers secure by default?
No. NIST SP 800-190 identifies risks across images, registries, orchestrators, containers and host operating systems that teams must manage.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE