Key takeaway
- Agentic AI lets software plan and act toward a goal. Compare framework categories, how to choose one, enterprise use cases and the governance agents need.
Agentic AI is software that uses an AI model to pursue a goal across several steps. It plans, calls tools and business systems, checks the result and adjusts, within limits that people set. An agentic AI framework is the code layer that makes this possible: it runs the agent loop, keeps state, connects tools and coordinates agents.
For enterprise leaders, the framework is the smaller decision. Today’s options fall into a few clear categories, and most now support open protocols such as MCP and A2A. The larger decision is the operating layer around the agents: what context they use, which policies they must obey, who approves high-impact actions, and how every decision is recorded.
What is agentic AI, and why does it matter now?
Traditional automation follows a fixed script. A generative AI assistant answers a prompt. An agent is given a goal, decides the steps, uses tools to act, and keeps going until the goal is met or it needs a person. Our guide to AI agent categories and business applications covers the agent types in more depth.
It matters now because agents are moving into the software enterprises already run. Gartner predicts that by 2028, 33% of enterprise software applications will include agentic AI, up from less than 1% in 2024, and that at least 15% of day-to-day work decisions will be made autonomously by agentic AI (Gartner, June 2025). Decisions made by software need the same accountability as decisions made by people.
| Aspect | Rule-based automation | Generative AI assistant | Agentic AI |
|---|---|---|---|
| Trigger | Event or schedule | User prompt | Goal, event or another agent |
| Steps | Fixed by a developer | Single response | Planned and revised at run time |
| Actions | Predefined integrations | Usually none; a person acts | Calls tools, APIs and other agents |
| Main risk | Breaks when inputs change | Wrong or invented answers | Wrong action taken at speed and scale |
| Control needed | Testing and change control | Review of outputs | Policy, permissions, approvals and decision traces |
What does an agentic AI architecture look like?
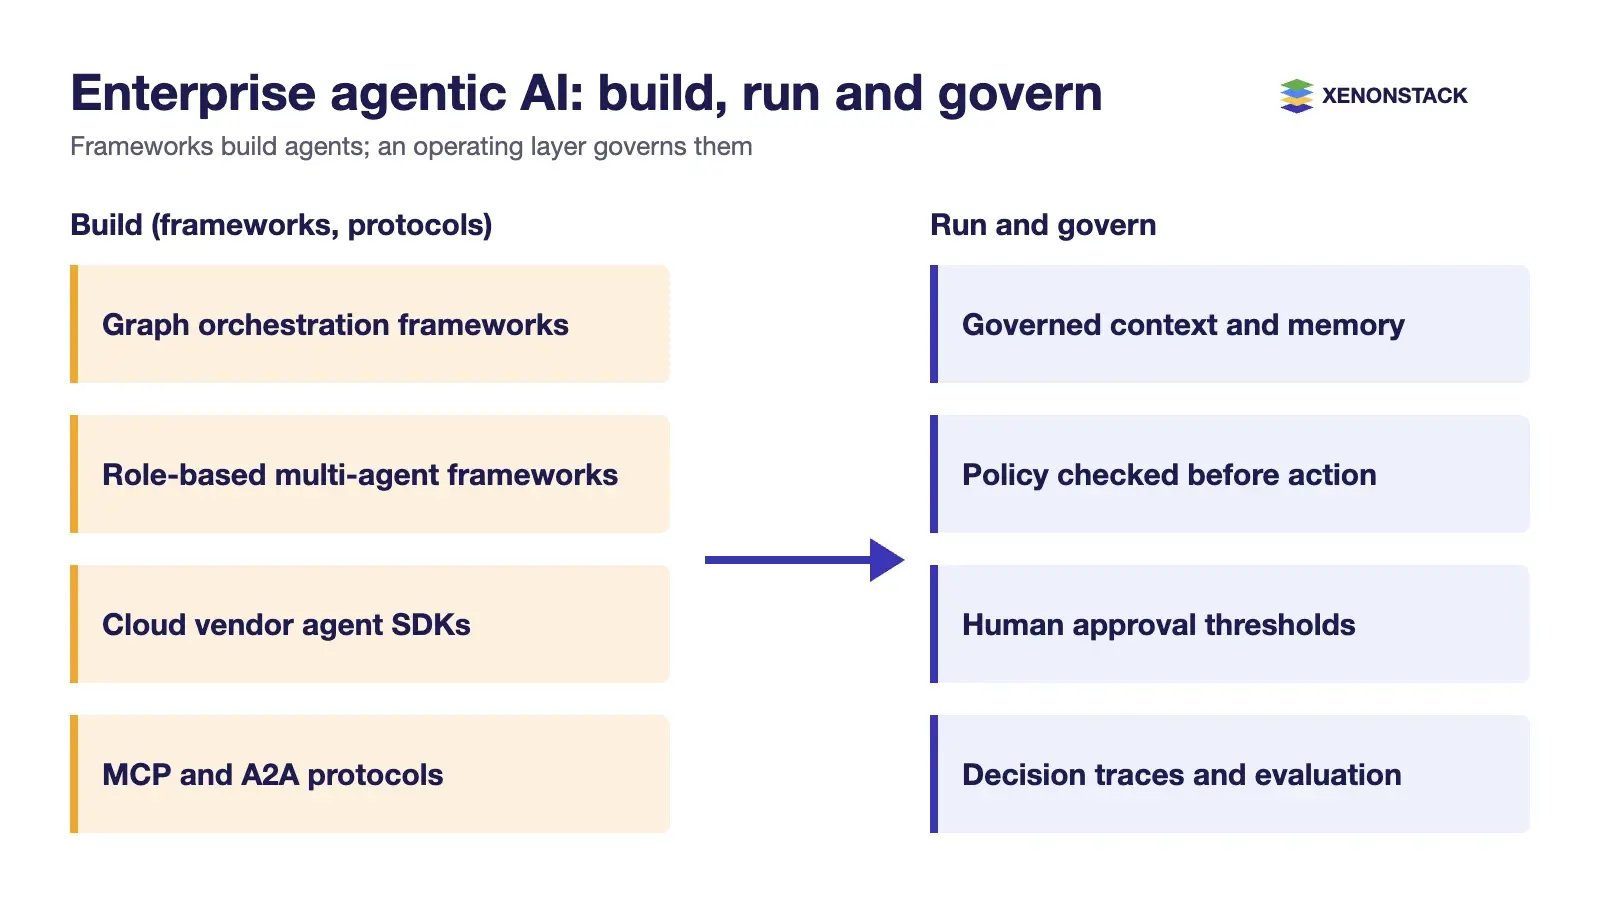
Most enterprise agent systems share six layers. Frameworks cover some of them; the rest is your platform and governance work.
Triggers and interfaces: a user request, a business event, a schedule or a message from another agent.
Reasoning: one or more models that plan, choose tools and judge results.
Context and memory: the business data, documents, prior decisions and policies the agent needs, with short-term and long-term memory.
Tools and integration: APIs, databases and applications, increasingly exposed through the Model Context Protocol (MCP).
Orchestration: workflows, hand-offs and multi-agent coordination, including agent-to-agent protocols such as A2A.
Governance and observability: identity, permissions, policy checks, human approvals, tracing, evaluation and cost control.
Where does it break?
Agent systems usually fail at the seams rather than in the model. Common points are stale or missing context, tools with broader permissions than the task needs, loops that run up cost, agents that pass errors to each other, and actions no one can explain afterwards. The trade-off is constant: more autonomy gives speed, but each extra step adds a point where the agent can go wrong. For patterns that keep this in check, see agentic workflow patterns and their governance.
Which categories of agentic AI frameworks exist today?
The market has settled into five categories. The options below are named as their own projects describe them in late 2026; check each project’s documentation before you commit, because releases move quickly.
| Category | What it gives you | Current options | Watch out for |
|---|---|---|---|
| Graph and state-machine orchestration | Explicit control flow, durable state, pause-and-resume for human approval | LangGraph (1.0 since October 2025) | More design work up front; you own the graph |
| Role-based multi-agent frameworks | Teams of agents with roles and tasks, plus a flow layer for state | CrewAI (Crews and Flows) | Fast to prototype; agent-to-agent behaviour can be hard to predict |
| Vendor agent SDKs | Agent loop, tools, hand-offs, guardrails and tracing tuned to one ecosystem | OpenAI Agents SDK; Google Agent Development Kit (ADK); Microsoft Agent Framework (1.0 in April 2026, successor to Semantic Kernel and AutoGen for new work); Strands Agents from AWS | Defaults favour the vendor’s models and cloud; check model portability |
| Managed agent runtimes | Hosted execution, memory, identity and monitoring for agents built with any framework | Amazon Bedrock AgentCore; Vertex AI Agent Engine | Cloud lock-in and data residency |
| Interoperability protocols | Standard ways to connect agents to tools and to each other | MCP and AGENTS.md under the Agentic AI Foundation; A2A at the Linux Foundation | Protocols move tools between frameworks, but not policy or accountability |
Frameworks help you build agents. Running many of them across an organisation needs a platform layer as well. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows. For a side-by-side view of multi-agent options, see multi-agent platforms and frameworks compared.
How should you choose an agentic AI framework?
Start from the decision the agent will make and the controls it needs, then pick the framework. Five questions settle most choices: does the work need durable, resumable state; where must a person approve; which models and clouds are you committed to; which languages does your team use; and how will you trace and evaluate every run?
| Choose | When |
|---|---|
| A graph or state-machine framework | The process runs for hours or days, needs explicit approval steps, or must be auditable step by step |
| A role-based multi-agent framework | You are exploring a problem quickly and the cost of a wrong step is low |
| Your cloud vendor’s SDK and runtime | You have standardised on that cloud and want managed identity, memory and monitoring |
| Microsoft Agent Framework | Your teams build in .NET or Python on Azure, or you are moving off Semantic Kernel or AutoGen |
| MCP and A2A at the edges, whatever the framework | You expect to swap models or frameworks, or need agents from different vendors to work together |
| No agent framework at all | The task is a single model call or a fixed workflow with no real decision |
What are the main enterprise use cases for agentic AI?
The strongest use cases share three traits: a clear goal, data the agent can reach, and a decision whose risk can be bounded. The table shows a sensible starting autonomy level for each.
| Function | What the agent does | Starting autonomy | Key control |
|---|---|---|---|
| IT operations | Triage alerts, correlate incidents, propose or run approved runbooks | Act on low-risk fixes; propose the rest | Runbook allow-list and change records |
| Customer service | Resolve routine requests across order, billing and account systems | Act within limits; hand off exceptions | Refund and credit thresholds |
| Finance operations | Match invoices, investigate exceptions, prepare close tasks | Recommend; a person approves | Segregation of duties |
| Risk and compliance | Collect control evidence, flag gaps, draft findings | Recommend | Evidence lineage and reviewer sign-off |
| Software delivery | Write tests, review changes, summarise failures | Act in non-production | Branch protection and review |
| Data and analytics | Answer business questions, build queries, explain results | Inform | Governed data access and metric definitions |
| Supply chain | Spot disruptions, re-plan orders, propose supplier changes | Recommend | Spend and contract limits |
Data access shapes every one of these. See data privacy with agentic AI for how to keep personal and sensitive data within bounds.
How do you govern agentic AI and manage its risk?
Governance for agents is about actions, not only outputs. Six controls cover most of the risk:
Identity per agent: each agent has its own credentials, so every action is attributable.
Least privilege: tools and data scoped to the task, not to the platform.
Policy before action: rules checked before a tool call executes, not reviewed afterwards.
Human approval thresholds: defined by value, risk and reversibility.
Decision traces: the context, policy version, reasoning and outcome recorded for each action.
Evaluation and monitoring: tests before release and drift, cost and error tracking in production.
Use recognised references. The OWASP Top 10 for Agentic Applications, released in December 2025, lists the main security risks specific to agents. In the EU, the AI Omnibus (Regulation (EU) 2026/1744, in force since 27 July 2026) moved obligations for stand-alone high-risk AI systems to 2 December 2027 and for AI in regulated products to 2 August 2028. Map each agent use case to these dates early. Our guide to responsible AI principles and governance covers the wider programme.
ElixirData provides governed context, versioned policy and decision traces in one decision layer above the agents, and AgentGRC supports AI governance, risk and compliance work.
Is it really agentic? How do you avoid agent washing?
Gartner warns of “agent washing”: vendors rebranding chatbots, AI assistants and scripted automation as agentic AI. It estimated that only about 130 of the thousands of vendors claiming agentic AI are genuine, and predicted that over 40% of agentic AI projects will be cancelled by the end of 2027 because of escalating costs and unclear business value (Gartner).
Ask every vendor, and every internal team, the same questions:
Does the system decide its own next step, or follow a fixed script with a model in one box?
Which tools can it call, with what permissions, and who granted them?
What happens when a step fails: does it recover, stop or carry on?
Can you show the decision trace for a past action, including the policy applied?
What business metric has moved in a live deployment, not a demo?
How should enterprises adopt agentic AI and measure success?
Adopt in four stages. First, pick one bounded decision with a named owner and measurable outcome. Second, run the agent in shadow or recommend-only mode and compare its decisions with people’s. Third, allow it to act within thresholds, with approvals above them. Fourth, widen scope only when the metrics hold. The operating discipline for this is covered in AgentOps for enterprise AI.
| Metric | What it tells you |
|---|---|
| Task completion rate | Share of goals met without a person stepping in |
| Decision agreement rate | How often the agent matches expert reviewers in shadow mode |
| Escalation and override rate | Whether thresholds are set at the right level |
| Policy violations blocked | Whether controls are working before actions execute |
| Cycle time and cost per task | Business value against model and tool spend |
| Trace completeness | Share of actions with a full, auditable decision record |
When is agentic AI not the answer?
Agentic AI is the wrong tool when the process is fixed and rule-based, when every run must give the same deterministic result, when the data the agent needs is poor or out of reach, or when no one will own its decisions. In these cases conventional automation, a single model call or a better process is cheaper and safer. Agents also add running cost: every extra reasoning step and tool call is paid for, so measure value per task before scaling.
To map one decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is an agentic AI framework?
An agentic AI framework is the code layer that runs an agent loop: it calls a model to plan, invokes tools and systems, keeps state and memory, coordinates several agents where needed, and exposes hooks for human approval and tracing. Examples by category include LangGraph and CrewAI for orchestration, and vendor SDKs such as the OpenAI Agents SDK, Google Agent Development Kit, Microsoft Agent Framework and Strands Agents.
How is agentic AI different from generative AI?
Generative AI produces content such as text, code or images in response to a prompt. Agentic AI uses models, often generative ones, to pursue a goal across several steps: it plans, calls tools and enterprise systems, checks the result and adjusts, within limits that people set.
Which agentic AI framework should an enterprise choose?
Choose by need rather than popularity. Use a graph-based framework such as LangGraph when you need durable state and explicit approval steps, a cloud vendor SDK when you are standardising on that cloud, a role-based framework such as CrewAI for fast multi-agent prototypes, and protocols such as MCP and A2A so that tools and agents stay portable whichever framework you pick.
What are MCP and A2A?
The Model Context Protocol (MCP) is an open standard for connecting agents to tools and data. It is now a project of the Agentic AI Foundation under the Linux Foundation. Agent2Agent (A2A) is an open protocol for agents to communicate with other agents, also hosted by the Linux Foundation.
What is agent washing?
Agent washing is Gartner’s term for vendors rebranding chatbots, AI assistants or scripted automation as agentic AI without real agentic capability. Gartner estimated that only about 130 of the thousands of vendors claiming agentic AI are genuine, and predicted that over 40% of agentic AI projects will be cancelled by the end of 2027.
How should agentic AI be governed?
Give each agent its own identity and least-privilege access, check policy before an action executes, require human approval above defined risk thresholds, and keep a decision trace for every action. Use the OWASP Top 10 for Agentic Applications for security risks, and map high-risk uses to the EU AI Act timeline.
When is agentic AI not the right approach?
Agentic AI is not the right approach when the process is fixed and rule-based, when every step needs the same deterministic outcome, when the data an agent would need is poor or inaccessible, or when no one can define who is accountable for its decisions. Conventional automation or a simple model call is often cheaper and safer.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE