Key takeaway
- Responsible AI in healthcare: the risks, HIPAA, FDA and EU AI Act rules, and the controls CIOs and architects need for clinical models and AI agents.
Responsible AI in healthcare means running clinical and operational AI so that its decisions can be explained, checked for bias, kept inside patient-privacy law and overseen by named clinicians. For a hospital, payer or health-technology vendor, the test is simple: when a model or an agent influences a patient outcome, can you show what it saw, which policy applied and who was accountable?
This guide is for CIOs, Chief AI Officers, CISOs, clinical informatics leads and architects. It covers the clinical risks, the rules that apply (HIPAA, FDA, the EU AI Act and WHO guidance), the controls that work and an adoption sequence. For the general principles see our responsible AI principles guide; for a customer-facing view see responsible AI in customer service.
Why is responsible AI different in healthcare?
A wrong recommendation in most industries costs money. In care delivery it can change a diagnosis or a treatment, so the standard for evidence, traceability and human oversight is higher. Healthcare data is also among the most sensitive an enterprise holds, and it is often unstructured (notes, images, scans), which makes bias and leakage harder to see.
Three questions come before any deployment. How far can clinicians rely on the output? How do we ensure the model is used only for its intended purpose? How do we know it does not perform worse for particular groups of patients? The rest of this guide turns these into controls.
What are the main risks of AI in healthcare?
| Risk | What it looks like in practice | Control to put in place |
|---|---|---|
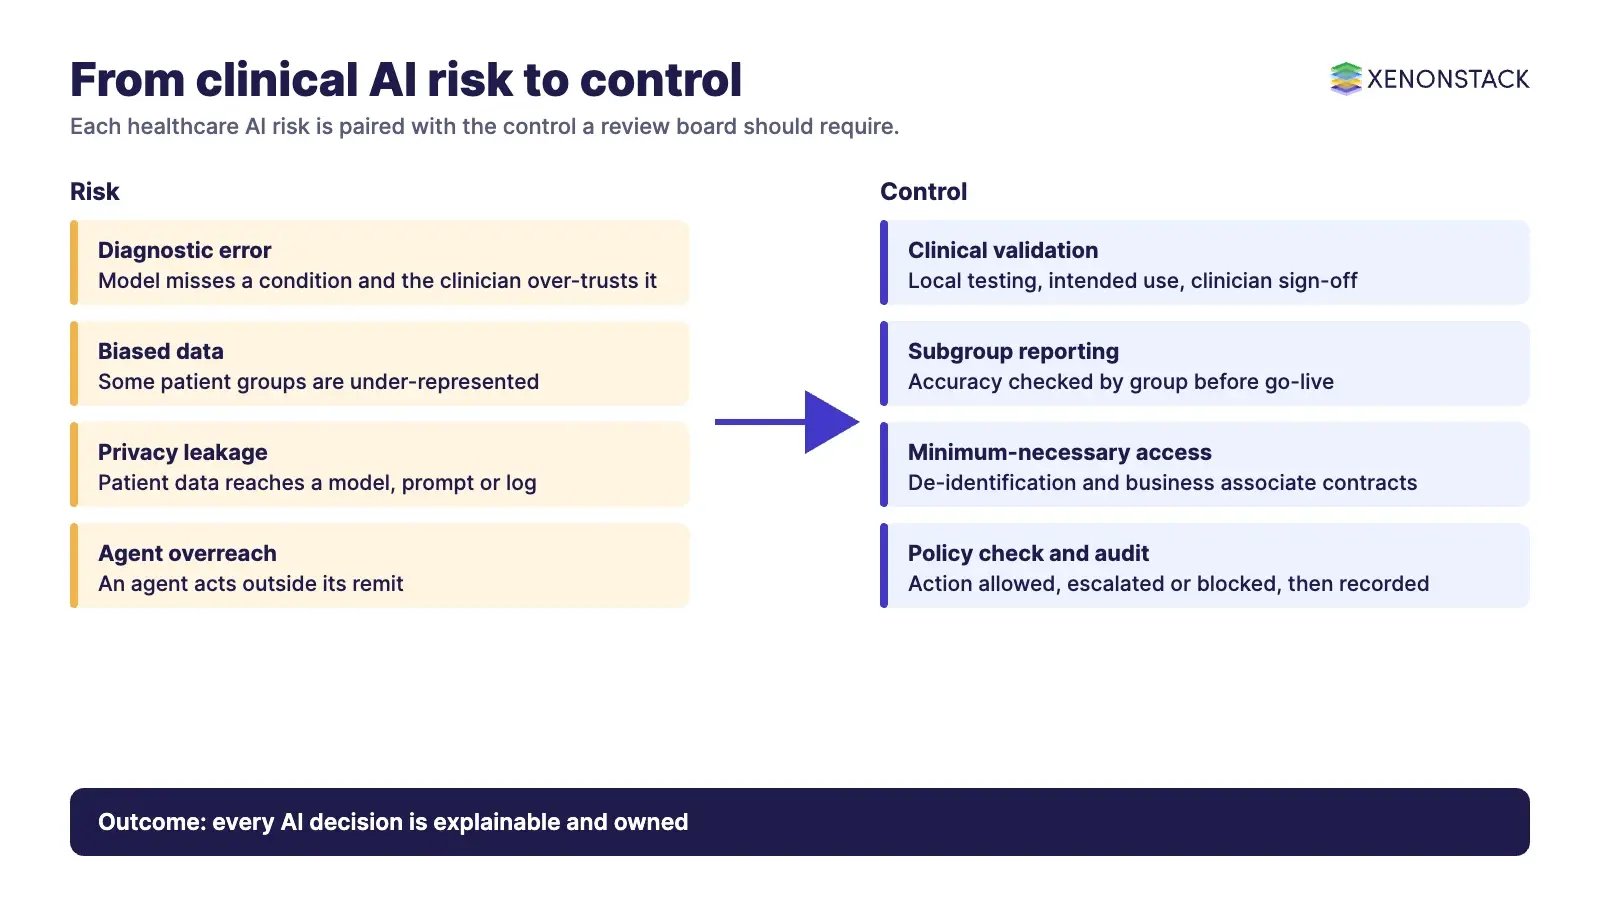
| Diagnostic error | A model misses or over-calls a condition, and the clinician over-trusts it | Clinical validation on local data, defined intended use, clinician sign-off on every recommendation |
| Biased or poor-quality data | Training data under-represents some patient groups, so accuracy differs between them | Subgroup performance reporting before go-live and on a schedule afterwards |
| Privacy and leakage | Protected health information reaches a model, a prompt or a log it should not | Minimum-necessary access, de-identification where suitable, contracts with business associates |
| Opacity | Nobody can explain why a score or a prior-authorisation decision came out as it did | Explainability methods and a stored record of inputs, model version and outcome |
| Model drift | Performance changes after a new scanner, coding change or patient mix | Monitoring with thresholds, retraining under change control |
| Agent overreach | An AI agent takes an action (scheduling, coding, messaging a patient) outside its remit | Policy checks before each action, escalation to a human, audit trail |
Data quality and bias
A model learns from the records it is given. If those records under-represent a population, or encode past unequal treatment, the model repeats it. The practical response is to measure accuracy by subgroup, not only overall, and to treat a gap as a release blocker. Our guide to ethical AI in healthcare and its principles covers the ethical framework in more depth.
Privacy and security
In the United States, the HIPAA Privacy Rule protects individually identifiable health information held by covered entities and their business associates. HHS states that de-identified information falls outside the Rule's use and disclosure limits, and that de-identification is achieved either by expert determination or by removing the specified identifiers (source: HHS HIPAA Privacy Rule summary). Any vendor that processes patient data for you on behalf of a covered entity needs a written business associate contract. Privacy-preserving techniques such as federated learning help when data cannot leave a site; see privacy-preserving AI and edge AI vs federated learning.
Which rules and guidance apply?
| Source | What it says | Where it fits | Status |
|---|---|---|---|
| HIPAA Privacy Rule (HHS) | Protects identifiable health information held by covered entities and business associates | Any AI that touches patient records in the US | In force |
| FDA list of AI-enabled medical devices | A resource identifying AI-enabled devices authorised for marketing in the US; FDA says it is not comprehensive | Checking whether a clinical AI product is an authorised device | Updated periodically; page modified 4 Sep 2026 |
| EU AI Act, Article 6(1) | An AI system is high-risk if it is a safety component of, or is itself, a product under Annex I legislation that needs third-party conformity assessment | AI in regulated products sold in the EU | Annex I obligations apply from 2 Aug 2028 as shown by the Commission's service desk |
| EU AI Act, Article 50 | Systems that interact directly with people must tell them it is AI, unless obvious | Patient-facing chat and voice agents | General application from 2 Aug 2026 |
| WHO, Ethics and governance of AI for health | Report with six consensus principles for AI that serves the public benefit | Policy baseline for health systems and ministries | Published 28 Jun 2021 |
| NIST AI RMF 1.0 | Govern, Map, Measure and Manage functions for AI risk | Internal risk programme structure | Released 26 Jan 2023 |
Sources: FDA, EU AI Act Article 6, Article 50, Article 113, WHO, NIST. Dates are as shown on those pages; have legal counsel confirm how they apply to your products.
What does a responsible AI programme in a hospital or payer look like?
Empower leadership
Name one accountable executive, often a Chief AI Officer or a chief medical information officer, and a review board that includes clinicians, compliance, security and a patient or ethics voice. Without a named owner, model decisions default to whoever built the tool.
Set principles, policy and training
Write down intended use for each model, who may override it and what must never be automated. Train clinicians on what the tool can and cannot do, including automation bias, where people accept a suggestion because it came from a machine.
Review end to end
Assess each use case before launch and after changes: data sources, subgroup results, failure modes and the clinical workflow around the output. Record the result so the next reviewer can see what was decided and why.
Build and test a response plan
Decide in advance how to pause a model, notify clinicians, review affected patients and report an incident. Rehearse it, as you would a downtime procedure.
How do you govern AI agents in clinical and administrative workflows?
Models that score or classify are being joined by agents that act: drafting notes, coding encounters, chasing prior authorisations, booking appointments. Each action needs a check against policy before it reaches a system of record, and a record afterwards. A decision layer such as ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
For compliance and quality teams, an evidence trail matters as much as the control. The ElixirData Audit Agent gathers decision records, policy versions, approvals and authority chains into evidence packages for auditors on request.
What the record should hold
- The inputs the model or agent used and the model version.
- The policy that applied and whether the action was allowed, changed, escalated or blocked.
- The clinician or staff member who reviewed or overrode it.
What are the benefits of responsible AI in healthcare?
- Less unintended bias: subgroup testing finds gaps before patients do.
- Transparency: explainable AI shows how an algorithm reached a result; see explainable AI. Common methods include LIME (Ribeiro, Singh and Guestrin, 2016) and SHAP (Lundberg and Lee, 2017).
- Privacy: sensitive data stays inside agreed boundaries.
- Faster approval: a documented review is easier for security, legal and clinical boards to sign off.
In what order should a health system adopt it?
- Inventory every AI tool in use, including those inside vendor products.
- Classify each by clinical risk and by whether it touches patient data.
- Set intended use, owner and override rules for the highest-risk tools first.
- Add subgroup testing and monitoring, then audit trails.
- Extend to agents with policy checks before action.
When is AI not the right answer?
Where there is no validated evidence for the use case, where the data cannot be made safe to use, or where a clinician cannot realistically review the output in the time available, hold back. A simpler rule or a manual step with a clear owner is better than an unexplained model.
AI can speed research, prevention, diagnosis and treatment, but people must govern it. To map one decision your clinical or administrative agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is responsible AI in healthcare?
It is the practice of building and running healthcare AI so that its results can be explained, tested for bias, kept within privacy law and overseen by accountable people.
Does HIPAA apply to AI tools?
Yes, where the tool handles identifiable health information for a covered entity or business associate. De-identified information is outside the Privacy Rule's use and disclosure limits, according to HHS.
Is a clinical AI product an FDA-authorised device?
Check the FDA's list of AI-enabled medical devices, which identifies devices authorised for marketing in the US. FDA states the list is not comprehensive, so confirm with the vendor as well.
How does the EU AI Act affect healthcare AI?
Under Article 6(1), AI that is a safety component of a regulated product, or is such a product, and needs third-party conformity assessment is high-risk. Patient-facing agents must also disclose they are AI under Article 50.
How should AI agents be governed in healthcare?
Check each action against policy before it happens, escalate uncertain cases to a person and keep a record of the inputs, the policy and the outcome.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE