Key takeaway
- Continuous compliance in DevOps: how to automate controls in CI/CD, keep audit evidence on every change, and govern AI agents, with NIST sources.
What is continuous compliance in DevOps?
Continuous compliance means checking, enforcing and evidencing your controls on every change, not once a year before an audit. Each commit, build, deployment and configuration change is tested against written policy, and the result is stored as evidence that an auditor can read later.
The reason to do it is speed with proof. A release process that ships daily cannot wait for a change advisory board to read documents. Compliance as code, covered in our guides to compliance as code and governance as code, moves the control into the pipeline so the check runs at the same pace as delivery.
Why do periodic audits fail in a continuous delivery model?
A periodic audit samples a system at one moment. In a cloud-native estate, where releases and infrastructure changes happen continuously, that picture can be out of date the next day. One release can expose an endpoint or loosen a permission and nobody sees it until the next review.
Documentation, sign-offs and change advisory boards were designed for slower release cycles. If the organisation already has risk controls, documentation and approvals, the better move is to automate them on each update so that safe release and agility come together. For the release side of this, see our guide to release engineering best practices.
What does the standards body say about continuous monitoring?
NIST SP 800-137, published on 30 September 2011, describes information security continuous monitoring as an ongoing programme that gives an organisation visibility into its assets, threats and vulnerabilities, and into how well its security controls work. Its stated aim is to keep controls aligned with the organisation's risk tolerance and to respond in time when a control falls short. NIST SP 800-53 Rev. 5 is the catalogue of security and privacy controls that most programmes map to, and NIST SP 800-218 (published 3 February 2022) sets out secure development practices that can be added to any software development life cycle.
On the tooling side, NIST OSCAL is a NIST-led initiative that describes security and compliance controls in machine-readable form, in XML, JSON and YAML. According to its page, it is intended to replace document-based security plans with structured data that tools can assess. Whether your regulator accepts such formats depends on the regulator, so confirm that with the relevant official page before you rely on it.
What are the best practices for continuous compliance?
| Practice | What it means in the pipeline | What the executive should ask |
|---|---|---|
| Agility and security as one goal | Compliance is designed in, so it speeds delivery rather than blocking it | Does a compliant release take less effort than a non-compliant one? |
| Compliance in the release cycle | Teams, including business owners, share one vocabulary for requirements before design starts | Who owns each requirement, and where is it written down? |
| Automated checks | Vulnerability scanning and policy checks run in CI/CD at build time | Which controls are still checked by hand? |
| Data classification | Data is classified, with policies per class, including encryption in transit and at rest | Do we know where our most sensitive data sits? |
| Access control audit | Access is given to roles and teams, not individuals; SSO and SAML avoid shared passwords; least privilege applies | Can we show who had access to what, and when? |
| Continuous auditing | Audits are automated, so they are predictable, measurable and repeatable | How old is the evidence we would hand an auditor today? |
How does compliance as code fit into the CI/CD pipeline?
Compliance as code uses programmatic methods to automate the implementation, validation, remediation, monitoring and reporting of the standards your organisation must meet. Start by listing the security standards, regulations and internal governance rules that apply, then turn each control into a precise, versioned rule.
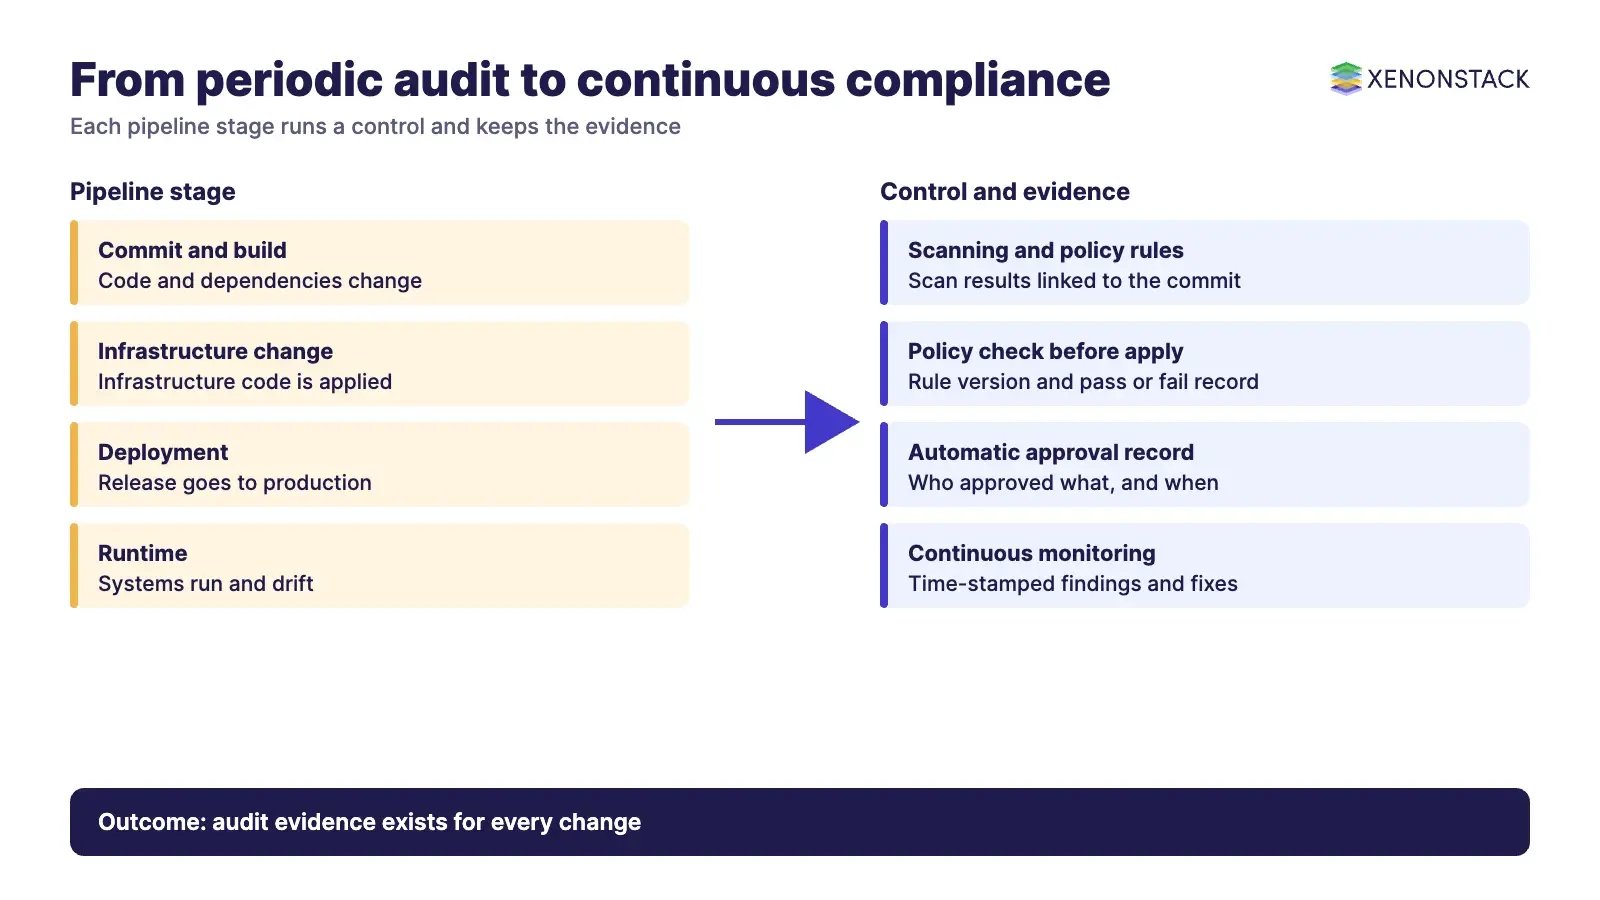
Once the rules sit in the pipeline, developers see the compliance status of every commit and fix issues early, and the security team sees problems at the start of the life cycle instead of at the end. Both teams finish sooner, and compliance status can be audited and reported continuously. For the infrastructure layer, see Infrastructure as Code security, automated remediation and continuous compliance and DevSecOps tools and governance.
| Pipeline stage | Example control | Evidence kept |
|---|---|---|
| Commit and build | Static and dependency scanning, policy rules on the change | Scan results linked to the commit |
| Infrastructure change | Policy checks on infrastructure code before apply | Rule version and pass or fail record |
| Deployment | Approval and change record attached automatically | Who approved what, and when |
| Runtime | Continuous monitoring of configuration and access | Time-stamped findings and fixes |
How do you measure whether continuous compliance is working?
Treat compliance signals like delivery signals. Our guide to DevOps metrics explains the DORA delivery measures, and compliance can sit beside them: how many controls are automated, how long a failed control stays open, and how old your newest evidence is. The same approach of agreed targets and error budgets from SRE versus DevOps suits compliance objectives too.
The 2025 DORA report describes AI as an amplifier that magnifies an organisation's existing strengths and weaknesses, with the greatest returns coming from the underlying organisational system. For compliance this means AI-assisted code and agents make a weak control process fail faster, so automated policy checks matter more as AI writes more code. More on the 2026 picture is in DevOps trends for 2026.
How do you govern AI agents inside a compliant pipeline?
As agents begin to act in delivery and operations, each agent action needs the same policy check and the same evidence as a human change. According to its site, ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents. AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need, and the Audit Agent is described as assembling decision lineage, policies and approvals into audit-ready evidence. Its page notes that full lineage is available only for decisions made through Context OS.
What is the adoption sequence, and when should you not automate?
| Step | Action | Watch out for |
|---|---|---|
| 1 | Pick one framework or regulation and read it on the official page | Do not rely on summaries from vendors or blogs |
| 2 | Map each control to an owner and a check | Controls with no owner stay manual |
| 3 | Automate the checks that are objective and repeatable | Judgement calls still need a person |
| 4 | Store evidence automatically with each run | Evidence that cannot be traced to a change has little value |
| 5 | Report status to leadership alongside delivery metrics | Avoid counting checks, count controls covered |
Do not automate a control you do not yet understand. Automating a poorly defined rule only produces failures faster. Keep human review for exceptions and for risk decisions.
To map one compliance decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is continuous compliance in DevOps?
It is the practice of checking and evidencing compliance controls on every change in the delivery pipeline, instead of at periodic audits.
Why are annual audits not enough for cloud-native delivery?
Releases and infrastructure change continuously, so a point-in-time audit can be out of date the next day.
What does NIST say about continuous monitoring?
NIST SP 800-137 describes information security continuous monitoring as an ongoing programme that gives visibility into assets, threats, vulnerabilities and control effectiveness.
What is NIST OSCAL?
According to NIST, OSCAL is a NIST-led initiative that describes security and compliance controls in machine-readable formats (XML, JSON and YAML).
How is compliance as code different from continuous compliance?
Compliance as code is the technique of expressing controls as code. Continuous compliance is the wider practice of enforcing and evidencing them on every change.
How should AI agents be handled?
Apply the same policy checks and evidence trail to agent actions as to human changes, as the 2025 DORA report notes that AI amplifies existing organisational strengths and weaknesses.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE