Key takeaway
- Amazon EKS security explained: shared responsibility, access entries, Pod Identity, network policy, encryption, supported versions and adoption order.
Amazon EKS security is a shared job. AWS runs and secures the Kubernetes control plane, including the control plane nodes and the etcd database. You secure everything that runs on it: identity and access, pod security, runtime, network, and the nodes you manage. The split moves towards AWS as you go from self-managed nodes to managed node groups, Fargate and EKS Auto Mode (source: EKS best practices guide).
This guide gives CISOs, platform leads and solution architects a decision-ready view: who owns what, the controls that matter in 2026 (access entries, Pod Identity, network policy, API endpoint access, encryption, logging), which Kubernetes versions are supported, and the order to adopt them. For the wider picture, see our posts on AWS security services and Kubernetes architecture and components.
Who is responsible for what in Amazon EKS?
AWS is responsible for security "of" the cloud: the managed Kubernetes control plane, the control plane nodes, the etcd database and the supporting infrastructure. You are responsible for security "in" the cloud, such as IAM, pod security, runtime security and network security. The amount you manage depends on the compute option you choose.
| Compute option | What AWS secures | What you still own |
|---|---|---|
| Self-managed nodes | Control plane | Most of the node infrastructure, including patching and the node image |
| Managed node groups | Keeps the EKS-optimised AMI patched with Kubernetes and security updates | Upgrading node groups to the latest AMI through the EKS API, CLI, CloudFormation or console; autoscaling tooling |
| AWS Fargate | Control plane, plus the underlying instance and runtime that run your pods | Pod configuration, identity, application security |
| EKS Auto Mode | Compute, networking, storage and network policy enforcement; OS, component and Kubernetes patching; nodes replaced within a 21-day maximum lifetime | Application containers, VPC infrastructure and EKS cluster configuration |
Sources: EKS best practices guide and EKS Auto Mode. Auto Mode nodes are immutable, with no SSH or SSM access, which removes a common node-level risk but also means node-level debugging must go through Kubernetes tooling.
Which EKS security controls matter most in 2026?
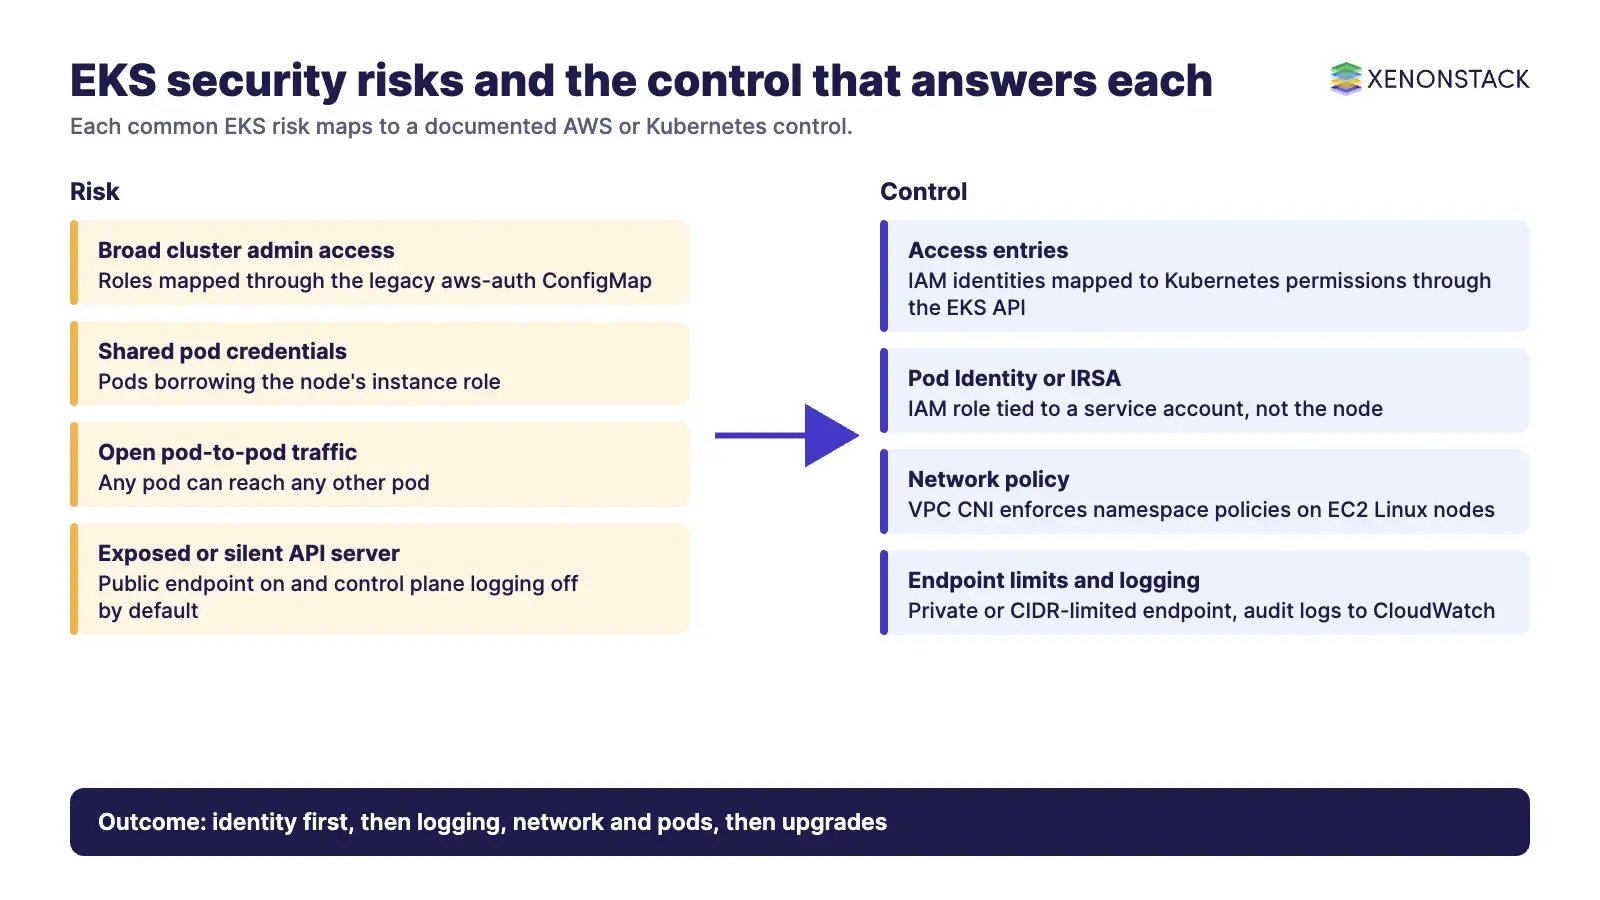
The AWS guide groups its recommendations into identity and access management, pod security, runtime security, network security, multi-tenancy, detective controls, infrastructure security, data encryption and secrets management, regulatory compliance, incident response and image security. The table below picks the controls an enterprise review should check first and states the current position of each.
| Control | What it does | Current status (as documented by AWS or Kubernetes) |
|---|---|---|
| Cluster access (access entries) | Maps IAM identities to Kubernetes permissions through the EKS API | Recommended way to give users Kubernetes API access; replaces the aws-auth ConfigMap method |
| Workload IAM (Pod Identity) | Gives pods IAM permissions through a service account association | Needs the Pod Identity Agent; not supported on Fargate or Windows nodes |
| Network policy | Controls pod-to-pod traffic at layers 3 and 4 | Built into the Amazon VPC CNI plugin from version 1.21.0; EC2 Linux nodes only |
| API endpoint access | Decides whether the Kubernetes API is reachable from the internet | New clusters start with the public endpoint on and the private endpoint off |
| Secrets and API data encryption | Envelope encryption of Kubernetes API data with KMS | On by default for clusters on Kubernetes 1.28 or later |
| Control plane logging | Sends audit and diagnostic logs to CloudWatch Logs | Disabled by default; enable each log type per cluster |
| Pod Security Standards | Three profiles: privileged, baseline, restricted | Applied per namespace by the Pod Security admission controller |
How should you control cluster access: access entries or the aws-auth ConfigMap?
Use access entries. AWS describes them as the recommended way to give users access to the Kubernetes API. An access entry links an IAM identity, such as an IAM role, to Kubernetes permissions. Permissions can come from AWS-maintained access policies or from a Kubernetes group that you bind with RBAC. The older aws-auth ConfigMap method is the legacy route.
To move a cluster across, change its authentication mode to API_AND_CONFIG_MAP, which keeps the ConfigMap method available alongside access entries, or to API, which uses only the EKS API. AWS states that choosing API disables the ConfigMap method permanently, and that you cannot change the mode back to one that removes the EKS API and access entries. When you enable access entries on a cluster that uses the ConfigMap, EKS creates an entry only for the identity that created the cluster, so you must create entries for the other roles yourself before you rely on API mode. Source: change authentication mode and access entries.
How do pods get AWS permissions safely?
EKS Pod Identity associates an IAM role with a Kubernetes service account. Pods that use that service account receive the role's credentials, so no long-lived keys sit in containers and pods do not borrow the node's instance role. Pod Identity needs no OIDC provider, and one trust policy principal, pods.eks.amazonaws.com, works across clusters. IAM roles for service accounts (IRSA) needs an OIDC identity provider and a trust relationship per cluster.
| Point | EKS Pod Identity | IRSA |
|---|---|---|
| Identity provider | Not needed | OIDC provider required |
| Trust policy | One principal works across clusters | Separate principal per cluster |
| Runs on | Linux EC2 worker nodes with the Pod Identity Agent (not needed in EKS Auto Mode) | Not covered on the AWS page read; check the IRSA documentation for your compute option |
| Ownership | Associations set in EKS, permissions in IAM | OIDC setup is often owned by a different team |
| Audit | Access and events logged in AWS CloudTrail | Not covered on the AWS page read |
Two cautions from AWS: Pod Identity is not supported on Fargate, Windows EC2 nodes, Outposts, EKS Anywhere or self-managed Kubernetes on EC2, and it is not a security boundary, because pods on one node share a kernel. Source: EKS Pod Identity.
How do you limit network exposure in EKS?
Restrict the API server endpoint
New EKS clusters have the public endpoint enabled and the private endpoint disabled. You can run public and private together, or private only. If you restrict public access to specific CIDR ranges, also enable the private endpoint, or make sure the ranges include the addresses nodes and Fargate pods use. Before you disable public access, confirm your kubectl principal is mapped in RBAC, otherwise you may lose access. Source: cluster endpoint access.
Segment pods with network policy
The Amazon VPC CNI plugin can enforce Kubernetes NetworkPolicy and cluster-wide admin policies from version 1.21.0. Standard policies are namespace scoped and work at layers 3 and 4. Policies apply to Amazon EC2 Linux nodes only, not to Fargate or Windows nodes, and only to the primary interface. If you already run a third-party enforcer such as Calico, AWS says to remove it before the VPC CNI manages the same policies, and recommends replacing the nodes that ran it. Source: network policy in the VPC CNI.
How should you harden pods, data and logging?
Pod Security Standards define three profiles: privileged (unrestricted, for trusted system workloads), baseline (blocks known privilege escalations) and restricted (follows current hardening practice, building on baseline). The Pod Security admission controller applies them to namespaces. Start with audit and warn on a namespace, fix what is reported, then enforce. Source: Kubernetes Pod Security Standards.
For data, clusters on Kubernetes 1.28 or later have envelope encryption enabled by default for all Kubernetes API data, such as ConfigMaps and Secrets, using an AWS owned key unless you bring your own customer managed key. If you use your own key, restrict who can administer it: AWS states that a disabled key degrades the cluster and a deleted key makes it unrecoverable. Source: envelope encryption.
For detection, turn on control plane logging. It is disabled by default and offers five log types: api, audit, authenticator, controllerManager and scheduler. Logs go to CloudWatch Logs and you pay CloudWatch ingestion and storage costs. Source: control plane logs.
Which Kubernetes versions on EKS are supported today?
Each Kubernetes minor version gets 14 months of standard support on EKS, then 12 months of extended support at an additional per-cluster-hour cost. Clusters still running a version when extended support ends are automatically upgraded. Unsupported versions are a security risk in themselves, so version currency belongs on the review list. Dates below are from the EKS Kubernetes release calendar, read on 12 November 2026.
| Kubernetes version | Amazon EKS release | End of standard support | End of extended support |
|---|---|---|---|
| 1.37 | 1 October 2026 | 1 December 2027 | 1 December 2028 |
| 1.36 | 2 June 2026 | 2 August 2027 | 2 August 2028 |
| 1.35 | 27 January 2026 | 27 March 2027 | 27 March 2028 |
| 1.34 | 2 October 2025 | 2 December 2026 | 2 December 2027 |
| 1.33 | 29 May 2025 | 29 July 2026 (passed) | 29 July 2027 |
| 1.32 | 23 January 2025 | 23 March 2026 (passed) | 23 March 2027 |
| 1.31 | 26 September 2024 | 26 November 2025 (passed) | 26 November 2026 |
Versions 1.37, 1.36, 1.35 and 1.34 are in standard support. Versions 1.33, 1.32 and 1.31 are in extended support, and 1.31 leaves it on 26 November 2026.
What order should you adopt EKS security controls in?
| Step | Action | Why first |
|---|---|---|
| 1 | Move cluster access to access entries; remove broad admin mappings | Identity decides who can change everything else |
| 2 | Enable control plane logging, at least audit and authenticator | You cannot investigate what was never recorded |
| 3 | Restrict the API endpoint; prefer private access or tight CIDRs | Shrinks the exposed surface |
| 4 | Replace node-level credentials with Pod Identity or IRSA | Removes shared instance-role permissions |
| 5 | Apply network policy by namespace, default deny first | Limits blast radius if a pod is abused |
| 6 | Roll out Pod Security Standards in audit and warn, then enforce | Prevents privileged pods |
| 7 | Plan version upgrades before standard support ends | Keeps patches flowing |
| 8 | Benchmark against CIS, then re-scan on every upgrade | Gives auditors an evidence trail |
The Center for Internet Security publishes benchmarks for Kubernetes (2.1.0), Amazon EKS (2.1.0) and EKS Auto Mode (1.1.0), as listed on the CIS Kubernetes benchmark page. Pick the one that matches your compute option and record accepted exceptions, because AWS runs the control plane and some checks will not be yours to change.
What are the trade-offs, and when is EKS Auto Mode not the answer?
Auto Mode reduces node patching and removes SSH access, but you give up direct node control. Customisation happens through custom NodePools and NodeClasses, and node-level services run as DaemonSets. Teams that need custom node images or host-level agents should check this fit first. Fargate removes node management too, but network policy and Pod Identity are not supported there, so you rely on other controls. Private-only API access is the safest setting but needs a connected network, a bastion or CloudShell for administrators. None of these choices is wrong; the right one depends on who must operate the nodes.
How does AI agent governance fit EKS security?
Many enterprises now run AI agents on Kubernetes. Each agent is a workload with an IAM role, and the cluster controls above decide what it can reach. They do not decide whether an action is allowed by policy or leave a decision record. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control. For the pipeline side, see DevSecOps on AWS and DevSecOps pipeline, tools and governance.
To map one decision your agents should make on EKS, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
What should you plan for in 2027?
The EKS release calendar sets four support dates in the first eight months of 2027 for the Kubernetes versions covered above. Each one is a deadline for an upgrade plan.
- 23 March 2027: extended support ends for Kubernetes 1.32.
- 27 March 2027: standard support ends for Kubernetes 1.35.
- 29 July 2027: extended support ends for Kubernetes 1.33.
- 2 August 2027: standard support ends for Kubernetes 1.36.
Source: EKS Kubernetes release calendar, read on 15 November 2026. Check it again before you schedule upgrades.
Frequently asked questions about Amazon EKS security
Who secures the Kubernetes control plane in Amazon EKS?
AWS secures the managed Kubernetes control plane, including the control plane nodes and the etcd database. You secure identity and access, pod security, runtime, network and the nodes you manage, and the split shifts towards AWS with managed node groups, Fargate and EKS Auto Mode.
Should I still use the aws-auth ConfigMap?
AWS recommends access entries for giving users access to the Kubernetes API. Moving a cluster to API authentication mode disables the ConfigMap method permanently, so create access entries for all needed roles first.
What is the difference between EKS Pod Identity and IRSA?
Pod Identity needs no OIDC provider and one trust policy principal works across clusters. IRSA needs an OIDC identity provider and a trust relationship per cluster. Pod Identity is not supported on Fargate.
Are Kubernetes Secrets encrypted by default on EKS?
Clusters on Kubernetes 1.28 or later have envelope encryption enabled by default for all Kubernetes API data, such as ConfigMaps and Secrets, using an AWS owned key unless you supply your own customer managed key.
Does the VPC CNI support Kubernetes network policy?
Yes, from Amazon VPC CNI version 1.21.0, on Amazon EC2 Linux nodes. Policies cannot be applied to Fargate or Windows nodes.
Are EKS control plane logs on by default?
No. Control plane logging is disabled by default, and you enable each log type per cluster. Logs go to CloudWatch Logs, which adds ingestion and storage cost.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE