Key takeaway
- ONAP explained for network and enterprise architects: the architecture, main components, current release status, Kubernetes deployment and when to use it.
ONAP, the Open Network Automation Platform, is an open-source project hosted by the Linux Foundation (LF Networking) that provides network automation functions for the orchestration, management and automation of network and edge computing services, according to its ONAP architecture documentation. Operators use it to design network services, orchestrate them across virtual network functions (VNFs) and other resources, and run closed-loop automation on top.
For a technology leader the useful question is no longer "what is ONAP" but "which parts are still maintained and which fit our network". The project now describes itself as a set of automation functions rather than one platform, and several older components are obsolete. This guide explains the architecture, the current status and when ONAP is, or is not, the right choice.
What does ONAP do?
ONAP separates the work into two environments. The design-time environment is, in the words of its documentation, a development environment with tools, techniques and repositories for defining resources, services and products, and for writing the policies and workflows that govern them. The run-time environment executes the rules and policies distributed from design time, which covers instantiation, configuration and lifecycle management of services.
Typical blueprints in the ONAP community cover use cases such as 5G network services. Treat these as starting points, not finished products: the project documents what each release supports, and each component has its own release notes.
What are the main ONAP components and what do they do?
The table below lists components named in the ONAP architecture documentation, with the role each one plays. Names and scope change between releases, so confirm the current list in the release notes before you plan a deployment.
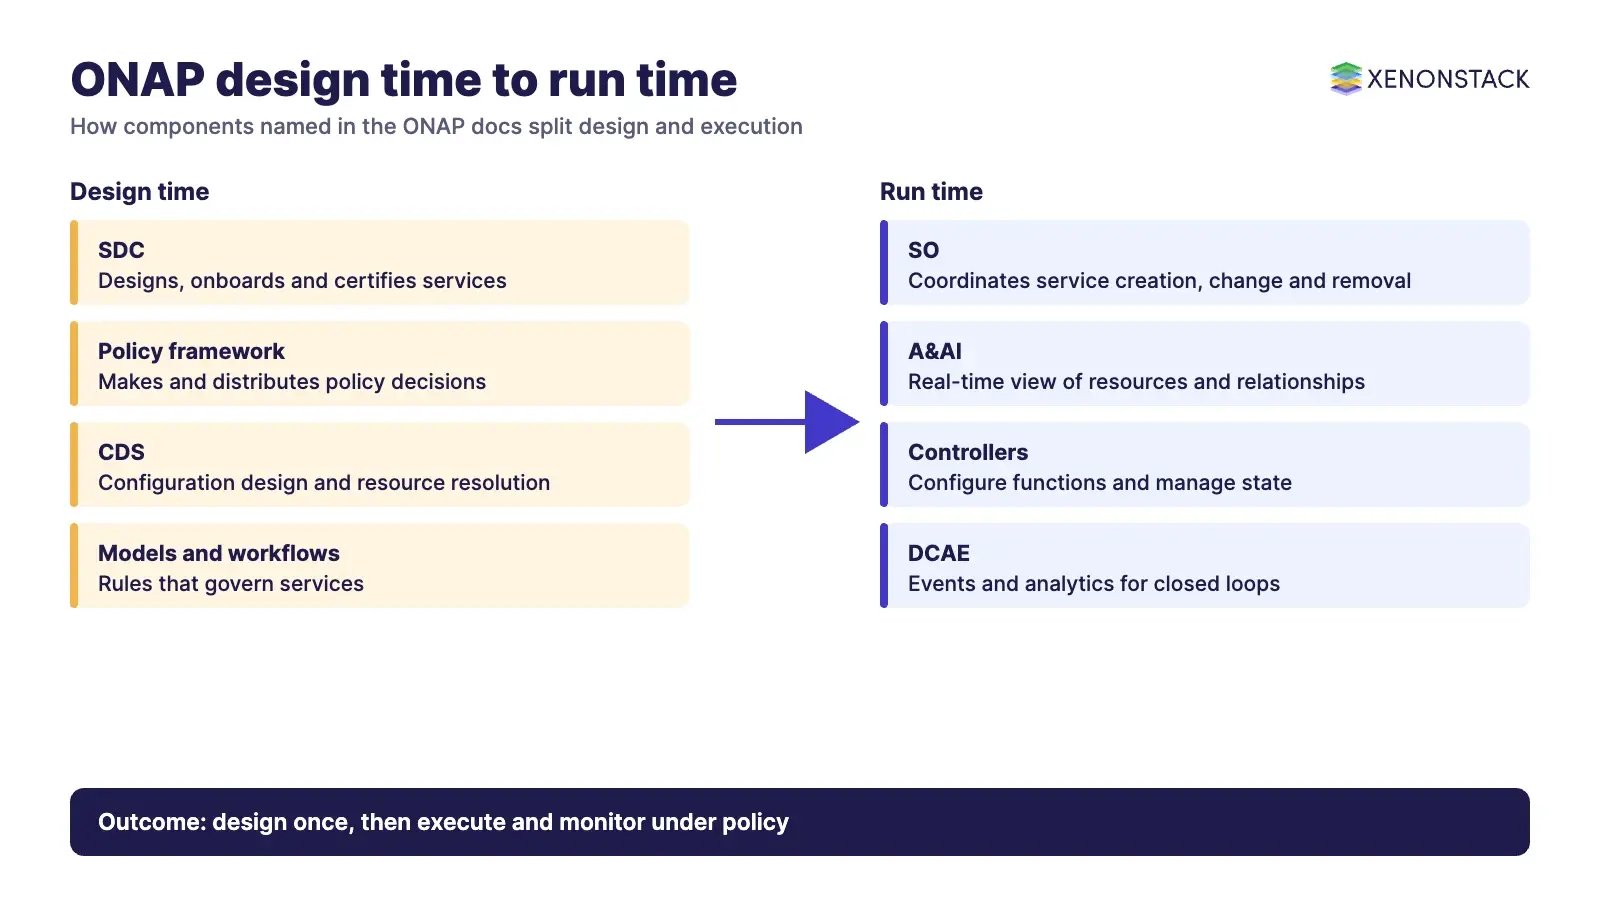
| Component | Role (according to the ONAP docs) | Environment |
|---|---|---|
| SDC (Service Design and Creation) | Designs, onboards and certifies resources, services and products | Design time |
| Policy framework (with CLAMP) | Makes policy decisions and distributes policies; CLAMP is now part of Policy | Design time and run time |
| SO (Service Orchestrator) | Coordinates end-to-end creation, change and removal of services and resources | Run time |
| A&AI (Active and Available Inventory) | Keeps real-time, metadata-driven views of resources, services and their relationships | Run time |
| Controllers (SDN-C, CDS) | Configure network functions and manage their state; CDS handles configuration design and resource resolution | Run time |
| OOF (Optimization Framework) | Runs policy-driven placement decisions | Run time |
| DCAE | Collects events and data, and hosts analytics applications that feed closed-loop automation | Run time |
| Multi-VIM/Cloud | Adapts several VIMs, clouds and Kubernetes clusters for workload deployment | Run time |
| VF-C | Provides NFVO and generic VNFM lifecycle management under ETSI NFV | Run time |
| Security framework | Uses Istio, Ingress, oauth2-proxy and Keycloak for secure communication, authentication and authorisation | Cross-cutting |
| OOM (ONAP Operations Manager) | Deploys and manages ONAP itself on Kubernetes | Deployment |
The same documentation says MSB, VID, APPC and AAF are obsolete or no longer deployed. If you are reading an older description of ONAP that depends on them, it describes an earlier architecture.
Why did operators need VNFs and software-defined networking?
Traditional network hardware bundles a data plane, which forwards traffic, with a control plane, which decides where traffic should go. Each device type carries its own control plane, so a network with routers, firewalls and WAN accelerators has many separate decision-makers to configure. Virtual network functions move a function such as a firewall or NAT from dedicated hardware to software, and software-defined networking separates control from forwarding. That makes functions easier to scale and change, but it also creates a lifecycle problem: someone has to design, place, configure, monitor and heal many software functions. ONAP is one open-source answer to that orchestration problem.
What is the current status of ONAP?
The ONAP release notes list Paris, version 16.0.0, released on 10 July 2025, as the latest release, with security work (HTTPS, removal of hard-coded passwords, non-root Kubernetes pods), Java 17 upgrades, and support for LLM-based generative AI and intent-driven networks among the key features. The page carries a "to be updated" marker and an inconsistent heading, so confirm the current release on the official page before you plan around it.
The LF Networking 2024 annual report article on ONAP (19 February 2025) adds context. It says ONAP has shifted from a single platform to a set of individual automation functions, that the NewDelhi release replaced MSB and DMaaP with Strimzi/Kafka and upgraded security with Istio and Keycloak, and that Deutsche Telekom ran an Argo CD based deployment of ONAP components as a proof of concept. It also states that CPS and the Policy Framework reached the OpenSSF Gold badge. We could not confirm release dates beyond Paris, and we did not find a statement of how many operators run ONAP in production, so we make no adoption claim.
| What | Where it stands | Source |
|---|---|---|
| Latest release | Paris 16.0.0, 10 July 2025 (confirm on the official page) | ONAP release notes |
| Positioning | A set of network automation functions, not one platform | ONAP architecture docs; LF Networking article |
| Obsolete components | MSB, VID, APPC, AAF | ONAP architecture docs |
| Security | HTTPS, no hard-coded passwords, non-root pods, Istio; CPS and Policy Framework at OpenSSF Gold | ONAP release notes; LF Networking article |
| Direction | Intent-based operation, generative AI, secure software supply chain | LF Networking article |
How is ONAP deployed?
ONAP is built as microservices and runs on Kubernetes. According to its architecture documentation, OOM is the lifecycle manager: it uses Kubernetes to handle deployment with dependency management, unified configuration, health monitoring, automatic restarts, scaling, upgrades and deletion, and it provides mTLS between components through Istio. The documentation also says individual components can be deployed through a continuous delivery tool of your choice, which is how the Argo CD proof of concept above fits in.
Operationally, that means ONAP inherits the skills your team needs for Kubernetes. If you are new to it, start with our guides to Kubernetes architecture and Helm. Do not rely on old one-line install commands from earlier ONAP guides; follow the installation guide for the release you choose.
How should an enterprise adopt ONAP?
A sensible sequence limits risk and makes the scope visible:
- Pick one service. Choose a single network service or use case, such as a virtual CPE or a 5G slice, and write the closed-loop outcome you want.
- Select only the components you need. Because ONAP is now a set of functions, a smaller footprint (for example SDC, SO, A&AI, a controller and Policy) is easier to run than the full set.
- Stand up a lab on the chosen release. Use OOM on a Kubernetes cluster and read the component release notes for known issues.
- Add security from day one. Use the Istio and Keycloak based security framework and keep ONAP in the same DevSecOps pipeline as your other platforms.
- Prove closed-loop control with humans in the loop before any automated action changes live traffic.
What are the trade-offs, and when should you not use ONAP?
| Situation | Fit | Why |
|---|---|---|
| Large operator with its own platform team and a multi-vendor network | Good fit | Open interfaces and the design-time and run-time split suit multi-vendor orchestration |
| Small network or a single-vendor stack with its own orchestrator | Weak fit | The operating cost of a Kubernetes-hosted set of components is high for a small scope |
| Need for a single supported product with one vendor SLA | Check first | ONAP is a community project; support comes from the community or a commercial distributor |
| Plan built on MSB, APPC, VID or AAF | Replan | The architecture documentation lists them as obsolete or not deployed |
Be honest about effort. ONAP is powerful but broad, and its documentation describes continuing work to make components more modular and independent. Budget for integration, upgrades and skills, not only for the first deployment.
How does agentic AI relate to ONAP?
ONAP itself points in this direction: the release notes mention LLM-based generative AI support and intent-driven networks, and the LF Networking article lists generative AI and open-source LLMs among its 2025 goals. The governance question follows. When an agentic workflow proposes a network change, someone must be able to show which policy allowed it and what context it used. Our own view is that this belongs in a decision layer above the agents: ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. For the wider 5G picture, see our guide to AI in 5G networks.
To map one network automation decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What does ONAP stand for?
ONAP stands for Open Network Automation Platform. It is an open-source project hosted by the Linux Foundation under LF Networking.
What is ONAP used for?
According to its documentation, ONAP provides network automation functions for the orchestration, management and automation of network and edge computing services, with design-time and run-time environments.
Is ONAP still maintained?
Its release notes list Paris 16.0.0, released on 10 July 2025, as the latest release, and the LF Networking article describes ONAP as actively developed. Confirm the current release on the official page.
Does ONAP run on Kubernetes?
Yes. According to the architecture documentation, OOM uses Kubernetes to deploy and manage ONAP components, and components can also be deployed through a continuous delivery tool of your choice.
Which ONAP components are obsolete?
The architecture documentation says MSB, VID, APPC and AAF are obsolete or no longer deployed.
Is ONAP a single platform?
The LF Networking article says ONAP is no longer a platform but a set of individual network automation functions that can be adopted selectively.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE