Key takeaway
- Agentic AI in banking runs onboarding, KYC, fraud and reconciliation work within set limits. See use cases, controls, SR 26-2, DORA and EU AI Act duties.
Agentic AI in banking and finance means AI agents that pursue a goal across several steps, such as onboarding a customer, preparing a credit file, triaging a fraud alert or reconciling accounts, and act inside limits the bank sets. The value is not the model alone. It is the agent working across systems, handling exceptions and handing the hard calls to a person with the evidence already assembled.
For a regulated institution, the deciding question is control. Every agent action needs a policy behind it, a named owner, and a record an auditor can replay. This guide covers the use cases that suit agents first, a reference architecture, the rules that apply in 2026 (SR 26-2 in the US, DORA and the EU AI Act in Europe), the audit trail you need, and when agents are the wrong tool.
What is agentic AI in banking, and why does it matter now?
Banks have automated for decades. Rules engines and robotic process automation (RPA) move data between systems along fixed paths. They work well until an input changes shape, a document is missing or a case needs judgement. Then the work drops into a queue for a person.
An agent is different in three ways. It reads unstructured inputs such as documents, emails and notes. It plans the next step rather than following one script. And it can call tools, such as a core banking API, a sanctions screening service or a case management system, to complete the task. That makes agents suited to the exception-heavy middle of banking operations, where most manual effort sits today.
| Approach | How it works | Best fit in banking | Main limit |
|---|---|---|---|
| Rules engine | Fixed if-then logic | Limits, eligibility checks, routing | Breaks on inputs it was not written for |
| RPA | Scripted clicks and data moves between screens | Stable, high-volume back-office steps | Fragile when screens or formats change |
| Single AI agent | Plans and calls tools towards one goal | Document-heavy tasks with clear outcomes | Needs guardrails, evaluation and logging |
| Multi-agent workflow | Several agents with distinct roles and hand-offs | End-to-end processes such as onboarding or AML case work | More moving parts to test, monitor and explain |
Why now? Three things have changed. Models can now read financial documents and call tools reliably enough for supervised production use. Supervisors have updated their expectations: the Federal Reserve, OCC and FDIC replaced SR 11-7 with SR 26-2 in April 2026, and EU firms are working under DORA. And boards are asking for productivity gains in operations without adding operational or conduct risk.
Rapid Market Growth
The global market for AI agents in financial services was an estimated USD 845 million in 2025, according to MarketsandMarkets.
Forecasted Expansion by 2032
MarketsandMarkets projects the market will reach USD 9,450 million by 2032, a compound annual growth rate of 41% from 2026 to 2032.
Which banking and finance use cases suit agents first?
Start where the work is high-volume, document-heavy and already well controlled. The agent does the gathering, checking and drafting. A person keeps the decision where the rules or the risk require it.
| Use case | What the agent does | Where a person stays in the loop | Key control |
|---|---|---|---|
| Customer onboarding and KYC | Extracts identity and company data, checks registries, flags gaps, requests missing documents | Approval of high-risk or complex customers | Data access limited to the case; every check logged |
| AML alert triage | Gathers transaction history, screening hits and prior cases; drafts a case narrative | Decision to escalate or file a suspicious activity report | Evidence pack attached to every recommendation |
| Fraud operations | Reviews flagged transactions, contacts the customer through approved channels, closes clear false positives | Account blocks and refunds above a threshold | Action limits per agent and per customer |
| Credit file preparation | Collects financials, spreads statements, checks covenants, drafts the credit memo | The credit decision itself | Validated scoring model; agent never sets the score |
| Reconciliation and close | Matches ledger to bank and sub-ledger data, explains breaks, proposes adjusting entries | Posting of entries above a materiality limit | Maker-checker on every posting |
| Accounts payable and receivable | Matches invoices to purchase orders, chases overdue items, routes exceptions | Payment release outside policy | Segregation of duties enforced by the platform |
| Regulatory and management reporting | Pulls data from source systems, checks consistency, drafts commentary | Sign-off by the report owner | Lineage from each figure back to its source |
Customer-facing advice and automated credit decisions on individuals come later, if at all. They carry the highest conduct and regulatory risk, and in the EU credit scoring of individuals falls into the high-risk category described below. Service agents that answer and route customer requests are a separate track, covered in how agentic AI is changing customer service.
What does a governed architecture for banking agents look like?
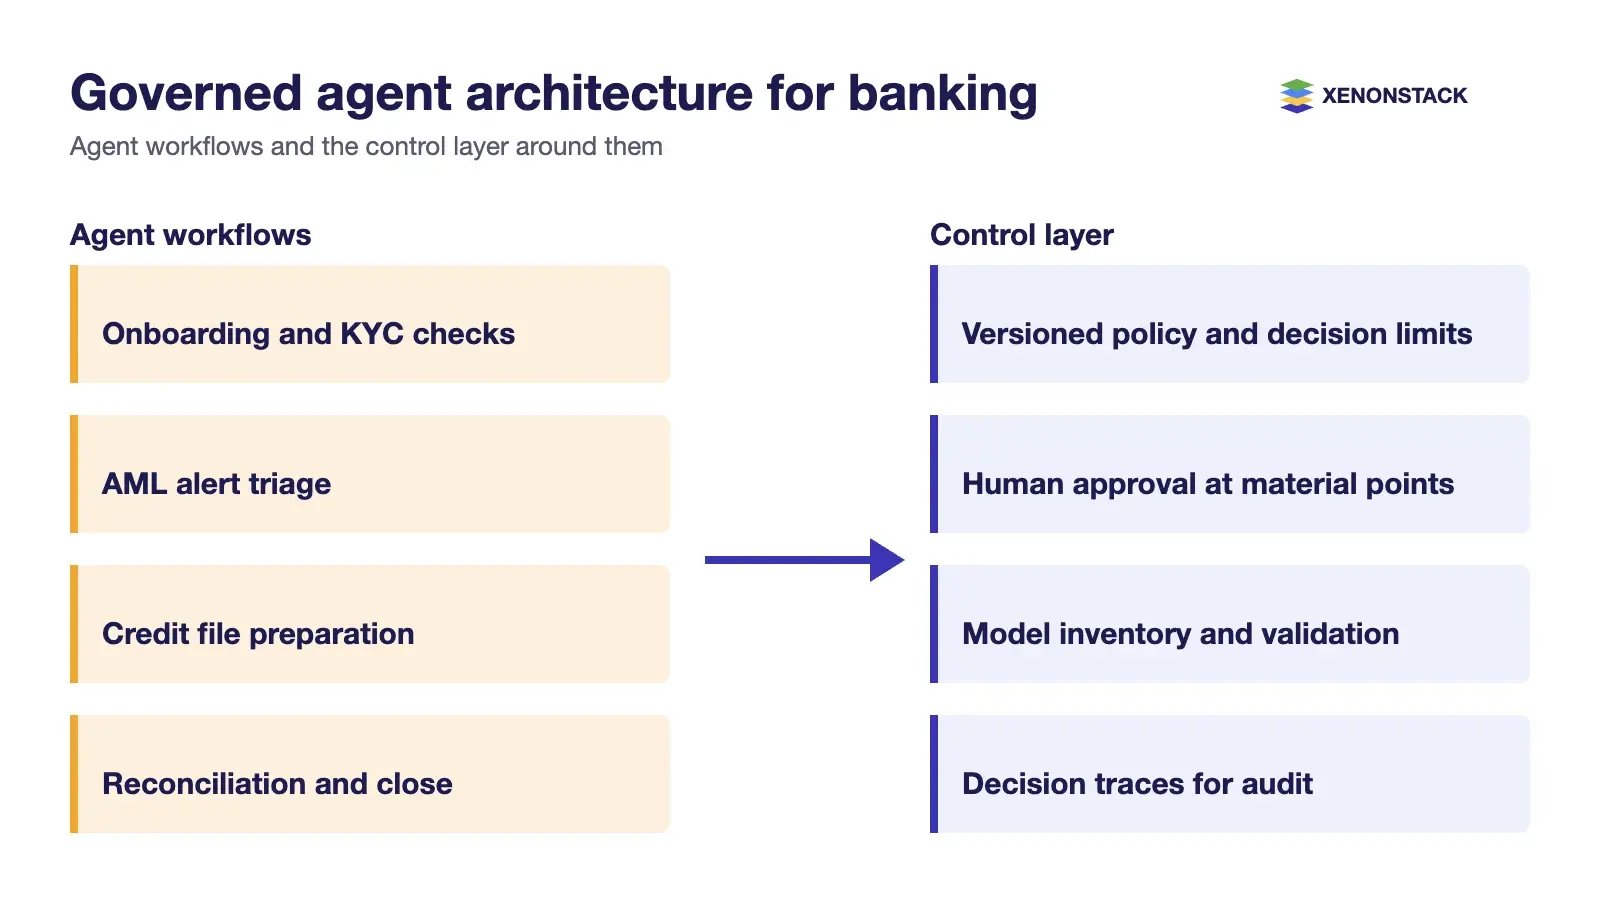
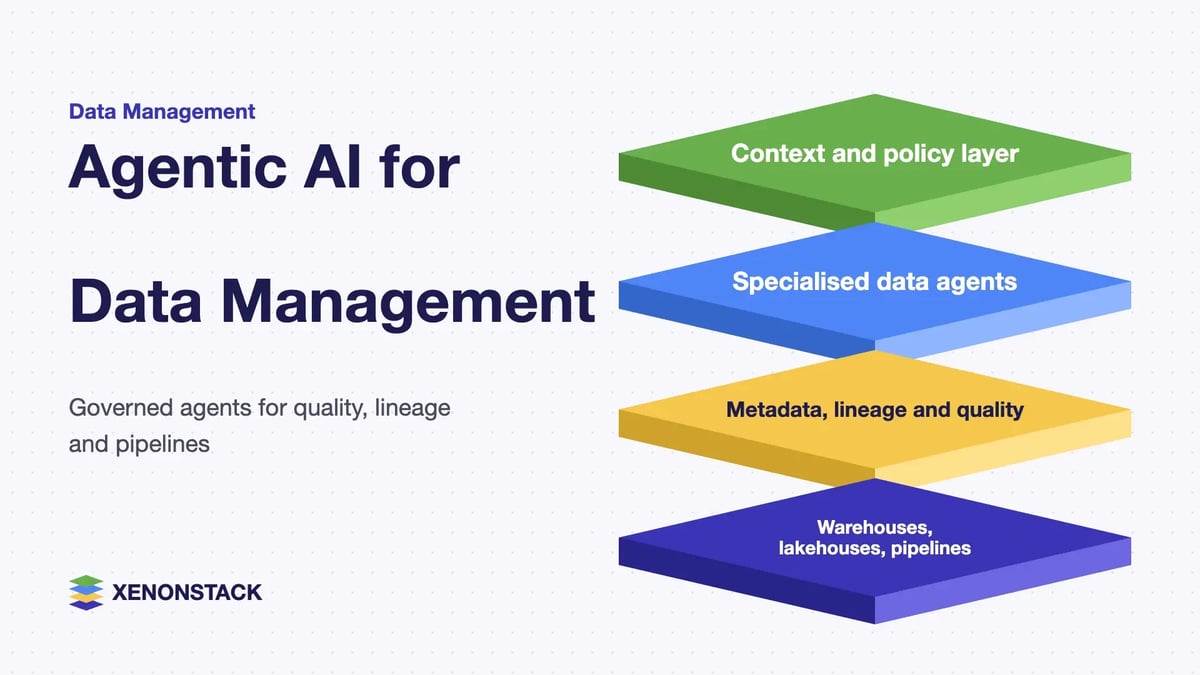
A bank-grade agent system has four layers. Each one has an owner, and each one is a place where things can go wrong.
1. Data and context layer
Agents need customer, account, transaction, ledger and risk data with known quality and lineage. If two agents read different versions of a customer record, their decisions will conflict. A governed context layer gives every agent the same entitled view, and records which data each decision used.
2. Agent and workflow layer
This is where agents plan, call tools and hand work to each other. Keep each agent narrow: one for document extraction, one for screening, one for drafting the case narrative. Narrow agents are easier to test, monitor and explain to a model risk team.
3. Policy and control layer
Decision boundaries live here: what an agent may do alone, what needs approval, and what it must never do. Limits should be versioned policy, not prompt text. Human approval steps, segregation of duties and per-agent permissions are enforced here, outside the model.
4. Observability and audit layer
Every input, tool call, policy check, approval and output is recorded as a decision trace. This layer serves operations (is the agent healthy?), model risk (is it performing as validated?) and audit (can we reconstruct what happened?). For the monitoring side, see our guide to agentic observability for autonomous AI systems.
Where it breaks
The common failure points are integration with legacy core systems, agents granted broader system access than the task needs, limits written only in prompts, and logs that capture the final answer but not the steps. Each of these is a design choice, and each can be fixed before go-live.
Which rules apply: SR 26-2, DORA and the EU AI Act?
No single rulebook covers banking agents. Three frameworks shape most designs in 2026.
| Framework | Status | What it means for agents |
|---|---|---|
| SR 26-2, Revised Guidance on Model Risk Management (Federal Reserve, OCC, FDIC) | Issued 17 April 2026; replaces SR 11-7 and SR 21-8 | Risk-based model inventory, validation, ongoing monitoring and vendor model oversight. Generative and agentic AI are stated to be out of its scope, so banks must govern agents under their wider risk management, while the statistical and non-generative models that agents call stay in scope. |
| DORA, Regulation (EU) 2022/2554 | Applies since 17 January 2025 | Agents are ICT systems. ICT risk management, incident classification and reporting, resilience testing, and third-party risk rules apply, including the register of information for ICT providers such as model and platform vendors. |
| EU AI Act, Regulation (EU) 2024/1689, as amended by the Digital Omnibus on AI, Regulation (EU) 2026/1744 | Annex III high-risk obligations apply from 2 December 2027 | AI used to evaluate the creditworthiness of individuals or set their credit score is high-risk (Annex III, point 5(b)); fraud detection is excluded. High-risk systems need risk management, data governance, automatic logging, human oversight and documentation. |
Two practical points follow. First, the SR 26-2 scope exclusion does not mean agents are unregulated in the US. It means the bank must decide and document how it governs them. Most banks extend their model risk disciplines to agents rather than invent a parallel process. Second, an EU agent that only prepares a credit file may still feed a high-risk decision. Map the whole decision, not just the agent, to see which obligations apply. Confirm interpretations with your legal and compliance teams.
What controls and audit trail should a bank put around agents?
The aim is simple: any decision an agent touched can be explained and replayed later, by someone who was not there.
- Agent inventory. Each agent has an owner, a purpose, the models and tools it uses, its data access and its risk tier. Treat it like a model inventory entry.
- Decision boundaries as versioned policy. Limits on amounts, customer segments and actions are held as policy with versions and approvals, so you can show which rule applied on a given date.
- Least-privilege access. Agents get only the data and system rights the task needs, with separate credentials per agent.
- Human approval at material points. Approvers see the evidence and the agent's reasoning, not just a yes or no button.
- Pre-release evaluation. Test agents against historical cases, edge cases and adversarial inputs before go-live, and after every model or prompt change.
- Ongoing monitoring. Track accuracy, override rates, escalations and drift. Set thresholds that pause an agent automatically.
- Complete decision traces. Record inputs, data versions, tool calls, policy checks, approvals and outputs, with timestamps, retained in line with your record-keeping rules.
These controls map to existing expectations: model inventory and validation from SR 26-2, ICT risk and incident logging from DORA, and logging and human oversight from the EU AI Act. Building them once, at the platform level, is cheaper than retrofitting each agent. For a wider control set, read controls and a framework for agentic AI risk management.
Should you use rules, a single agent or a multi-agent workflow?
| Choose | When | Example |
|---|---|---|
| Rules engine or RPA | The path is fixed, inputs are structured and exceptions are rare | Standing order processing, field-to-field data transfer |
| Single agent with human approval | Inputs are unstructured but the outcome is clear and bounded | Invoice matching with exceptions, document checks in onboarding |
| Multi-agent workflow | The process spans teams, systems and several decisions | AML case investigation, end-to-end commercial onboarding |
| Validated statistical model, no agent | The output is a score or estimate that drives a regulated decision | Probability of default, credit scoring |
| People, supported by search and summaries | The decision is rare, novel or carries high conduct risk | Complex restructuring, complaints with legal exposure |
How should a bank adopt agentic AI, and what should it measure?
- Pick one decision. Choose a workflow with clean data, a clear owner and an outcome you already measure, such as reconciliation breaks or onboarding document checks.
- Map the context and policy. List the data the decision depends on, who may approve what, and the limits that apply.
- Run in shadow mode. Let the agent work alongside people without acting, and compare results.
- Go live with approval gates. Release with a person approving each material action, then widen the agent's limits as evidence builds.
- Reuse the platform. Add the next workflow on the same context, policy and audit layers.
| Metric | What it tells you |
|---|---|
| Cycle time per case | Whether the agent removes waiting and hand-offs |
| Straight-through rate | Share of cases completed within policy without manual rework |
| Human override rate | How often approvers disagree with the agent; a rising rate signals drift |
| Error and loss events | Operational risk impact, reported through existing incident processes |
| Audit findings | Whether decision traces satisfy internal audit and supervisors |
Enhanced Operational Efficiency
Agentic AI will automate repetitive tasks like data extraction and report generation. Accenture estimates that early adopters of generative AI in banking could raise productivity by 22% to 30% over three years. This allows banks to allocate resources more effectively and concentrate on higher-value activities.
Personalized CX
Financial institutions will utilize agentic AI to deliver tailored services, such as personalized financial advice and customized product recommendations. AI-driven chatbots will also enhance customer support, improving overall satisfaction.
Advanced Risk Management
Agentic AI will enhance risk assessment and fraud detection by analyzing large datasets in real-time. This will enable banks to identify suspicious transactions and evaluate creditworthiness more accurately, reducing financial losses and ensuring regulatory compliance.
Revenue Growth and Innovation
McKinsey estimates that generative AI could add $200 billion to $340 billion in value to global banking each year. This technology will drive efficiency and foster innovation in product development and service delivery, helping banks remain competitive in a changing market.
When is agentic AI not the answer?
Agents are the wrong tool when a deterministic rule does the job, because a rule is cheaper, faster and easier to explain. They are also wrong where data is poor or fragmented, since an agent will act confidently on bad inputs. Avoid letting agents set credit scores or make final decisions on individuals unless the system meets high-risk requirements and your model risk function has signed it off. And do not deploy agents where no one owns the outcome. If you cannot name the person accountable for an agent's decisions, the agent is not ready.
Where do ElixirData and ElixirClaw fit?
In financial services, agents must act on data that can be traced and stay within limits risk and compliance teams control. ElixirData provides governed context, versioned policy and decision traces in one decision layer above the agents. ElixirClaw is an agentic OS platform to build, orchestrate, and govern AI agents and automation workflows. XenonStack's wider work for the sector is summarised on the agentic AI for financial services page. For control testing and evidence collection, AgentGRC supports governance, risk and compliance teams.
To map one decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is agentic AI in banking and finance?
It is the use of AI agents that pursue a goal across several steps, such as onboarding, AML alert triage, credit file preparation or reconciliation, and act within limits the bank sets, handing material decisions to a person.
How is agentic AI different from RPA in banking?
RPA follows fixed scripts to move data between systems. An agent reads unstructured inputs, plans the next step and calls tools, so it can handle exceptions that would otherwise drop into a manual queue.
Does SR 26-2 cover AI agents?
SR 26-2, issued on 17 April 2026 by the Federal Reserve, OCC and FDIC, replaces SR 11-7. It states that generative and agentic AI are outside its scope, so banks must govern agents under their wider risk management, while the models agents call remain in scope.
Is credit scoring by AI high-risk under the EU AI Act?
Yes. AI used to evaluate the creditworthiness of individuals or set their credit score is listed as high-risk in Annex III, point 5(b), with fraud detection excluded. After the Digital Omnibus on AI, these obligations apply from 2 December 2027.
How does DORA apply to AI agents?
DORA has applied since 17 January 2025. Agents are ICT systems, so ICT risk management, incident reporting, resilience testing and third-party risk rules, including the register of information for providers, apply to them.
What audit trail do banking agents need?
A complete decision trace: inputs, data versions, tool calls, policy checks, approvals and outputs with timestamps, so any decision an agent touched can be explained and replayed later.
Where should a bank start with agentic AI?
Start with one decision that has clean data, a clear owner and a measured outcome, such as reconciliation or onboarding document checks. Run in shadow mode, go live with approval gates, then reuse the same platform.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE