Key takeaway
- Governance as code turns cloud security, cost and compliance rules into versioned policy checks, run from Terraform plans to AI agent actions.
What is governance as code?
Governance as code is the practice of writing your cloud rules for security, cost, availability and compliance as versioned, testable code that is enforced automatically, instead of as documents that people check by hand. It extends Infrastructure as Code from "how the estate is built" to "what the estate is allowed to do".
For a CIO or platform lead the point is control without a queue: every change is checked against the same rules at the same stage, and the result is recorded. This post covers the governance layer across cloud and AI agents. For the policy language itself see our guide to policy as code, and for audit evidence see compliance as code.
Why does manual cloud governance fail?
A security team that reviews a web application or cluster by hand finds loopholes late, because the cloud estate changes faster than a review cycle. Spreadsheet standards drift from what is deployed, and each team reads them differently. Infrastructure as Code made builds repeatable, but it does not by itself check that what is built meets security, cost or compliance standards.
Governance as code closes that gap in the same way the DevOps operating model closed the build gap: the rule is written once, kept in version control, reviewed like any other change and run on every change.
Where do governance rules run in the delivery path?
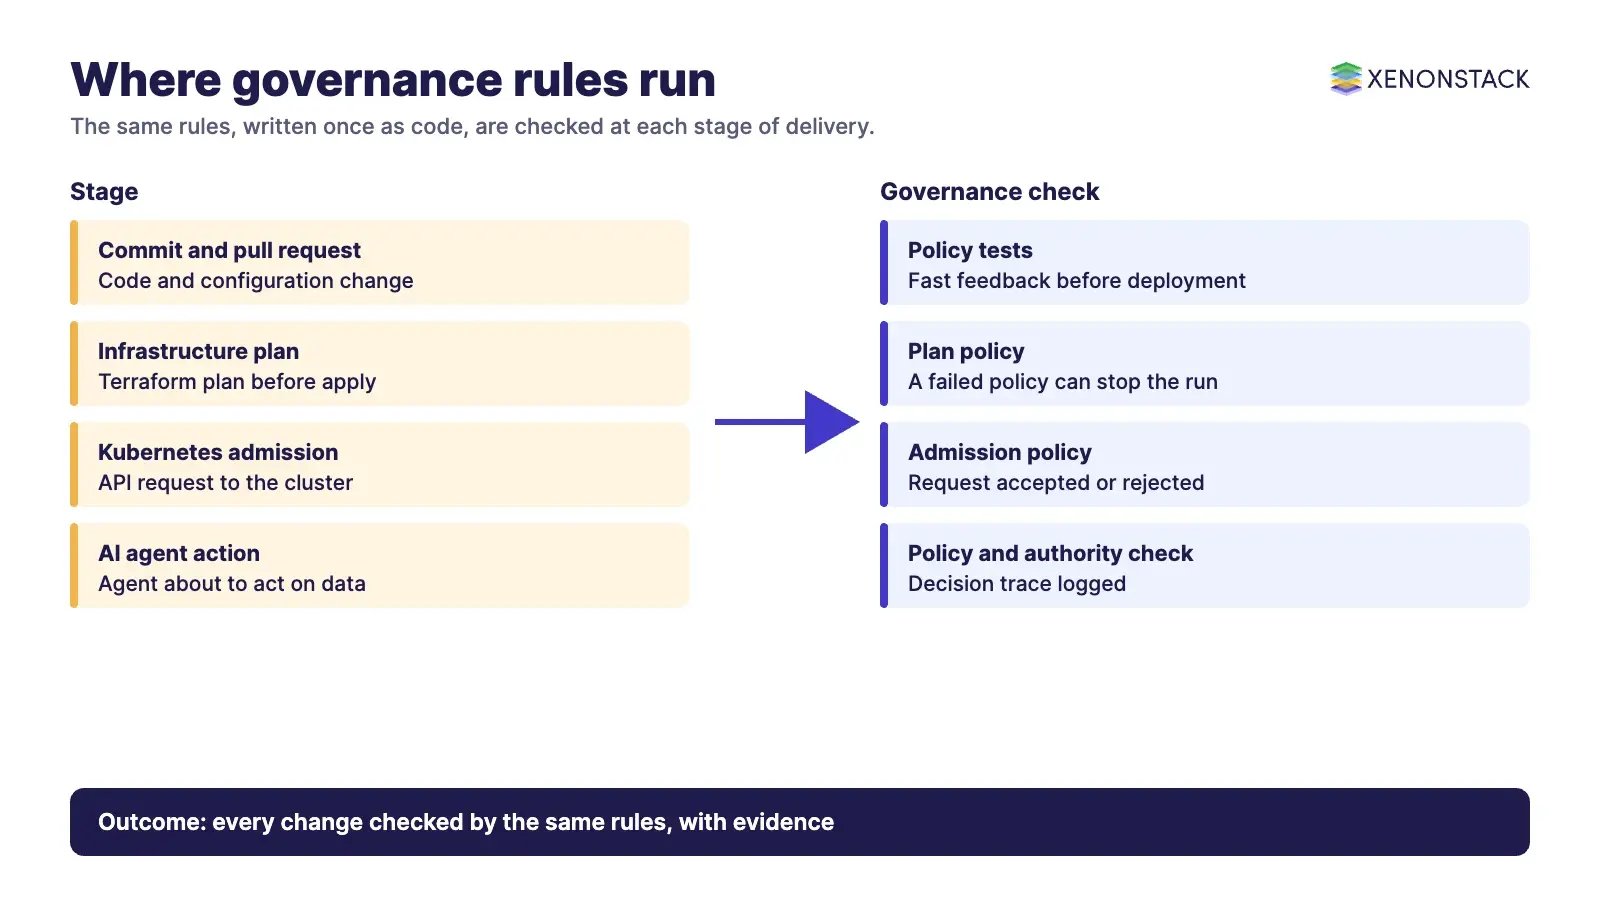
Rules are most useful when they run at several points, from the developer's commit to the running cluster. The tools below are documented by their own projects.
| Stage | What is checked | Example tooling (vendor documentation) | When it fits |
|---|---|---|---|
| Commit and pull request | Policy tests on code and configuration | Open Policy Agent: a general-purpose policy engine that takes structured input such as JSON and returns a decision | Fast feedback before anything is deployed |
| Infrastructure plan | The Terraform plan against policy before apply | HCP Terraform policy enforcement: policies can be written in Terraform policy, Sentinel or OPA (Rego), and a failed policy can stop the run depending on its enforcement level | Stopping non-compliant infrastructure before it exists |
| Kubernetes admission | API requests accepted or rejected as they arrive | ValidatingAdmissionPolicy, stable since Kubernetes v1.30, uses CEL rules without a separate webhook server; Kyverno offers validate, mutate, generate and image-verification policies | Guardrails on running clusters |
| Runtime and reporting | Drift, exceptions and evidence | Your monitoring and ticketing systems, fed by the policy results | Proving to auditors that controls ran |
OPA is a graduated project of the Cloud Native Computing Foundation, and it can act as a Kubernetes admission controller or validate Terraform plans. Our CI/CD pipeline guide shows where these gates sit in a pipeline.
How do you implement governance as code?
- Decide scope: Pick the workloads, owners and risks to cover first. Start with one high-value control, such as blocking public storage or untagged resources.
- Write standards as rules: Turn each standard into a testable rule with an owner, a severity and a link to the requirement it supports.
- Automate the gates: Run the rules in the pipeline, at infrastructure plan and at cluster admission. Use advisory mode first, then move critical rules to blocking.
- Handle exceptions in code: Record who approved each exception, why and until when, in the same repository.
- Track and report: Send policy results to the internal management systems so each team sees its own findings and risk teams see the evidence.
How does governance as code apply to AI agents?
Cloud rules answer "may this resource exist?". Agents raise a second question: "may this agent take this action now, with this data, under this authority?". The same idea applies. Agent permissions, approval thresholds and data boundaries are written as versioned policy, checked before the agent acts, and logged afterwards. The NIST AI Risk Management Framework gives a common vocabulary for this work and organises AI risk management around four functions: Govern, Map, Measure and Manage.
ElixirData describes ElixirData Context OS as a decision layer that builds decision-ready context, checks policy and authority before agents act, and logs a lineage record of each action. AgentGRC is described by ElixirData as governance, risk and compliance controls for autonomous agent actions, keeping agents within policy and recording the evidence audit and risk teams need. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
| Layer | Question it answers | Typical control | Evidence produced |
|---|---|---|---|
| Infrastructure | May this resource be created? | Plan and admission policies | Policy result per change |
| Pipeline | May this change be released? | Policy tests and approvals | Pipeline logs |
| AI agents | May this agent act now? | Policy and authority checks before action | Decision trace per action |
What are the trade-offs and when should you not use it?
- Rules need owners. Code that nobody maintains blocks teams and is soon bypassed.
- Start in advisory mode. Blocking too early on rules with false positives hurts delivery.
- Not every control is codable. Judgement calls, such as risk acceptance, still need a named human approver. Code should route them, not replace them.
- Small estates. A handful of resources may need only a checklist and a pipeline test.
What does this look like in practice?
Compliance automation is one visible result of the approach. The video below shows how an agent-driven compliance workflow assembles audit evidence.
ElixirClaw video: compliance automation and audit evidence with AI agents.
To map one governance decision your cloud estate and agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
FAQ
What is governance as code?
It is writing security, cost, availability and compliance rules as versioned code that is enforced automatically across cloud infrastructure and delivery pipelines.
How is it different from Infrastructure as Code?
Infrastructure as Code describes what to build. Governance as code checks that what is built, and every change to it, meets your standards.
Which tools are used?
Common choices include Open Policy Agent, HashiCorp Sentinel and Terraform policy in HCP Terraform, Kyverno and Kubernetes ValidatingAdmissionPolicy.
Can policies stop a Terraform change?
Yes. In HCP Terraform each run's plan is checked against policy sets, and depending on the enforcement level a failed policy can stop the run.
Does it apply to AI agents?
Yes. Agent actions can be checked against policy and authority before they run and logged afterwards, in line with the Govern, Map, Measure and Manage functions of the NIST AI Risk Management Framework.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE