Key takeaway
- Compliance as code explained for CIOs and CISOs: how OPA, Gatekeeper, Conftest and NIST OSCAL fit, an adoption sequence and where it falls short.
Compliance as code turns written compliance requirements into versioned rules and automated tests that run in the delivery pipeline and against live systems. The result is a check on every change, evidence generated as a by-product, and a report that does not depend on a manual audit sprint.
This guide is for CIOs, CISOs, platform leads and architects who must decide where to start. It covers how the approach works, what Open Policy Agent (OPA) and OSCAL each contribute, where it fits and where it does not, and a sequence for adopting it. For the wider pipeline view, see our guide to DevSecOps pipeline, tools and governance.
What is compliance as code?
Compliance as code uses programmatic methods to implement, validate, remediate, monitor and report on the standards an organisation must meet. A requirement such as "storage must be encrypted" is written once as a rule, kept in version control and evaluated automatically against infrastructure definitions, pipelines and running resources.
It does not replace security work. Security is not the same as compliance: a rule set proves that the encoded controls were checked, not that the system is safe against every threat.
How does compliance as code work?
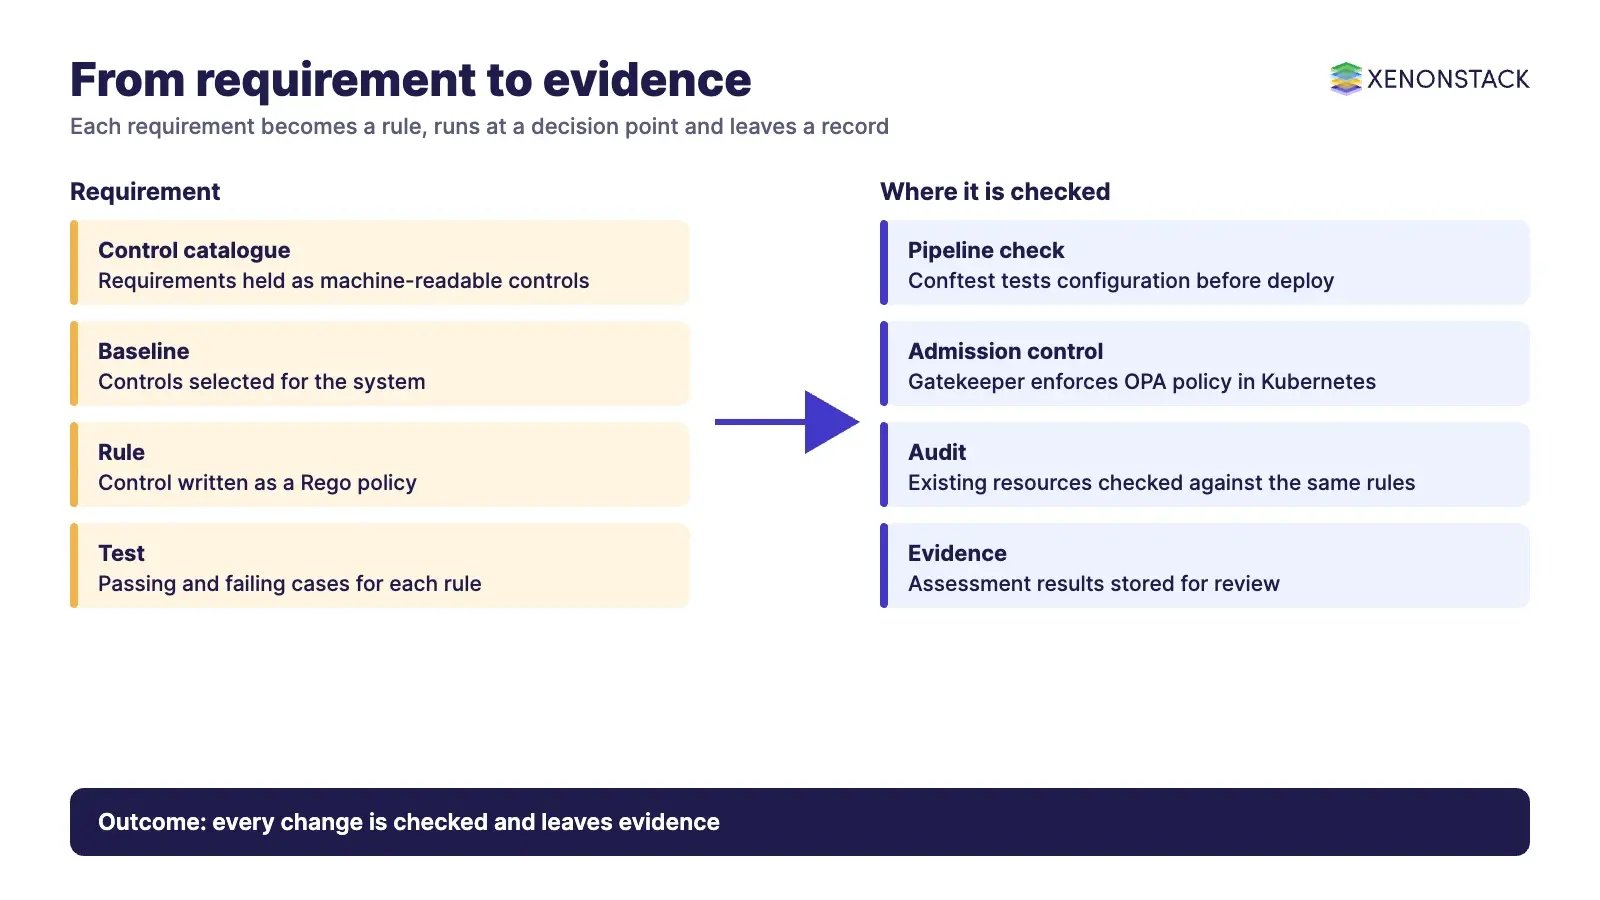
Teams translate each requirement into three separate things: the specification (what must be true), the implementation (the rule that checks it) and the enforcement (where the rule runs and what happens on failure). Keeping them separate lets an auditor read the specification while engineers maintain the rule.
| Stage | What happens | Typical mechanism |
|---|---|---|
| Define | Requirements and internal policies are mapped to controls | Control catalogue and baseline (for example in OSCAL) |
| Write | Controls become rules and tests in a policy language | Rego policies for OPA |
| Enforce | Rules run at commit, build, deploy and admission | Conftest in CI, Gatekeeper in Kubernetes |
| Monitor | Running systems are checked against the same rules | Audit of existing resources, scheduled scans |
| Evidence | Results are stored with who, what, when and why | Assessment results, logs, decision records |
What do Open Policy Agent and OSCAL each do?
Open Policy Agent (OPA) describes itself as an open source, general-purpose policy engine that unifies policy enforcement across the stack, and it is a graduated Cloud Native Computing Foundation project under the Apache Licence 2.0. Software sends structured input such as JSON to OPA and receives a decision, so policy is separated from the code that enforces it. Policies are written in Rego, a declarative language built for hierarchical data.
OSCAL, the Open Security Controls Assessment Language, is led by NIST with industry. It provides open, machine-readable formats in XML, JSON and YAML for control-based risk assessment. Its models sit in three layers: a control layer (catalogue, profile and control mapping), an implementation layer (system security plan and component definition) and an assessment layer (assessment plan, assessment results and plan of action and milestones).
| Standard or tool | Role | Use it when | Source |
|---|---|---|---|
| OPA and Rego | Decides allow, deny or other outcomes from structured input | You need enforcement at Kubernetes admission, in CI/CD or on Terraform plans | OPA documentation |
| Gatekeeper | Validating and mutating Kubernetes webhook that enforces OPA policies as custom resources; its audit feature lists resources already violating a policy | You run Kubernetes and want policy before and after deployment | Gatekeeper documentation |
| Conftest | Tests structured configuration (Kubernetes, Terraform, Tekton and others) with Rego | You want policy checks in a pipeline before anything deploys | Conftest |
| OSCAL | Machine-readable controls, plans and assessment results | You must exchange control baselines and assessment evidence in a standard format | NIST OSCAL layers |
Why do enterprises need compliance as code?
Does it fit CI/CD pipelines?
Yes. When checks run on every commit, developers see compliance status while the change is still small, and non-compliant changes are stopped before release. Our guide to infrastructure as code in a CI/CD pipeline and the explainer on infrastructure as code best practices cover the pipeline side.
Does it improve the audit trail?
An audit trail should answer what changed, who changed it, who requested and reviewed it, why, whether it was tested, and when. Rules and policies held in version control give most of that history for free. Automated evidence collection also shortens audit preparation, because the same rules run every time.
Does it close the knowledge gap?
Compliance documents are long and hard to read. Encoding them as rules means engineers do not need to interpret every clause, and a report listing, for example, twenty non-compliant applications can be ranked by business criticality.
Does it help teams move faster?
Rules can be tested, versioned and grouped into bundles that are shared across teams. Checks can be re-run after each small change, and security teams release a new bundle when a requirement changes instead of briefing every team.
How should an enterprise adopt compliance as code?
| Step | Action | Outcome to look for |
|---|---|---|
| 1 | Pick one regulation or internal standard and a handful of high-value controls | A short, agreed control list |
| 2 | Write each control as a rule and test it with passing and failing examples | Rules that behave as the control owner expects |
| 3 | Run rules in CI in advisory mode, using a tool such as Conftest | Visible findings without blocking delivery |
| 4 | Run the same policies in a test environment, then in production, in that order | No surprise blocks in production |
| 5 | Switch selected rules to blocking and add admission control where you run Kubernetes | Non-compliant changes stopped before release |
| 6 | Store results as evidence and review them on a schedule | Audit-ready history and a rule review cycle |
For governance of AI agents that act on enterprise systems, the same idea applies to agent actions. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. The ElixirData Compliance Agent page describes monitoring of activity against regulations, internal rules and contract terms.
What are the best practices?
- Start early in the lifecycle (shift left) so developers see failures while changes are small.
- Test every rule with cases that should pass and cases that should fail, including edge cases.
- Deploy and test policies in a test environment before production.
- Review rules whenever a standard, regulation or internal policy changes.
- Keep security assessments of applications and infrastructure; rules do not replace them.
- Have people review automated reports instead of trusting them blindly.
- Do not encode every requirement. Some controls need human judgement.
When is compliance as code not the right answer?
Controls that depend on judgement, culture or physical processes, such as training quality or vendor relationships, cannot be tested by code alone. Rules written without the control owner can also drift from what the requirement means. Treat passing checks as evidence for those controls you have encoded, and keep manual review for the rest. Our guide on the GDPR gives a compliance checklist of the kind that mixes both.
Which video explains continuous compliance automation?
Compliance automation with AI agents, from ElixirClaw: SOC 2 audit evidence in 4 days, not 6 weeks.
To map one compliance decision your agents and pipelines should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is compliance as code?
Compliance as code means writing compliance requirements as machine-readable rules and tests that run automatically in the delivery pipeline and against running systems, so that checks, evidence and reports come from the same versioned source.
Is compliance as code the same as policy as code?
They overlap. Policy as code is the technique of writing policy in a language such as Rego and enforcing it through an engine such as OPA. Compliance as code applies that technique to a named regulation, standard or internal control, and adds evidence and reporting.
What is OSCAL and how does it relate to OPA?
OSCAL is a NIST-led set of open, machine-readable formats (XML, JSON and YAML) for control catalogues, baselines, system security plans and assessment results. OPA is a policy engine that makes decisions. OSCAL describes what must be met and what was found; OPA enforces rules at decision points. They complement each other and neither replaces the other.
Where does OPA enforce policy in a pipeline?
Per its own documentation, OPA can be used for Kubernetes admission control, CI/CD pipelines and Terraform plan validation, among other uses. Gatekeeper applies OPA policies to Kubernetes resources, and Conftest tests configuration files such as Kubernetes manifests, Terraform code and Tekton pipelines.
Does compliance as code mean we are compliant?
No. Automated checks cover only the controls you have encoded. Security is not the same as compliance, and assessors still need to review the rules, the evidence and the controls that cannot be tested by code.
Who should own the rules?
Compliance, security and engineering should own them jointly. Compliance interprets the requirement, security approves the control, and engineering implements, tests and versions the rule like any other code.
What next?
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Ready to put AI agents to work? Explore ElixirClaw, the agentic OS platform to build, orchestrate and govern AI agents.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE