Key takeaway
- GCP infrastructure as code after Deployment Manager: compare Infrastructure Manager, Terraform and Pulumi and plan a migration before 2027 turn-down.
For Google Cloud, infrastructure as code (IaC) now means one decision first: moving off Cloud Deployment Manager. Google's own notice says Deployment Manager reached end of support in 2026 and that, after 30 June 2027, the service will be turned down. Its recommended path is Infrastructure Manager, a managed service that runs Terraform, or another deployment technology of your choice.
This guide is for CTOs, platform leads and solution architects who own GCP estates. It explains what the change means, how the main GCP IaC options compare, how to sequence a migration, and what governance to put around it. For the basics, read our guide to infrastructure as code first.
What has changed for infrastructure as code on GCP?
Cloud Deployment Manager was the native GCP service for defining resources in YAML, with Jinja2 and Python templates. Google's deprecation page states that Deployment Manager reached end of support on 31 March 2026 (the page body gives 1 April 2026 for the same event), that new users are blocked from enabling it as of 30 June 2026, and that after 30 June 2027 the service cannot be used. Existing resources keep running, but you can no longer manage them with Deployment Manager or gcloud deployment-manager commands.
Treat the earlier advice to use Deployment Manager as outdated. Any template you still run through it is a dated liability, not a platform choice.
Which IaC option fits which GCP team?
Google's Terraform documentation lists Infrastructure Manager, the Cloud Development Kit for Terraform, the Google Cloud provider for Pulumi, Ansible, Crossplane and Cloud Deployment Manager under infrastructure as code. It does not rank them, so the choice is yours. The table gives a decision aid based on those sources.
| Option | When it fits | Current status |
|---|---|---|
| Infrastructure Manager | You want Google to run Terraform for you, with revisions, previews and Cloud Build integration | Google's recommended replacement for Deployment Manager |
| Terraform (own pipeline) | You already run Terraform across clouds and want one workflow | Documented by Google for provisioning on Google Cloud |
| Pulumi (Google Cloud provider) | Your engineers prefer general-purpose languages for infrastructure | Listed by Google as an IaC option |
| Ansible | You already manage configuration with playbooks and want the same tool for provisioning | Listed by Google as an IaC option |
| Crossplane | Your platform team already runs Crossplane | Listed by Google as an IaC option |
| Cloud Deployment Manager | Only to keep existing deployments running while you migrate | End of support reached in 2026; turn-down after 30 June 2027 |
What does Infrastructure Manager give an enterprise?
Google describes Infrastructure Manager as a managed service that simplifies and automates the deployment and management of Google Cloud infrastructure resources using Terraform. Its documented features matter to governance owners:
- Declarative Terraform configurations stored in Cloud Storage buckets, Git repositories or on a local machine.
- Deployments and revisions, with logs, configurations, resource lists and state files kept for each revision.
- Preview deployments that show how a change would affect infrastructure before it is applied.
- Terraform variables to customise a deployment without editing source code.
- Cloud Build integration for automated workflows, with each deployment running
terraform init,validateandapplyin an ephemeral Cloud Build environment. - A choice of supported Terraform version for each deployment.
Revisions and previews give you a change record and a review step. That is the evidence audit and risk teams ask for.
How should you migrate from Deployment Manager?
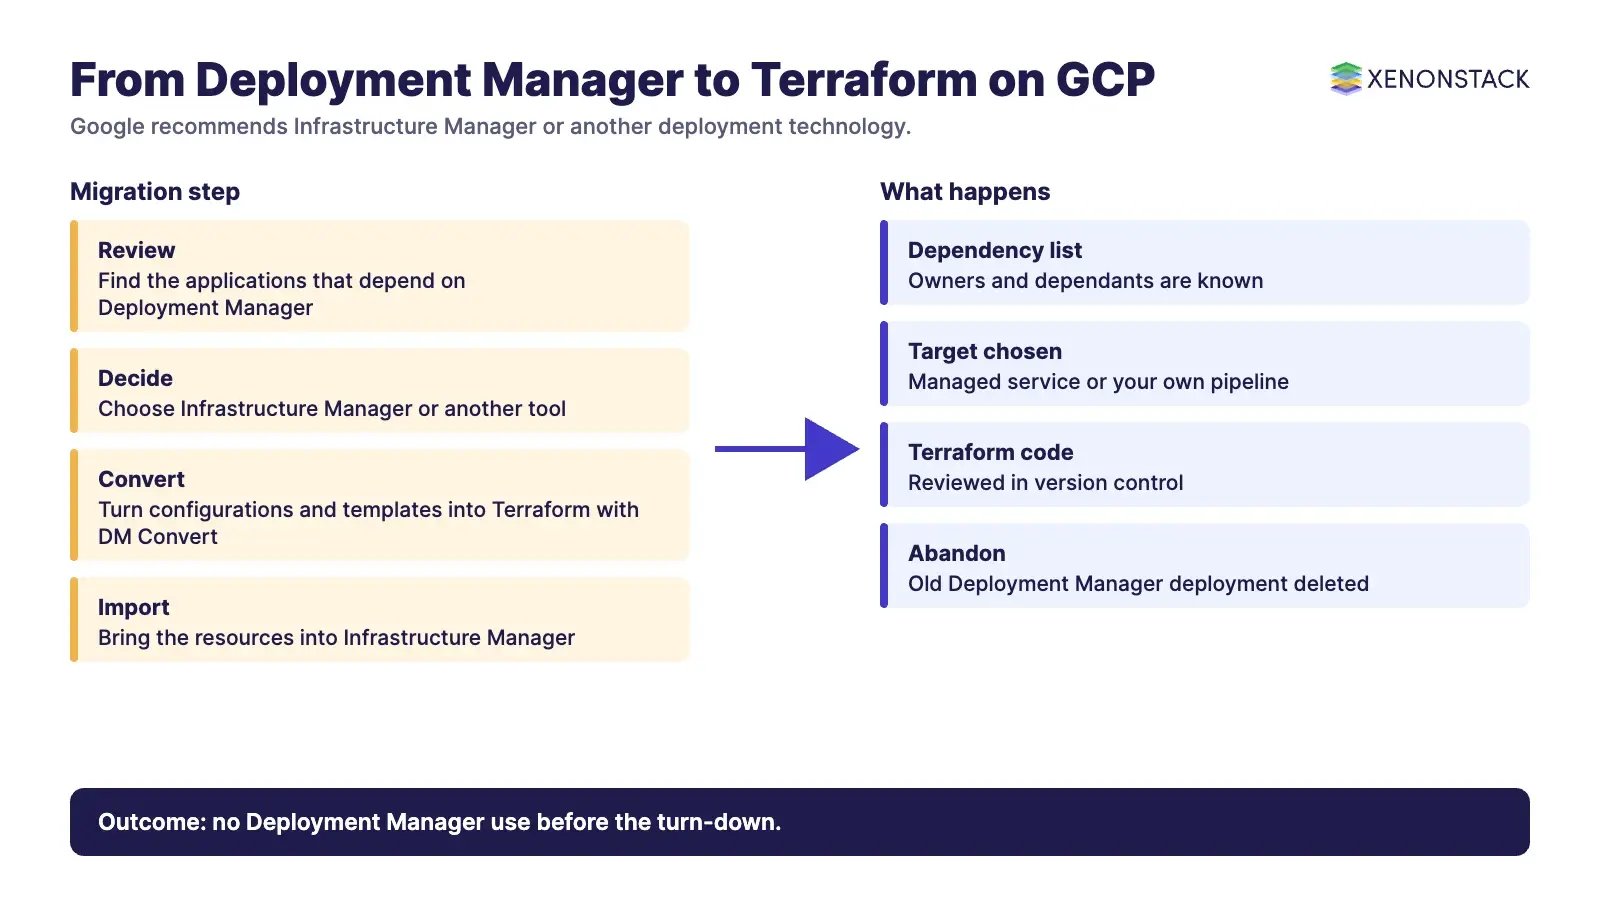
Google's migration guidance has three steps. Review the use cases and applications that depend on Deployment Manager. Decide whether Infrastructure Manager meets your needs or another tool fits better. Then convert configurations and templates to Terraform with DM Convert, import the resources into Infrastructure Manager, and delete the Deployment Manager deployment using abandon.
| Phase | What to do | Decision owner |
|---|---|---|
| 1. Inventory | List every Deployment Manager deployment, its owner and its dependants | Platform lead |
| 2. Choose the target | Infrastructure Manager, your own Terraform pipeline, or another listed tool | Enterprise architect |
| 3. Convert | Run DM Convert, review the Terraform output, test in a non-production project | Platform engineers |
| 4. Import and abandon | Import resources, confirm no drift, then abandon the old deployment | Platform lead with change board |
| 5. Retire | Remove Deployment Manager use before the turn-down date | CTO or head of engineering |
What governance, security and cost controls should surround GCP IaC?
Infrastructure code is now a control surface, so govern it like application code. Keep configurations in version control. Require a reviewed preview before every apply. Store Terraform state in a controlled location; Google has a tutorial on storing Terraform state in Cloud Storage. Separate who may write infrastructure code from who may approve and apply it.
As teams add AI agents that raise infrastructure changes, the question becomes which changes an agent may make and under what policy. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
In our delivery work, Terraform and Ansible-based provisioning, together with CI/CD pipelines, keep environments reproducible, auditable and documented. We apply the same pattern when deploying our platforms into a customer's preferred cloud, including GCP.
When should you not rush to Infrastructure Manager?
- You already run a mature multi-cloud Terraform pipeline. Moving it into a managed service adds a second control plane for little gain.
- Your team standardises on Pulumi, Ansible or Crossplane. Google lists them as infrastructure as code options.
- You have only a few, stable Deployment Manager deployments. Convert and import them on a schedule that clears the 2027 date, not in a panic.
Our Terraform guide, IaC tools overview, IaC principles and DevOps on Google Cloud cover the wider tooling and practices.
To map one infrastructure change your agents should be allowed to make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What replaces Cloud Deployment Manager on Google Cloud?
Google's deprecation page recommends migrating to Infrastructure Manager or an alternative deployment technology.
When does Deployment Manager stop working?
Google states it reached end of support in 2026, new users are blocked from enabling it as of 30 June 2026, and after 30 June 2027 the service cannot be used and will be turned down.
Does Infrastructure Manager use Terraform?
Yes. Google describes it as a managed service that runs Terraform configurations, and each deployment can specify a supported Terraform version.
How do I move existing deployments?
Convert configurations and templates to Terraform with DM Convert, import the resources into Infrastructure Manager, then delete the Deployment Manager deployment using abandon.
Can I use Ansible, Pulumi or Crossplane instead?
Yes. Google lists Ansible, the Pulumi provider for Google Cloud and Crossplane alongside Infrastructure Manager as infrastructure as code options.
How do previews help governance?
Infrastructure Manager can create preview deployments to show how changes would affect infrastructure before they are applied, and keeps logs, configurations and state files for each revision.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE