Key takeaway
- Compare software build tools such as Maven, Gradle, Ant, Bazel and CMake, and see how builds fit CI/CD and supply chain security for enterprise teams.
A software build tool turns source code into something that can run, and does it the same way every time. It compiles code, resolves dependencies, runs tests and packages the result as a versioned artefact, so that a release does not depend on one developer's laptop. For an enterprise, the choice of build tool shapes release speed, repeatability and how well you can prove what went into a release.
This guide explains what a build is, compares the main tool families (Make, Maven, Gradle, Ant, Bazel, CMake and meta-build tools), and shows where builds sit in a CI/CD pipeline. It also covers the build as a software supply chain control. For the wider toolchain, see our guide to DevOps tools.
What is a software build?
A build generates software artefacts from source code. Compilation, which turns source files into executable objects, is an important part of it, but a build usually also resolves dependencies, runs automated tests and packages the output with a version number. Builds are made at checkpoints in development, and again when code is ready for test or release.
| Aspect | What it means in practice |
|---|---|
| Quality | Each build runs the same compile and test steps, so a failing change is caught early. |
| Version control | Each build carries a version, usually incremental, so teams can tell which artefact is newest and trace it back to a commit. |
| Compilation and packaging | Source becomes executable objects, then a deployable package such as a JAR or container layer. |
Why do teams use build tools?
A build tool automates the many manual steps between a code change and a deployable package, such as compiling, running tests, copying files and packaging, behind one command. It also keeps track of changes, so unchanged parts are not rebuilt. Without it, builds drift between machines, release steps live in people's heads and onboarding a new engineer takes longer.
Which build tool fits which job?
The tools below solve the same problem in different ways. The status column is taken from each project's own pages, read on 13 November 2026.
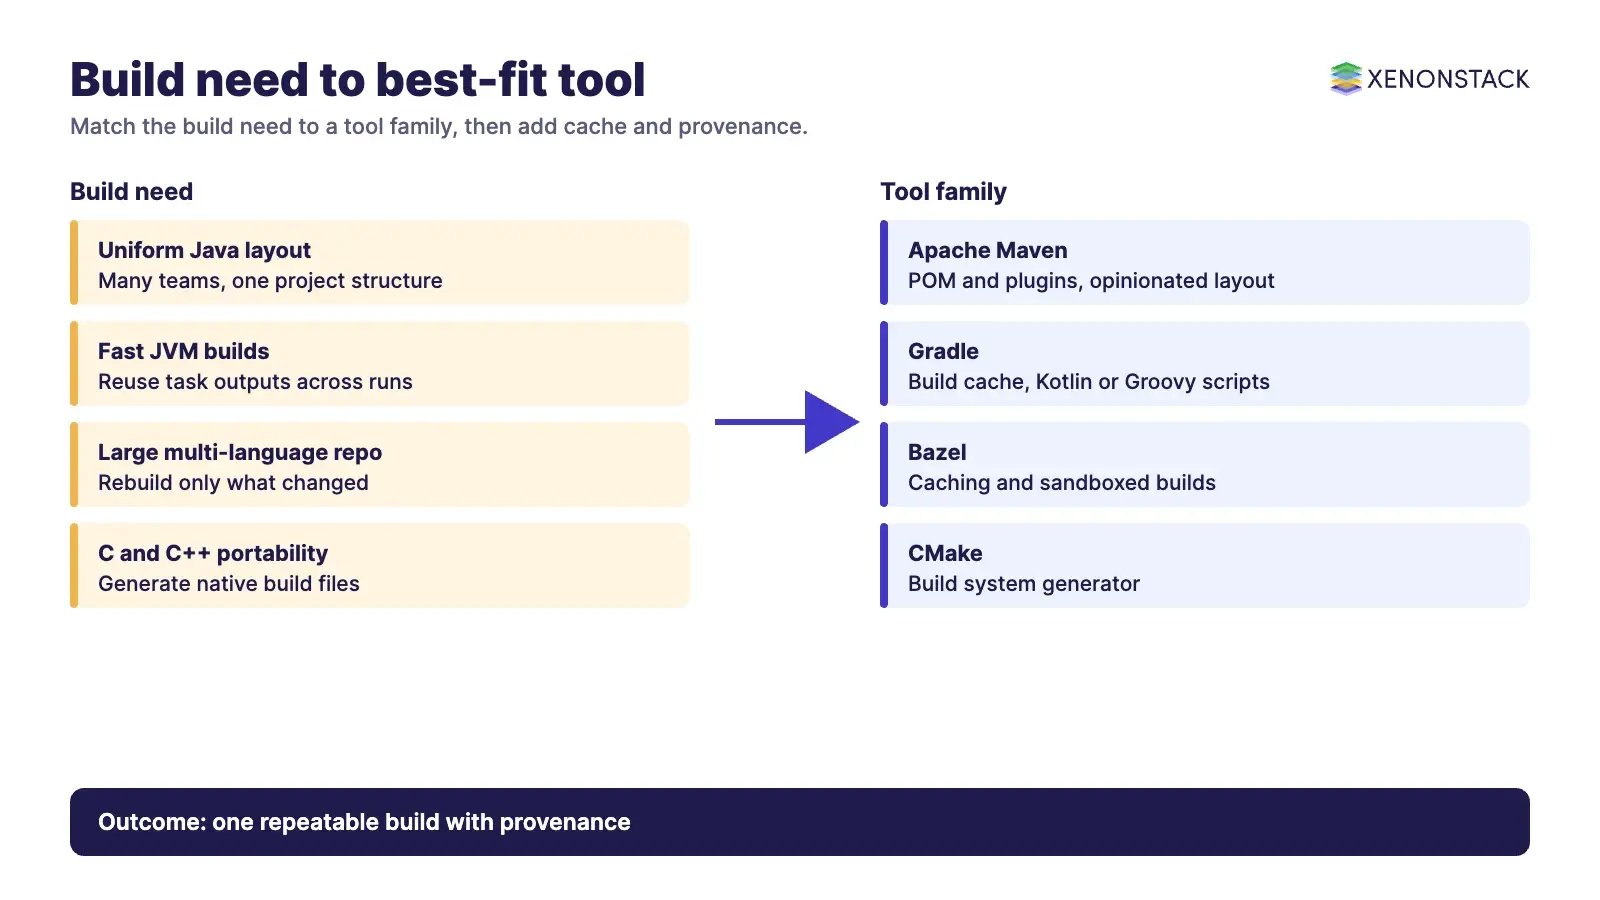
| Tool | Best fit | What its own site says | Trade-off |
|---|---|---|---|
| Make / GNU Make | C and C++ projects, small scripts | Classic Unix build tool driven by a Makefile (confirm details on the GNU Make page) | Manual dependency rules; limited for large multi-language builds |
| Apache Ant | Legacy Java builds | A Java library and command-line tool that runs targets from a build file; it imposes no coding conventions or directory layout; Ant 1.10.18 was released on 6 September 2026 and Ant 1.9.x is end of life (Apache Ant) | You write every step yourself |
| Apache Maven | Java projects that want one uniform layout | Builds a project from its project object model (POM) plus plugins; takes an opinionated approach to project layout; manages dependencies including transitive ones (Apache Maven) | Projects with unusual structure may fit poorly |
| Gradle | JVM and Android projects needing flexible, fast builds | Offers a build cache that reuses task outputs when inputs match a previous run; supports Kotlin and Groovy build scripts (Gradle build cache documentation) | More flexible than Maven, so more room for inconsistent scripts |
| Bazel | Large monorepos and multi-language builds | Caches earlier work, rebuilds only what changed, can run sandboxed builds and supports many languages (Bazel) | Needs investment in build rules and migration |
| CMake | C and C++ across platforms | A cross-platform build system generator that produces a native build system, for example Makefiles (CMake) | It generates builds; it does not run them itself |
How do Maven and Gradle differ?
Maven favours convention: if your project follows its layout, a new engineer can read any Maven build. Gradle favours flexibility and speed through task-output reuse. The Gradle documentation says its build cache is off by default, only tasks that opt in are cached, and the recommended set-up lets CI populate a remote cache while developers only read from it. Choose Maven when uniformity matters most, and Gradle or Bazel when build time on large codebases is the pain.
What are make-based and make-incompatible tools?
Make-based tools follow the Make model of targets and dependencies. They include GNU Make, Nmake (part of Visual Studio) and MPW Make for classic Mac OS. Make-incompatible tools, such as Ant, Maven, Gradle and Gulp (a front-end build tool), use their own build models and languages. Confirm the current status of each on its official page before standardising.
What are build script generators and meta-build tools?
Build script generators do not build the software themselves. They produce files that native build tools use. CMake is an example, and the GNU Build System, BuildAMation and qmake are others. Meta-build tools, often called package managers, build many projects from a list of packages. Examples include Pkgsrc, Portage and Homebrew, and Nix, which focuses on reproducible builds. Their features and status change, so confirm each on its own page.
Where do build tools sit in CI and CD?
In continuous integration, developers merge changes to a shared mainline several times a day, and each merge triggers a build and its tests. A CI server runs your build tool; it does not replace it. Our guides on CI/CD pipeline stages and tools and continuous delivery cover the stages after the build, and our DevOps metrics guide shows how to measure the result. Continuous delivery keeps software in a releasable state at all times, so an error in production code can be fixed quickly.
Good practice is to build an artefact once, version it, and promote that same artefact through test, staging and production environments, on any mix of cloud and on-premises infrastructure. That avoids the drift that comes from rebuilding for each environment.
Why does the build matter for software supply chain security?
The build is the point where source becomes the artefact you ship, so it is a target and a control point. Two ideas help. The first is provenance: records of how an artefact was built. The SLSA Build track describes Build L1 (provenance exists), L2 (a hosted build platform generates and signs provenance) and L3 (a hardened platform with stronger tamper protection). The SLSA page we read is marked retired, with version 1.2 as the current version, so check slsa.dev for the latest. The second is reproducibility. The Reproducible Builds project defines a build as reproducible if, given the same source, build environment and build instructions, any party can produce bit-for-bit identical copies of the specified artefacts.
The NIST Secure Software Development Framework (SP 800-218, version 1.1) groups secure development practices into four areas: prepare the organisation, protect the software, produce well-secured software and respond to vulnerabilities. Build integrity belongs under protecting the software. Our supply chain security guide goes further.
How should an enterprise choose and adopt a build tool?
| Step | What to do |
|---|---|
| 1. Inventory | List languages, repositories and current build scripts. |
| 2. Standardise | Pick one primary tool per language family, with a shared layout. |
| 3. Cache | Add a build cache and have CI populate it. |
| 4. Record provenance | Produce and store build provenance for release artefacts. |
| 5. Review | Retire tools whose projects are end of life. |
As builds are increasingly run and fixed by software agents, the same questions apply: which agent may change a build, under which policy, and where is the decision recorded. ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control, and ElixirData's Audit Agent is aimed at audit trails and compliance evidence.
To map one build or release decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
FAQ
What is a software build tool?
It is a program that automates turning source code into a runnable, versioned artefact by compiling, resolving dependencies, testing and packaging.
What is the difference between Maven and Gradle?
Maven builds from a POM and an opinionated project layout. Gradle offers a build cache that reuses task outputs when inputs match a previous run, and supports Kotlin and Groovy scripts.
Is Apache Ant still maintained?
According to its site, Ant 1.10.18 was released on 6 September 2026 and Ant 1.9.x reached end of life in June 2024.
What is a reproducible build?
One where, given the same source, build environment and instructions, any party can produce bit-for-bit identical artefacts, as the Reproducible Builds project defines it.
Is a build tool the same as a CI tool?
No. A CI server runs your build tool when code is merged. The build tool does the compiling and packaging.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE