Securing Apache ZooKeeper means deciding who can connect to the ensemble, who can read or change each znode, and how traffic between clients and servers is protected. According to the ZooKeeper client-server authentication guide, Kerberos is used through SASL with the GSSAPI mechanism, and the server and each client load a JAAS file that names a principal and a keytab. ACLs then limit what each identity can do on a znode.
This guide is for platform and security leads who run ZooKeeper under Hadoop, HBase, Solr or older Kafka estates. It sets out the Kerberos steps the project documents, the ACL, quorum and TLS controls around them, and what to check on versions and advisories. For how ZooKeeper itself works, read Apache ZooKeeper: architecture, ACLs and setup. For Kafka metadata and KRaft, see Kafka and ZooKeeper architecture.
What does ZooKeeper security cover?
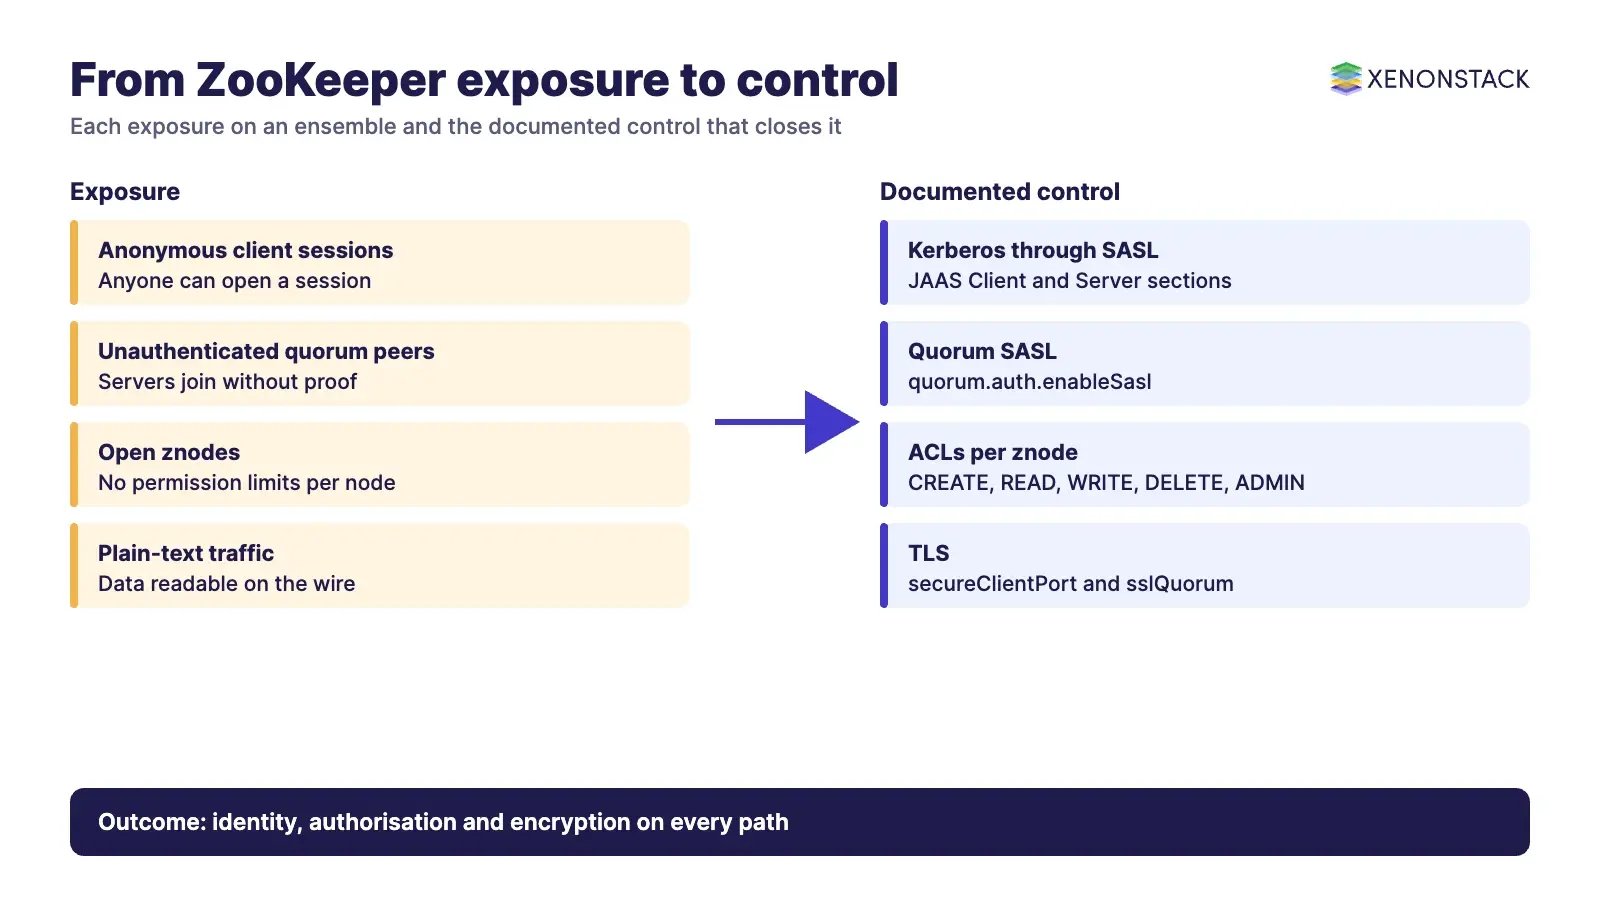
ZooKeeper holds small but critical data: configuration, leader state and locks. A user who can write to it can change how the systems above it behave, so the controls below should be treated as layers, not alternatives.
| Layer | What it protects | Documented control |
|---|---|---|
| Client authentication | Who may open a session | SASL with Kerberos (GSSAPI), set with authProvider.1 and a JAAS Client section |
| Server-to-server authentication | Who may join the quorum | quorum.auth.enableSasl, with QuorumServer and QuorumLearner JAAS sections |
| Authorisation | What an identity may do on a znode | ACLs with CREATE, READ, WRITE, DELETE and ADMIN permissions |
| Transport protection | Traffic on the wire | TLS through secureClientPort and sslQuorum |
| Exposure | Which commands and ports are reachable | 4lw.commands.whitelist and network controls |
Sources: client-server authentication, server-server authentication and the administrator's guide, read 13 November 2026.
How do you set up Kerberos authentication on a ZooKeeper server?
The project guide describes four server-side steps. First, create a service principal for each server host in the form zookeeper/hostname and a keytab for it, using your Kerberos administration tools. Second, add a Server section to a JAAS file. Third, enable the SASL provider in zoo.cfg. Fourth, point the server JVM at the JAAS file.
JAAS Server section, as shown in the guide (the path and host name are placeholders):
Server {
       com.sun.security.auth.module.Krb5LoginModule required
       useKeyTab=true
       keyTab="/path/to/server/keytab"
       storeKey=true
       useTicketCache=false
       principal="zookeeper/yourzkhostname";
};
In conf/zoo.cfg, the guide sets the provider, and in java.env it passes the JAAS file to the JVM:
authProvider.1=org.apache.zookeeper.server.auth.SASLAuthenticationProvider

SERVER_JVMFLAGS="-Djava.security.auth.login.config=/path/to/server/jaas/file.conf"
The guide notes that the keytab should not be readable by anyone other than the ZooKeeper server process user. It also lists two optional server settings, kerberos.removeHostFromPrincipal and kerberos.removeRealmFromPrincipal, which are commented out by default and which the administrator's guide documents with a default of false.
How does a client authenticate?
A client needs its own keytab and a Client section in a JAAS file, with the JVM flag set through CLIENT_JVMFLAGS in java.env. According to the guide, SASL is on by default for clients and can be turned off with -Dzookeeper.sasl.client=false. If the server principal is not zookeeper/hostname, the client can be told the user part with zookeeper.sasl.client.username, or the full principal with zookeeper.server.principal, which the guide says works in 3.5.7+ and 3.6.0+.
What happens when authentication fails?
By default, a client that fails SASL authentication is disconnected immediately. The guide says this can be relaxed with zookeeper.maintain_connection_despite_sasl_failure set to yes, which weakens the control and is not advised for production. To go further, sessionRequireClientSASLAuth (default false, from 3.6.0) requires clients to authenticate with SASL before a session is established.
Two further notes from the guide. A login thread periodically refreshes the credentials on client and server, so tickets do not lapse silently, and the addauth command has no effect for the SASL scheme. Under FIPS mode the administrator's guide says only GSSAPI (Kerberos) is available for SASL.
XenonStack's walkthrough video shows the same flow in a lab:
Video: How to Secure Apache Zookeeper with Kerberos (XenonStack, YouTube). Commands in the video may use older paths, so follow the current project guide above.
How do you secure traffic between ZooKeeper servers?
Quorum peers can authenticate each other with SASL. The server-server guide lists three settings in zoo.cfg, all defaulting to false:
| Setting | What the guide says |
|---|---|
| quorum.auth.enableSasl | Enables quorum authentication using SASL |
| quorum.auth.learnerRequireSasl | Learners send an authentication packet to peer servers; the guide says it can be used during upgrades |
| quorum.auth.serverRequireSasl | If true, all unauthenticated quorum peer learner connection requests are rejected |
The JAAS file gets QuorumServer and QuorumLearner sections, each with a Krb5LoginModule, a keytab and a principal. The guide says a single shared principal (servicename/localhost) does not support authorisation, whereas a host-based principal (servicename/_HOST) does: ZooKeeper replaces _HOST with each server's FQDN from the server.id entries, each host needs its own keytab, and servers accept only learners whose host name is in the ensemble list. It states that the feature is supported from 3.4.10.
How do ACLs limit what an authenticated user can do?
Authentication proves identity, and ACLs decide what that identity may do. According to the programmer's guide, ACLs are not recursive: an ACL on a parent does not apply to its children, so each znode that matters needs its own.
| Permission | Allows |
|---|---|
| CREATE | Creating a child node |
| READ | Getting data from a node and listing its children |
| WRITE | Setting data for a node |
| DELETE | Deleting a child node |
| ADMIN | Setting permissions |
The guide lists these built-in schemes: world (anyone), auth (the current authenticated user), digest (a username and password hash), ip (the client address) and x509 (the client's X500 principal). For SASL logins, the administrator's guide describes zookeeper.superUser as a way to name a user with super access to the znode tree, so keep that identity tightly held. The same guide describes zookeeper.skipACL under unsafe options: it skips ACL checks and, in its words, opens full access to the data tree to everyone, so never set it in production.
How do you add TLS to a ZooKeeper ensemble?
The administrator's guide describes TLS in addition to SASL, not instead of it. Kerberos proves who is connecting, while TLS protects the bytes. The settings below are from the guide, read 13 November 2026.
| Setting | What the guide says | Since |
|---|---|---|
| secureClientPort | Port for TLS client connections; set alongside clientPort for mixed mode | 3.5.5 |
| serverCnxnFactory | Set to NettyServerCnxnFactory for TLS-based server communication | 3.5.5 |
| sslQuorum | Enables encrypted quorum communication; default false | 3.5.5 |
| ssl.clientAuth | Authenticates TLS client connections (none, want or need; default need) | 3.5.5 |
| ssl.hostnameVerification | Default true | 3.5.5 |
| 4lw.commands.whitelist | Default is srvr only; * enables all four-letter commands | 3.5.3 |
The guide also describes upgrading an existing non-TLS cluster with no downtime, which is the safer path for a live ensemble. Take certificate and key store settings (ssl.keyStore.* and ssl.trustStore.*) from the guide for your release.
Which ZooKeeper versions and advisories should you check?
The releases page lists 3.9.7 as current and 3.8.8 as the latest stable release, and marks 3.7.2 as end of life since 2 February 2024. The security page lists fixes in 3.8.8 and 3.9.7, and its titles include a SASL authorisation bypass on the client port through a client-supplied authorisation ID, an ACL enforcement bypass after an ACL revocation, and several denial-of-service issues. Affected version ranges differ between a few entries' headers and descriptions, so confirm each range and the CVE record on the official page before planning an upgrade.
Related guides: see the Apache Storm security with Kerberos and HBase security with Kerberos guides for two systems that depend on a secured ZooKeeper.
What should an enterprise do first?
| Step | Action | Why first |
|---|---|---|
| 1. Inventory | List every system that depends on the ensemble, and which release it runs | You cannot secure or patch what you have not mapped |
| 2. Patch | Move to a supported release and read the security page | Recent advisories cover SASL and ACL handling |
| 3. Authenticate | Enable SASL with Kerberos for clients, then the quorum | Closes anonymous access |
| 4. Authorise | Set ACLs on the znodes that matter, not only the root | ACLs are not recursive |
| 5. Encrypt | Add TLS using the no-downtime upgrade path | Protects data on the wire |
| 6. Reduce exposure | Restrict ports and keep the 4lw whitelist narrow | Limits what an attacker can query |
When is Kerberos not the right answer?
Kerberos needs a working KDC, correct DNS and clock agreement, and keytab hygiene. If a small team lacks that operations capacity, the guide documents DIGEST-MD5 as an alternative SASL mechanism, with the trade-off that the JAAS file then holds plain-text passwords and must be locked down. FIPS-mode deployments cannot use DIGEST-MD5 at all.
Where does ZooKeeper security fit in governed enterprise AI?
Coordination services sit underneath the data platforms that AI agents depend on, so their access controls are part of governing what an agent can reach. They do not record why an agent acted. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need. See also zero trust security architecture for the wider control model.
Key takeaways on ZooKeeper security
Use Kerberos for identity, ACLs for authorisation per znode, SASL for quorum peers and TLS for transport, keep the ensemble on a supported release, and confirm every setting on the project guide for your version.
To map one decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is Apache ZooKeeper used for?
It is a coordination service for distributed systems. It handles configuration, naming, synchronisation and leader election for platforms such as Hadoop and HBase.
How does Kerberos secure ZooKeeper?
Clients and servers authenticate through SASL with the GSSAPI mechanism, using Kerberos principals and keytab files named in a JAAS file, so only identities the Kerberos realm recognises can open a session.
What are ZooKeeper ACLs?
Access control lists set permissions on each znode: CREATE, READ, WRITE, DELETE and ADMIN. They are not recursive, so each znode needs its own.
Is Kerberos enough on its own?
No. Combine it with ACLs, quorum authentication, TLS for transport and a restricted four-letter-word whitelist, and keep the release patched.
Can ZooKeeper servers authenticate each other?
Yes. Setting quorum.auth.enableSasl to true, with QuorumServer and QuorumLearner JAAS sections, enables SASL between quorum peers from release 3.4.10.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE