Key takeaway
- Build private and domain-specific LLMs and AI agents on private cloud compute: deployment options, governance, security, and a sequence to adopt them.
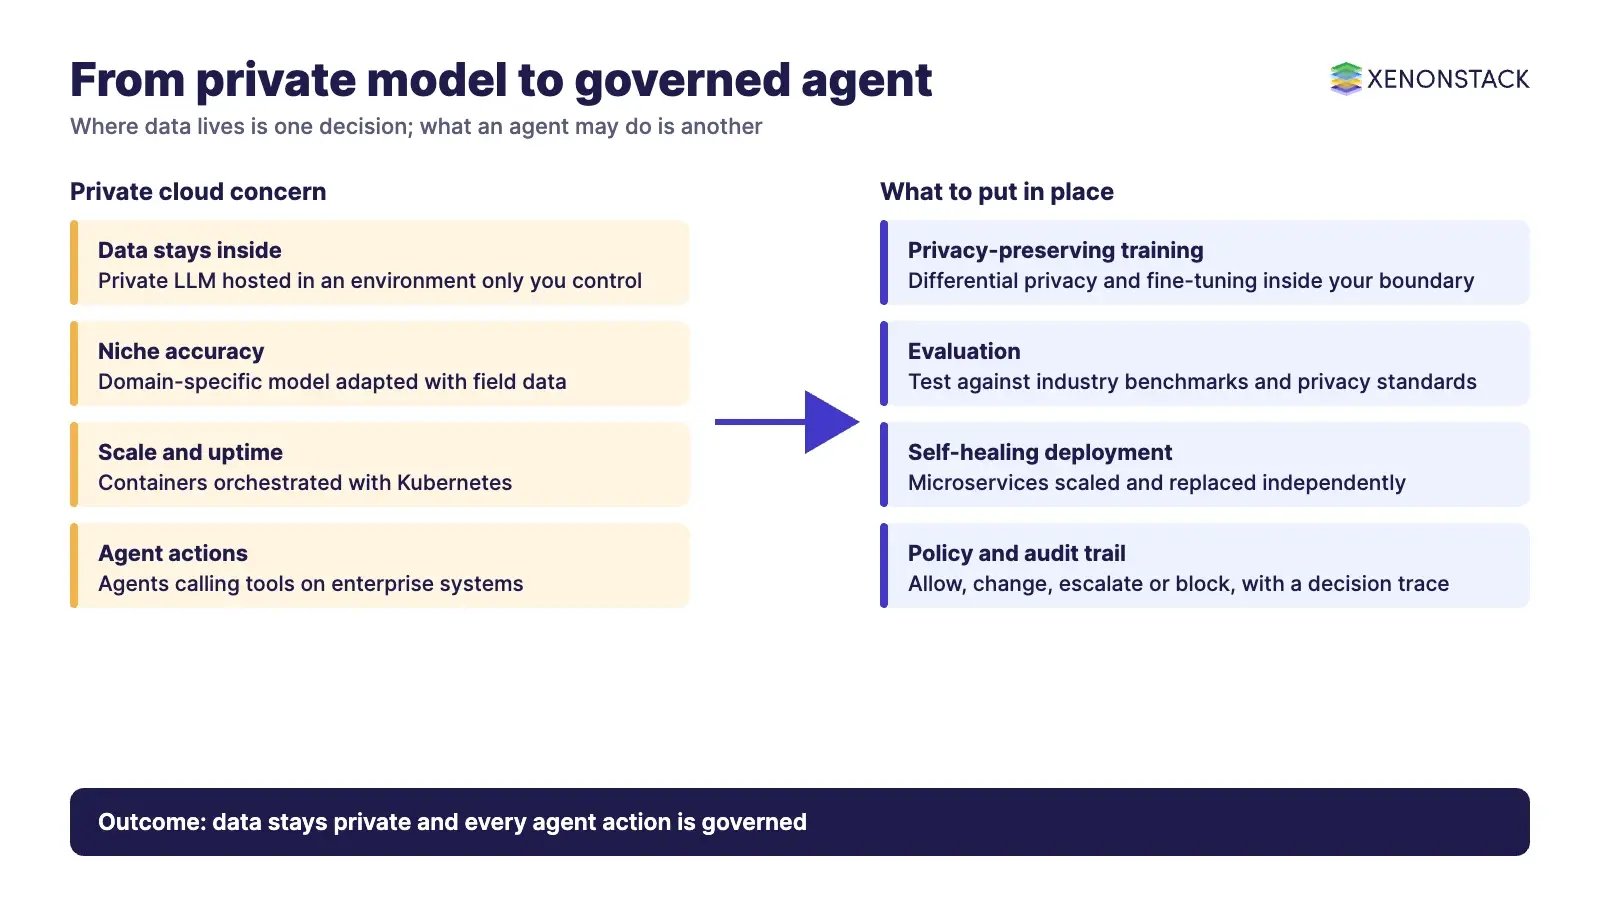
Agentic AI on private cloud compute means running AI agents, and the private or domain-specific models behind them, on infrastructure your organisation controls, such as a private cloud, a virtual private cloud or on-premises hardware. It suits enterprises whose data, audit needs or regulators rule out sending prompts and records to a shared model service. The model is only one part: the agent layer also needs policy, approvals and a record of every action.
This guide is for CTOs, CIOs, CISOs and solution architects. It compares private and domain-specific large language models, shows how to build and deploy them, and explains what changes once agents act on enterprise systems. For the model-building steps in depth, see how to build LLM and foundation models.
What is agentic AI on private cloud compute, and when does it fit?
Three terms are often mixed up. A private LLM is a model run in an environment only your organisation controls. A domain-specific LLM is a model adapted to one field such as law, medicine or customer service. An AI agent is software that uses a model to plan and take actions through tools. You can combine all three: a domain-specific model, hosted privately, driving an agent.
| Option | What it is | When it fits | Main trade-off |
|---|---|---|---|
| Private LLM | A model hosted in an environment only your organisation controls | Sensitive data, strict data-residency or audit needs, such as healthcare and finance | You run and update the infrastructure yourself |
| Domain-specific LLM | A base model adapted with field-specific data | Niche vocabulary and tasks where a general model is not accurate enough | Needs high-quality domain data and ongoing evaluation |
| Agent on private compute | An agent that calls tools and systems using a privately hosted model | Multi-step work across internal systems with data kept inside your boundary | Needs policy, approvals and monitoring on top of the model |
Why do enterprises prefer private and domain-specific models over general ones?
The reasons are practical, and each maps to a decision a leadership team has to own.
Targeted problem-solving: general models can struggle with niche problems that private and domain-specific models are built to address.
Control of results: you decide the training process, the data and the evaluation methods, so output can be tested against your own quality standards.
Data privacy and security: a private model can run in-house or in a cloud environment you control, which supports strict data security measures.
Reliability and compliance: private deployments let you set service levels and security controls that match your obligations.
How are private and domain-specific models built?
Both follow the same five steps. They differ in what each step emphasises: private models concentrate on protecting data, while domain-specific models concentrate on the quality and coverage of field data.
| Step | Private LLM | Domain-specific LLM |
|---|---|---|
| Define requirements | Set privacy needs, data sensitivity, risks and ethical data use | Identify the domain or industry to specialise in |
| Choose a base model | Weigh compliance, customisation, cost and performance | Same criteria, plus fit to the domain |
| Handle data | Apply privacy-preserving techniques such as federated learning, differential privacy, secure multi-party computation or homomorphic encryption | Gather and preprocess high-quality, domain-specific data |
| Train and fine-tune | Train with privacy-preserving methods and balance privacy against model effectiveness | Use transfer learning, hyperparameter tuning and parameter-efficient fine-tuning such as LoRA and QLoRA |
| Monitor, evaluate and refine | Update with new data and privacy requirements, and test against privacy standards | Update domain knowledge and test against industry benchmarks |
What do LoRA and QLoRA change for private teams?
Parameter-efficient fine-tuning lowers the hardware needed to adapt a model inside your own boundary. The LoRA paper reports that, against GPT-3 175B fine-tuned with Adam, LoRA can cut trainable parameters by 10,000 times and GPU memory requirements by a factor of three. The QLoRA paper reports that QLoRA makes it possible to fine-tune a 65B-parameter model on a single 48GB GPU. Both are the authors' own claims; test them on your model and data.
How should differential privacy be judged?
Differential privacy is a mathematical framework for measuring the privacy loss an individual faces when their data is in a dataset. NIST SP 800-226, published in March 2025, helps practitioners evaluate differentially private software and describes common implementation pitfalls it calls privacy hazards. Ask vendors and internal teams to show their evaluation against it, not only to name the technique.
How do you deploy and integrate private LLMs and agents?
Deployment means secure, scalable infrastructure with containers and APIs that integrate with existing systems without weakening data protection.
Should you deploy on a cloud, on-premises or hybrid?
| Option | When it fits | Trade-off |
|---|---|---|
| On-premises | You need the most direct control over private models and data | You own capacity planning and hardware |
| Private cloud or virtual private cloud | You want scalability for domain-specific models inside a boundary you control | Shared-responsibility details need to be agreed and audited |
| Hybrid | Sensitive workloads stay private while other workloads use wider cloud capacity | More integration and policy surface to manage |
For agents, ElixirClaw describes three deployment models on its own site: managed cloud, a private VPC or hybrid deployment where the platform runs inside your own AWS, Azure or GCP network, and on-premises or air-gapped deployment. It positions itself as an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
What do containers, Kubernetes and microservices add?
Docker containers package a model and its dependencies into one portable unit. This reduces conflicts between environments and adds isolation, which matters for private models.
Kubernetes automates scaling and management of containers. Its Kubernetes documentation describes self-healing behaviour such as restarting failed containers and replacing failed Pods to keep the specified number of replicas.
Microservices let you deploy and scale components independently, so one part of an LLM application can be updated without disturbing the rest.
What changes when agents act on enterprise systems from a private cloud?
A private deployment protects where data lives. It does not by itself control what an agent does. Once an agent can approve, change or send something, three questions matter.
| Concern | What to put in place | Related reading or tool |
|---|---|---|
| Security | Test the model and agent for known LLM weaknesses before release | See top LLM vulnerabilities and how to tackle them |
| Governance | Check each proposed agent action against policy and approvals before it reaches core systems | AgentGRC, ElixirData's governance, risk and compliance agent, which can allow, change, escalate or block an action |
| Audit | Keep the decision trace, the policy version in force and the authority chain for each decision | The ElixirData Audit Agent assembles that evidence for decisions made through Context OS |
| Context | Keep governed context, versioned policy and decision traces in one layer above the agents | ElixirData Context OS |
Cost is the other leadership question. A private deployment moves spend from usage fees to capacity, operations and staffing, so compare the full run cost with your expected workload before committing; the figures depend on your volumes and are not generic.
Where are private and domain-specific LLMs used?
| Sector | Model type | Typical use |
|---|---|---|
| Healthcare and finance | Private LLM | Handle confidential records such as patient data or transactions, and power secure customer tools |
| Banking | Domain-specific LLM | Virtual assistants for customer questions and staff retrieval from the bank's knowledge base |
| Retail | Domain-specific LLM | Personalised recommendations, offers and marketing content |
| Pharmaceuticals | Domain-specific LLM | Analysis of medical texts, test results and patient data in drug development and clinical trials |
| Education | Domain-specific LLM | Tailored learning materials, real-time assessment and personalised lessons |
What are the challenges, and when should you not go private?
Inference attacks: for private LLMs, staying robust against inference attacks while keeping the model useful is an ongoing balance.
Domain data: domain-specific models depend on high-quality data, and the quality and volume of that data set the depth of the model.
Bias: a model trained on inaccurate data produces inaccurate output, so review training data.
A private deployment is hard to justify when the data is not sensitive, the volume is low or you lack the staff to run and monitor the platform. In those cases a managed service with clear contractual terms may be the better first step.
What is a sensible adoption sequence?
Classify the data and decisions involved, and decide which must stay inside your boundary.
Pick one narrow domain use case and a base model that meets your compliance and cost needs.
Deploy on containers with orchestration, and set up monitoring and evaluation first.
Add the agent layer in shadow mode, comparing its actions with human decisions before widening its authority.
To map one decision your private-cloud agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is a private LLM?
A private LLM is a large language model built and run in a secure environment that only your organisation controls, with a focus on confidentiality and privacy.
How is a domain-specific LLM different from a private LLM?
A domain-specific LLM is customised for a field such as law, medicine or customer service. A private LLM is defined by where it runs and who controls the data. A model can be both.
Can a private cloud run AI agents and not only models?
Yes. ElixirClaw describes a private VPC or hybrid option where the platform runs inside your own AWS, Azure or GCP network, and an on-premises or air-gapped option.
What do LoRA and QLoRA do?
They are parameter-efficient fine-tuning methods. The LoRA paper reports 10,000 times fewer trainable parameters than full fine-tuning of GPT-3 175B, and the QLoRA paper reports fine-tuning a 65B model on a single 48GB GPU.
Why use Kubernetes for private LLMs?
Kubernetes automates scaling and management of containers, and its documentation describes restarting failed containers and replacing failed Pods to maintain the specified replicas.
Does a private deployment make agents safe?
No. It controls where data lives. Agent actions still need policy checks, approvals and an audit trail, which tools such as AgentGRC provide.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE